Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

Manage WhatsApp .crypt12, .crypt14 and .crypt15 files.

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…

Linux Distro for Mobile Security, Malware Analysis, and Forensics

Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

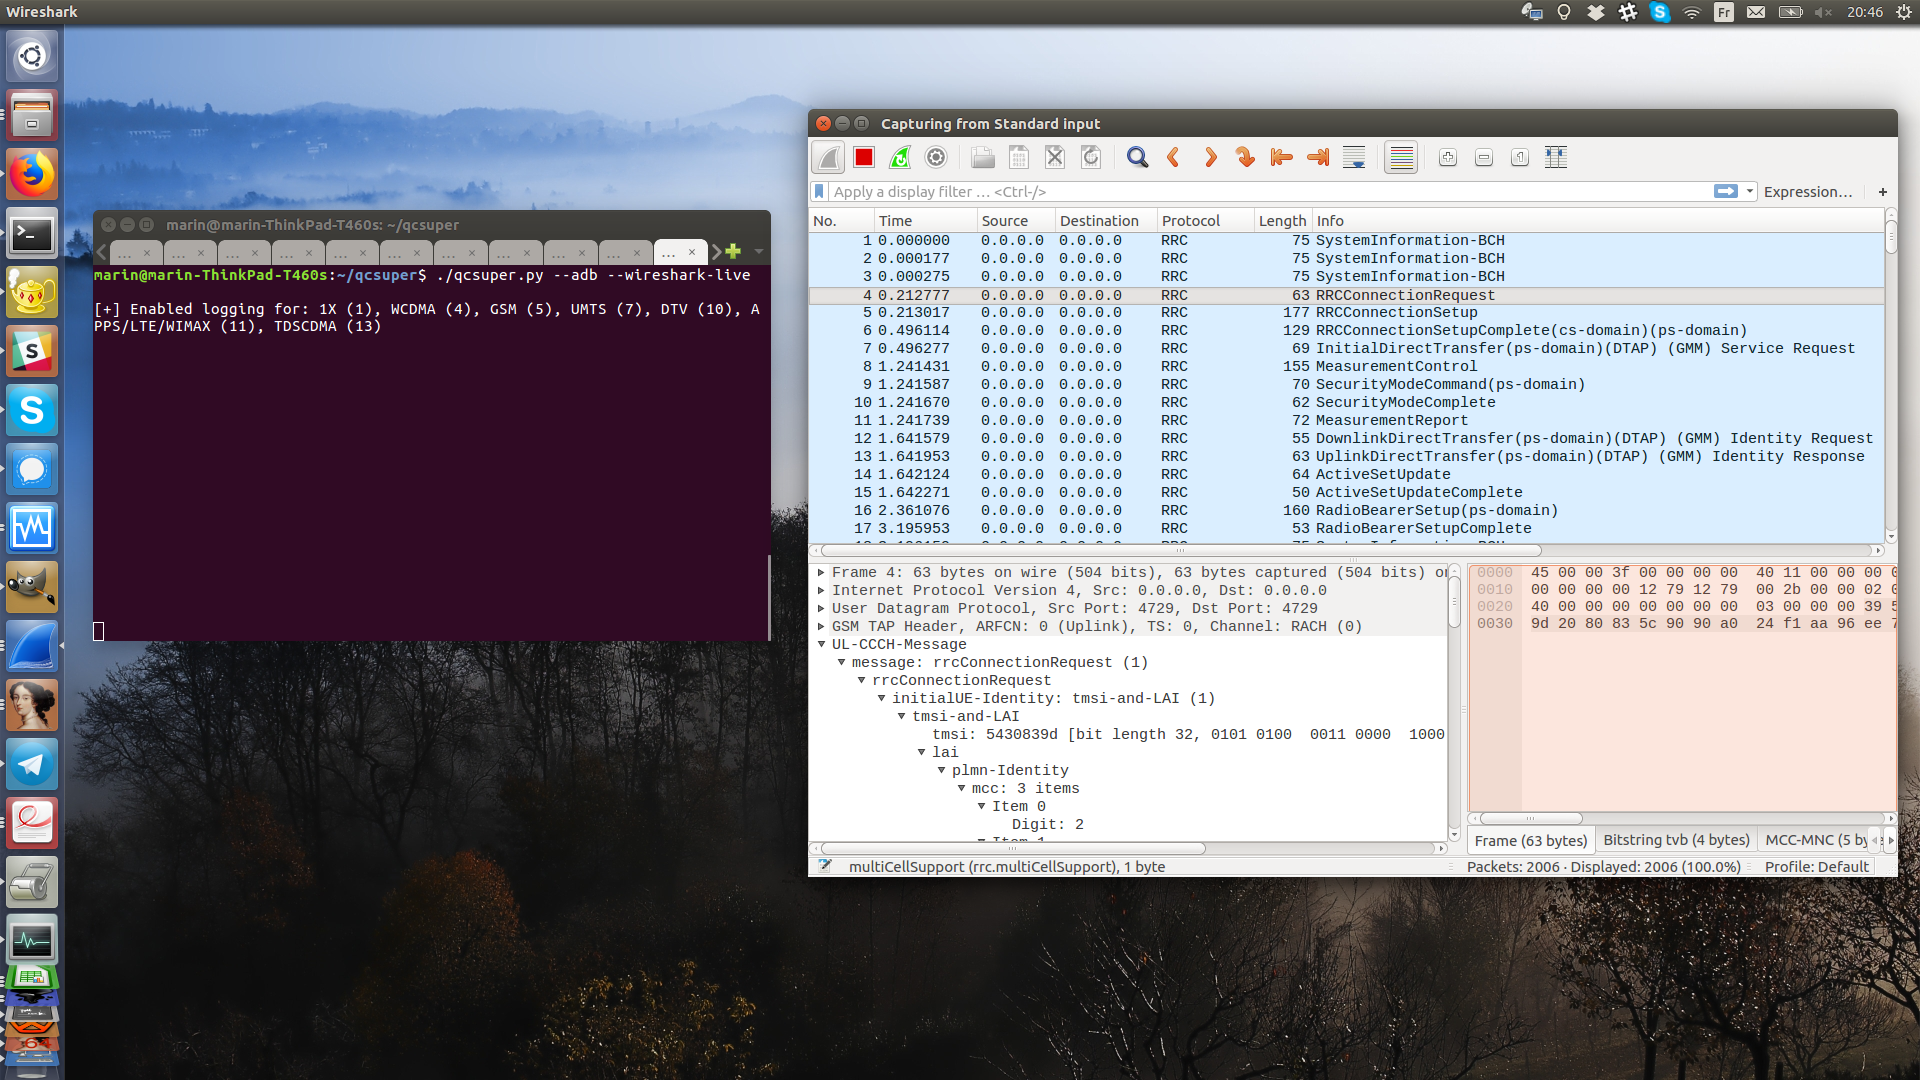
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.


Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser

📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…

Cellebrite Physical Analyzer python scripts to aid analysts with extended functionality

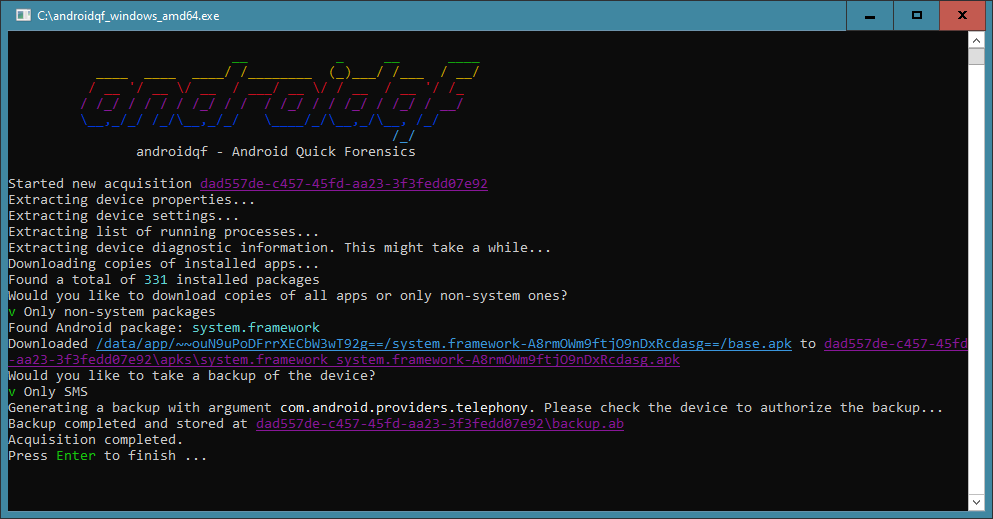
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…