AndroBugs_Framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…

AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…

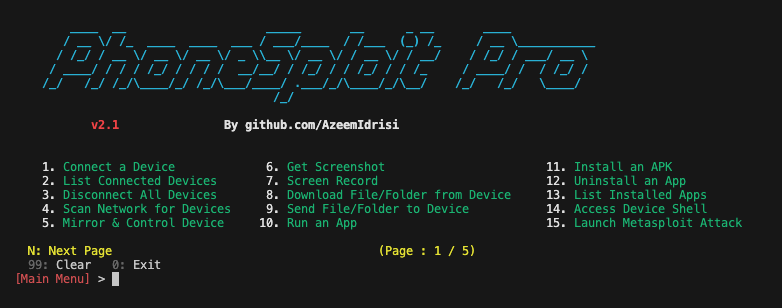
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!

Quickly analyze and reverse engineer Android packages

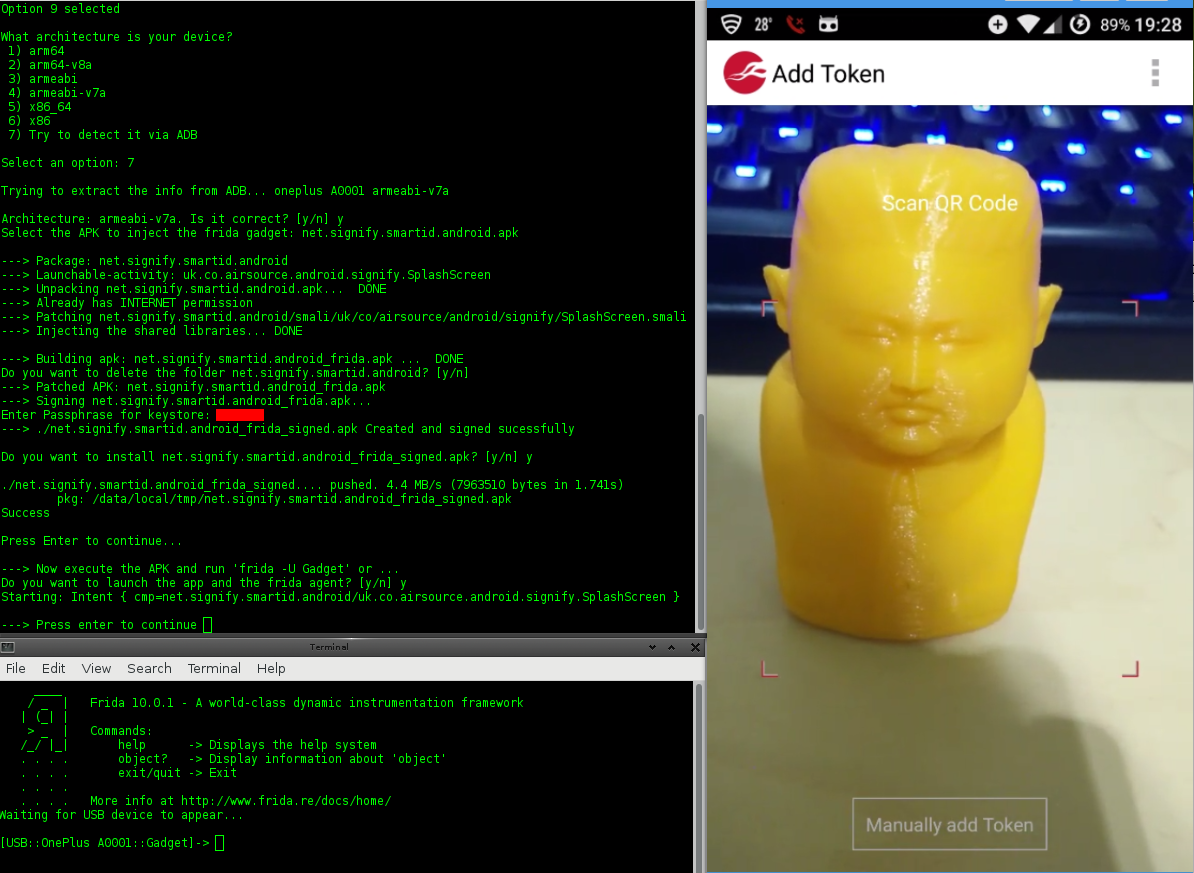
bash script to facilitate some aspects of an Android application assessment

Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…

An all-in-one hacking tool to remotely take over Android devices.

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.

Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…

A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.

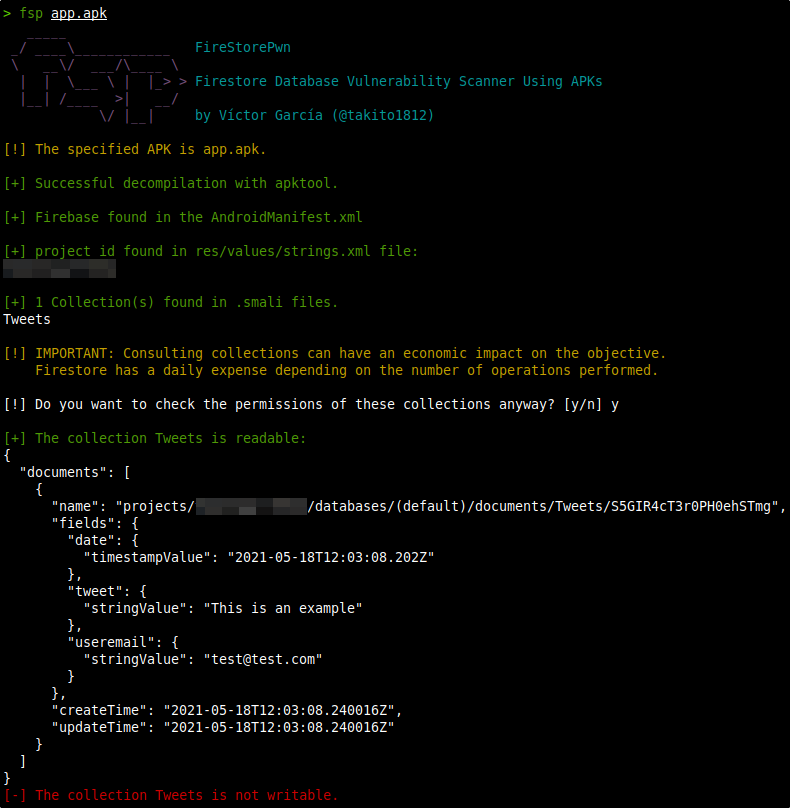
fsp - Firestore Database Vulnerability Scanner Using APKs

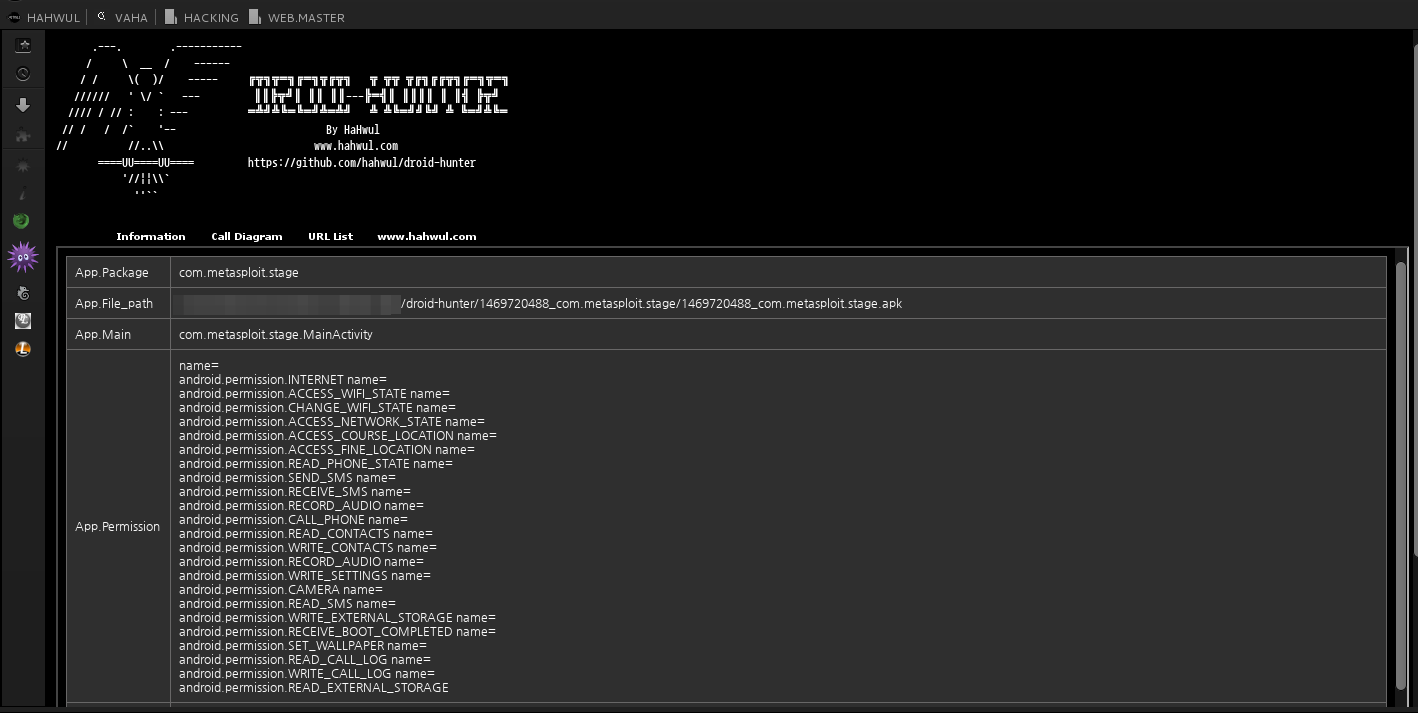
(deprecated) Android application vulnerability analysis and Android pentest tool

Ghidra is a software reverse engineering (SRE) framework

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

UNIX-like reverse engineering framework and command-line toolset

Main repo for hosting release binaries

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…