

iGoat-Swift
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
ctfeducationios-security+6
owasp/igoat-swiftOWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
 mzfr/slicer
A tool to automate the boring process of APK recon
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
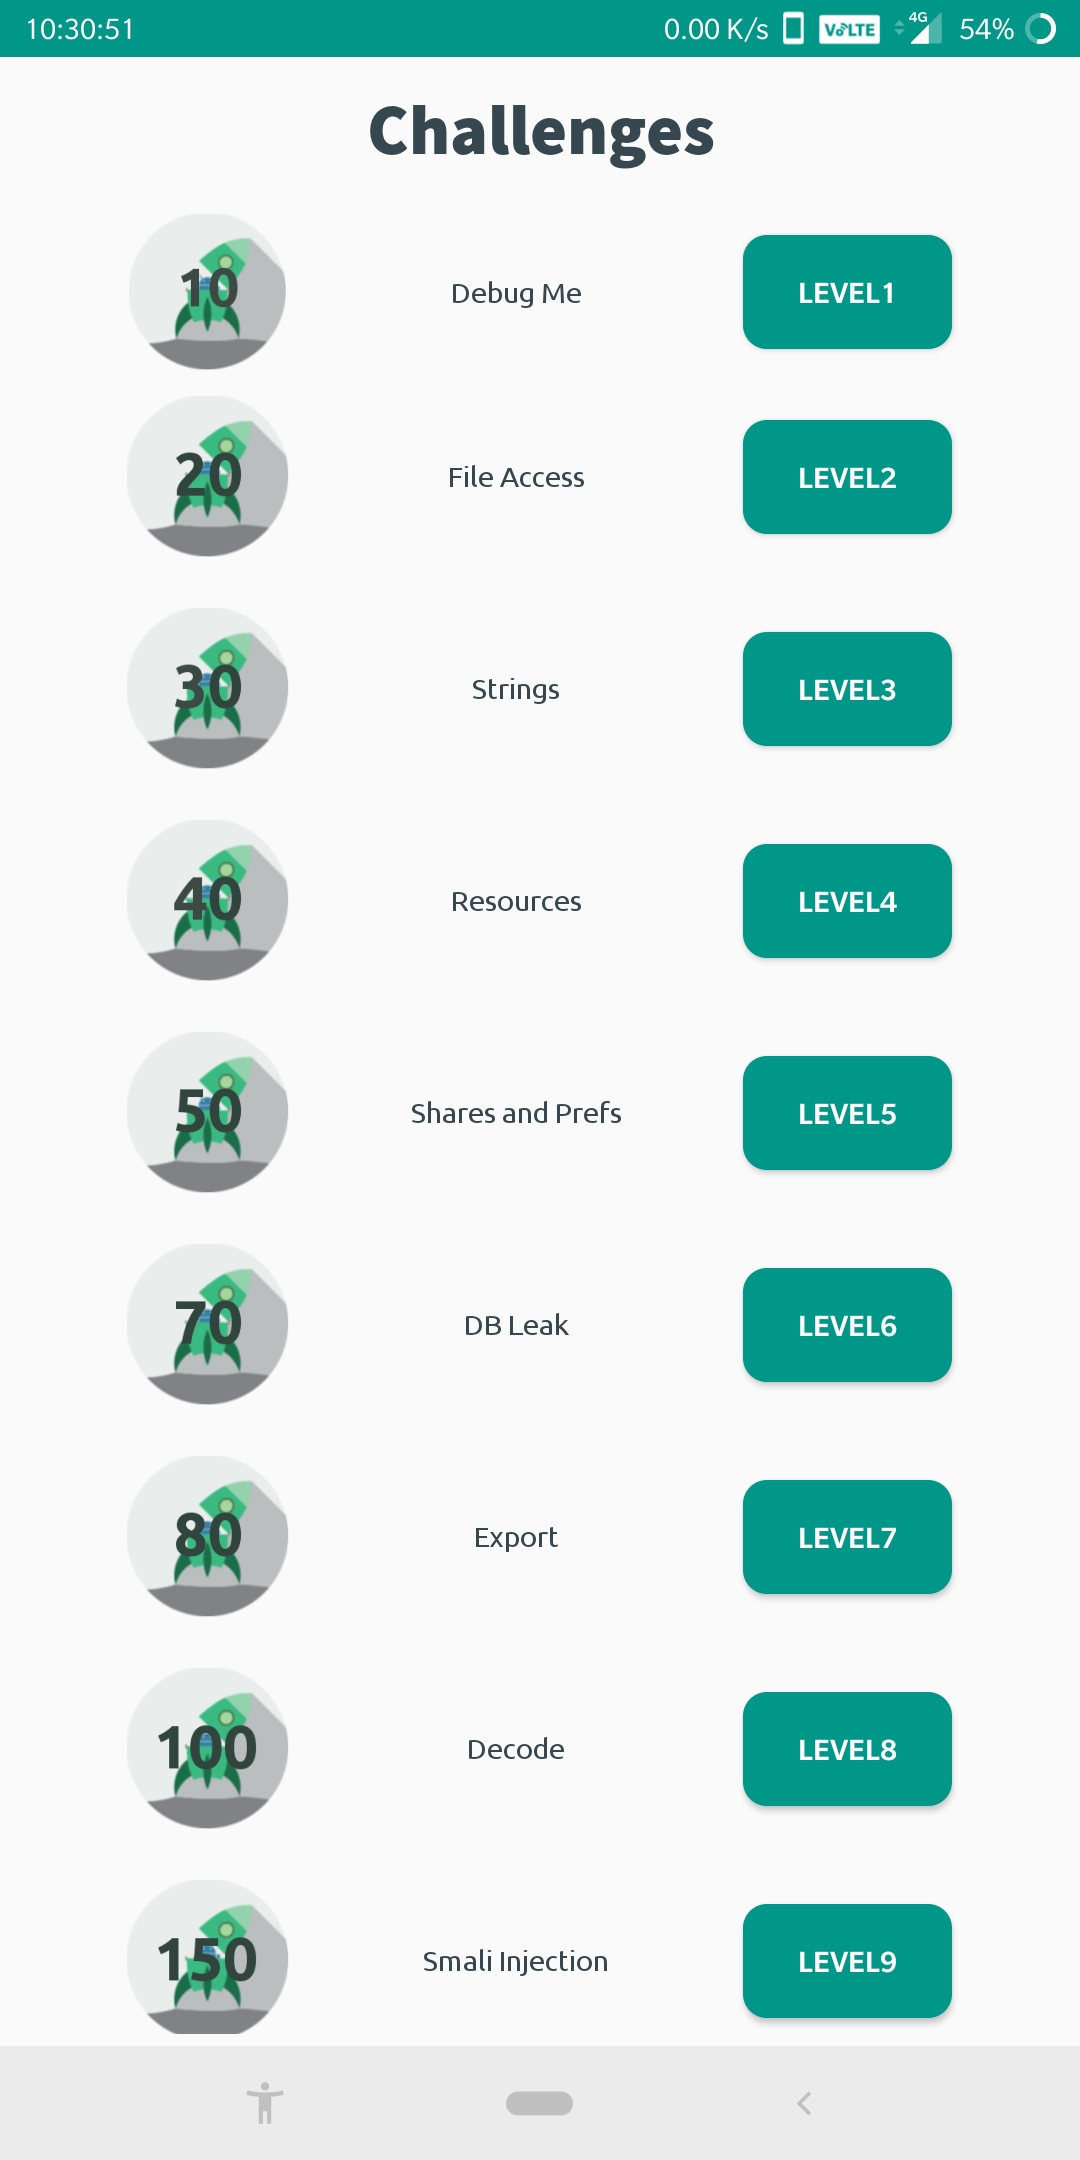 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
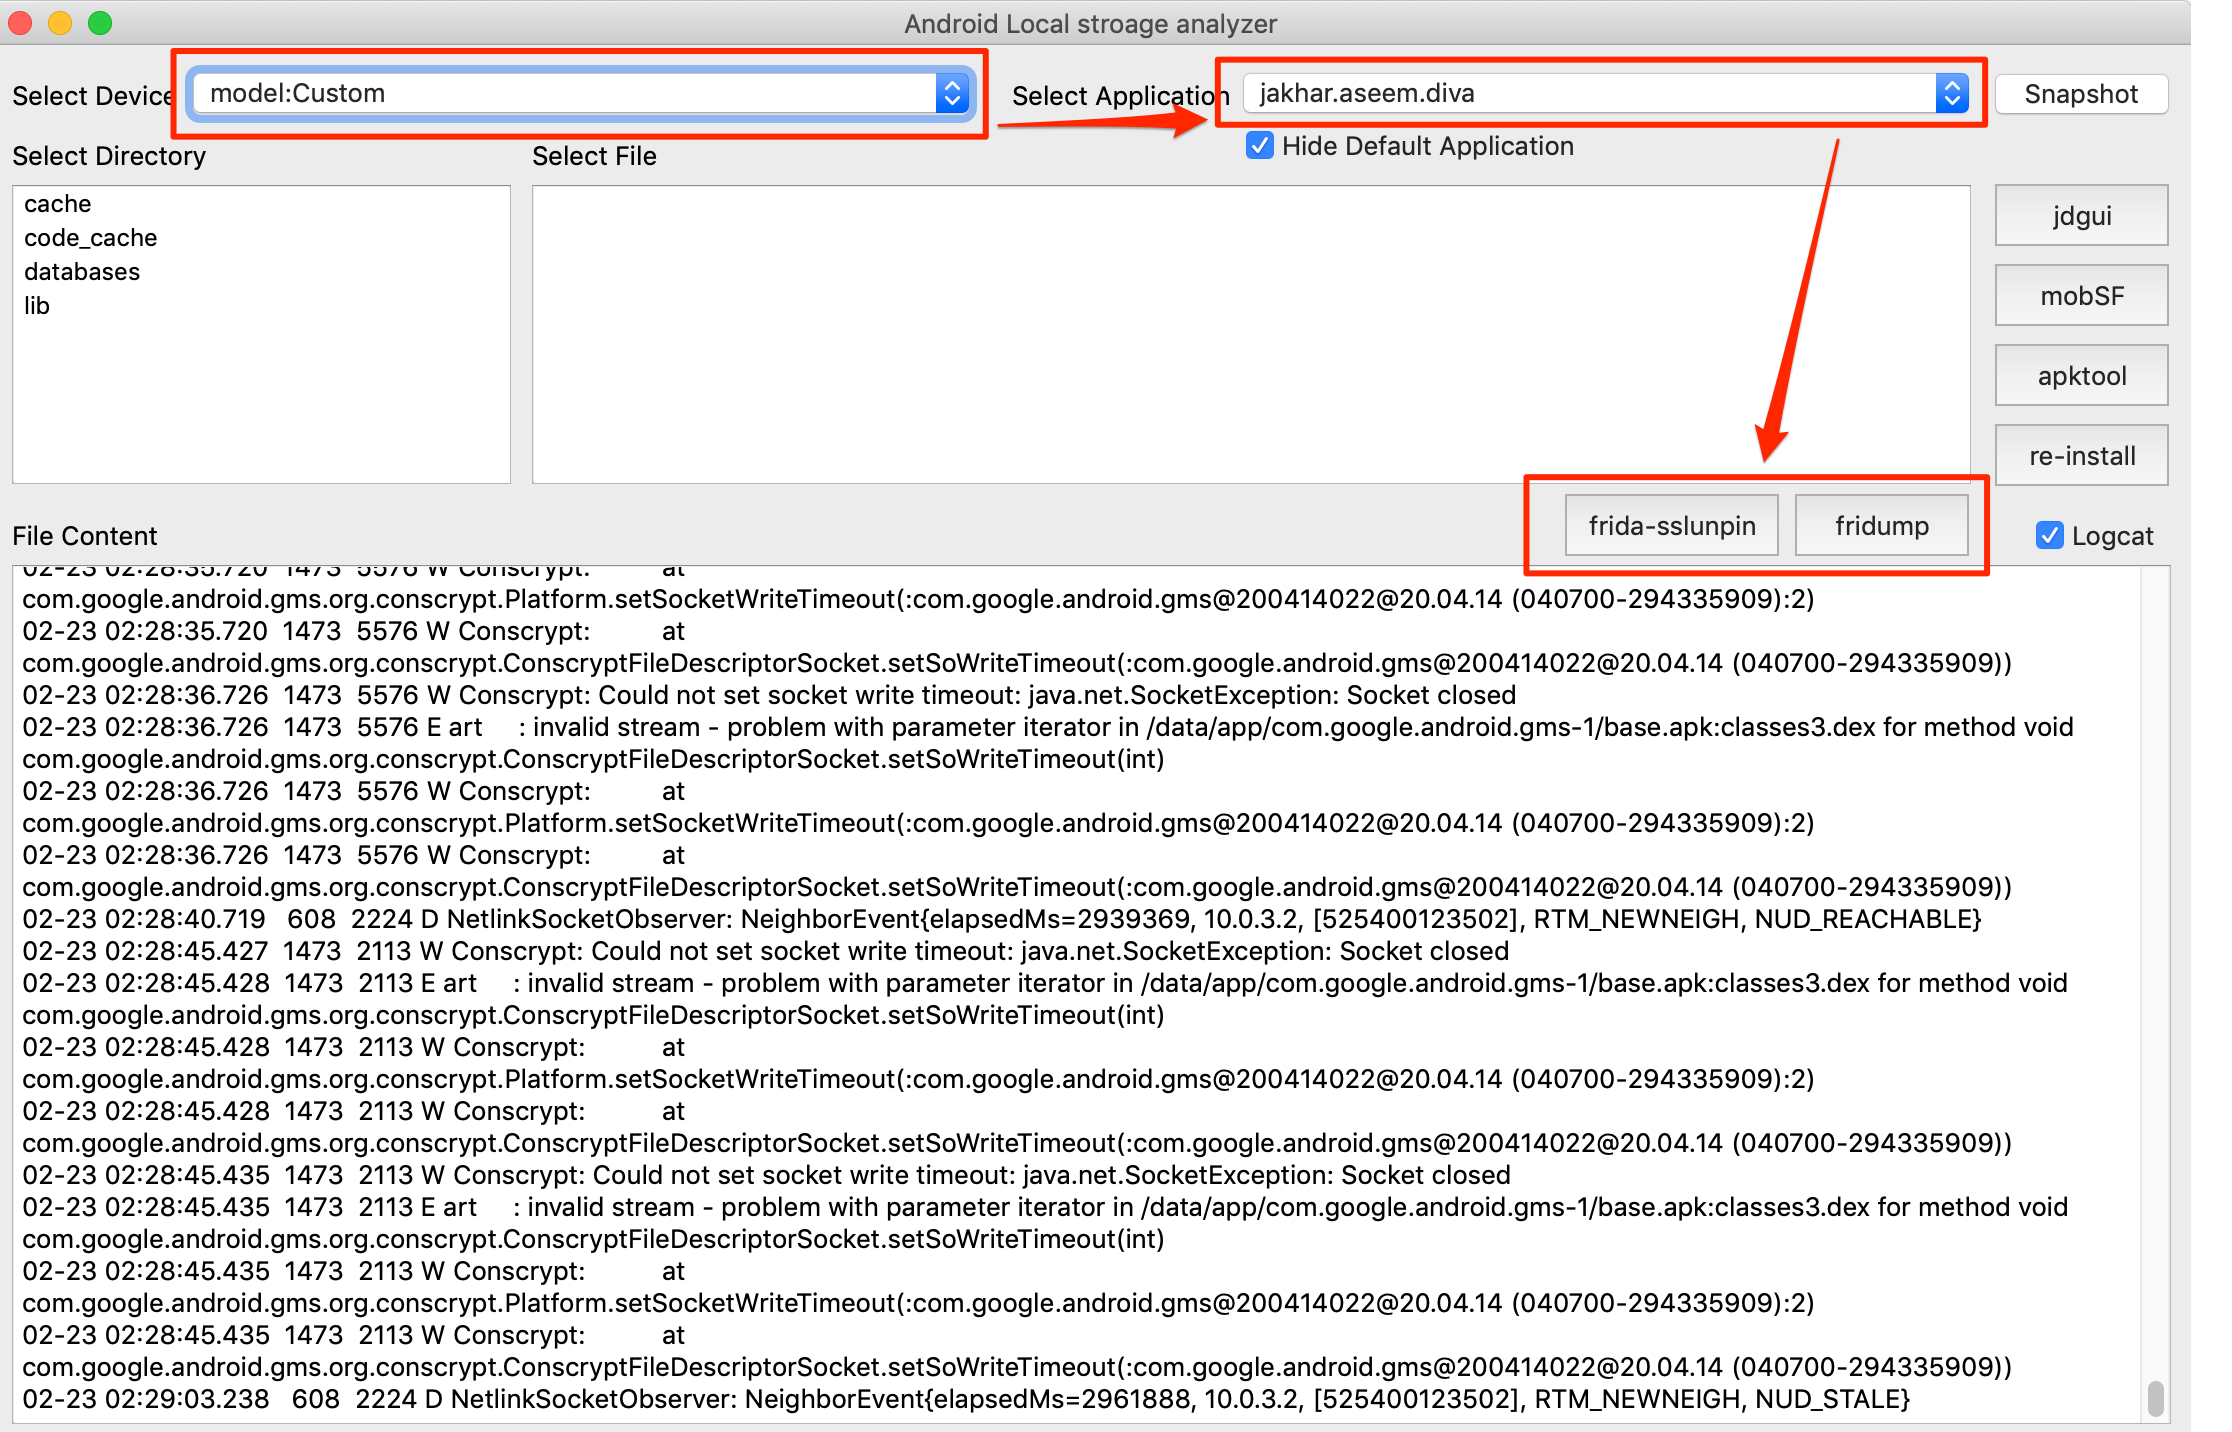 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.

 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…
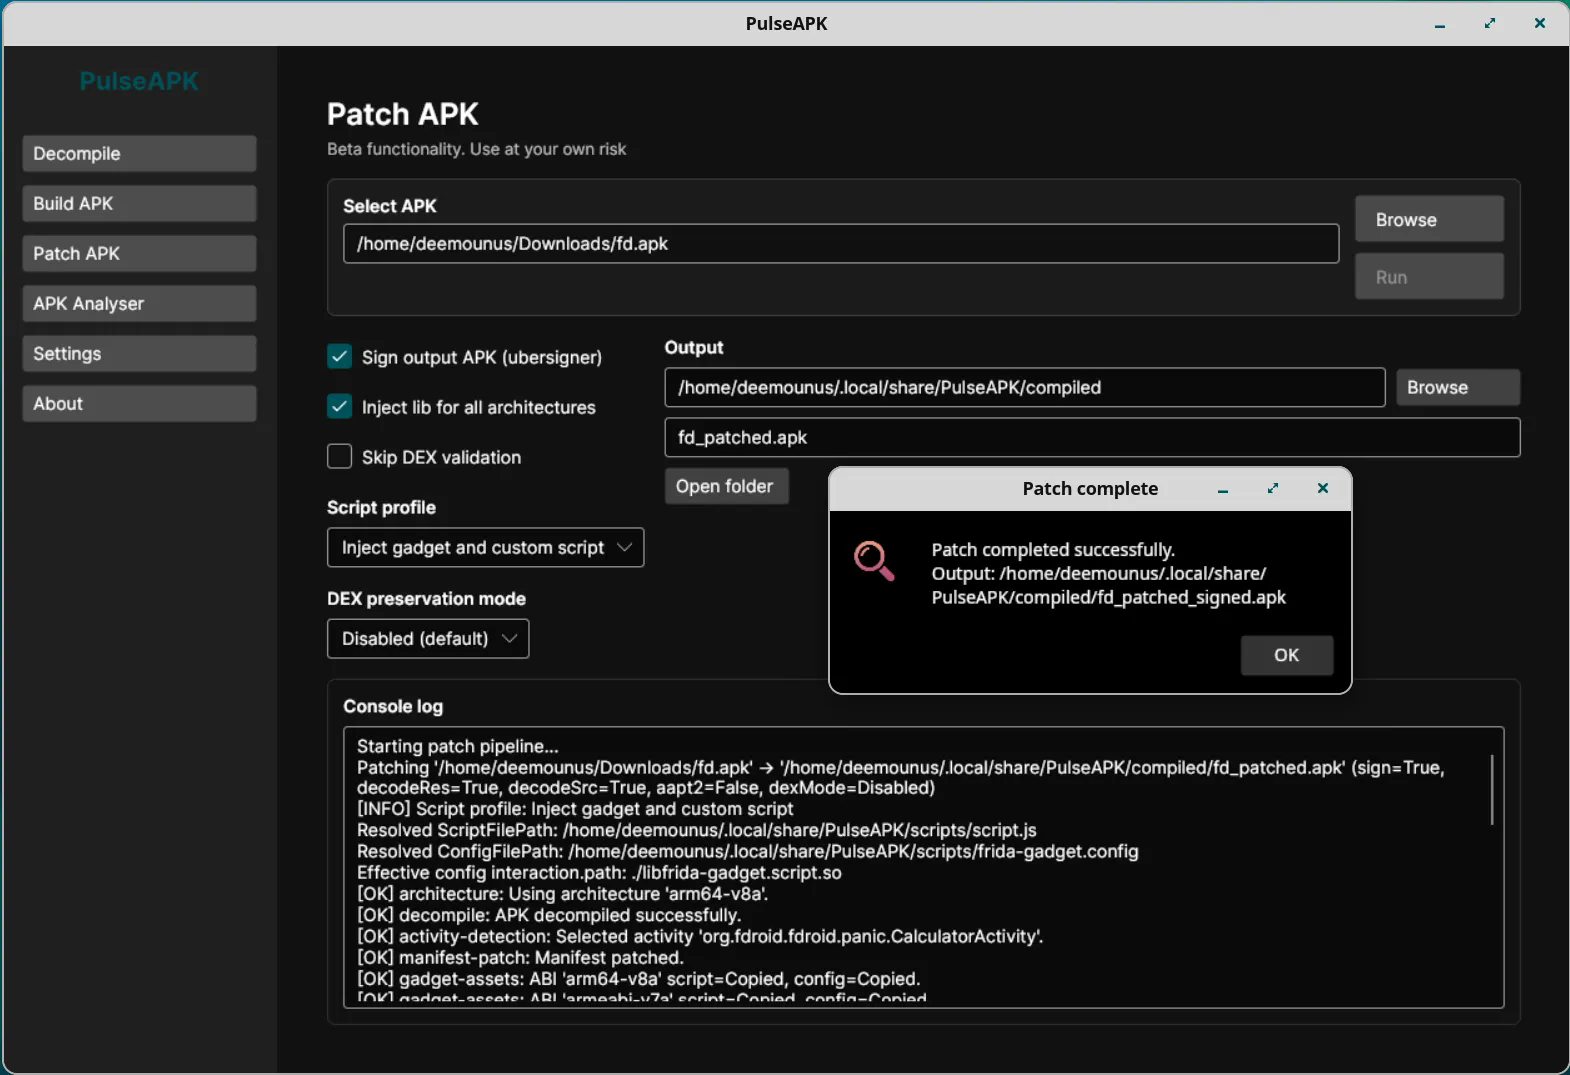 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 nccgroup/assethook
LD_PRELOAD magic for Android's AssetManager
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 ioactive/aosp-exploituserdictionary
PoC Exploit for AOSP UserDictionary Content Provider (CVE-2018-9375)
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
 tea9/cve-2020-0096-strandhogg2
CVE-2020-0096-StrandHogg2 复现