
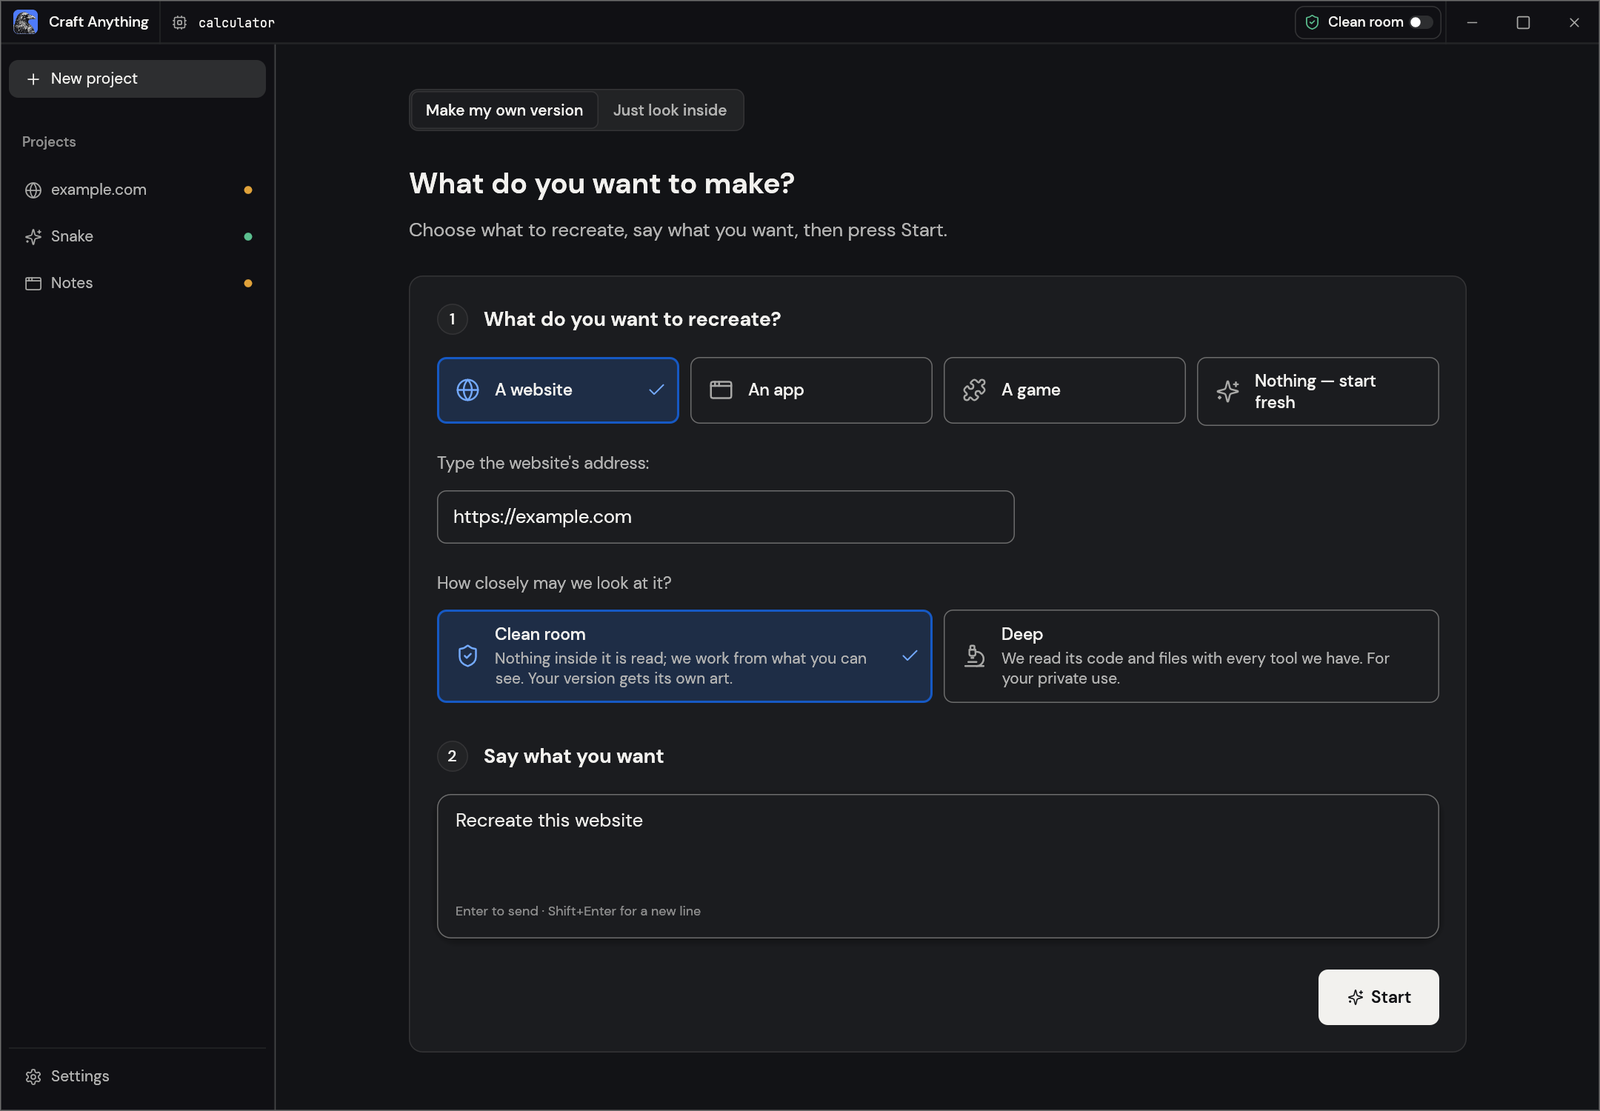
craft-anything
 storytold/craft-anything
Pure-Rust reverse-engineering engine with 314 CLI/MCP inspection tools (disassembly, decompilation, strings, call graphs) that studies any app, site…
ai-assisted-reversingai-securitybinary-analysis+9
4.6k
storytold/craft-anythingPure-Rust reverse-engineering engine with 314 CLI/MCP inspection tools (disassembly, decompilation, strings, call graphs) that studies any app, site…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
 anasfik/flutterguard
Offline security audits for Flutter APKs on Android. Inspect permissions, SDKs, endpoints and potential secrets. No root, account, ads or analytics.
 nowsecure/r2frida
Radare2 and Frida better together.
 androguard/androguard
Reverse engineering and pentesting for Android applications
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 bronils/aotopsy
Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
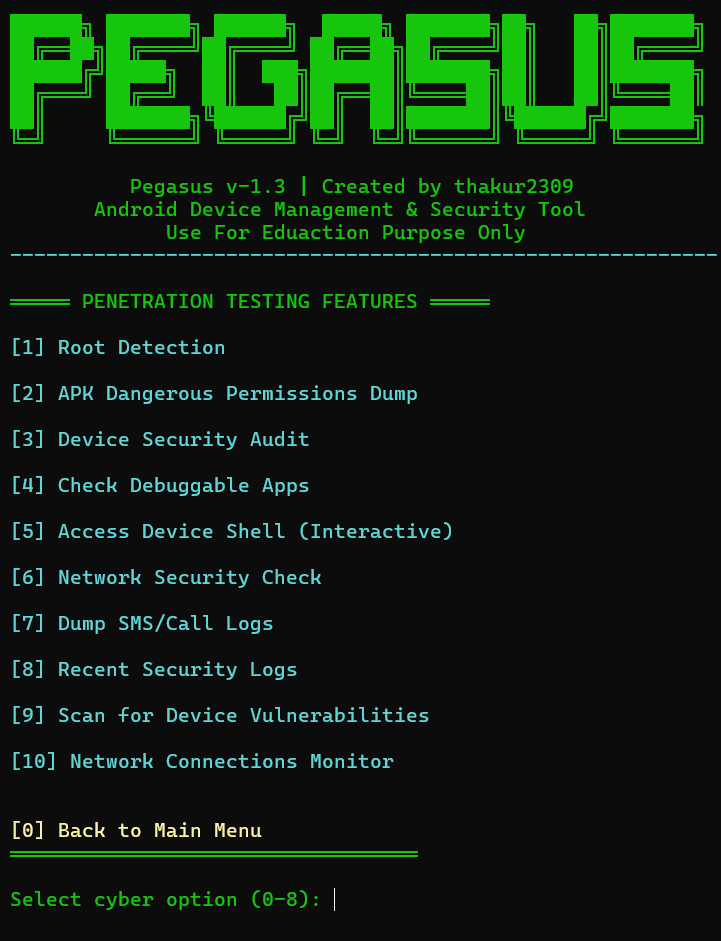 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.
 canyie/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 a0zhar/quarkpoc
iOS Application w/Implementation of CVE-2024-27804
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.