
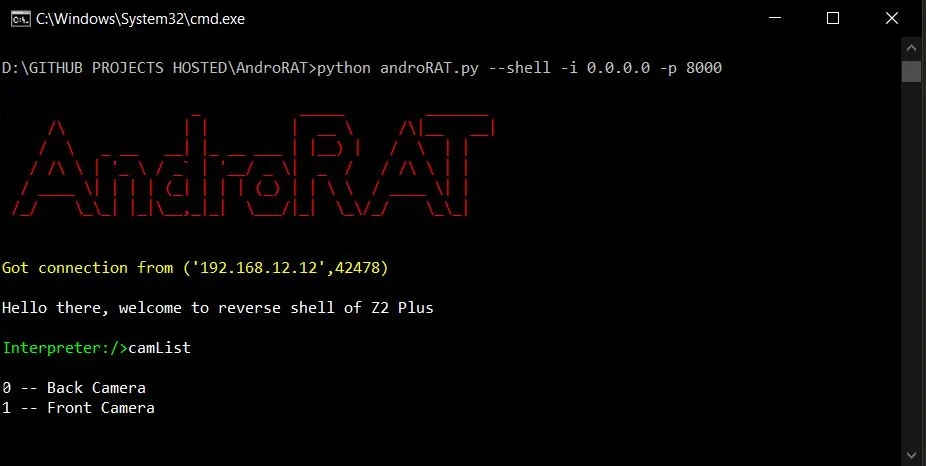
AndroRAT
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
android-securitycommand-and-controldata-exfiltration+7
5.2k
karma9874/androratA Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
 grapheneos/vanadium
Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 deancyl/s9180-rootmygalaxy
RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 rmdycz/k80pro-miro-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for RedMi K80pro miro OS 3.0.304.0