
DFRoot
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
android-securityexploitationmobile-app-pentesting+7
9
a2333c/dfrootAndroid root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
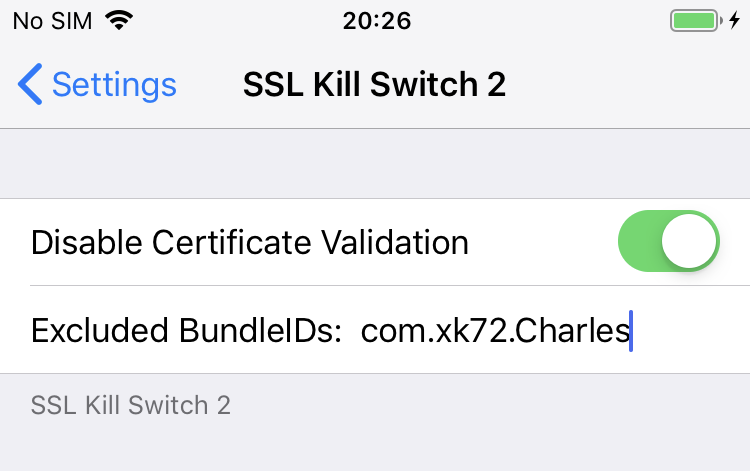 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
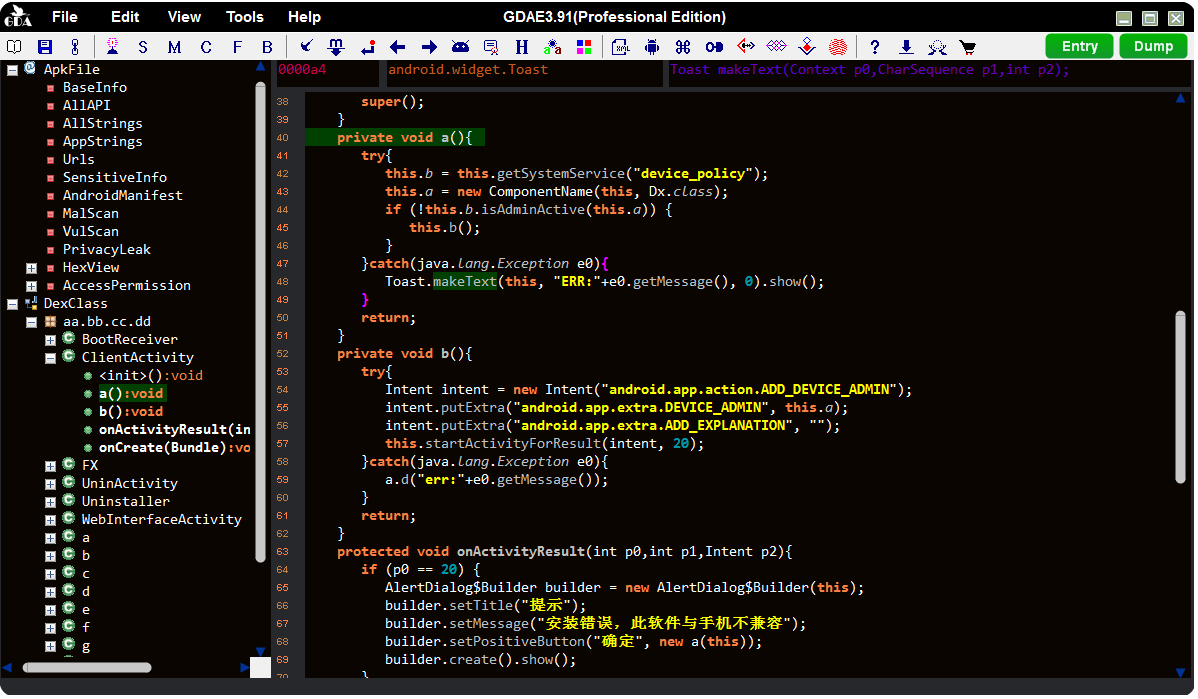 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…