

PhoneSploit-Pro
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
android-securitycommand-and-controldata-exfiltration+7
6.4k
azeemidrisi/phonesploit-proAn all-in-one hacking tool to remotely take over Android devices.
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 frida/frida
Main repo for hosting release binaries
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 xcodeon1/ipa-scope
Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
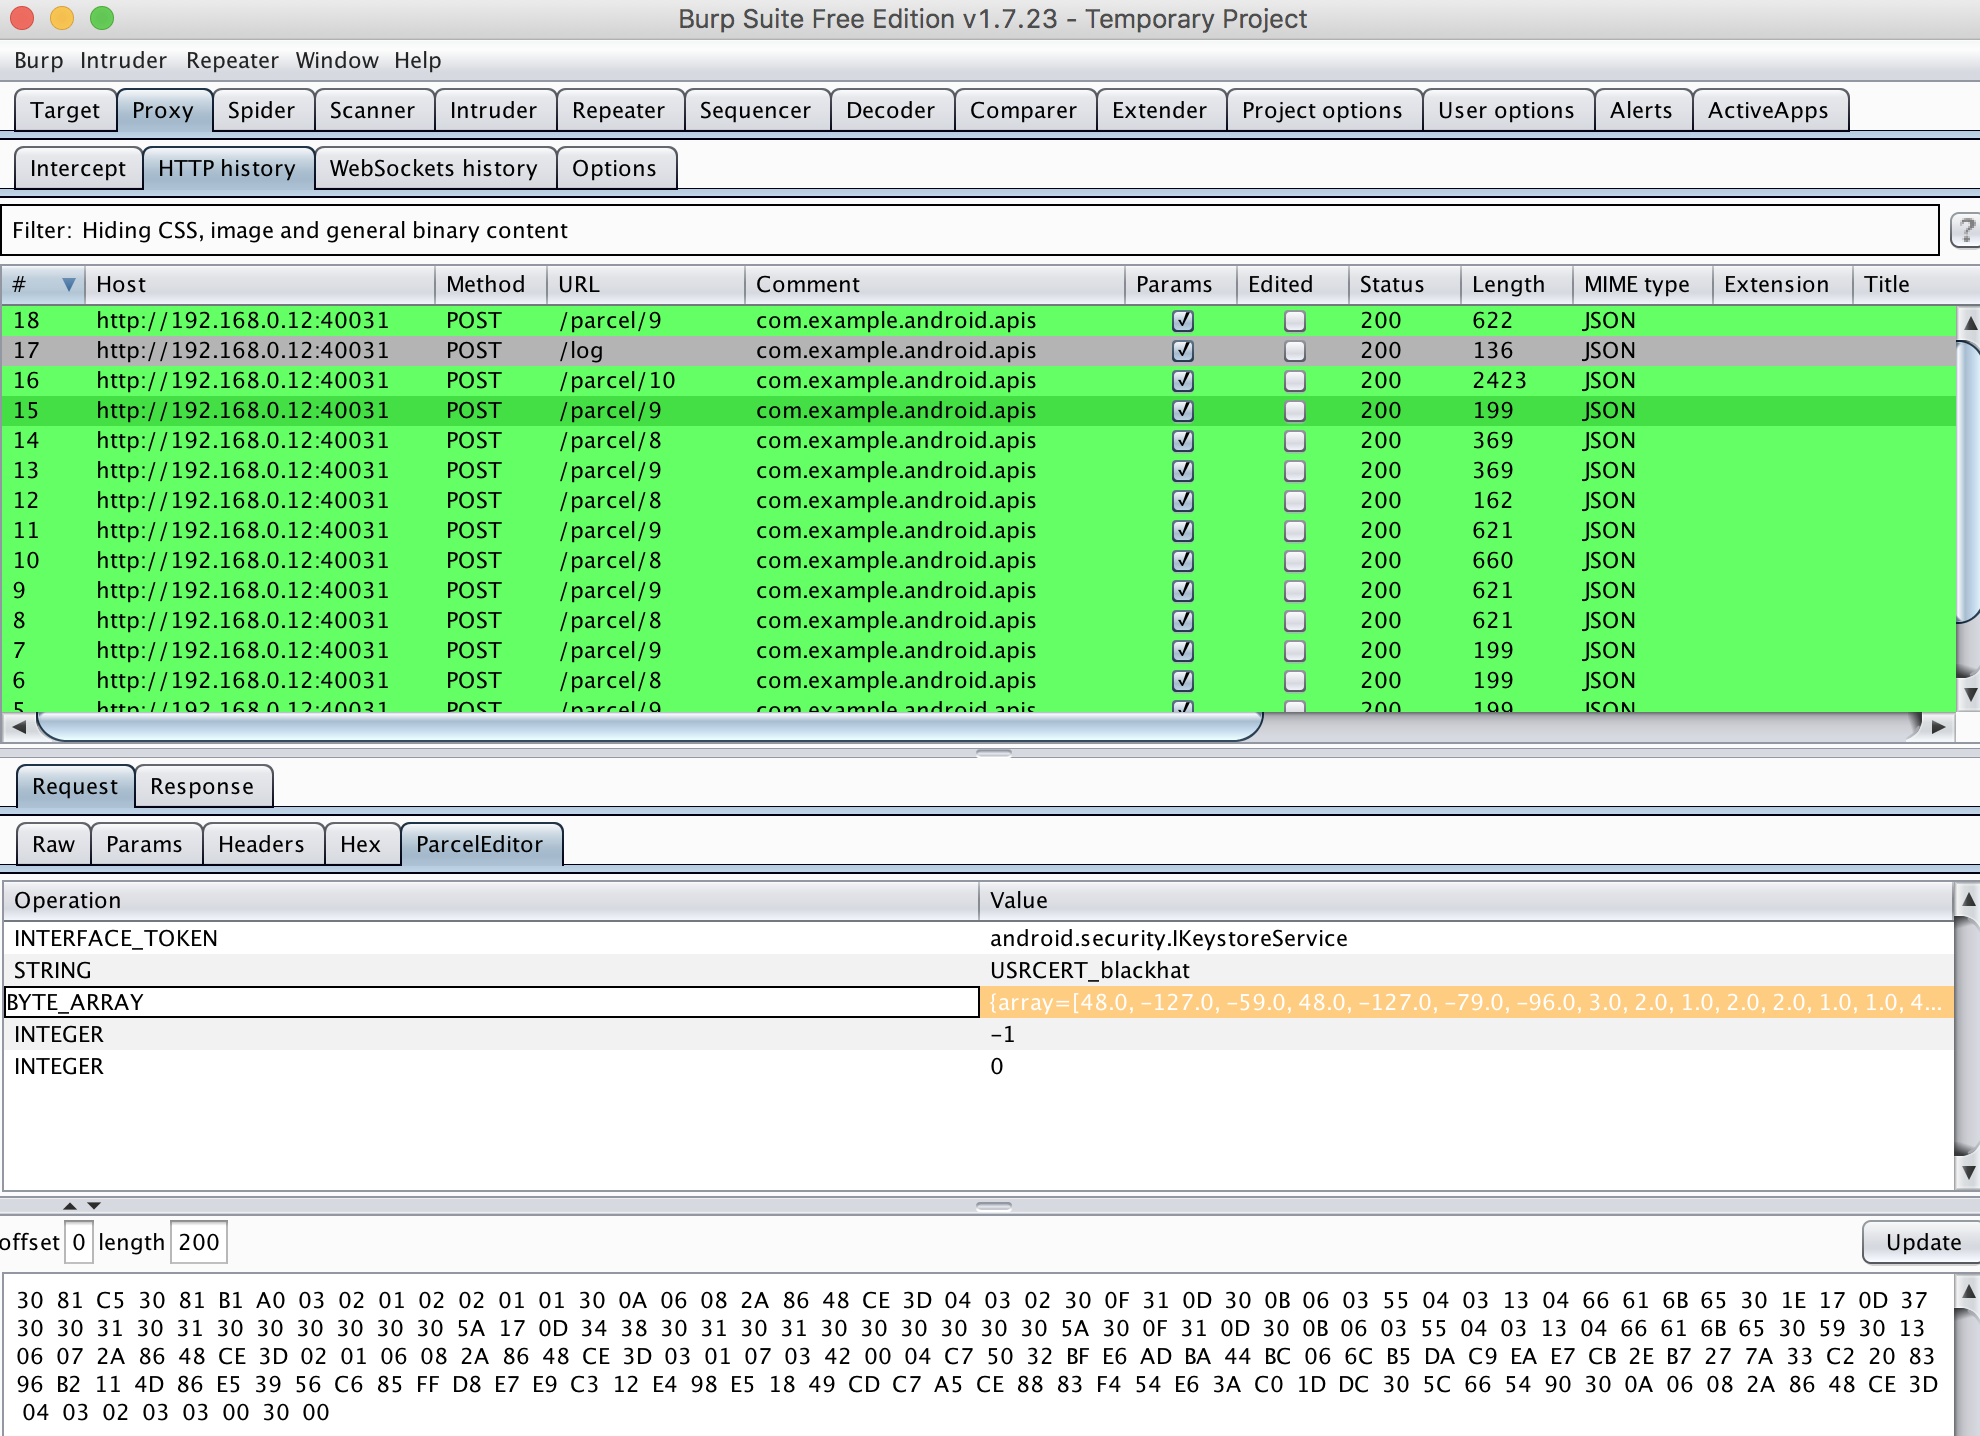 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
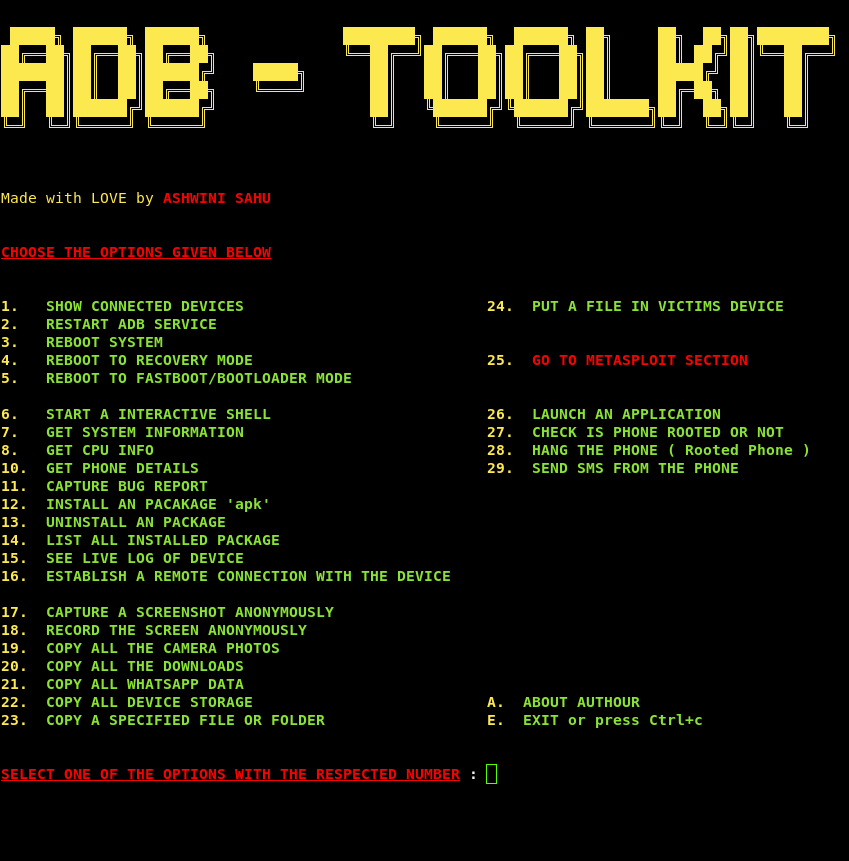 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!