
slythestx
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
android-securitydynamic-analysis-sandboxingios-security+6
14
stuxctf/slythestxMobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
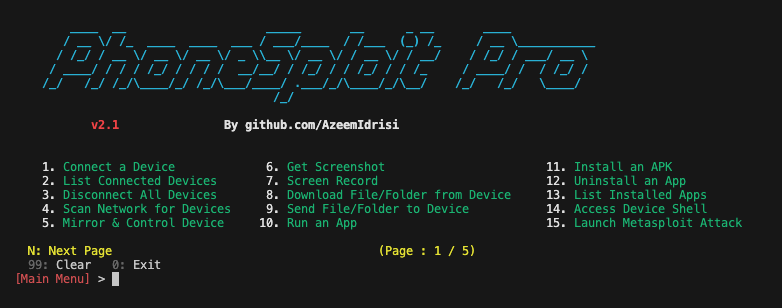 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
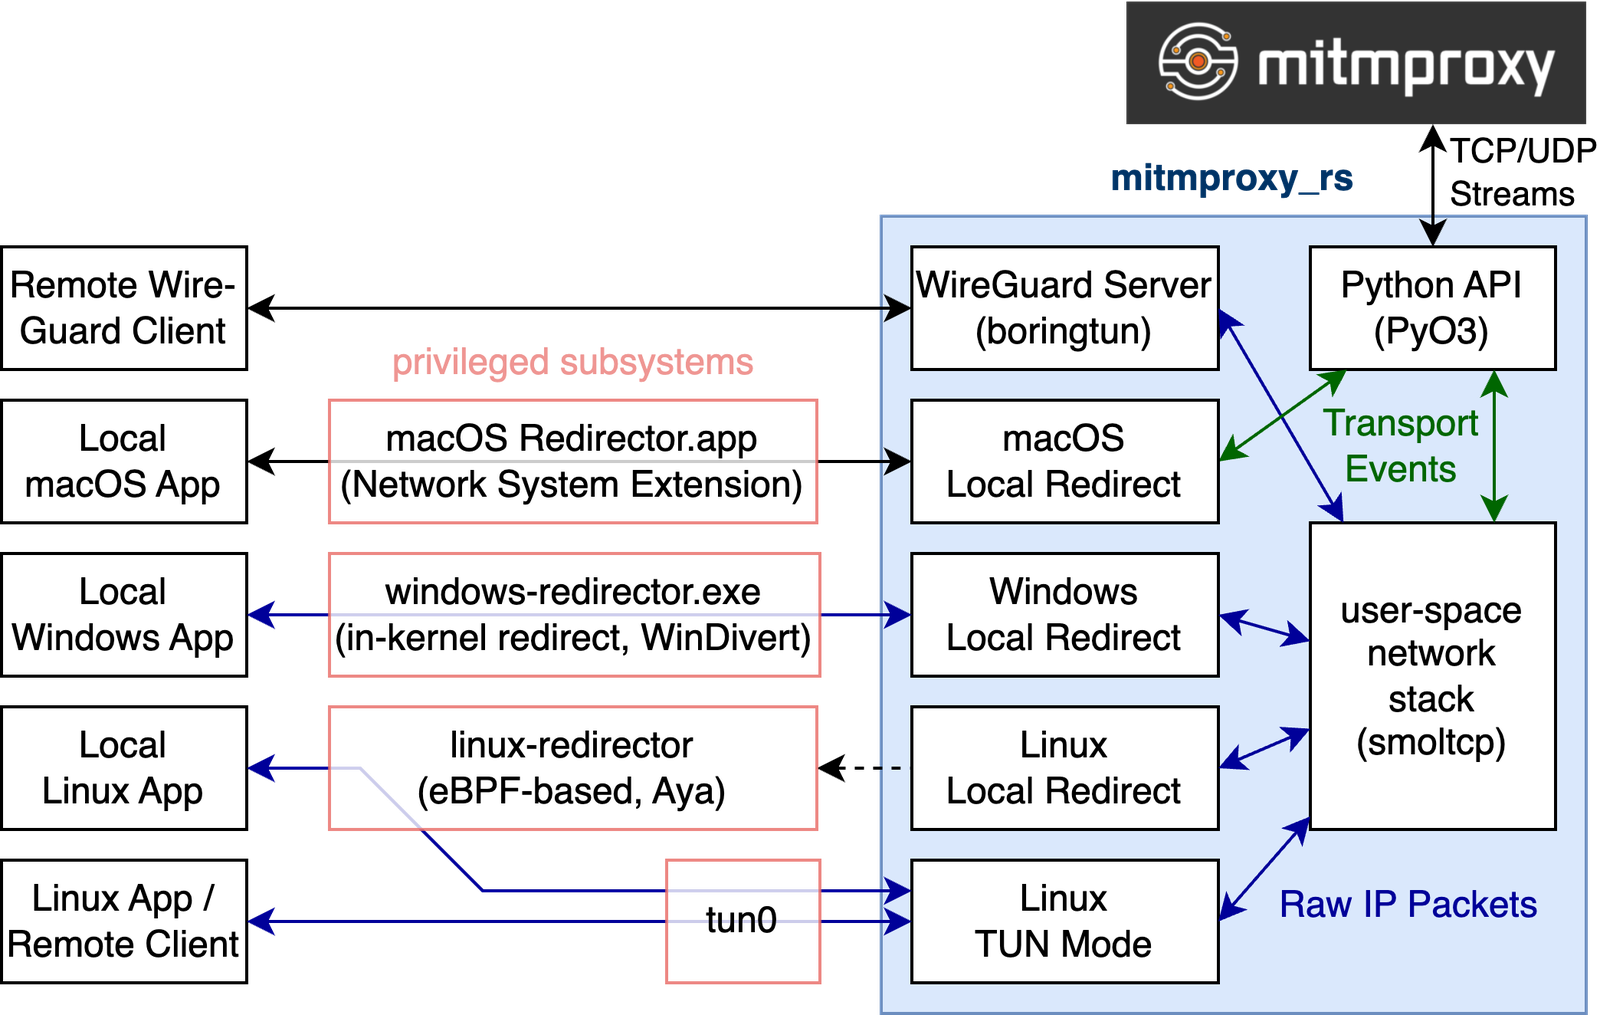 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 frida/frida
Main repo for hosting release binaries
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
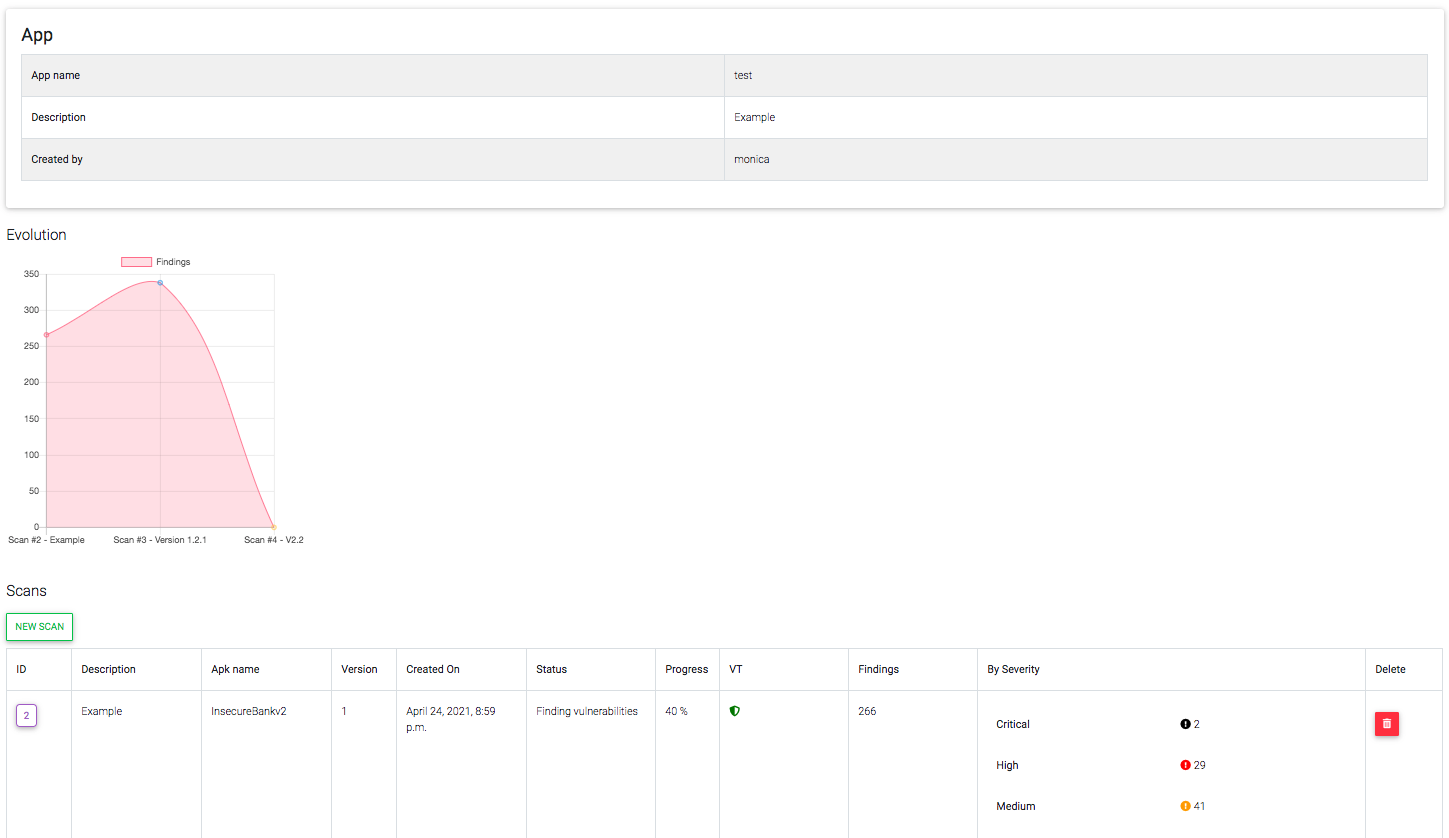 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
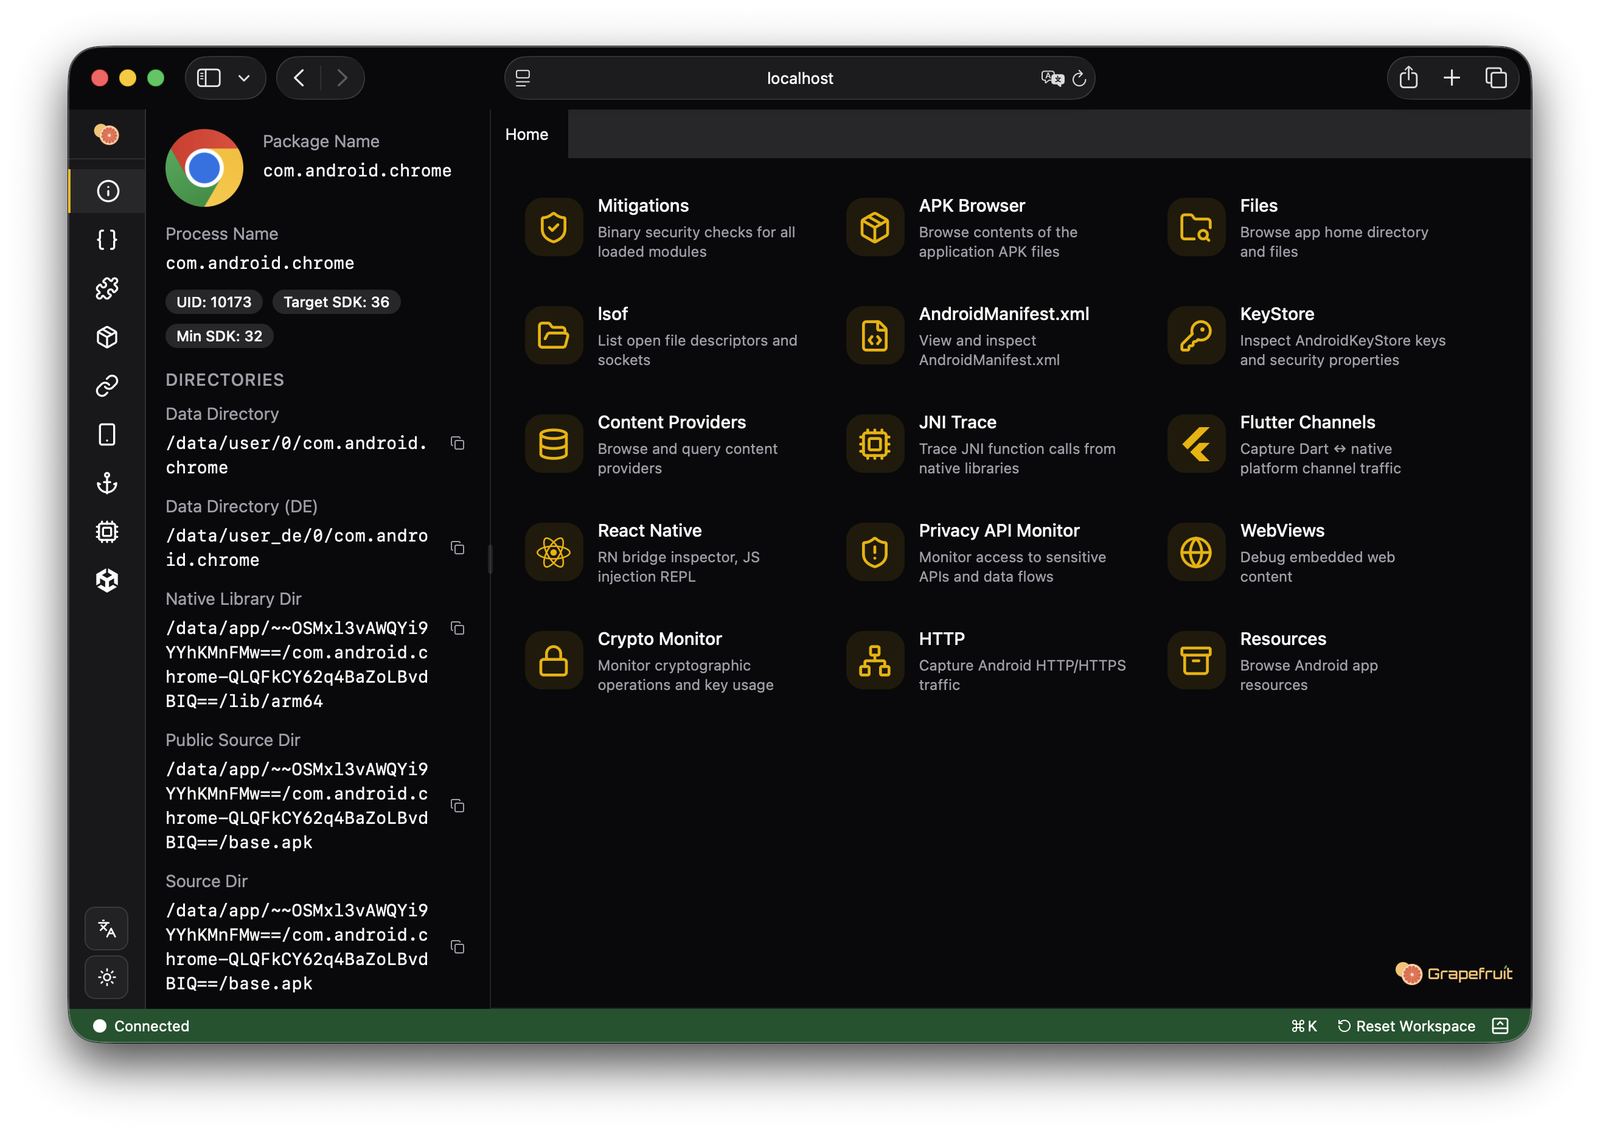 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 quarkslab/android-hardware-attestation-demo
An Android HW Attestation demo
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)