
CVE-2024-26144-test
 gmo-ierae/cve-2024-26144-test
Test tool for CVE-2024-26144 that checks if web servers and CDNs improperly cache HTTP responses containing Set-Cookie headers, revealing cache…
misconfigurationvulnerability-analysisweb-security
gmo-ierae/cve-2024-26144-testTest tool for CVE-2024-26144 that checks if web servers and CDNs improperly cache HTTP responses containing Set-Cookie headers, revealing cache…
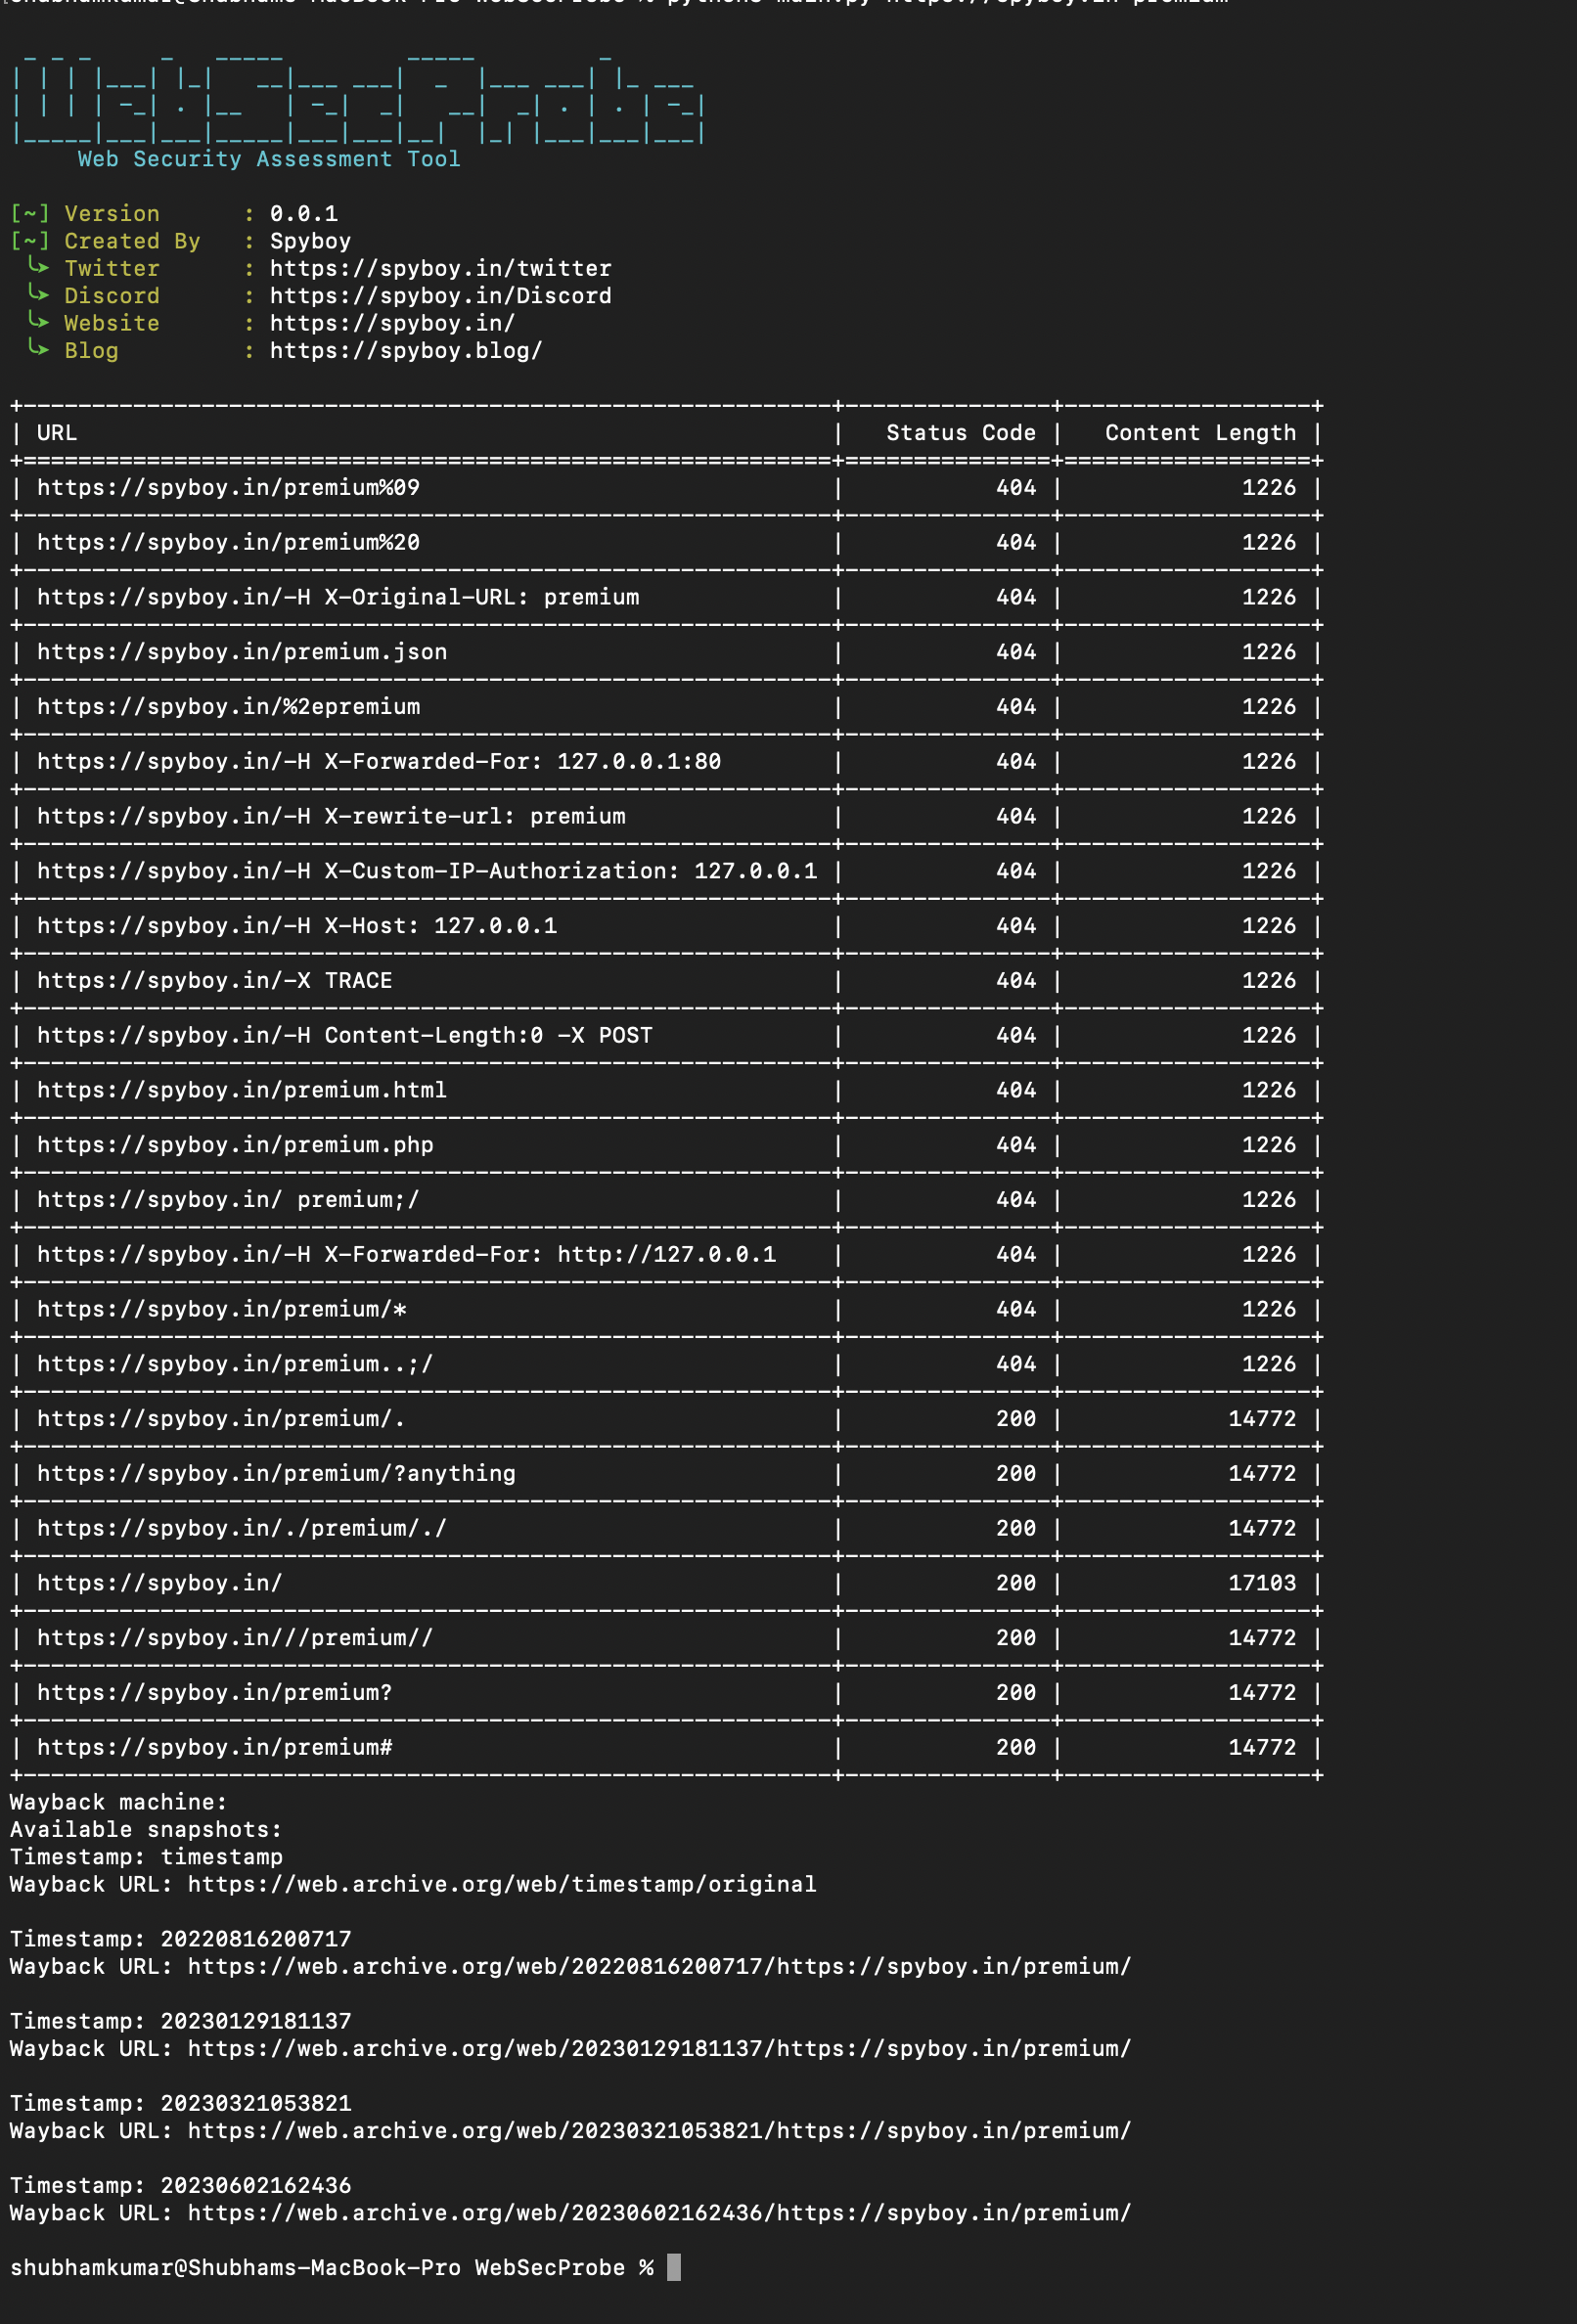 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 trufflesecurity/of-cors
Automated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…
 yousseflahouifi/dbdtct
Python-based scanner that detects debug mode misconfigurations in web applications using multiple HTTP methods and fingerprinting techniques to…
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
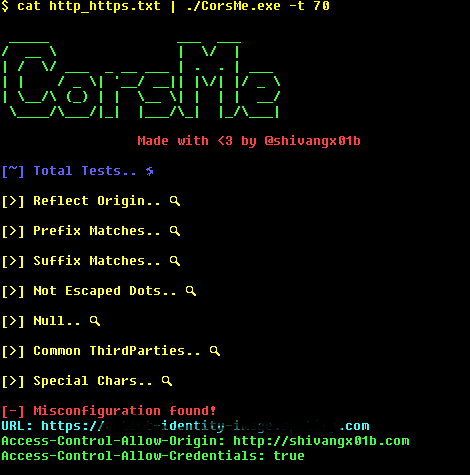 shivangx01b/corsme
Cross Origin Resource Sharing MisConfiguration Scanner
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 raffaele-forte/climber
Check UNIX/Linux systems for privilege escalation
 smaranchand/bucky
Bucky (An automatic S3 bucket discovery tool)
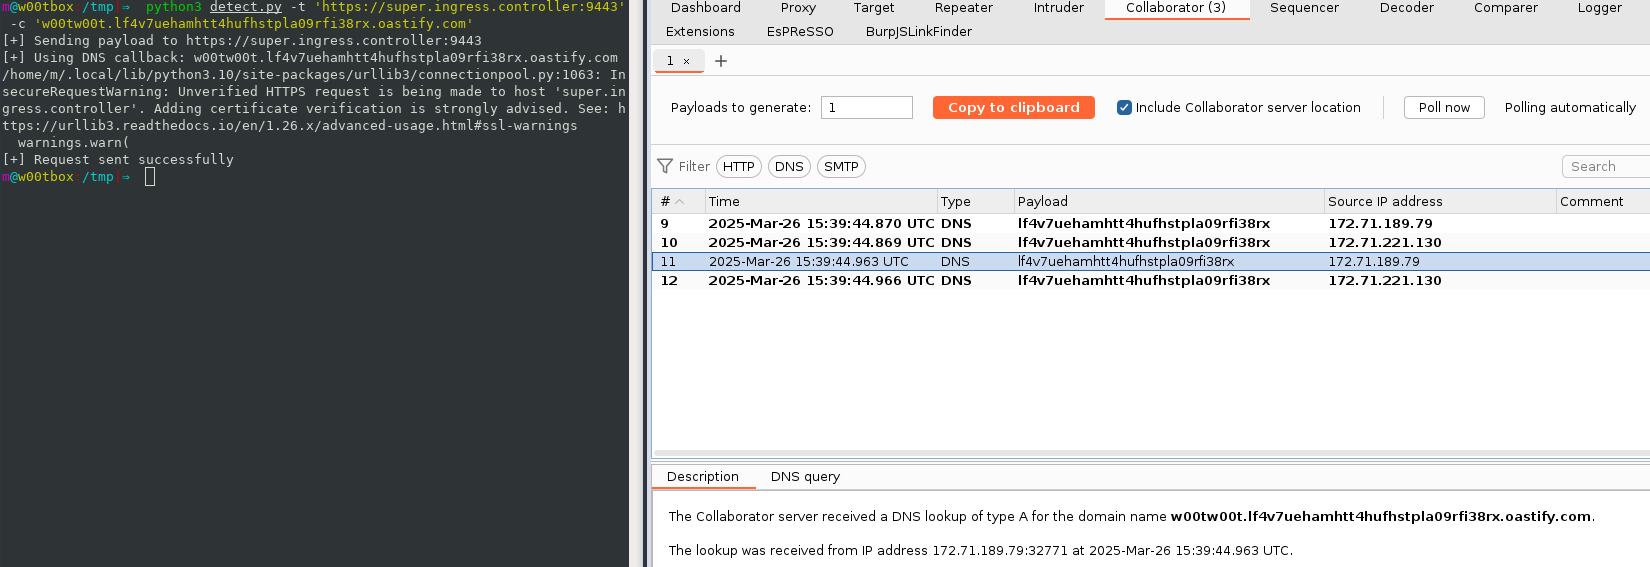 m-q-t/ingressnightmare-detection-poc
Proof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
 nitrado/cve-2017-9798
Checks a shared hosting environment for CVE-2017-9798
 infiniroot/nginx-mitigate-log4shell
Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 hazemkya/cve-2024-3094-checker
Bash script to detect and remediate CVE-2024-3094, a critical supply-chain vulnerability in the XZ Utils library, with automatic safe version…
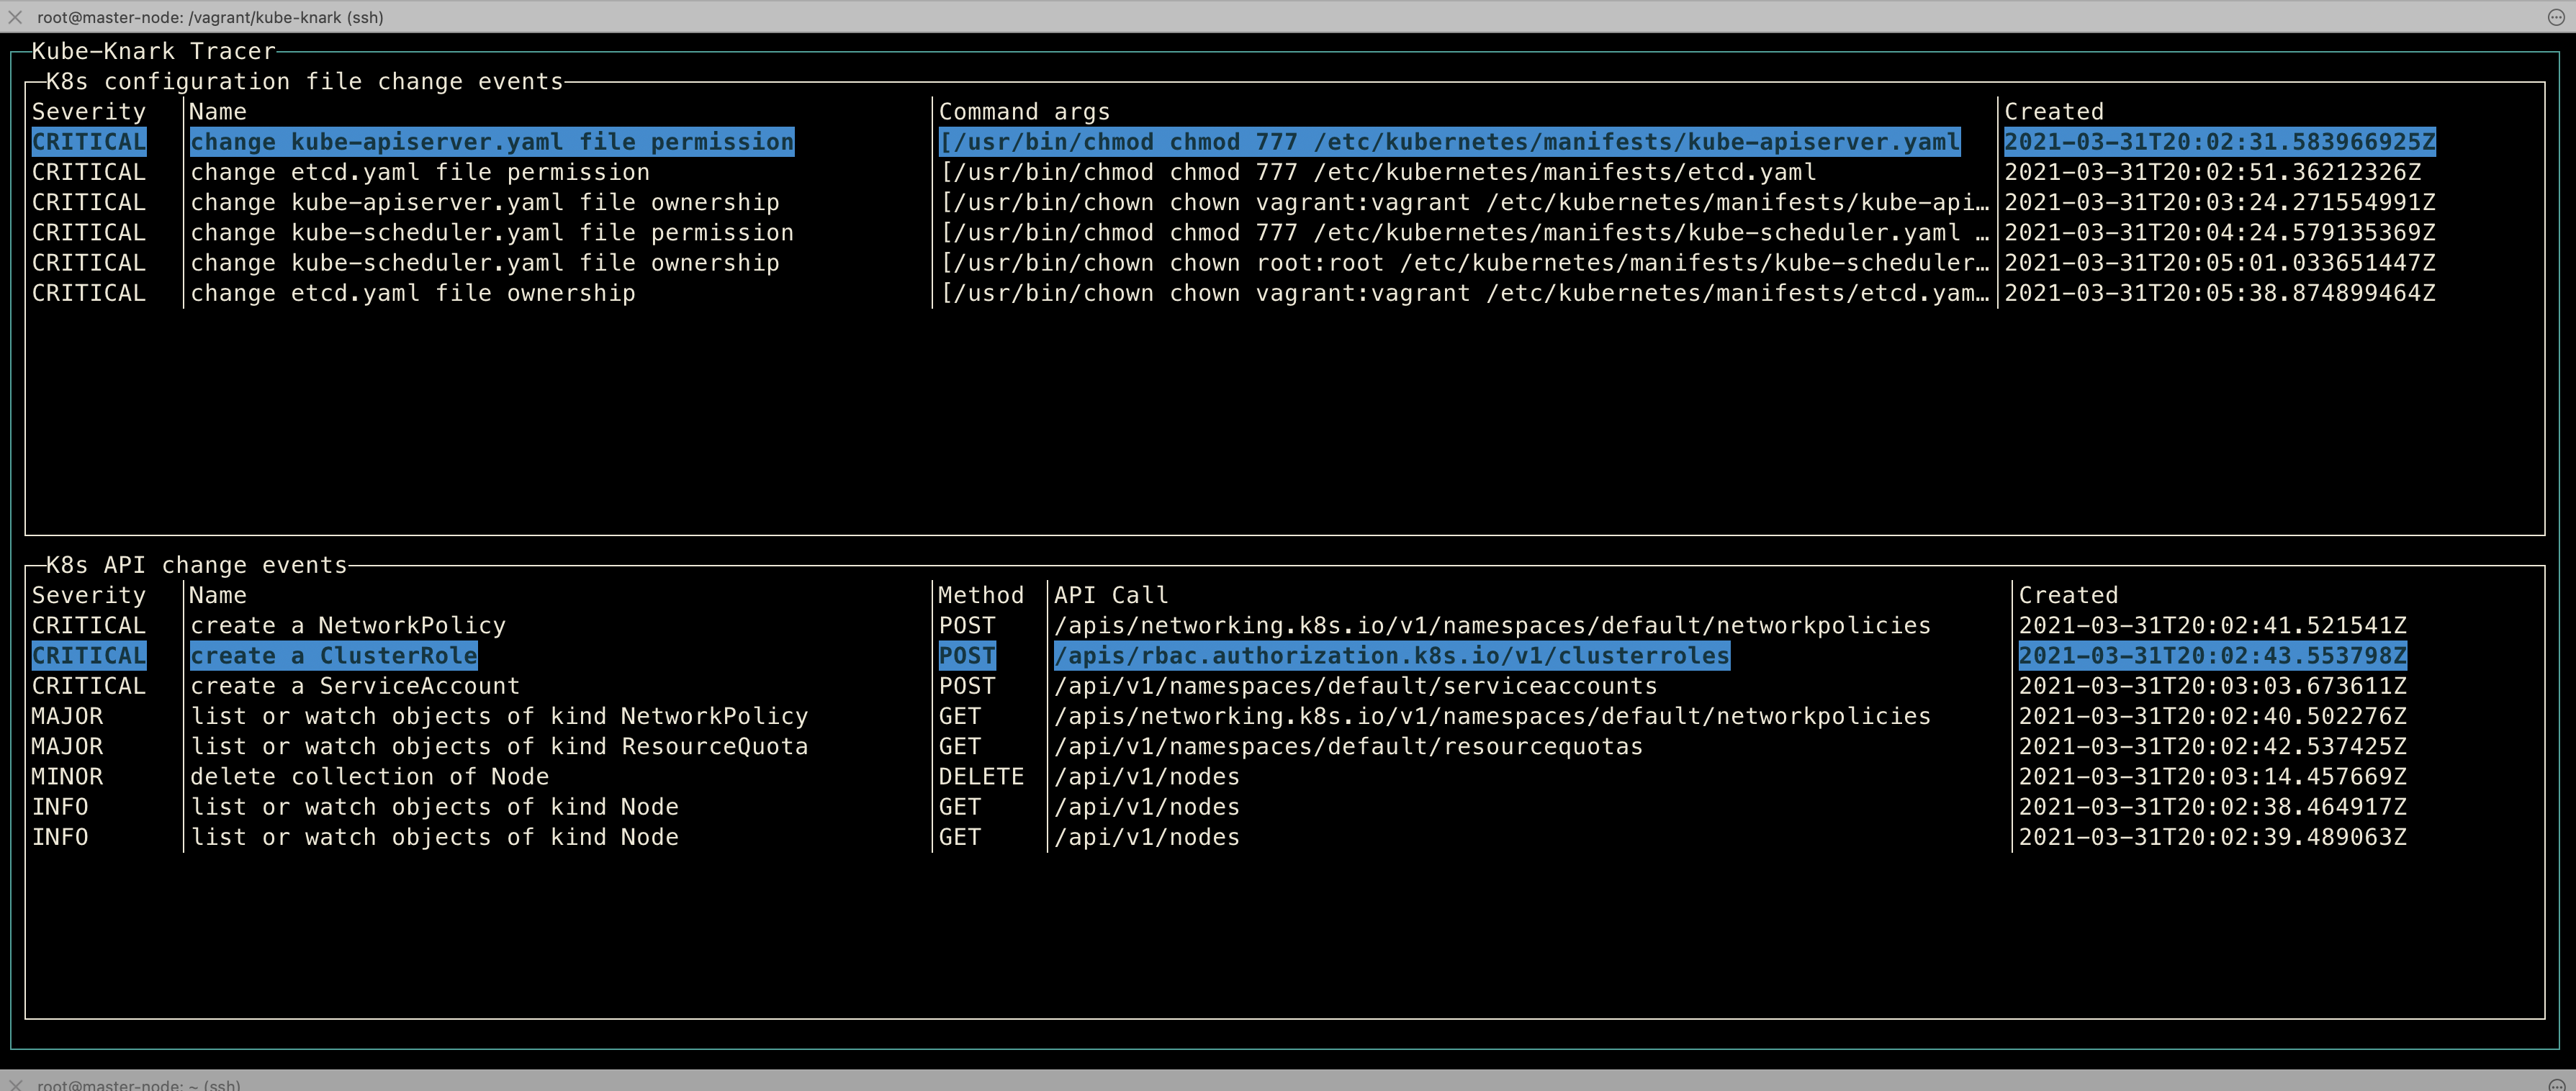 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…