CVE-2024-12252
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
authentication-authorizationexploitationmisconfiguration+5
1
randomrobbiebf/cve-2024-12252SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
 abraxas/ats-realip-plugin-acl
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
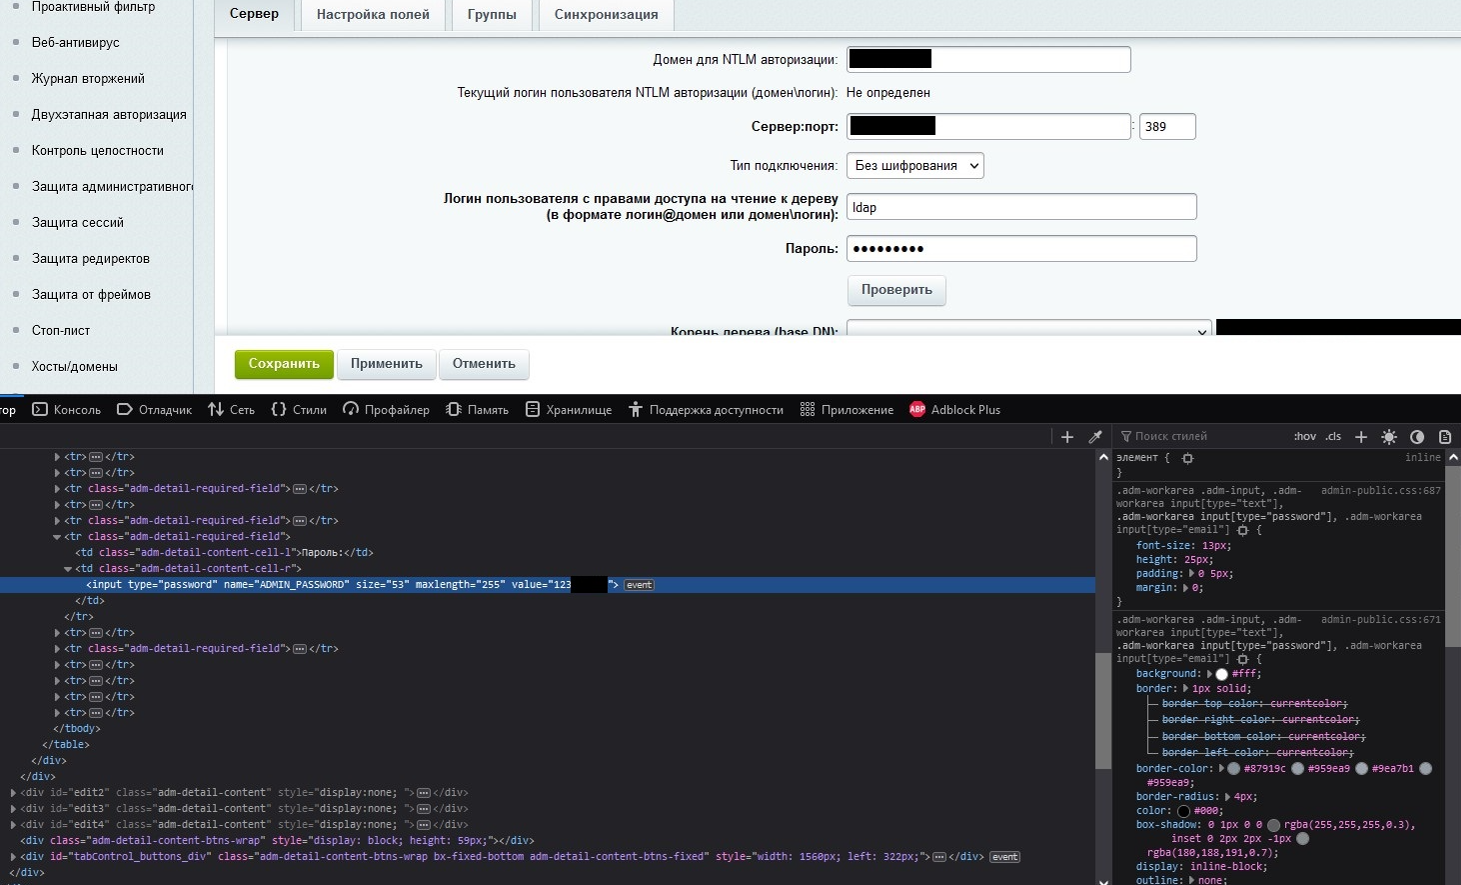 secware-ru/cve-2022-43959
Bitrix Vulnerability CVE-2022-43959
 mirackayikci/cve-2026-55584
CVE-2026-55584 — phpSysInfo IP Allowlist Bypass
 jakehildreth/locksmith
A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 technion/disablesmbcompression
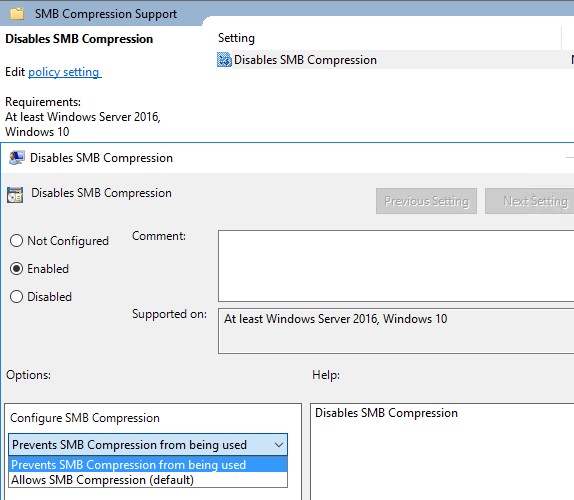
CVE-2020-0796 Flaw Mitigation - Active Directory Administrative Templates
 srlabs/certiception
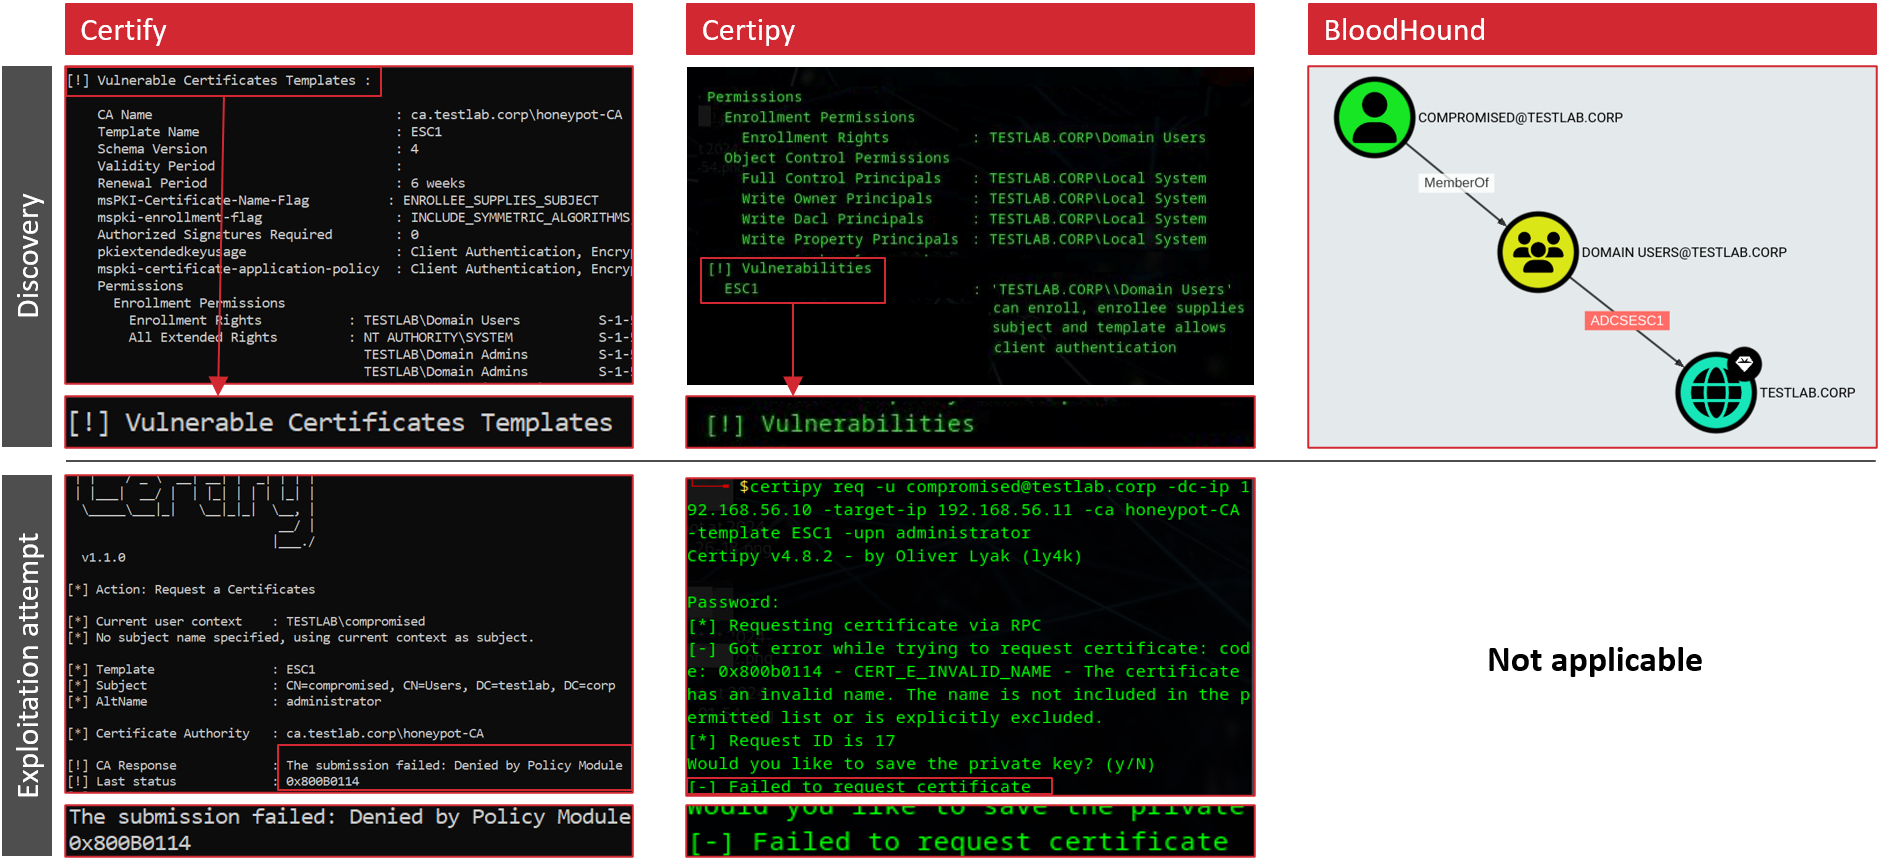
An ADCS honeypot to catch attackers in your internal network.
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 george0papasotiriou/cve-2026-21017-ldap-anonymous-bind-privilege-escalation
Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers