
GPOHound
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
configuration-auditinginformation-gatheringmisconfiguration+4
43121h 24m ago
cogiceo/gpohoundOffensive GPO dumping and analysis tool that leverages and enriches BloodHound data
 frigatecaptain/openclaw_vulnerabilities_and_solutions
> OpenClaw security audit and hardened deployment guide — known vulnerabilities (CVE-2026-25253, malicious skills, credential leakage), architectural…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 semonte/sisu
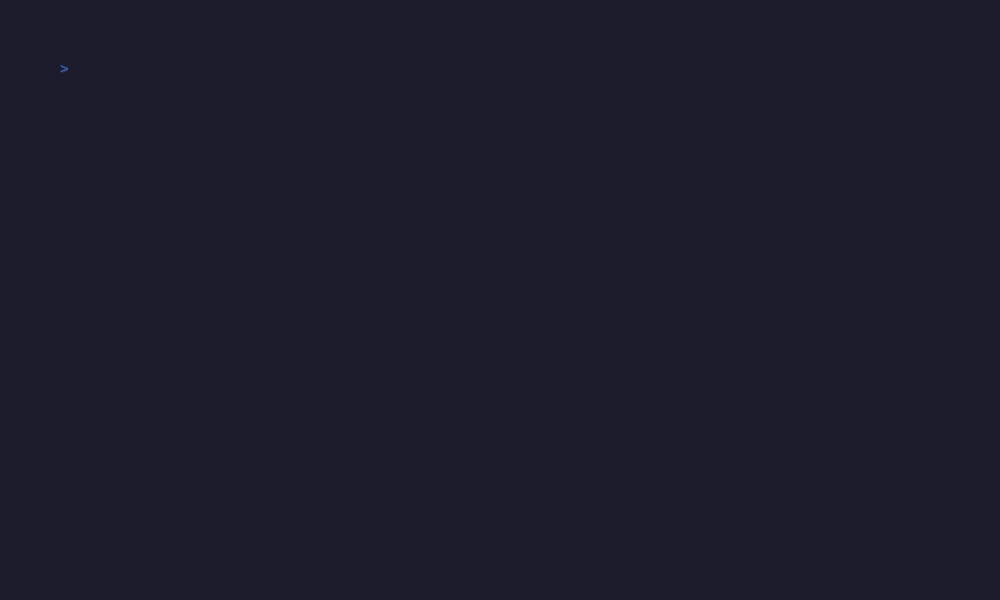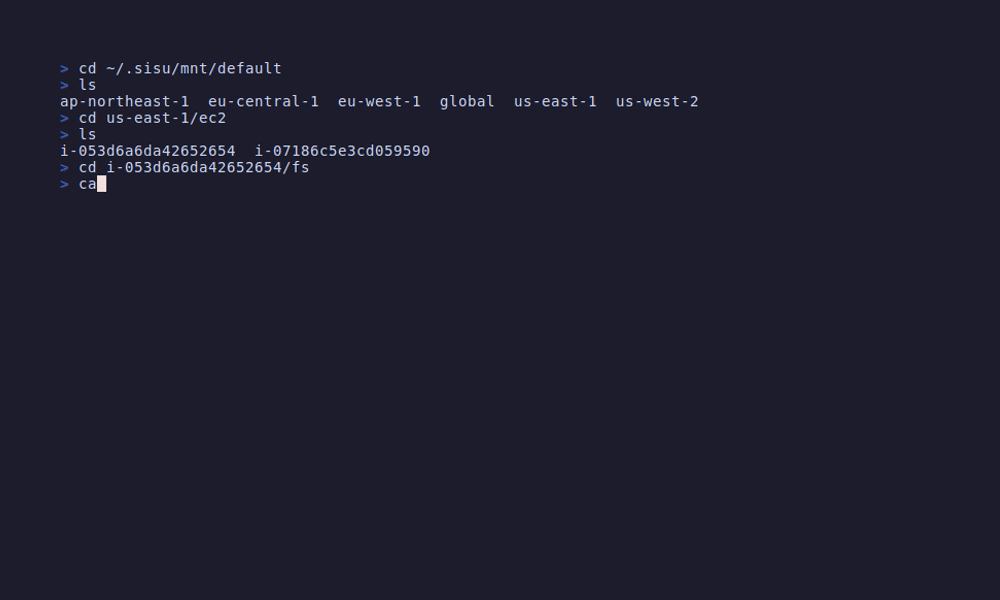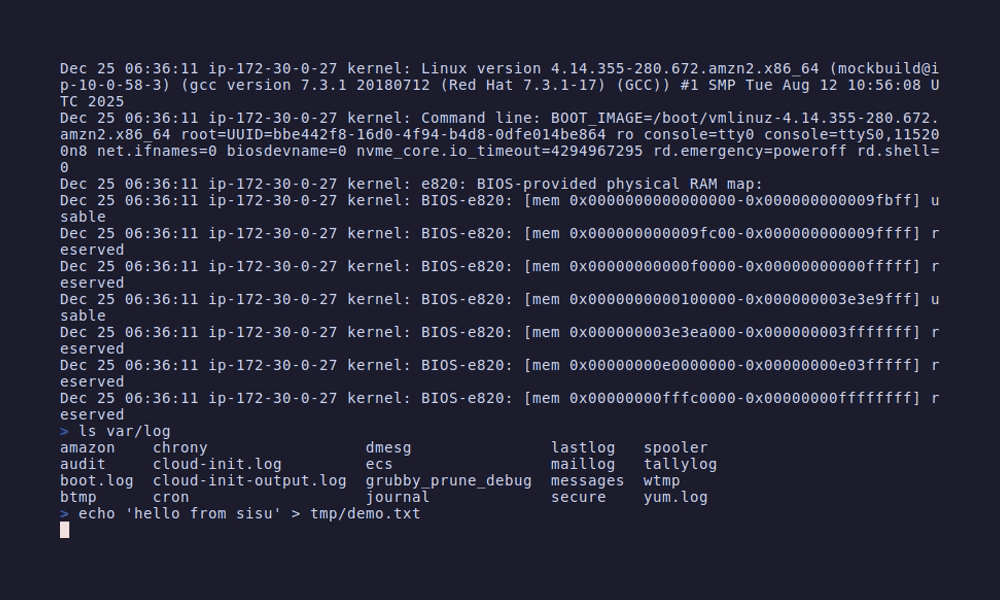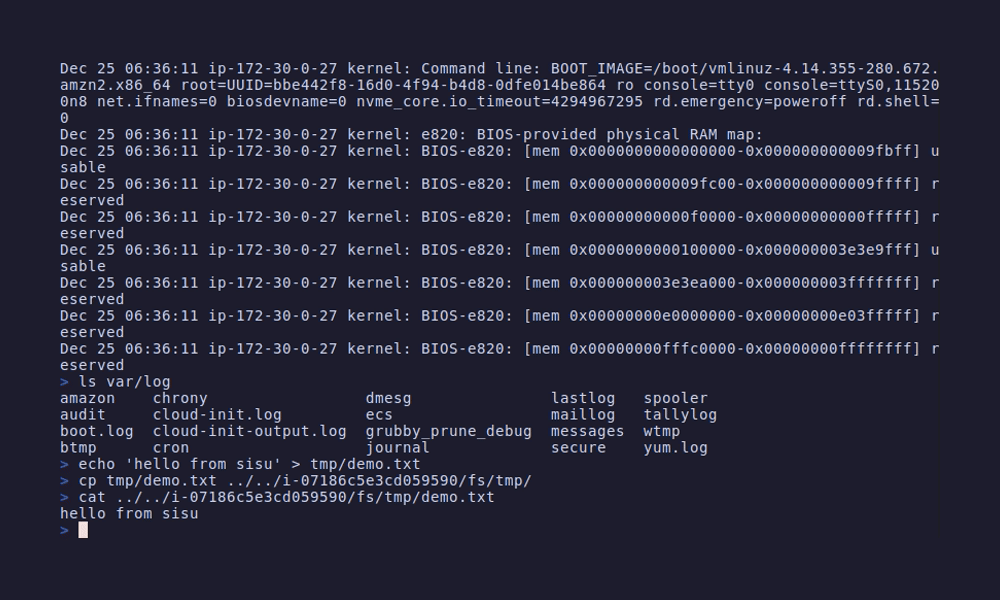
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
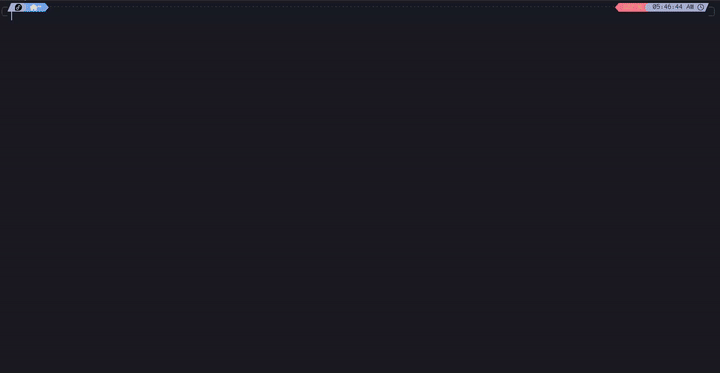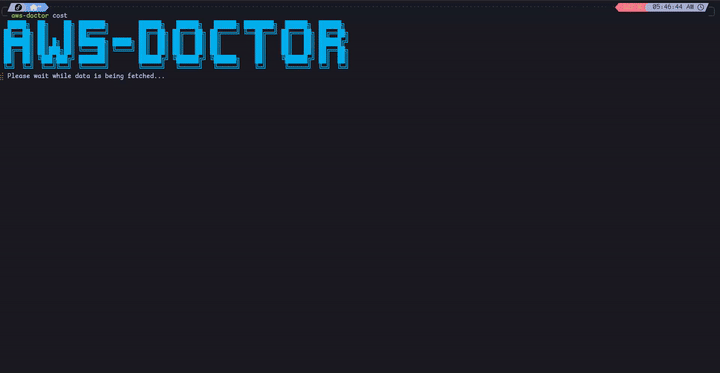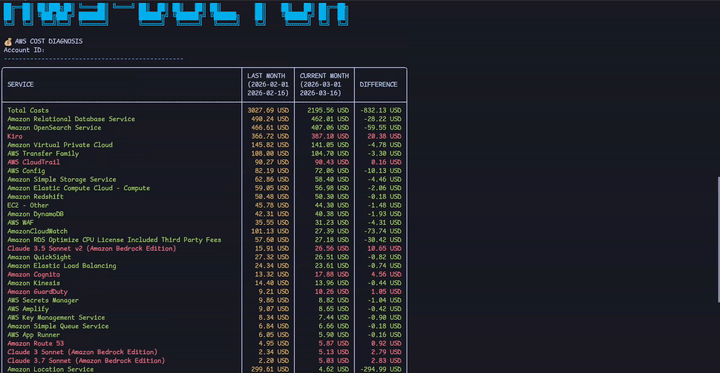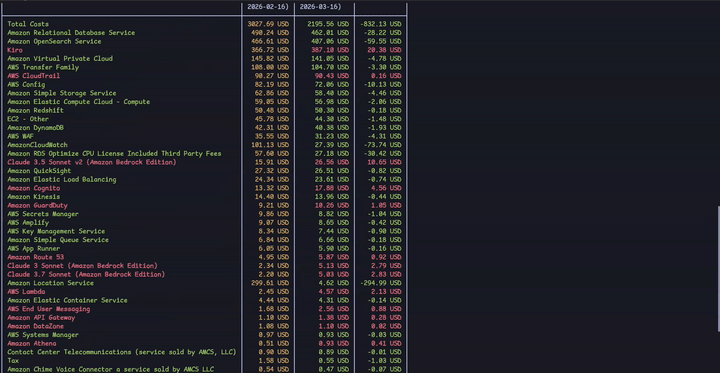 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
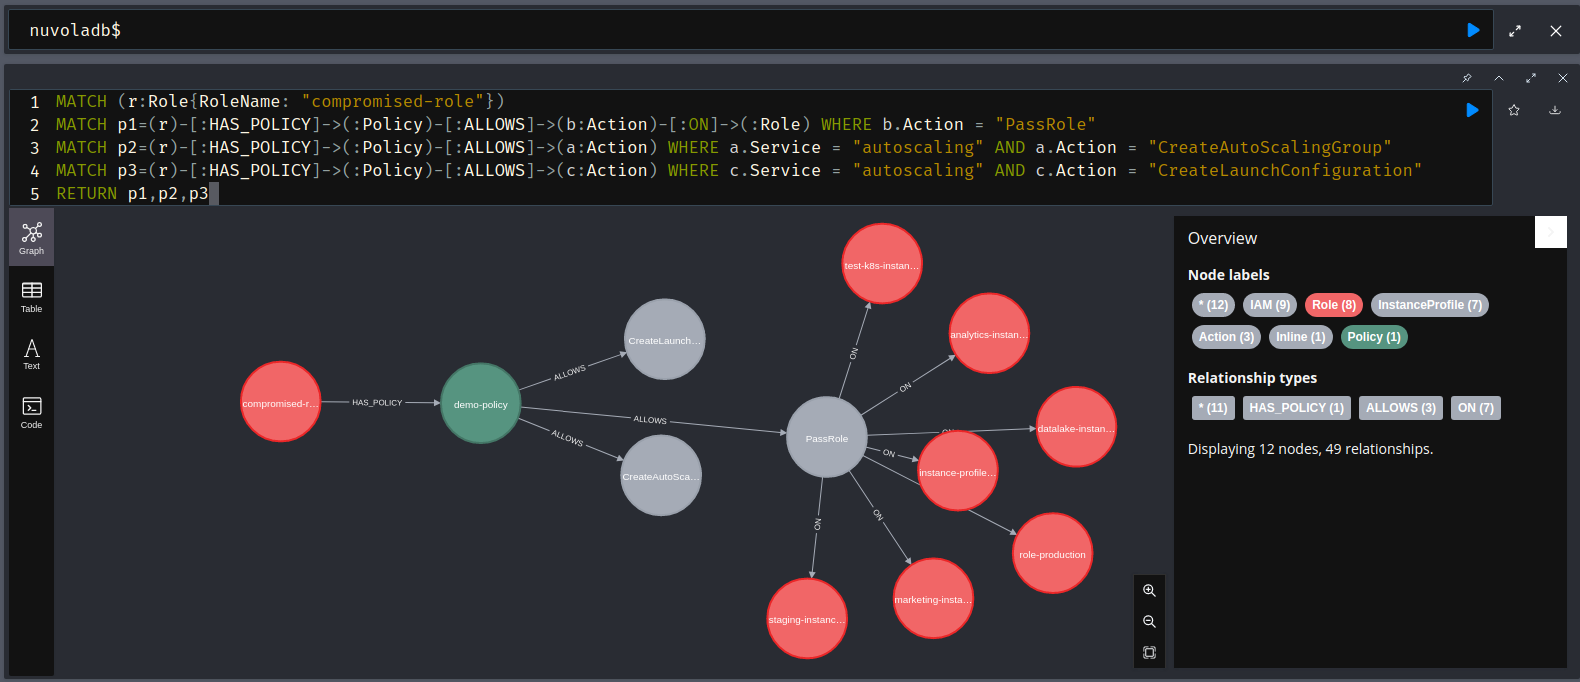 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 git-akki/cso-vibecheck
Senior-CSO security audit skill for vibe-coded apps. 22-check audit anchored to real 2026 incidents (Moltbook, Lovable CVE-2025-48757). Drop-in…
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 califio/ngxray
ngxray — nginx config security scanner
 tlwebdesign/joomla-3.10.12-languagehelper-hotfix
Plugin to fix security vulnerability CVE-2023-40626 in Joomla 3.10.12