
pypykatz
 skelsec/pypykatz
Mimikatz implementation in pure Python
authenticationdigital-forensicsencryption-decryption-tools+4
skelsec/pypykatzMimikatz implementation in pure Python
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 manhndd/cve-2019-19012
Integer overflow in Oniguruma
 tarantula-team/cve-2019-19012
An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
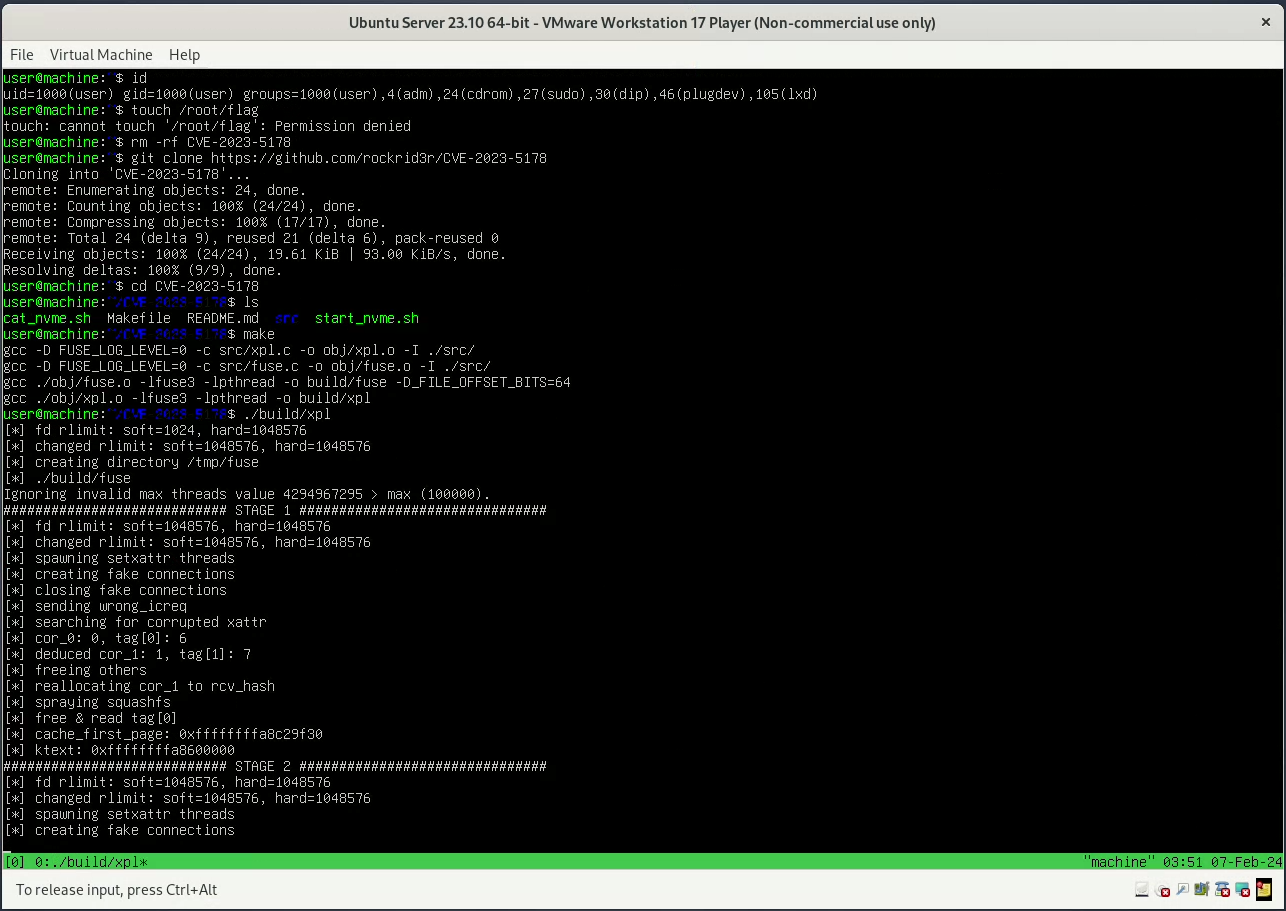 rockrid3r/cve-2023-5178
Exploit for CVE-2023-5178
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 0xatharv/cve-2025-40019-poc
A Proof Of Concept for CVE-2025-40019
 bazad/ctl_ctloutput-leak
CVE-2017-13868: Information leak of uninitialized kernel heap data in XNU.
 maldiohead/cve-2019-8540
Kernel Stack info leak at exportObjectToClient function
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
 nickcano/xenoscan
Open source memory scanner written in C++
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 benschlueter/cve-2021-33624
Proof of Concept for CVE-2021-33624
 mister-turtle/cve-2023-32784
Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…
 0x36/pixel_gpu_exploit
Android 14 kernel exploit for Pixel7/8 Pro
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…