

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 strongcourage/uafuzz
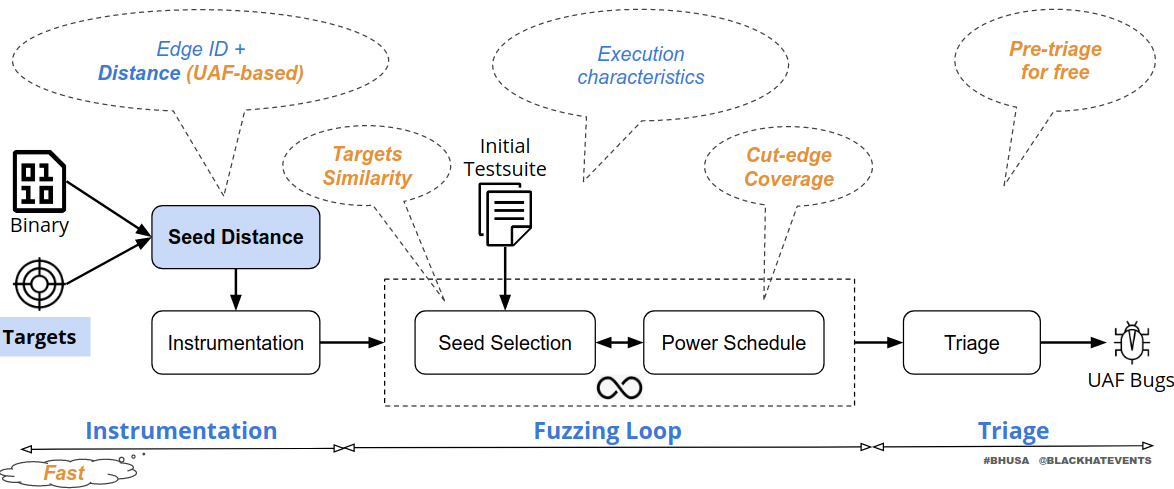
Binary-level directed fuzzer specialized in detecting Use-After-Free vulnerabilities via ordering-aware input metrics and static analysis, enabling…
 rainbowdynamix/ghostkatz
Dump LSASS via physical memory read primitives in vulnerable kernel drivers
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
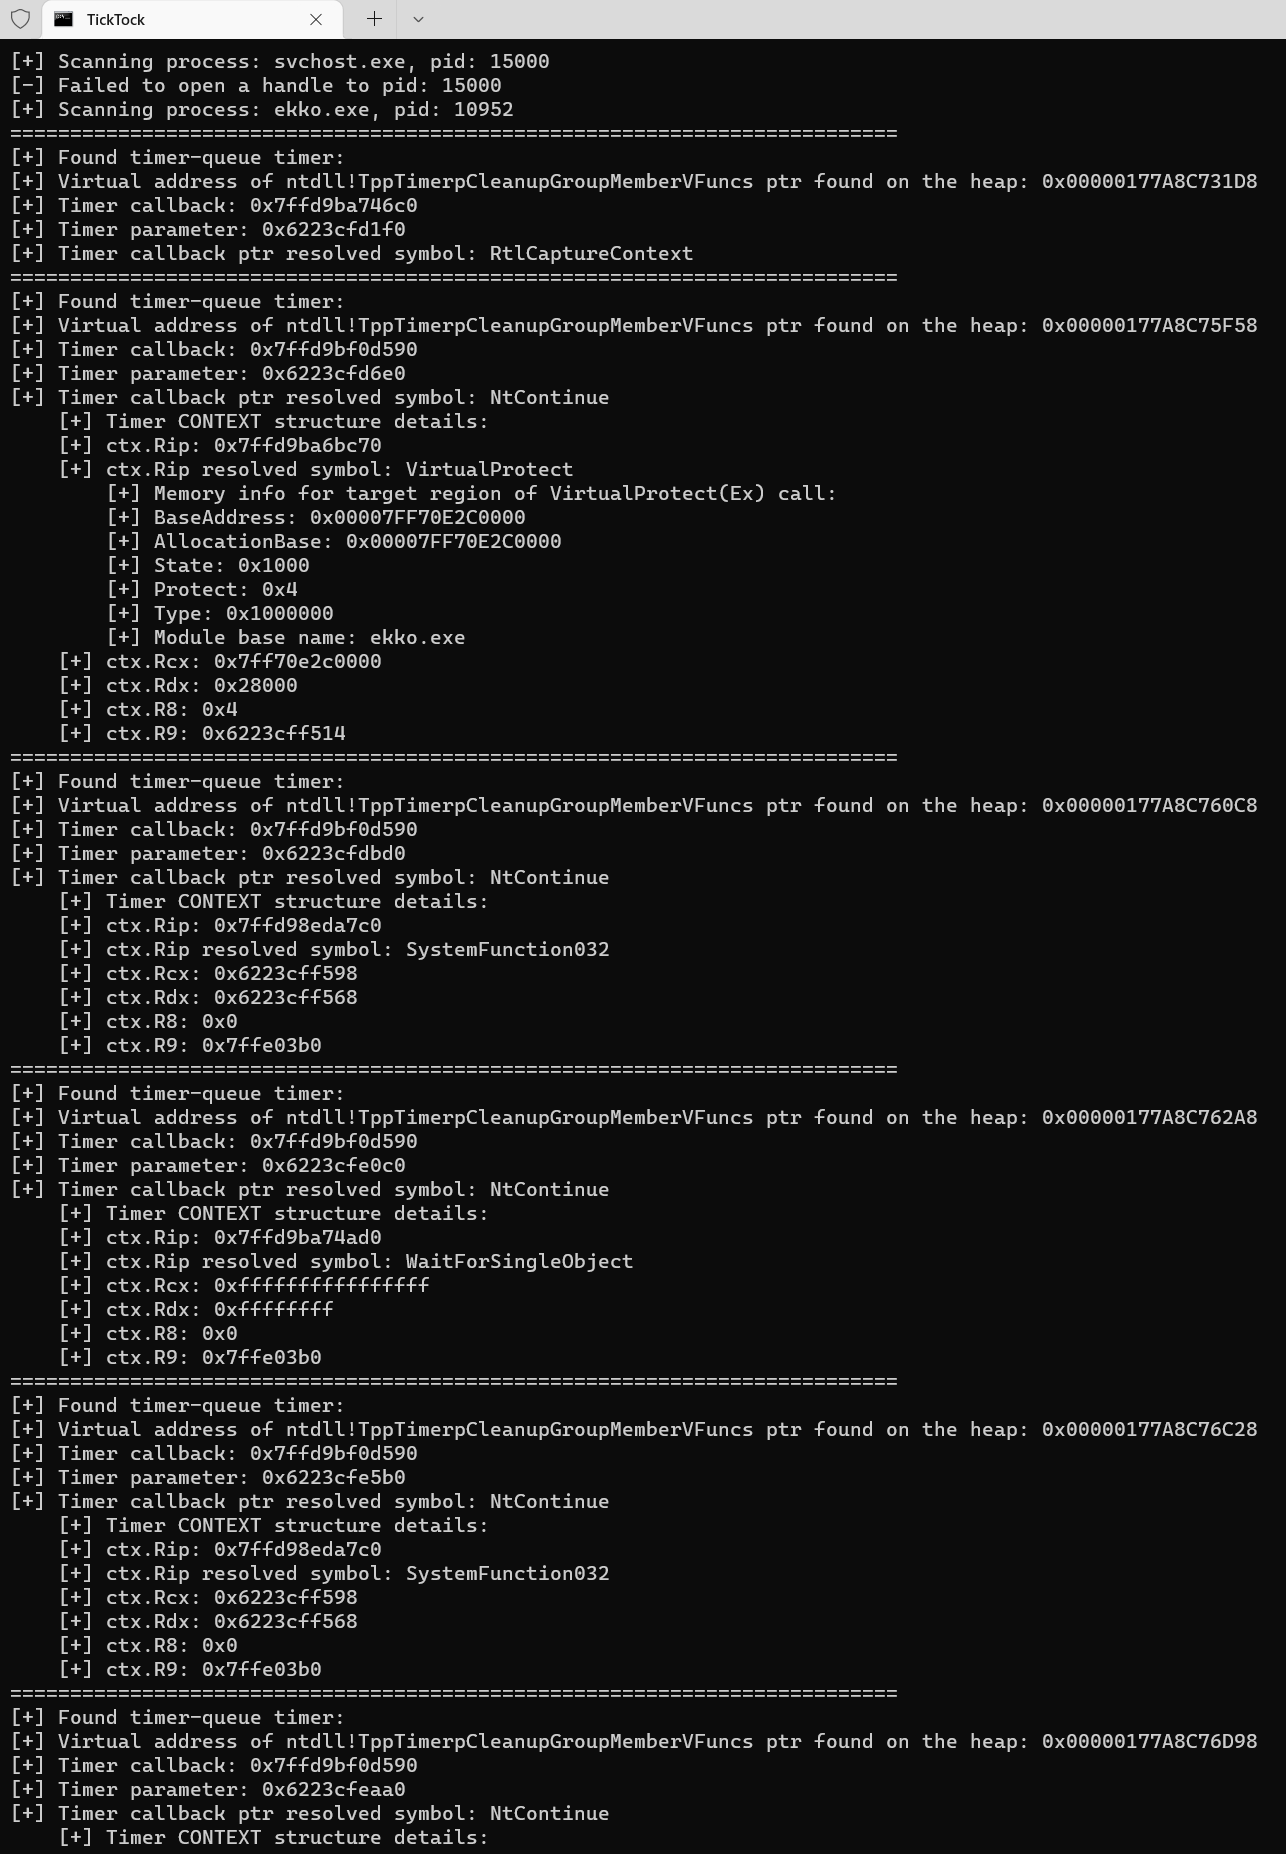 withsecurelabs/ticktock
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 theori-io/cve-2022-26717-safari-webgl-exploit
Proof-of-concept exploit for CVE-2022-26717, a use-after-free vulnerability in Safari's WebGL implementation, enabling remote code execution via…
 hakivvi/cve-2021-40449
Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
 sophoslabs/cve-2019-0888
PoC for CVE-2019-0888 - Use-After-Free in Windows ActiveX Data Objects (ADO)
 oferchen/poc-cve-2023-32233
Use-After-Free in Netfilter nf_tables when processing batch requests CVE-2023-32233
 hamza-megahed/volatility-gui
GUI for Volatility forensics tool written in PyQT5
 seemoo-lab/dtrace-memaccess_cve-2020-27949
Proof-of-concept exploit for CVE-2020-27949, demonstrating arbitrary memory read/write in macOS processes via DTrace fasttrap ioctl without elevated…
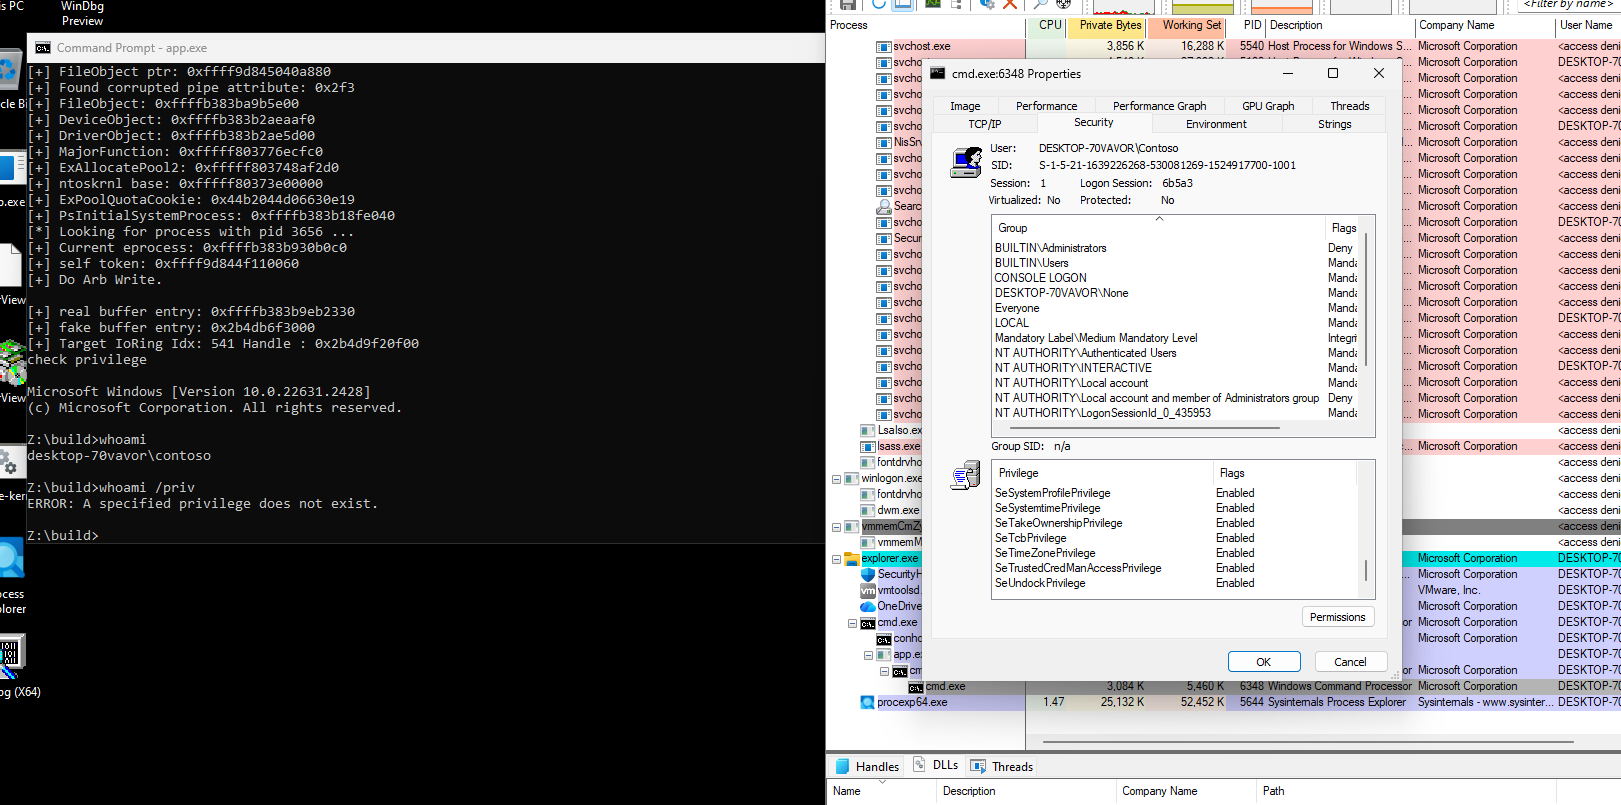 nu1lptr0/cve-2025-21333
LPE due to integer truncation in vskrnlintvsp.sys
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 jprx/cve-2024-54507
Proof-of-concept exploit for CVE-2024-54507, an integer type confusion vulnerability in XNU kernel, with technical writeup and exploitation details.