
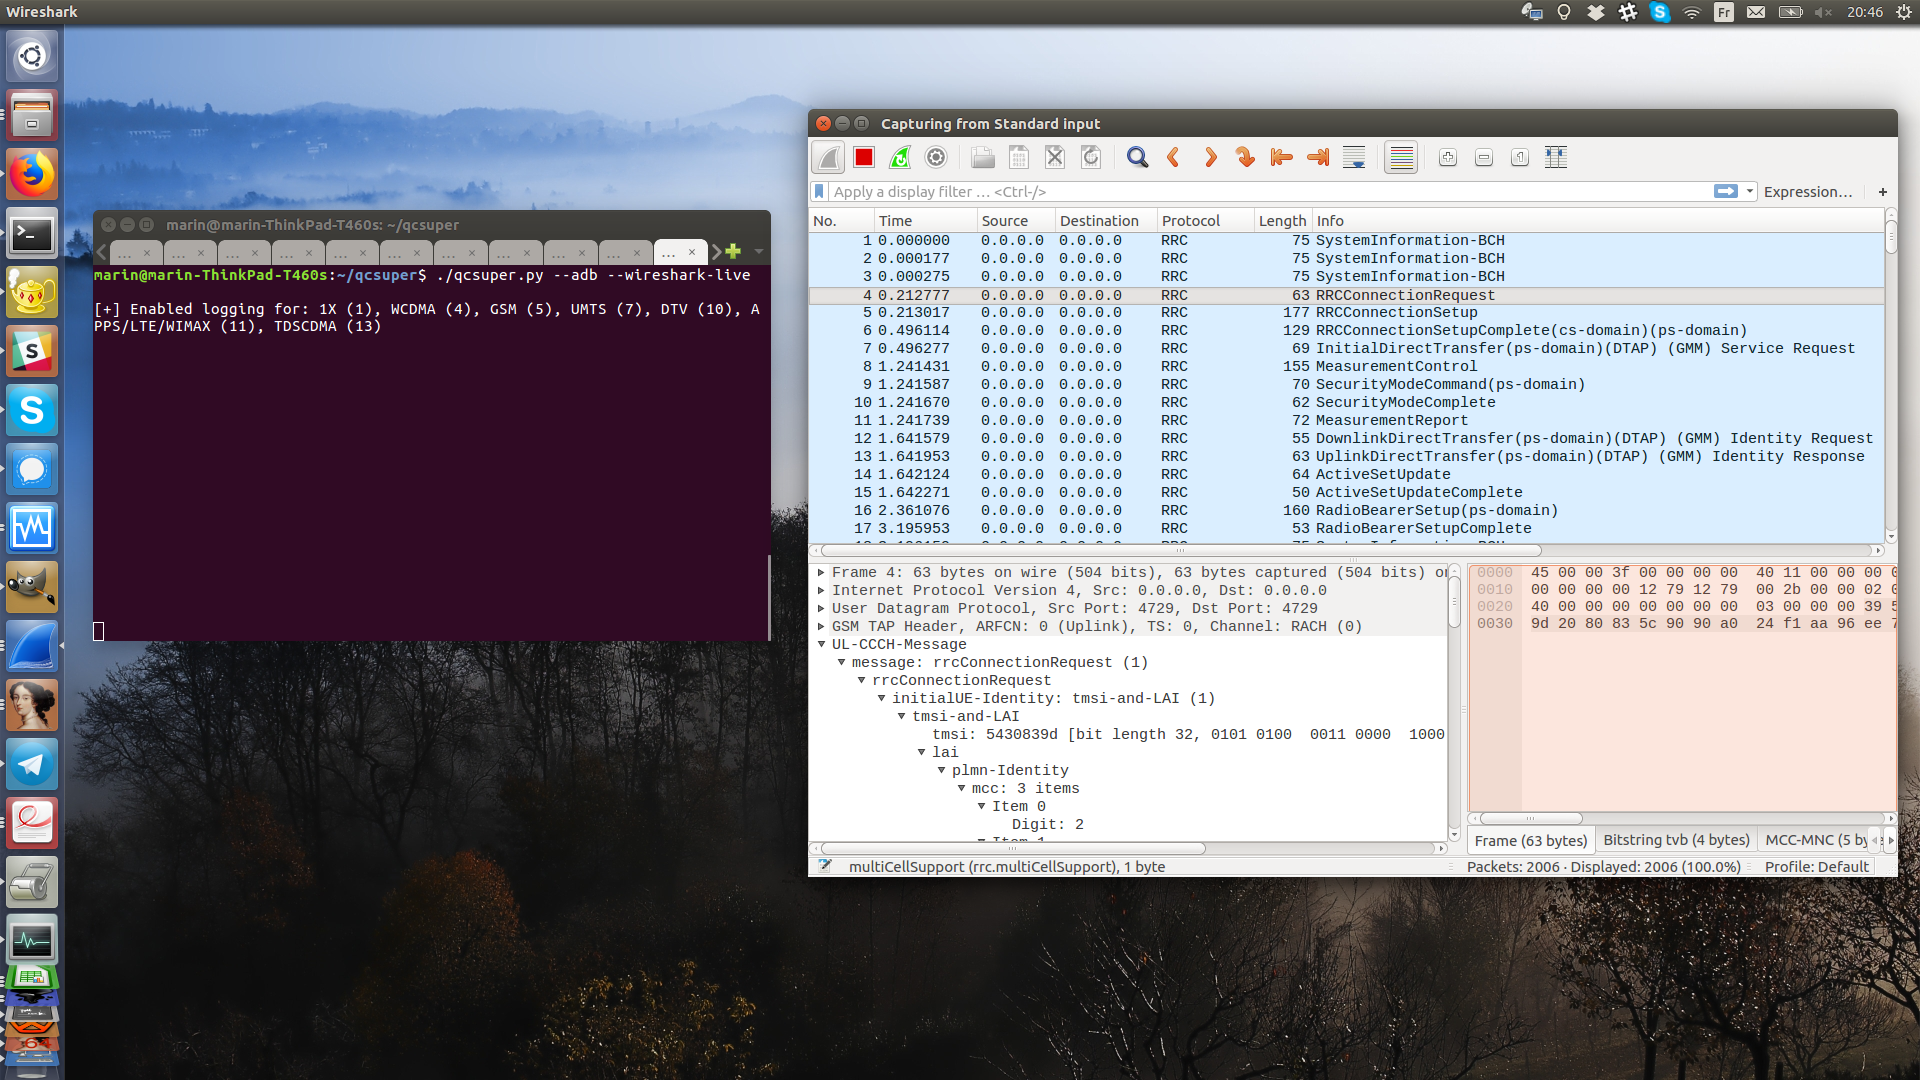
QCSuper
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
p1sec/qcsuperQCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 bazad/gsscred-move-uaf
CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.
 fy-poc/full-poc-cve-2025_21298
Complete analysis of CVE-2025-21298, a double free vulnerability related to ole32 library in windows.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 renukaselvar/libunwind_cve-2015-3239
C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…
 renukaselvar/libunwind_cve-2015-3239_after
Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
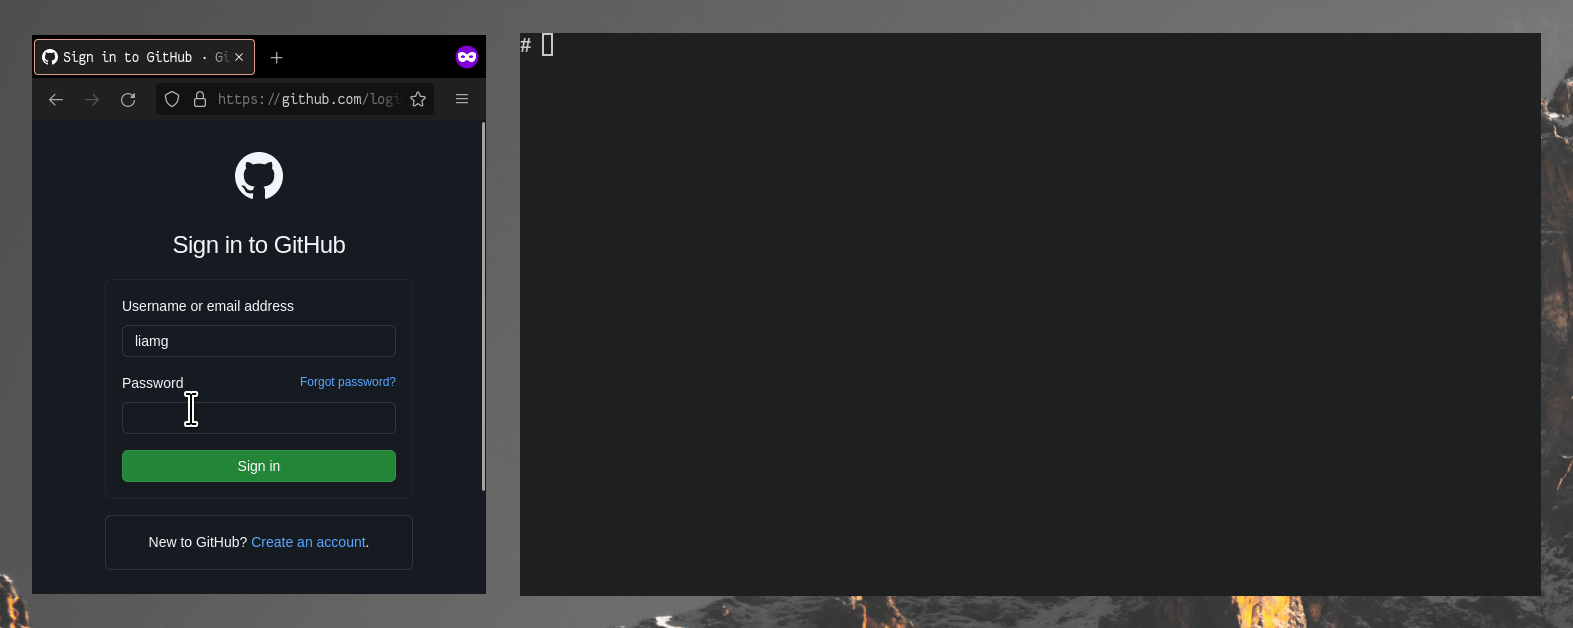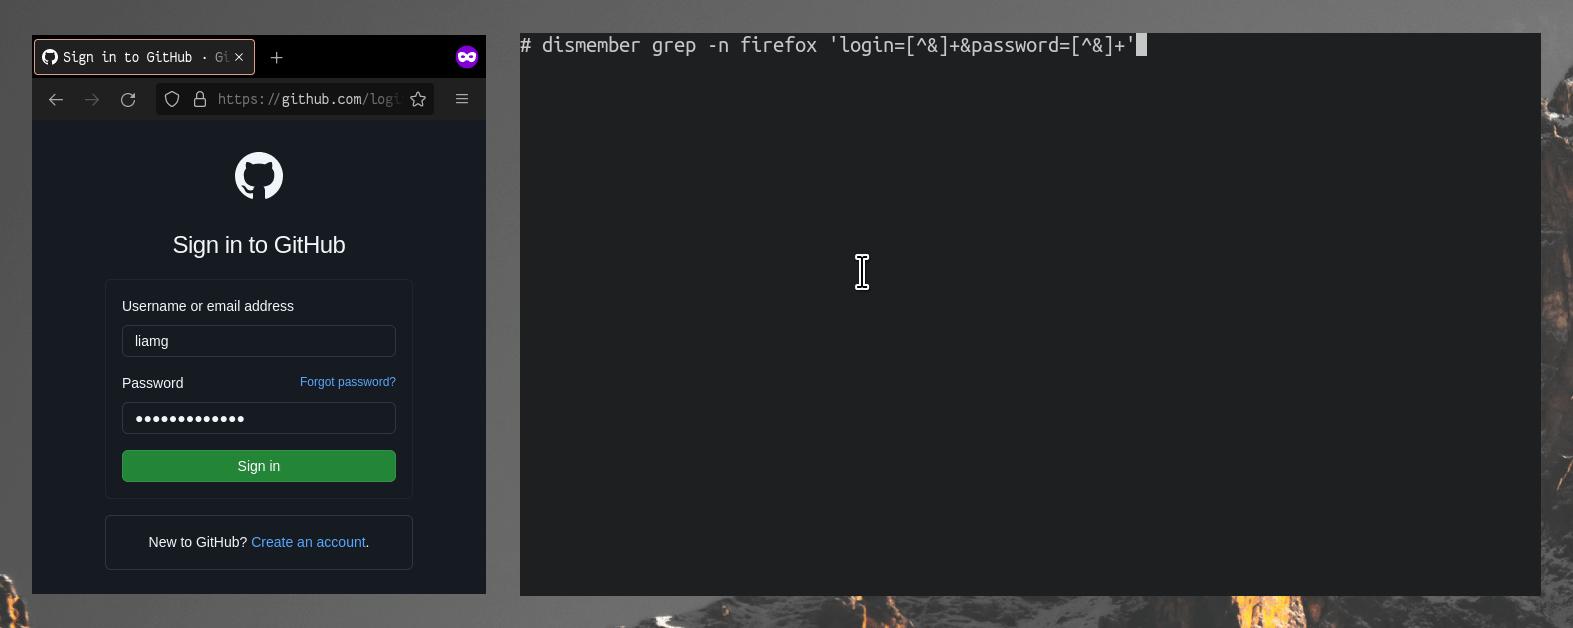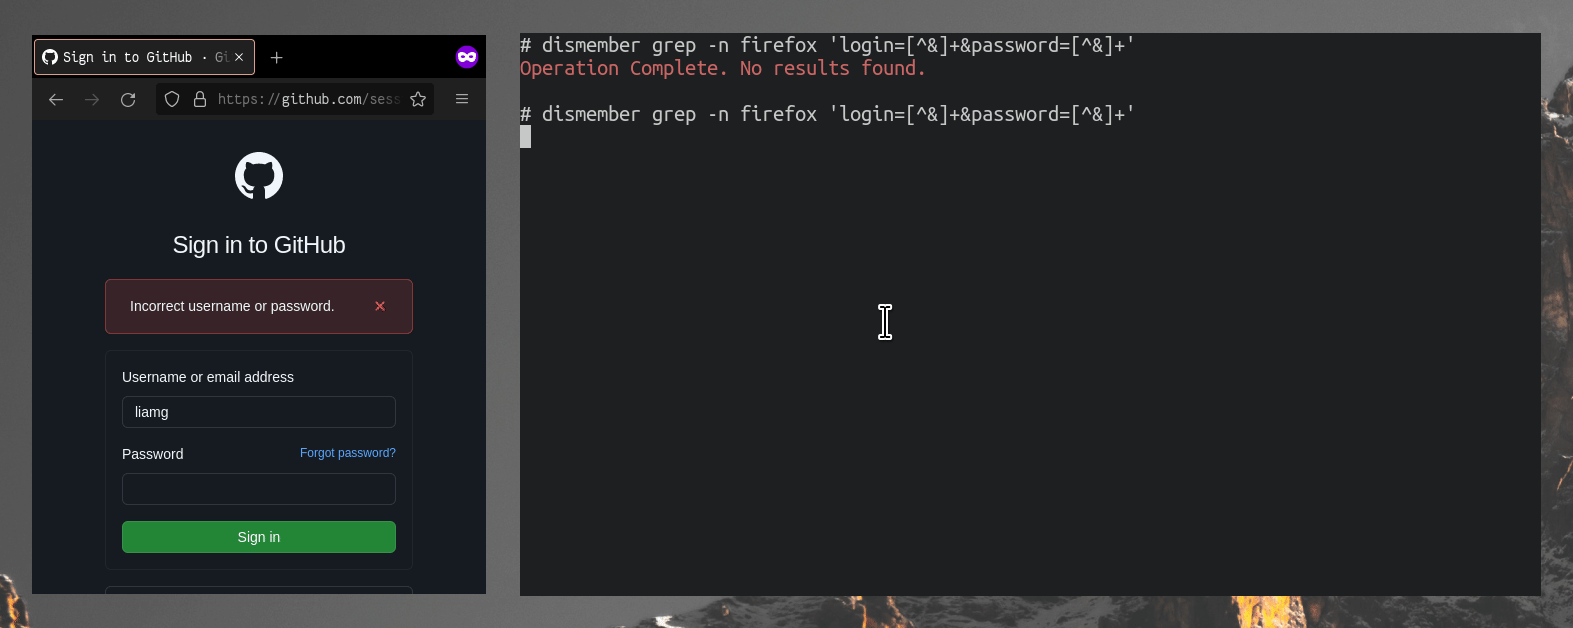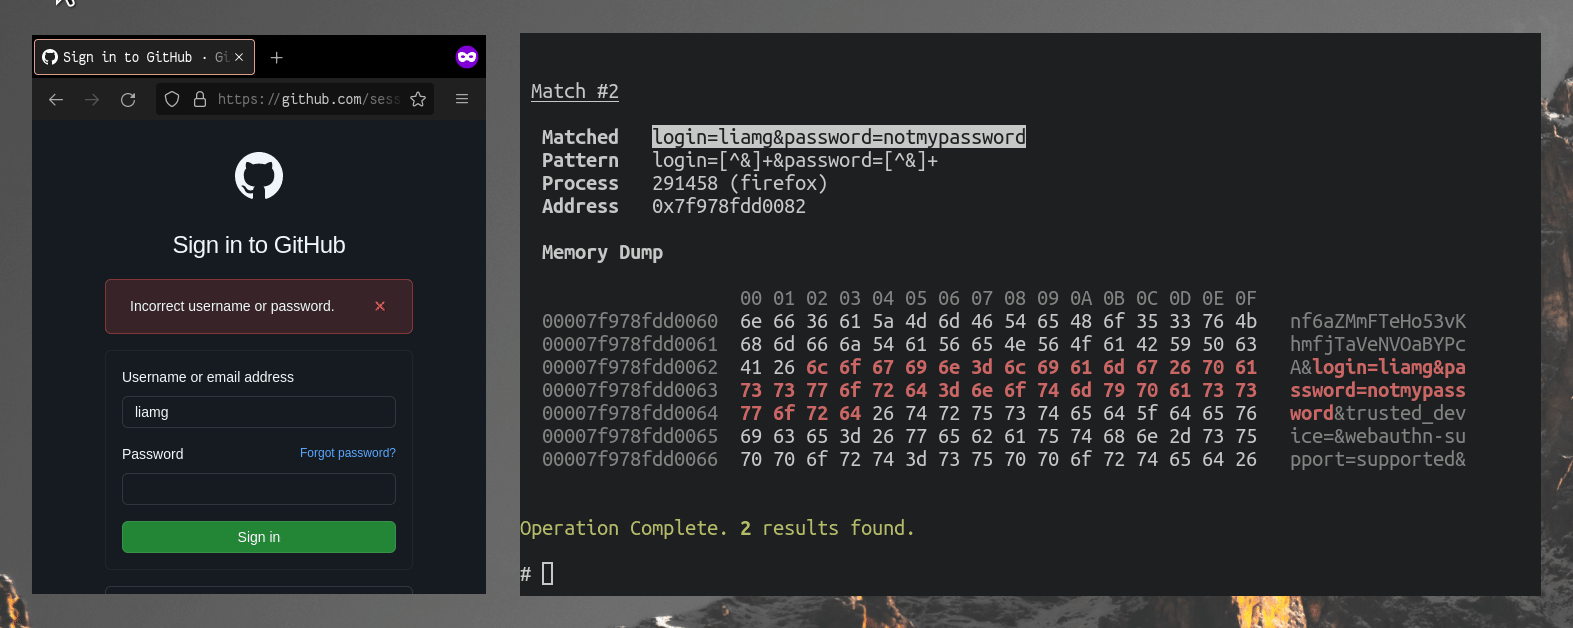 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
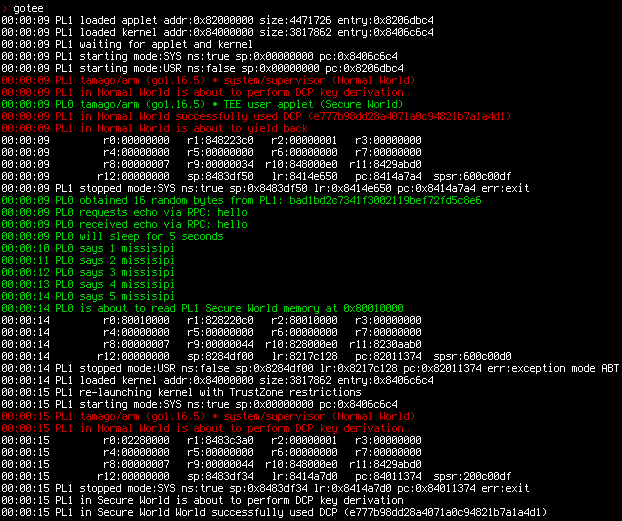 usbarmory/gotee-example
GoTEE - example application
 amberchalia/norm-edr
Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…