

KernelFlirt
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
ai-assisted-reversingai-securityanti-bot+9
55
akatorich/kernelflirtWindows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
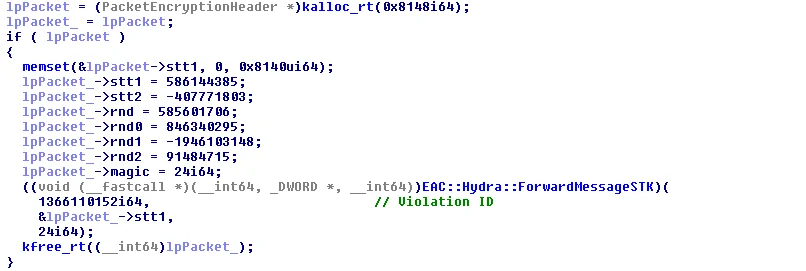 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 gmh5225/mapped-dumper
A program written in C++ for remotely dumping manual mapped modules.
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 ermensonx/cve-2025-14857-mongobleed
Functional proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a pre-authentication heap memory disclosure vulnerability in MongoDB. Includes…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 devianntsec/cve-2024-30051
Master's Thesis research on CVE-2024-30051 (Windows DWM Heap Overflow). Features a high-reliability exploit with automated heap spray optimization,…
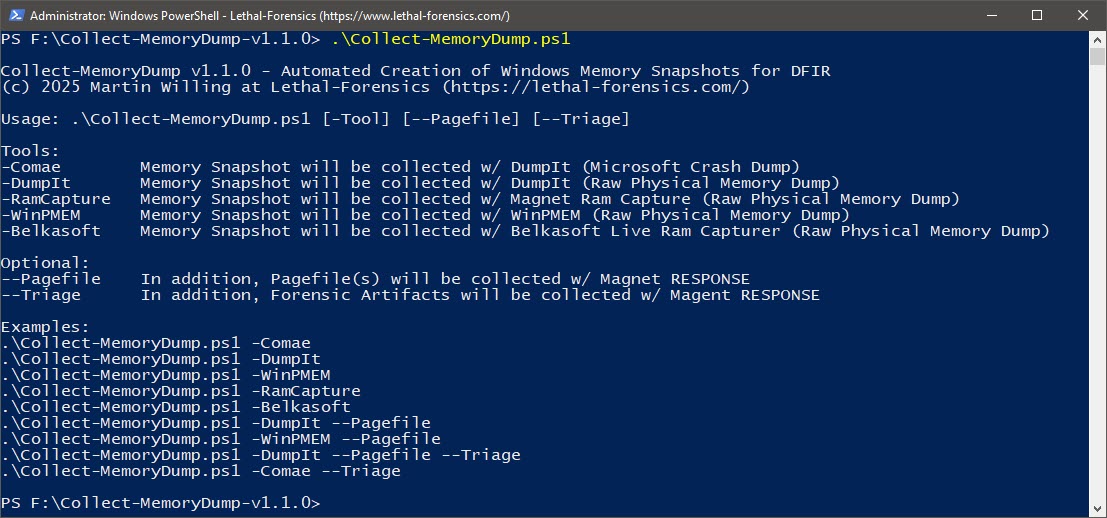 lethal-forensics/collect-memorydump
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 marcosd4h/memhunter
Live hunting of code injection techniques
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 hasherezade/pesieve-go
Golang bindings for PE-sieve
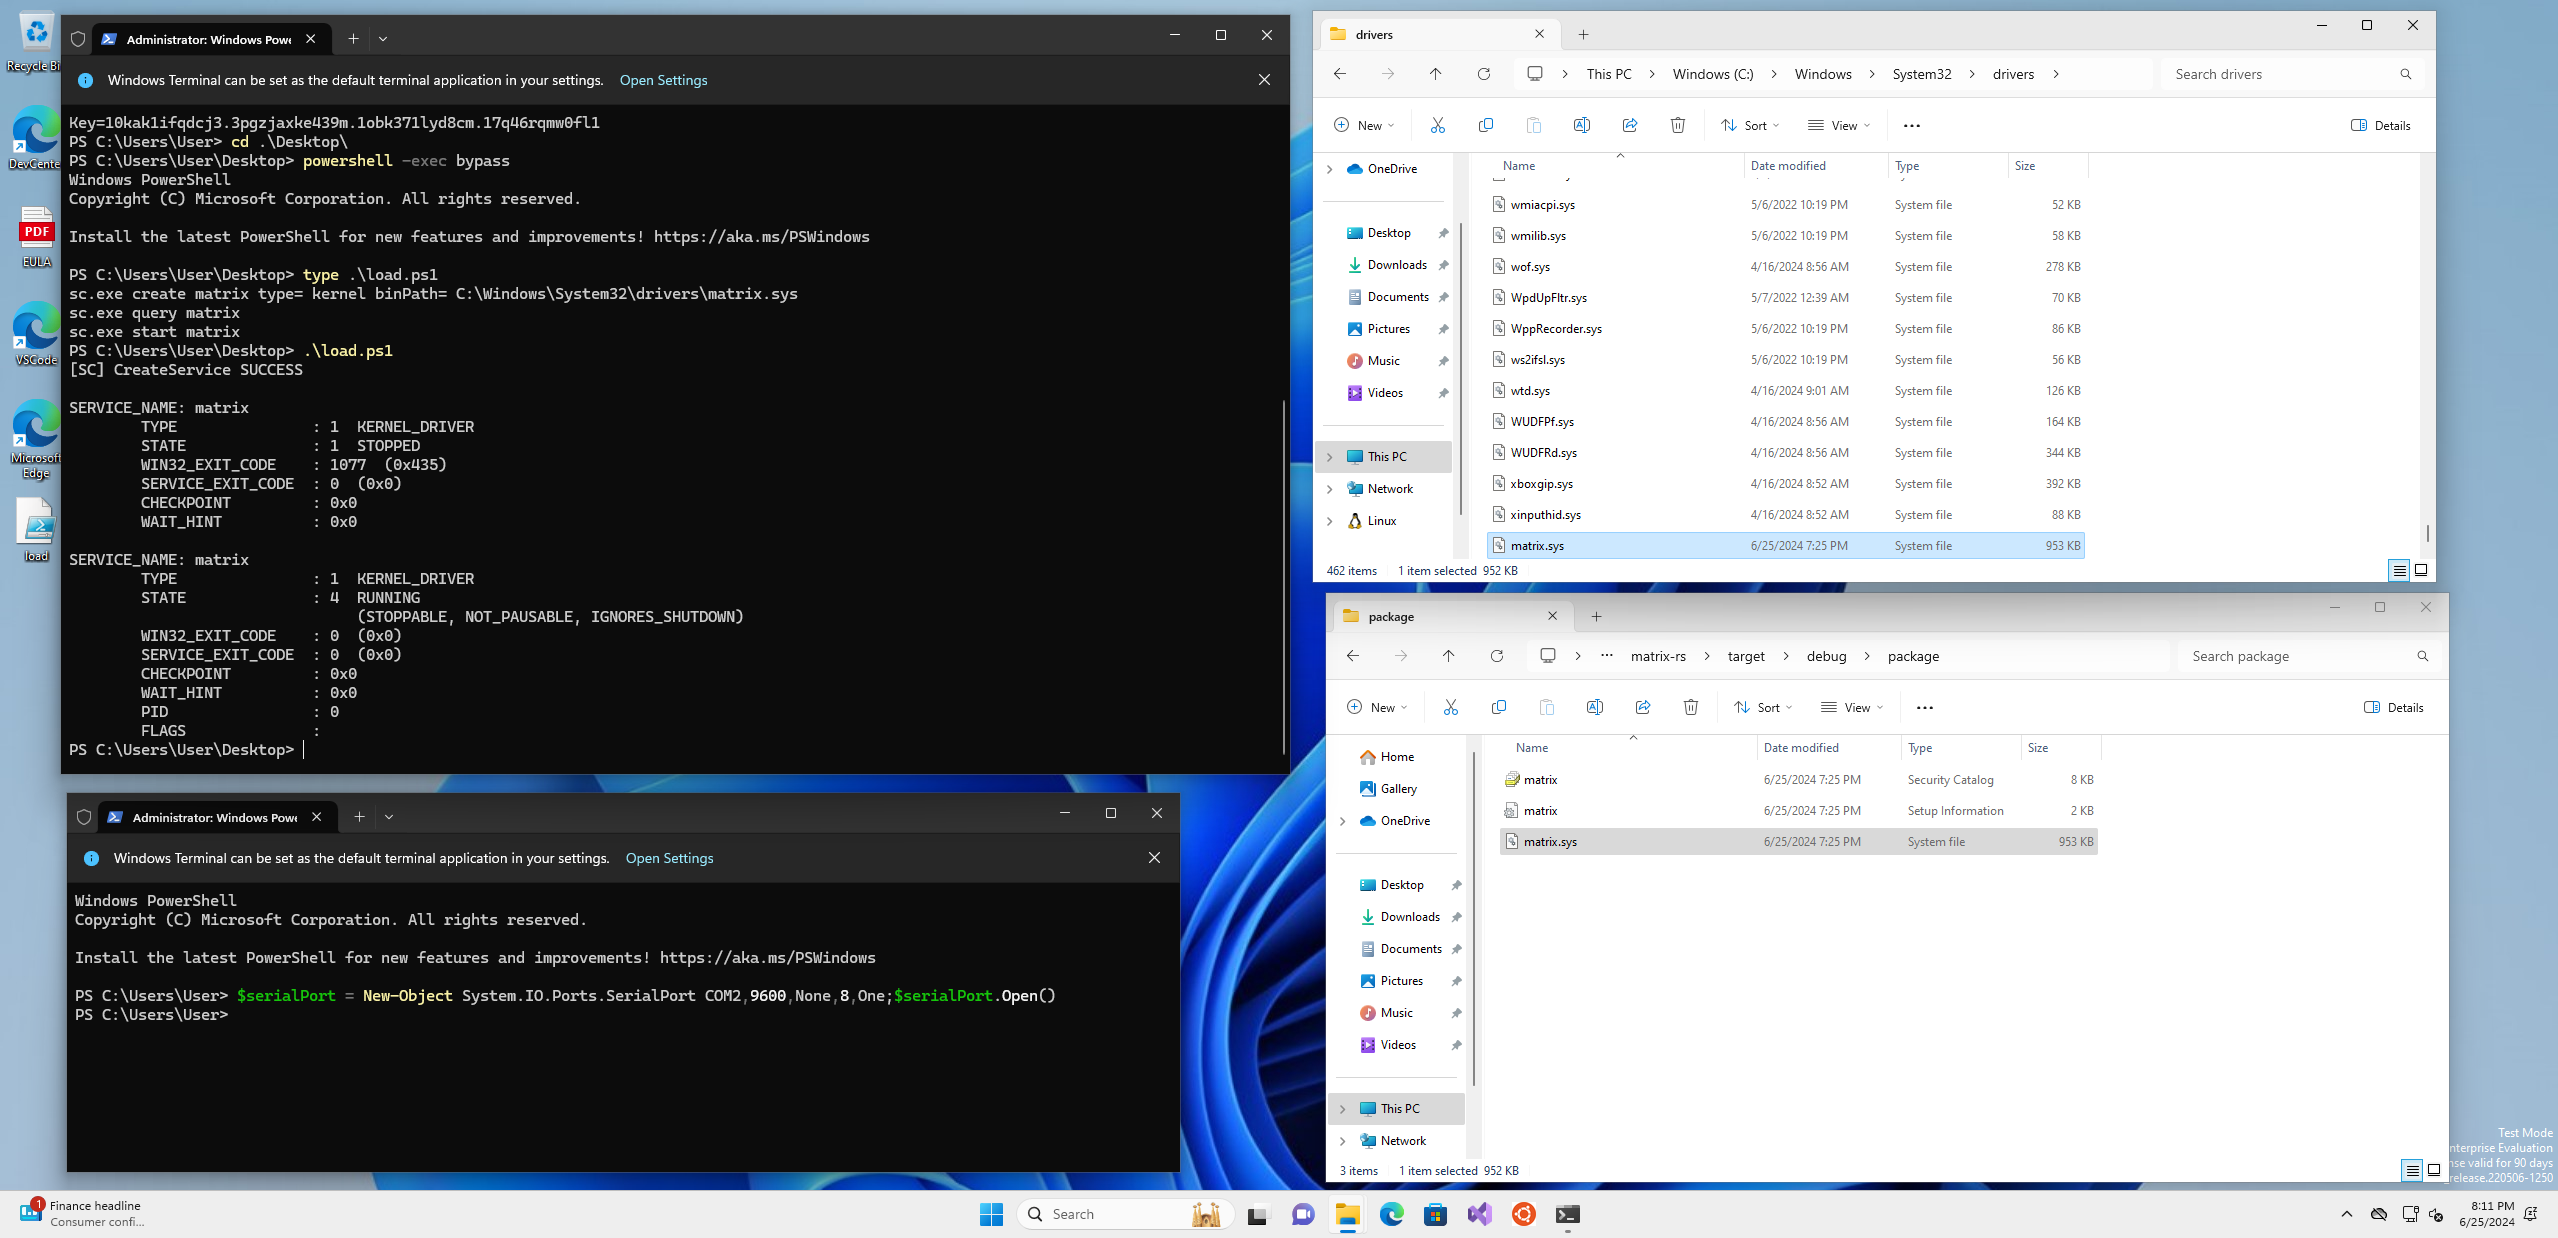 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 angr/angr
A powerful and user-friendly binary analysis platform!