
EvilKaspersky
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
2
gmh5225/evilkasperskyWindows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 lsw29475/cve-2020-17057
Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
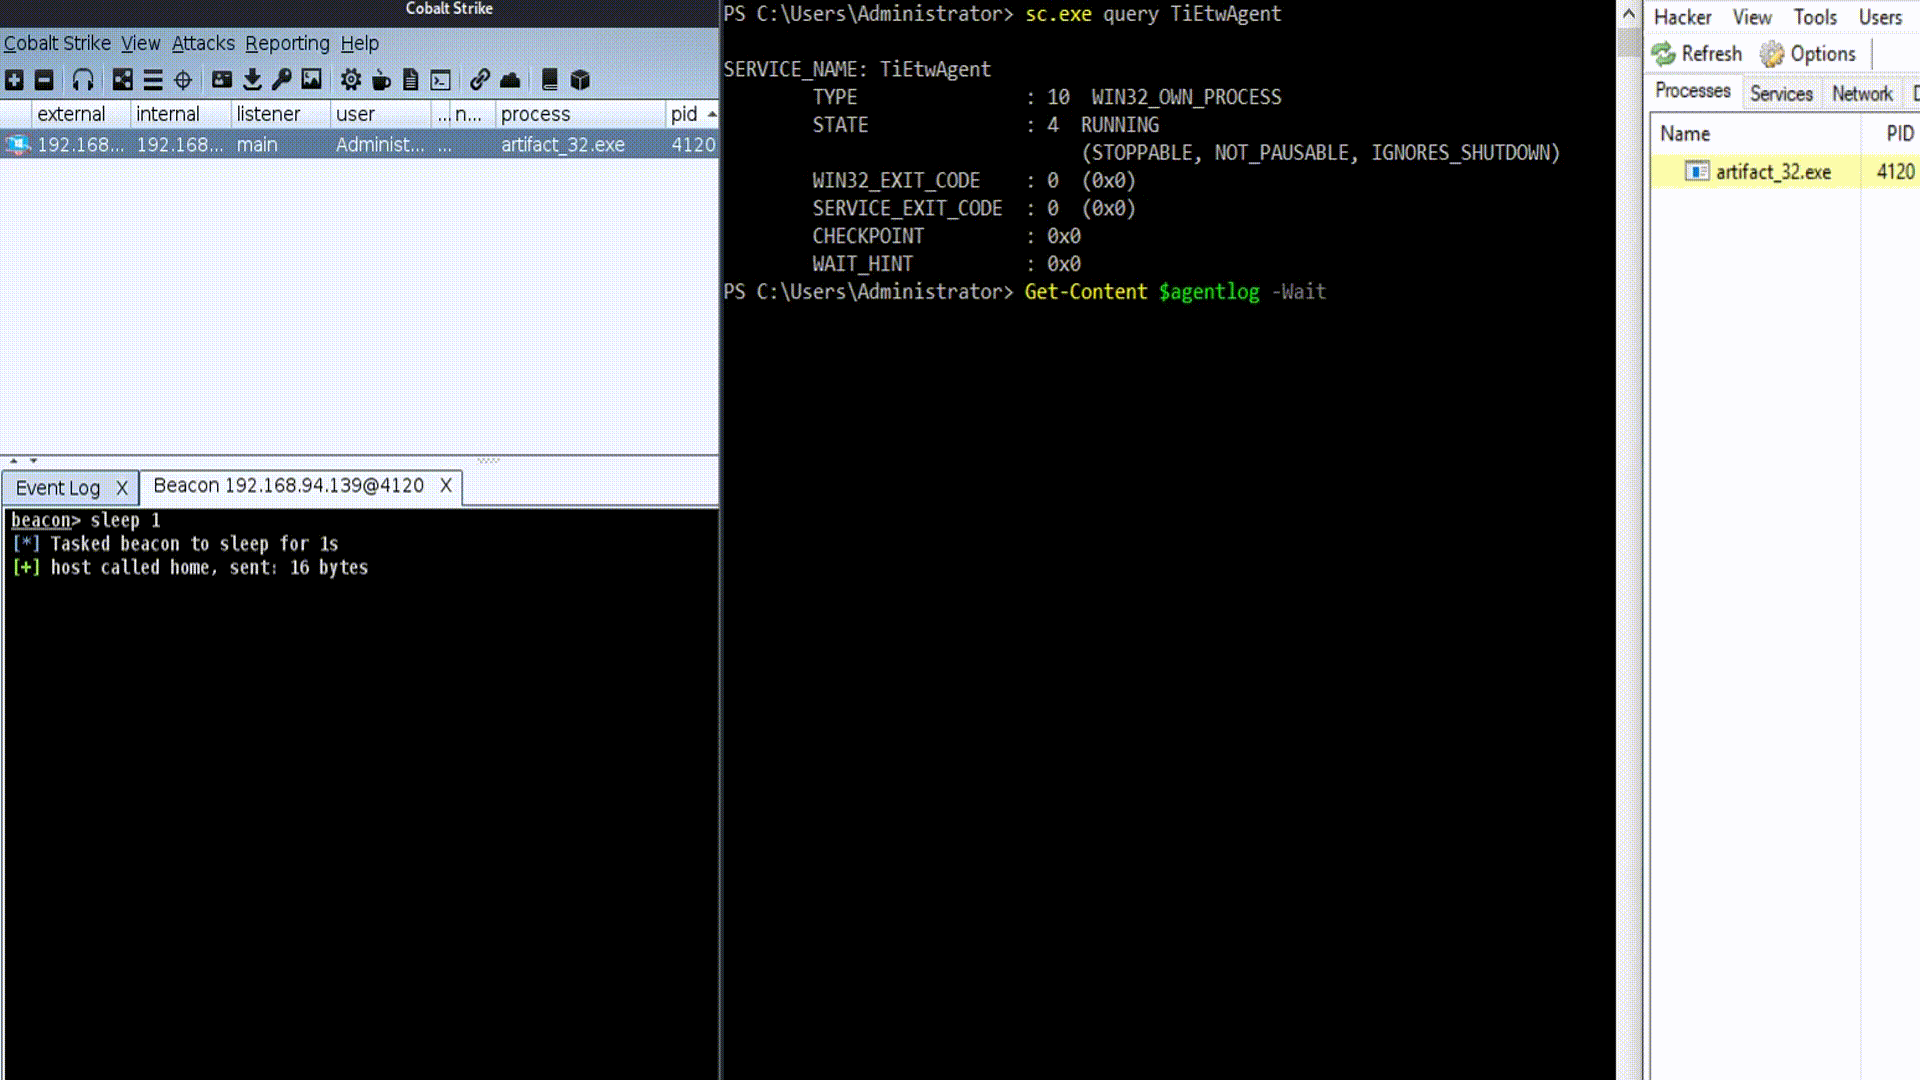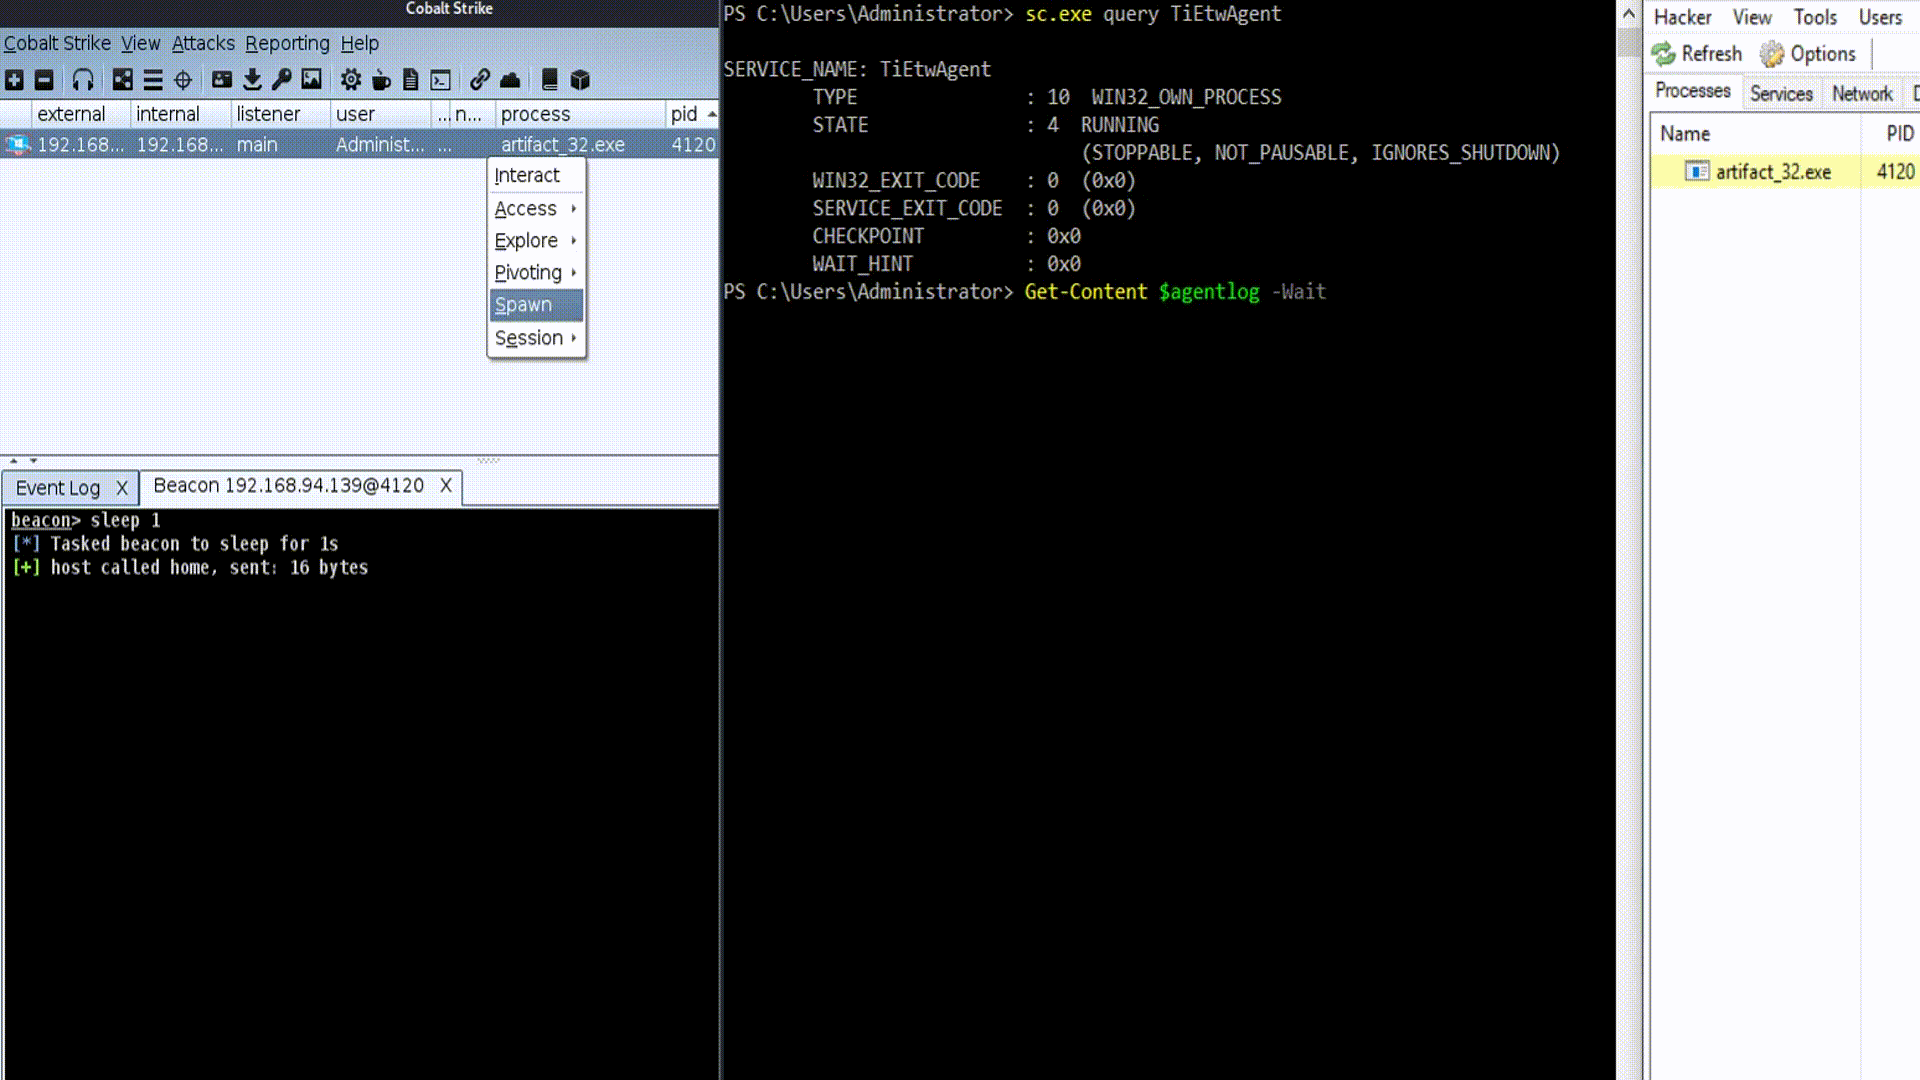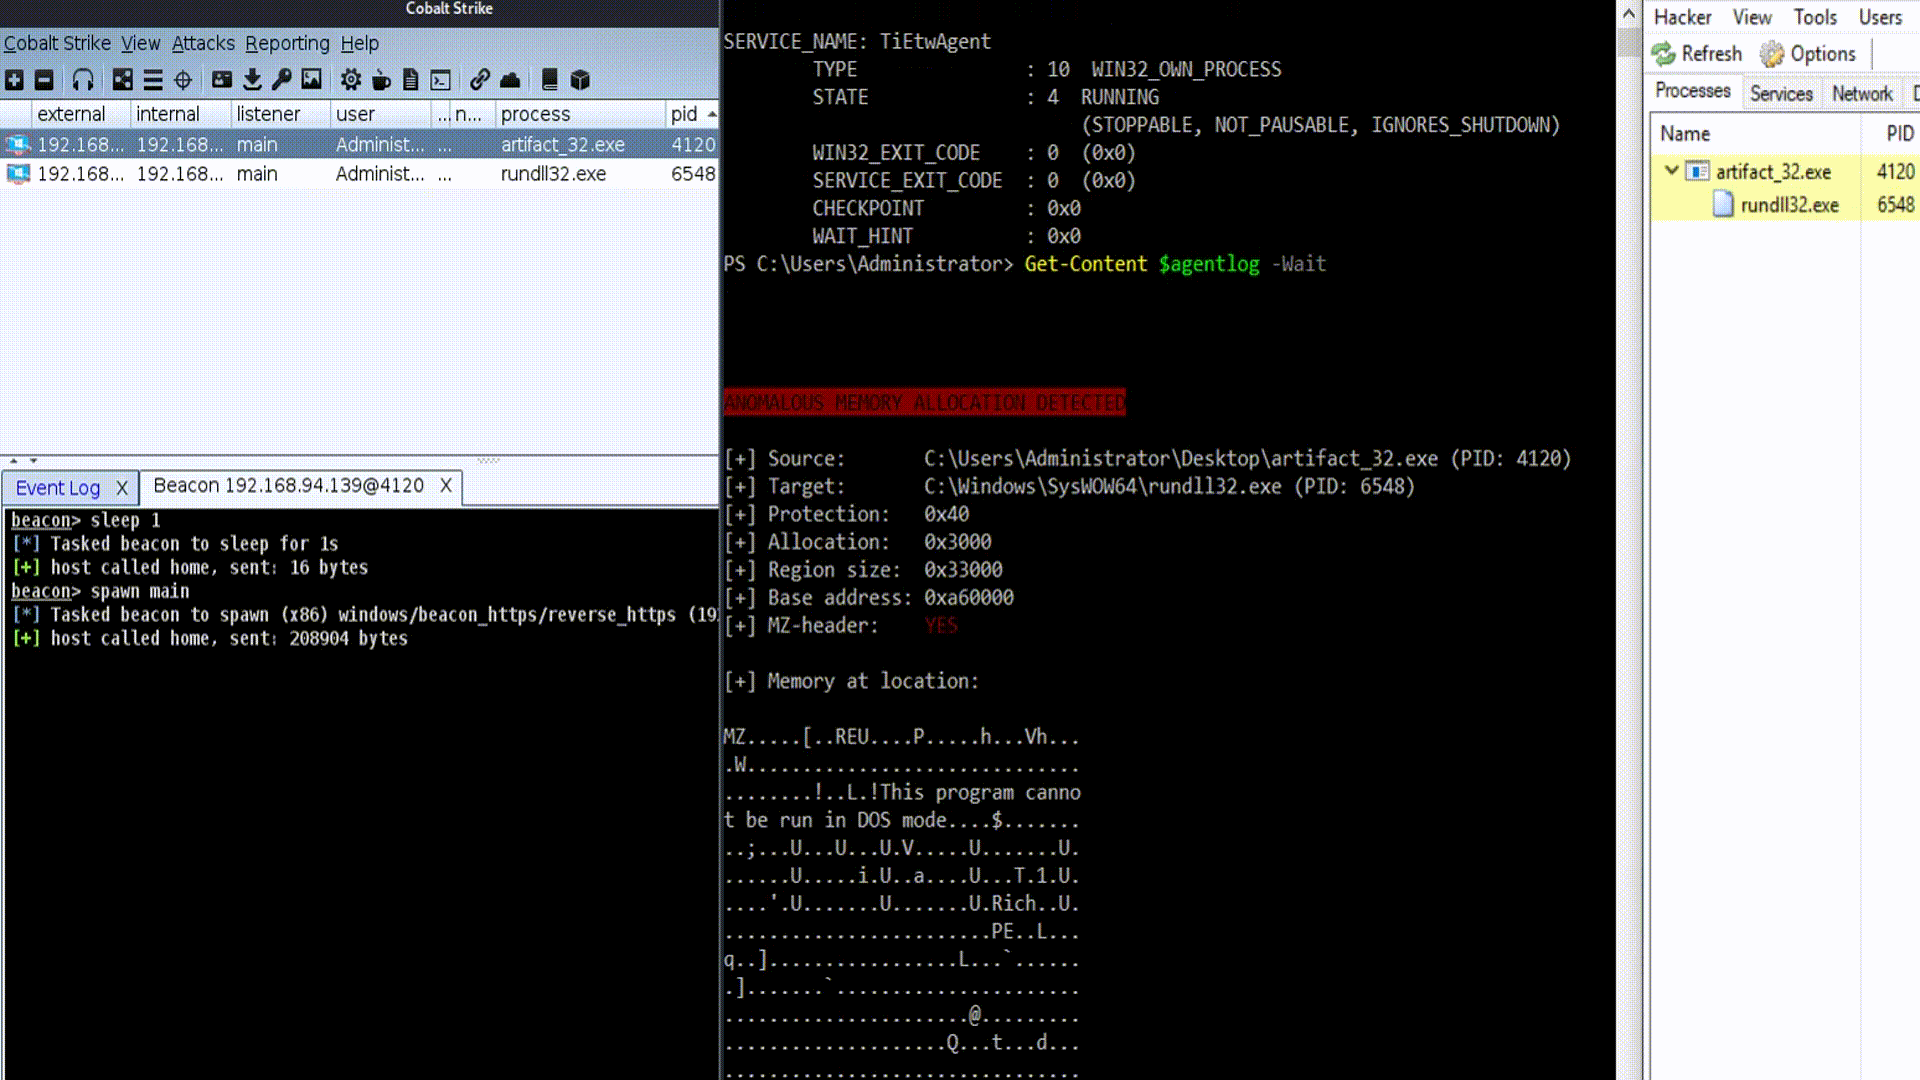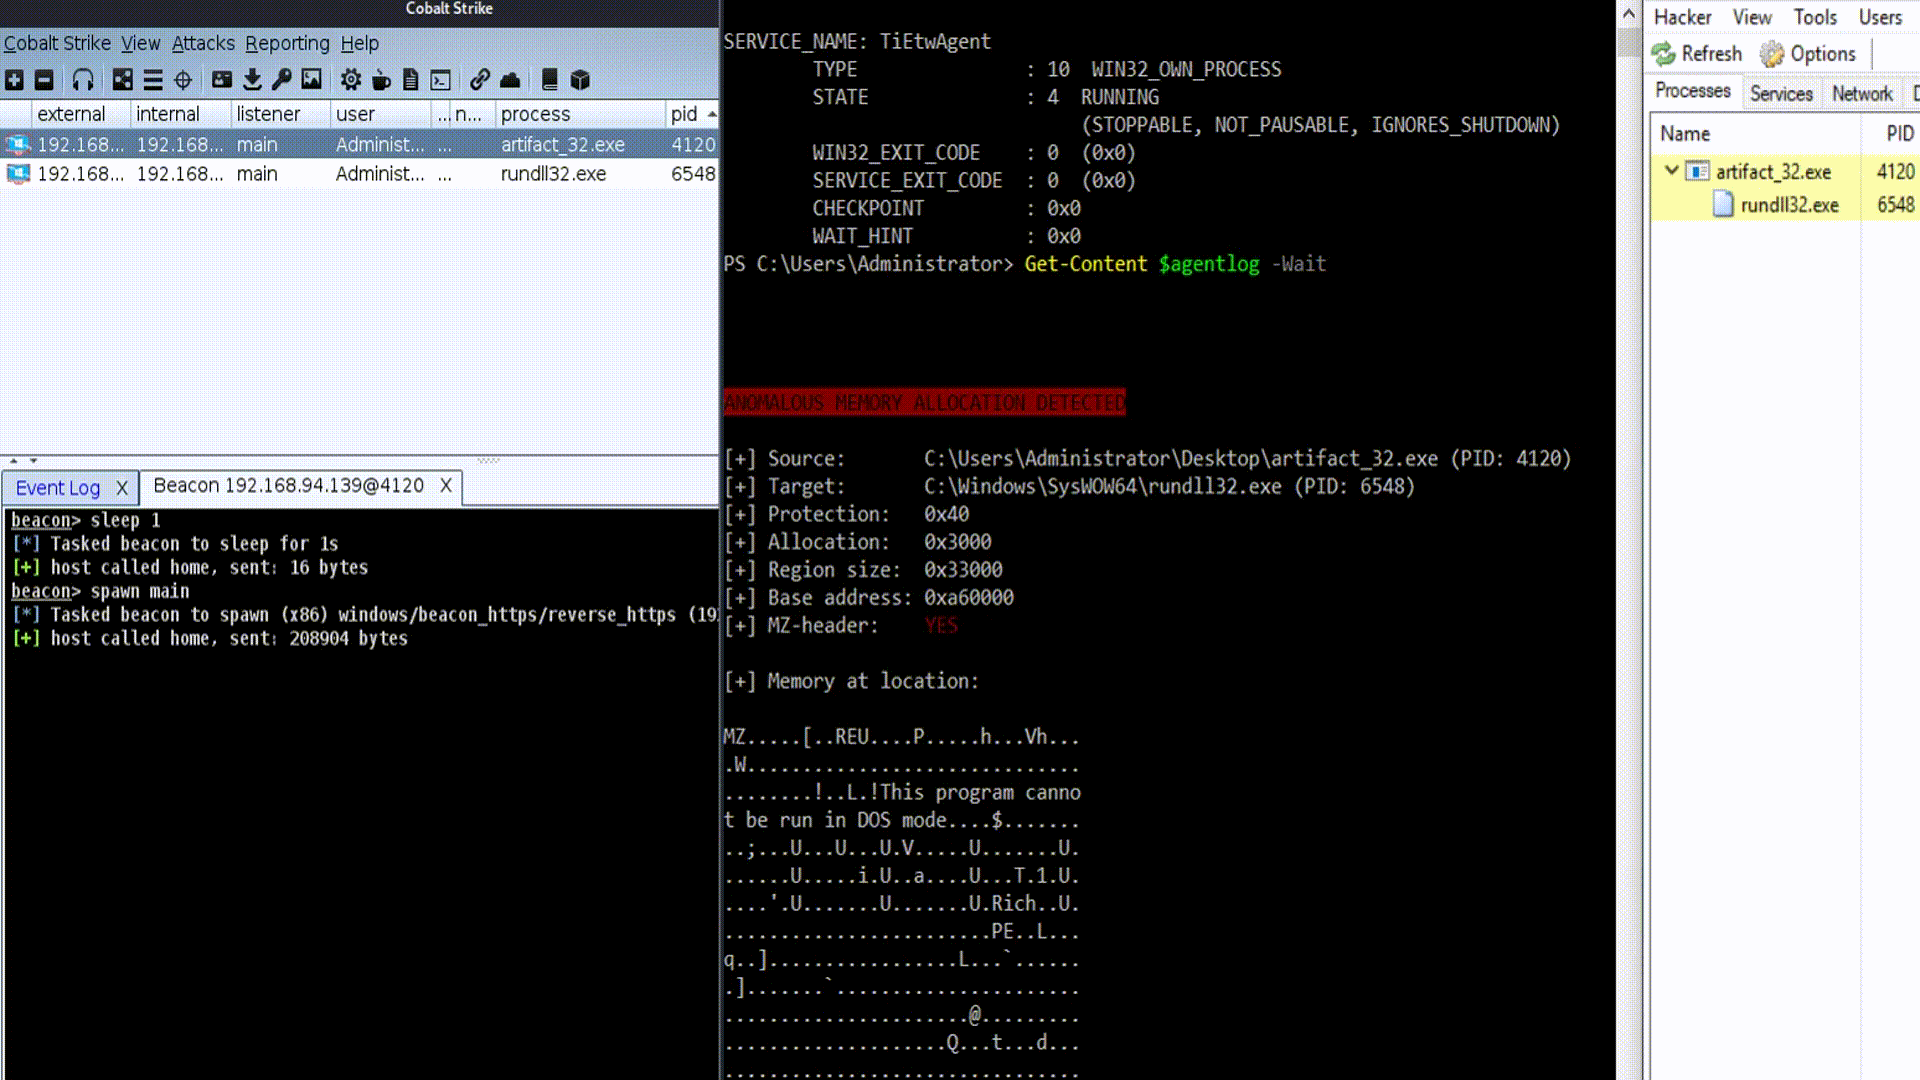 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
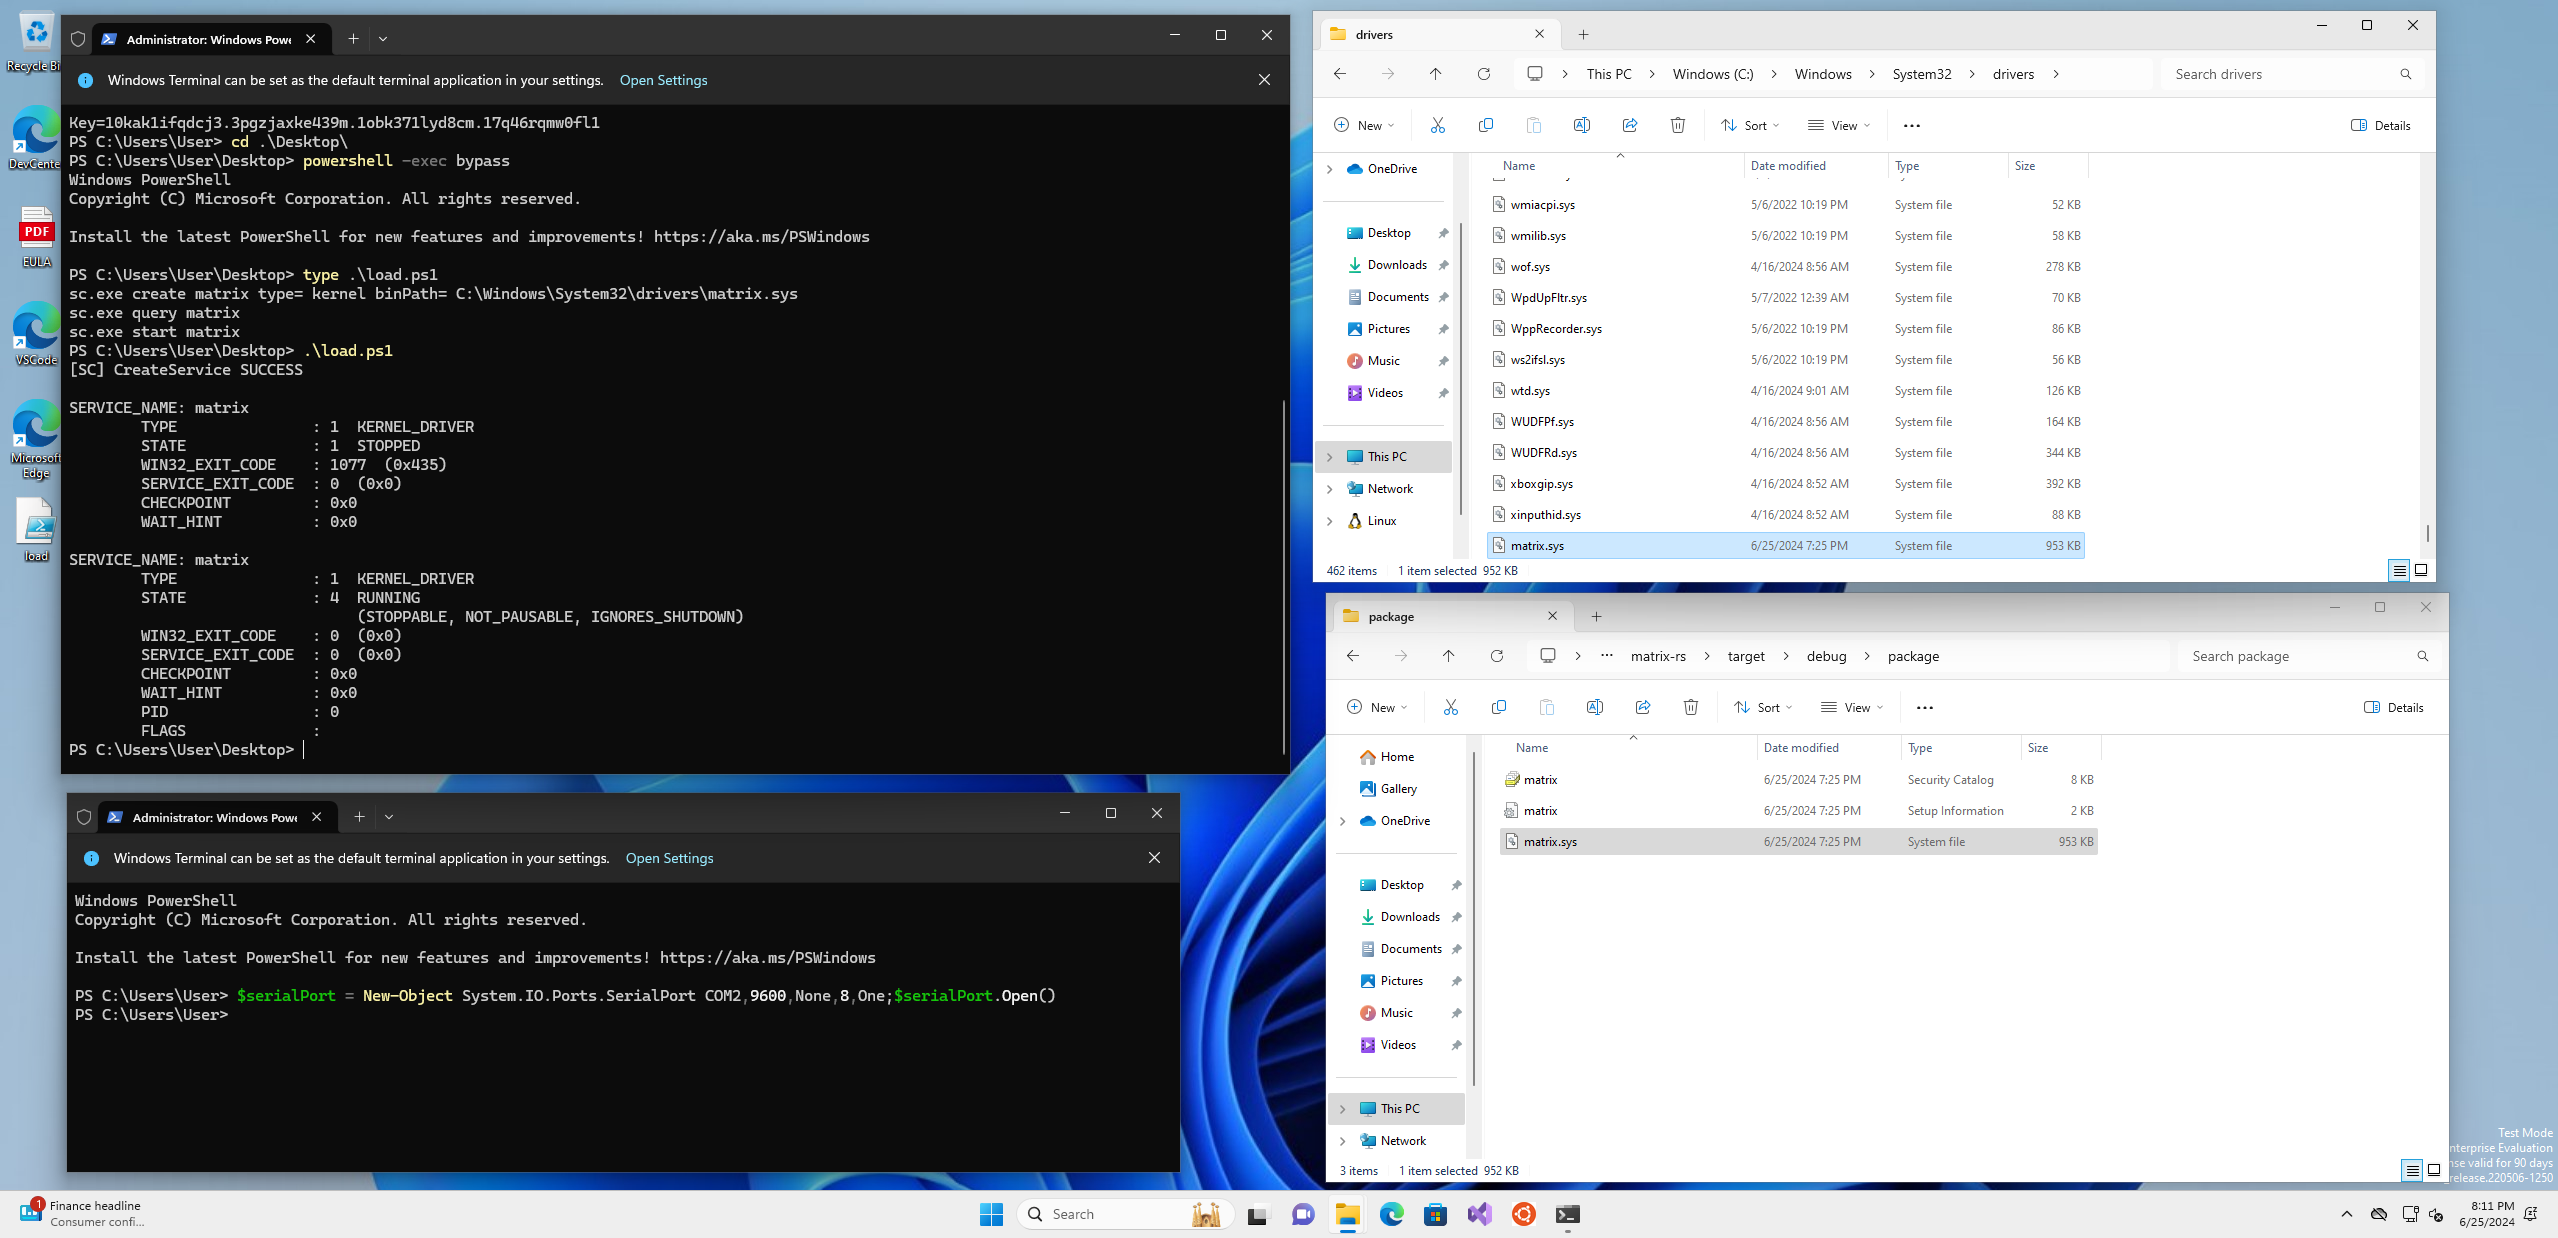 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver