
volatility3
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.4k
volatilityfoundation/volatility3Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 volatilityfoundation/volatility
An advanced memory forensics framework
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 angr/angr
A powerful and user-friendly binary analysis platform!
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
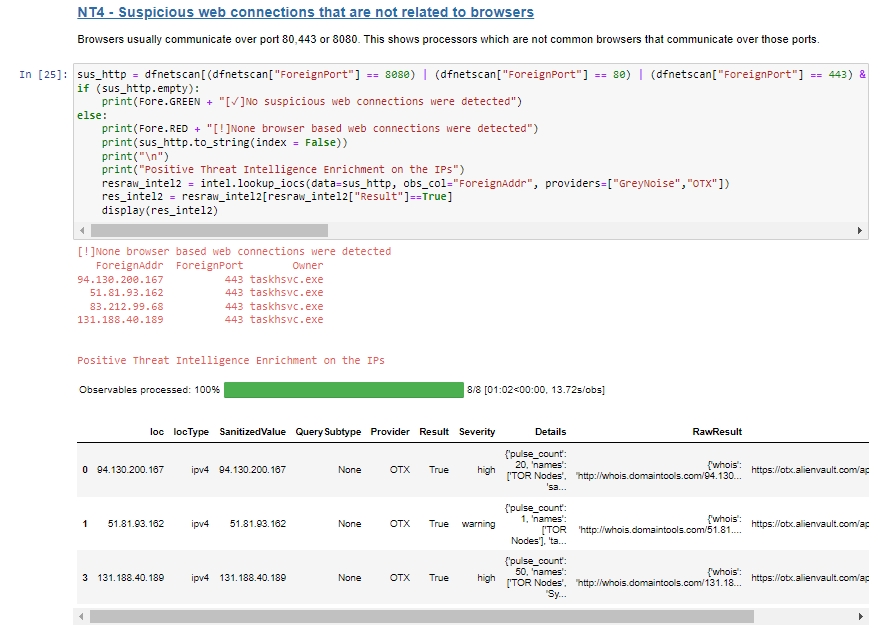 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
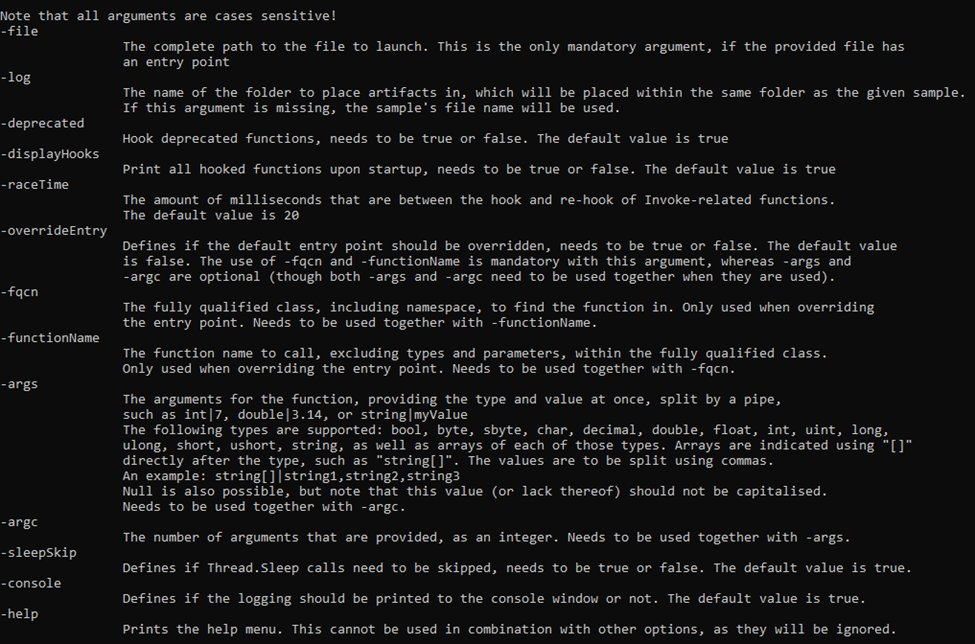 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
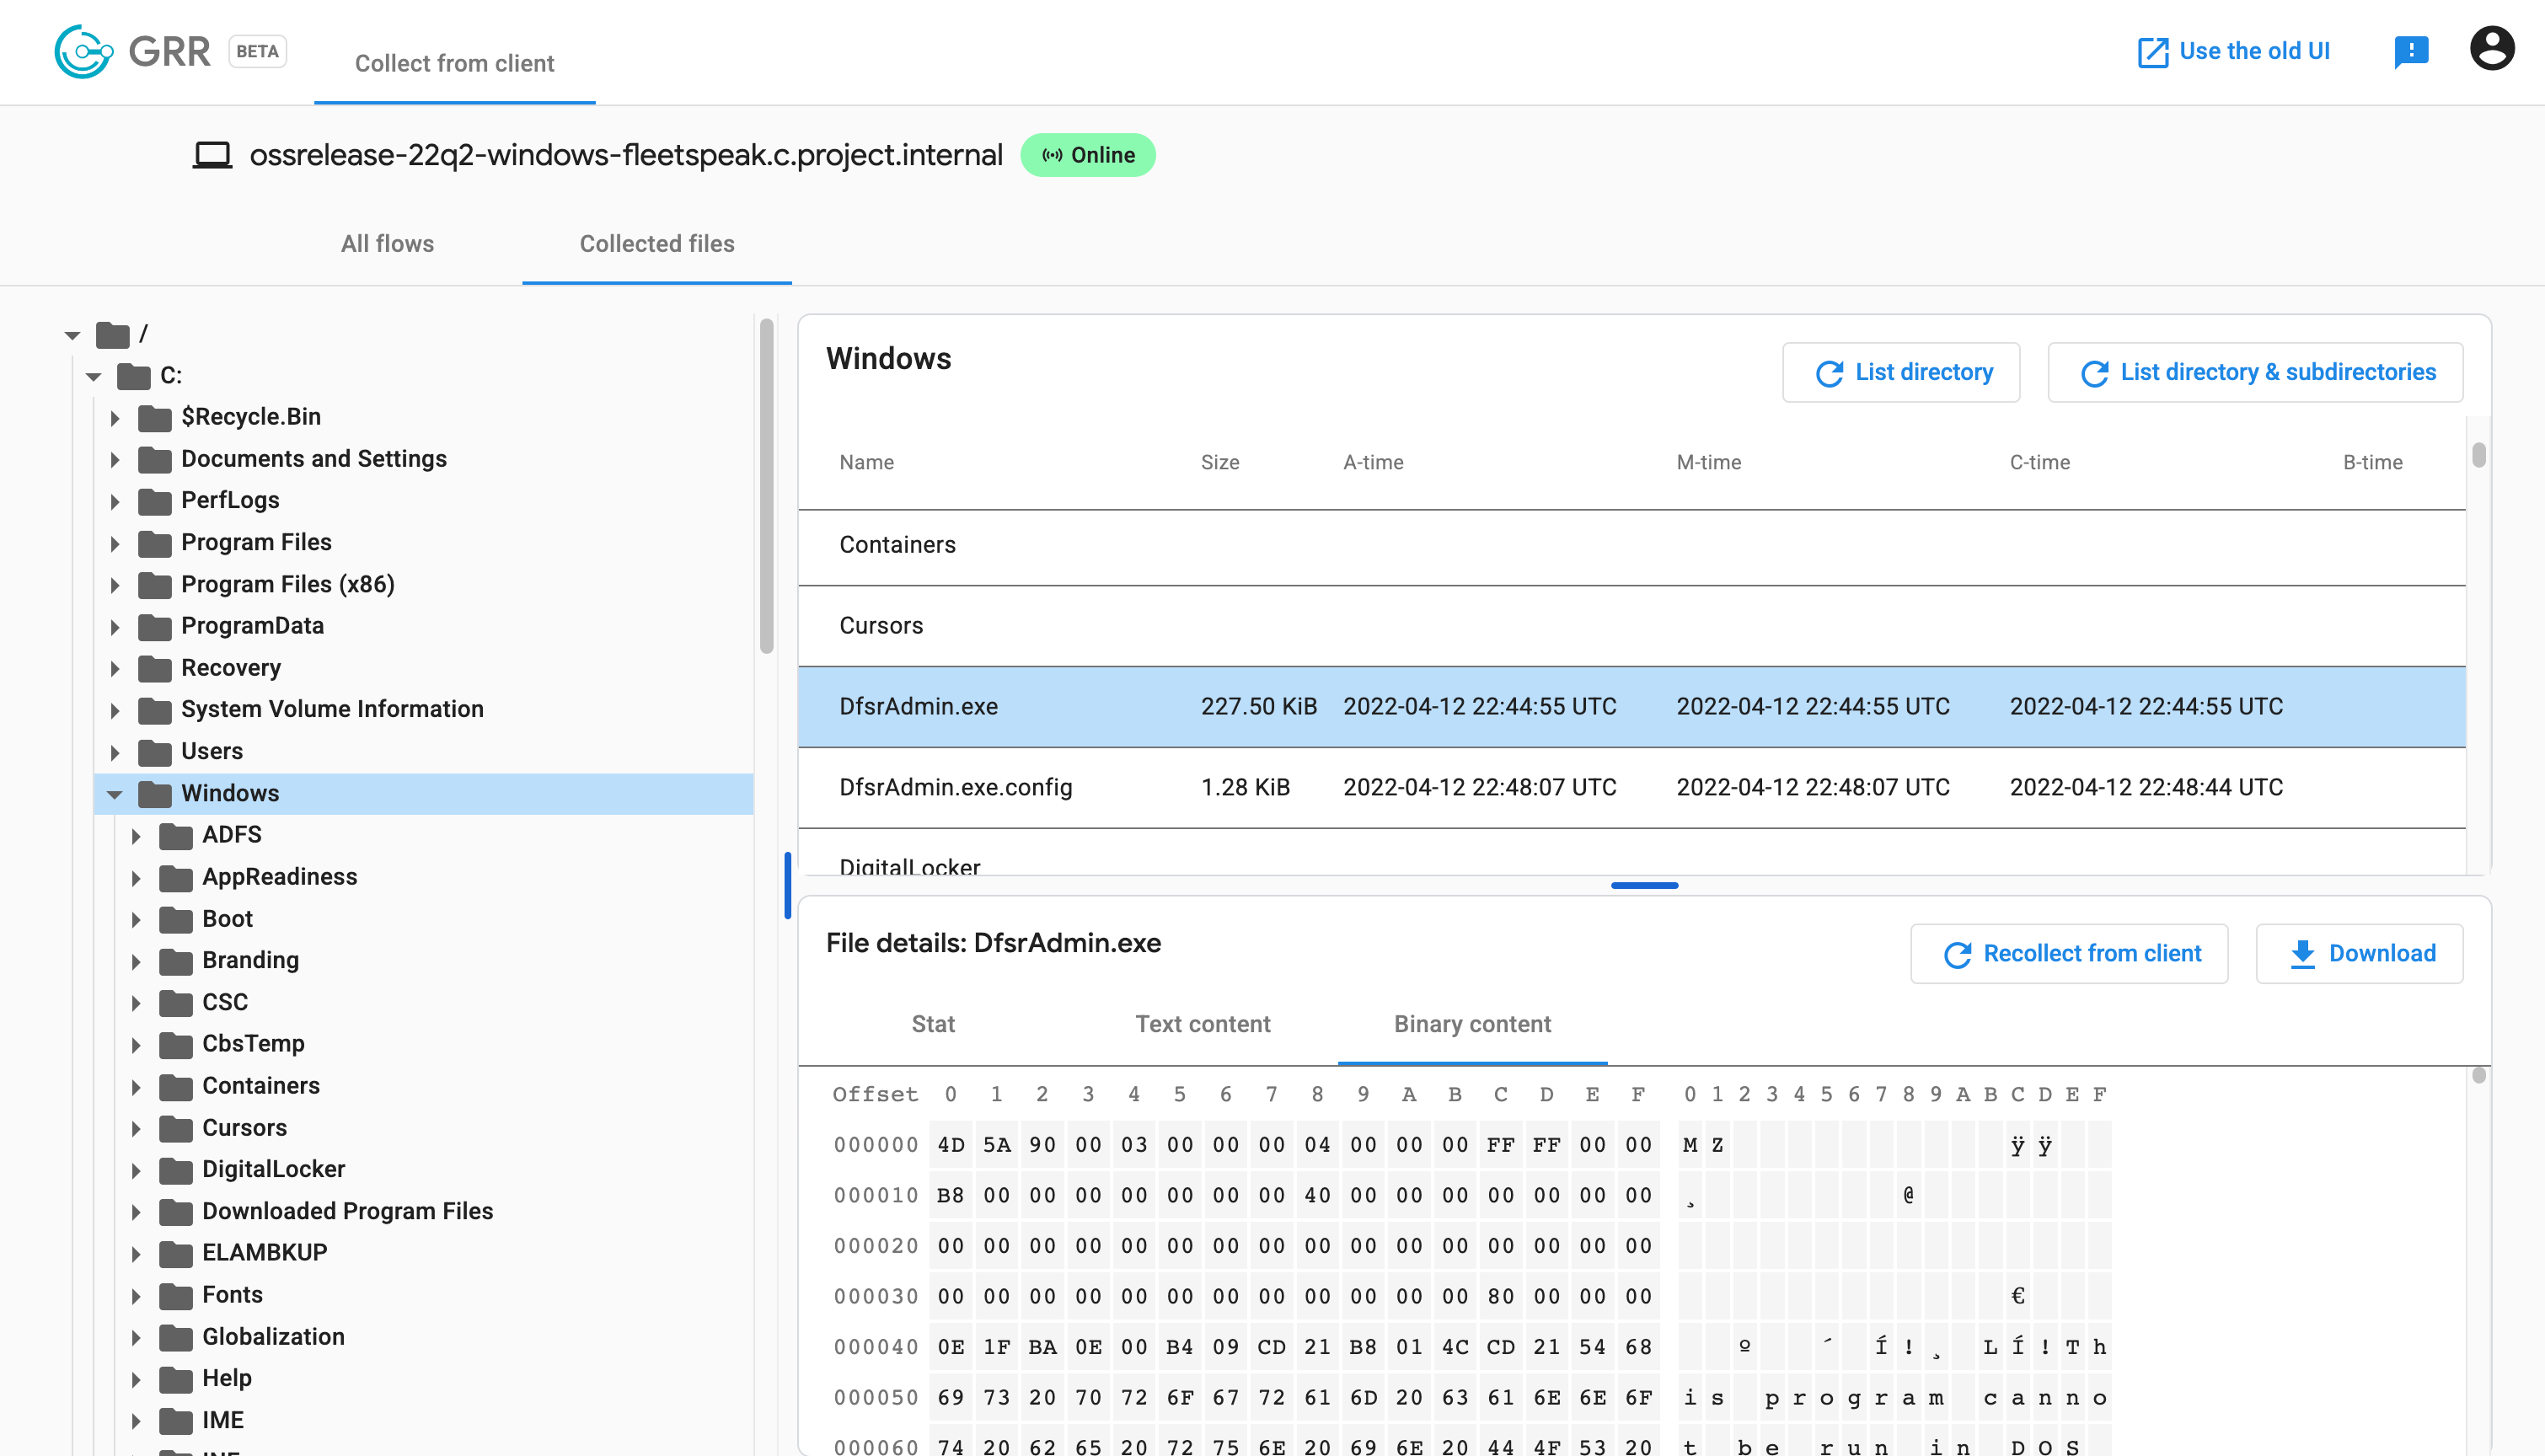 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
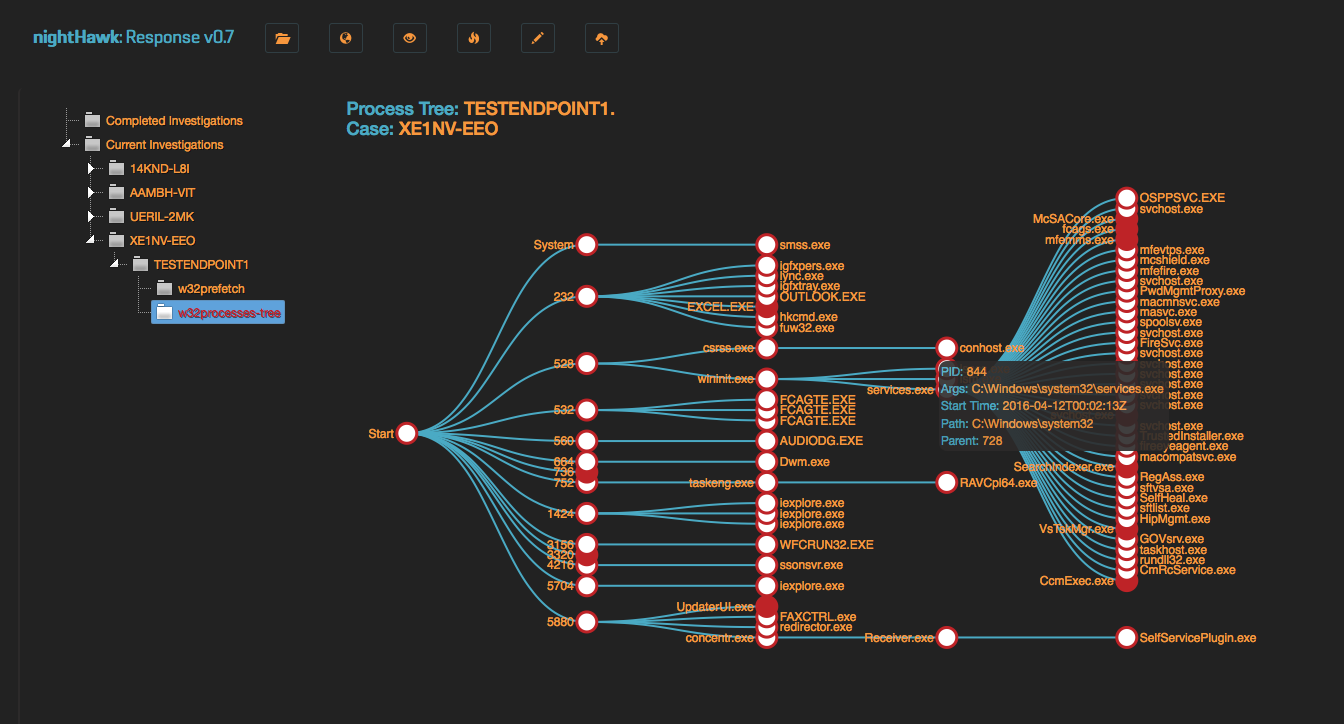 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
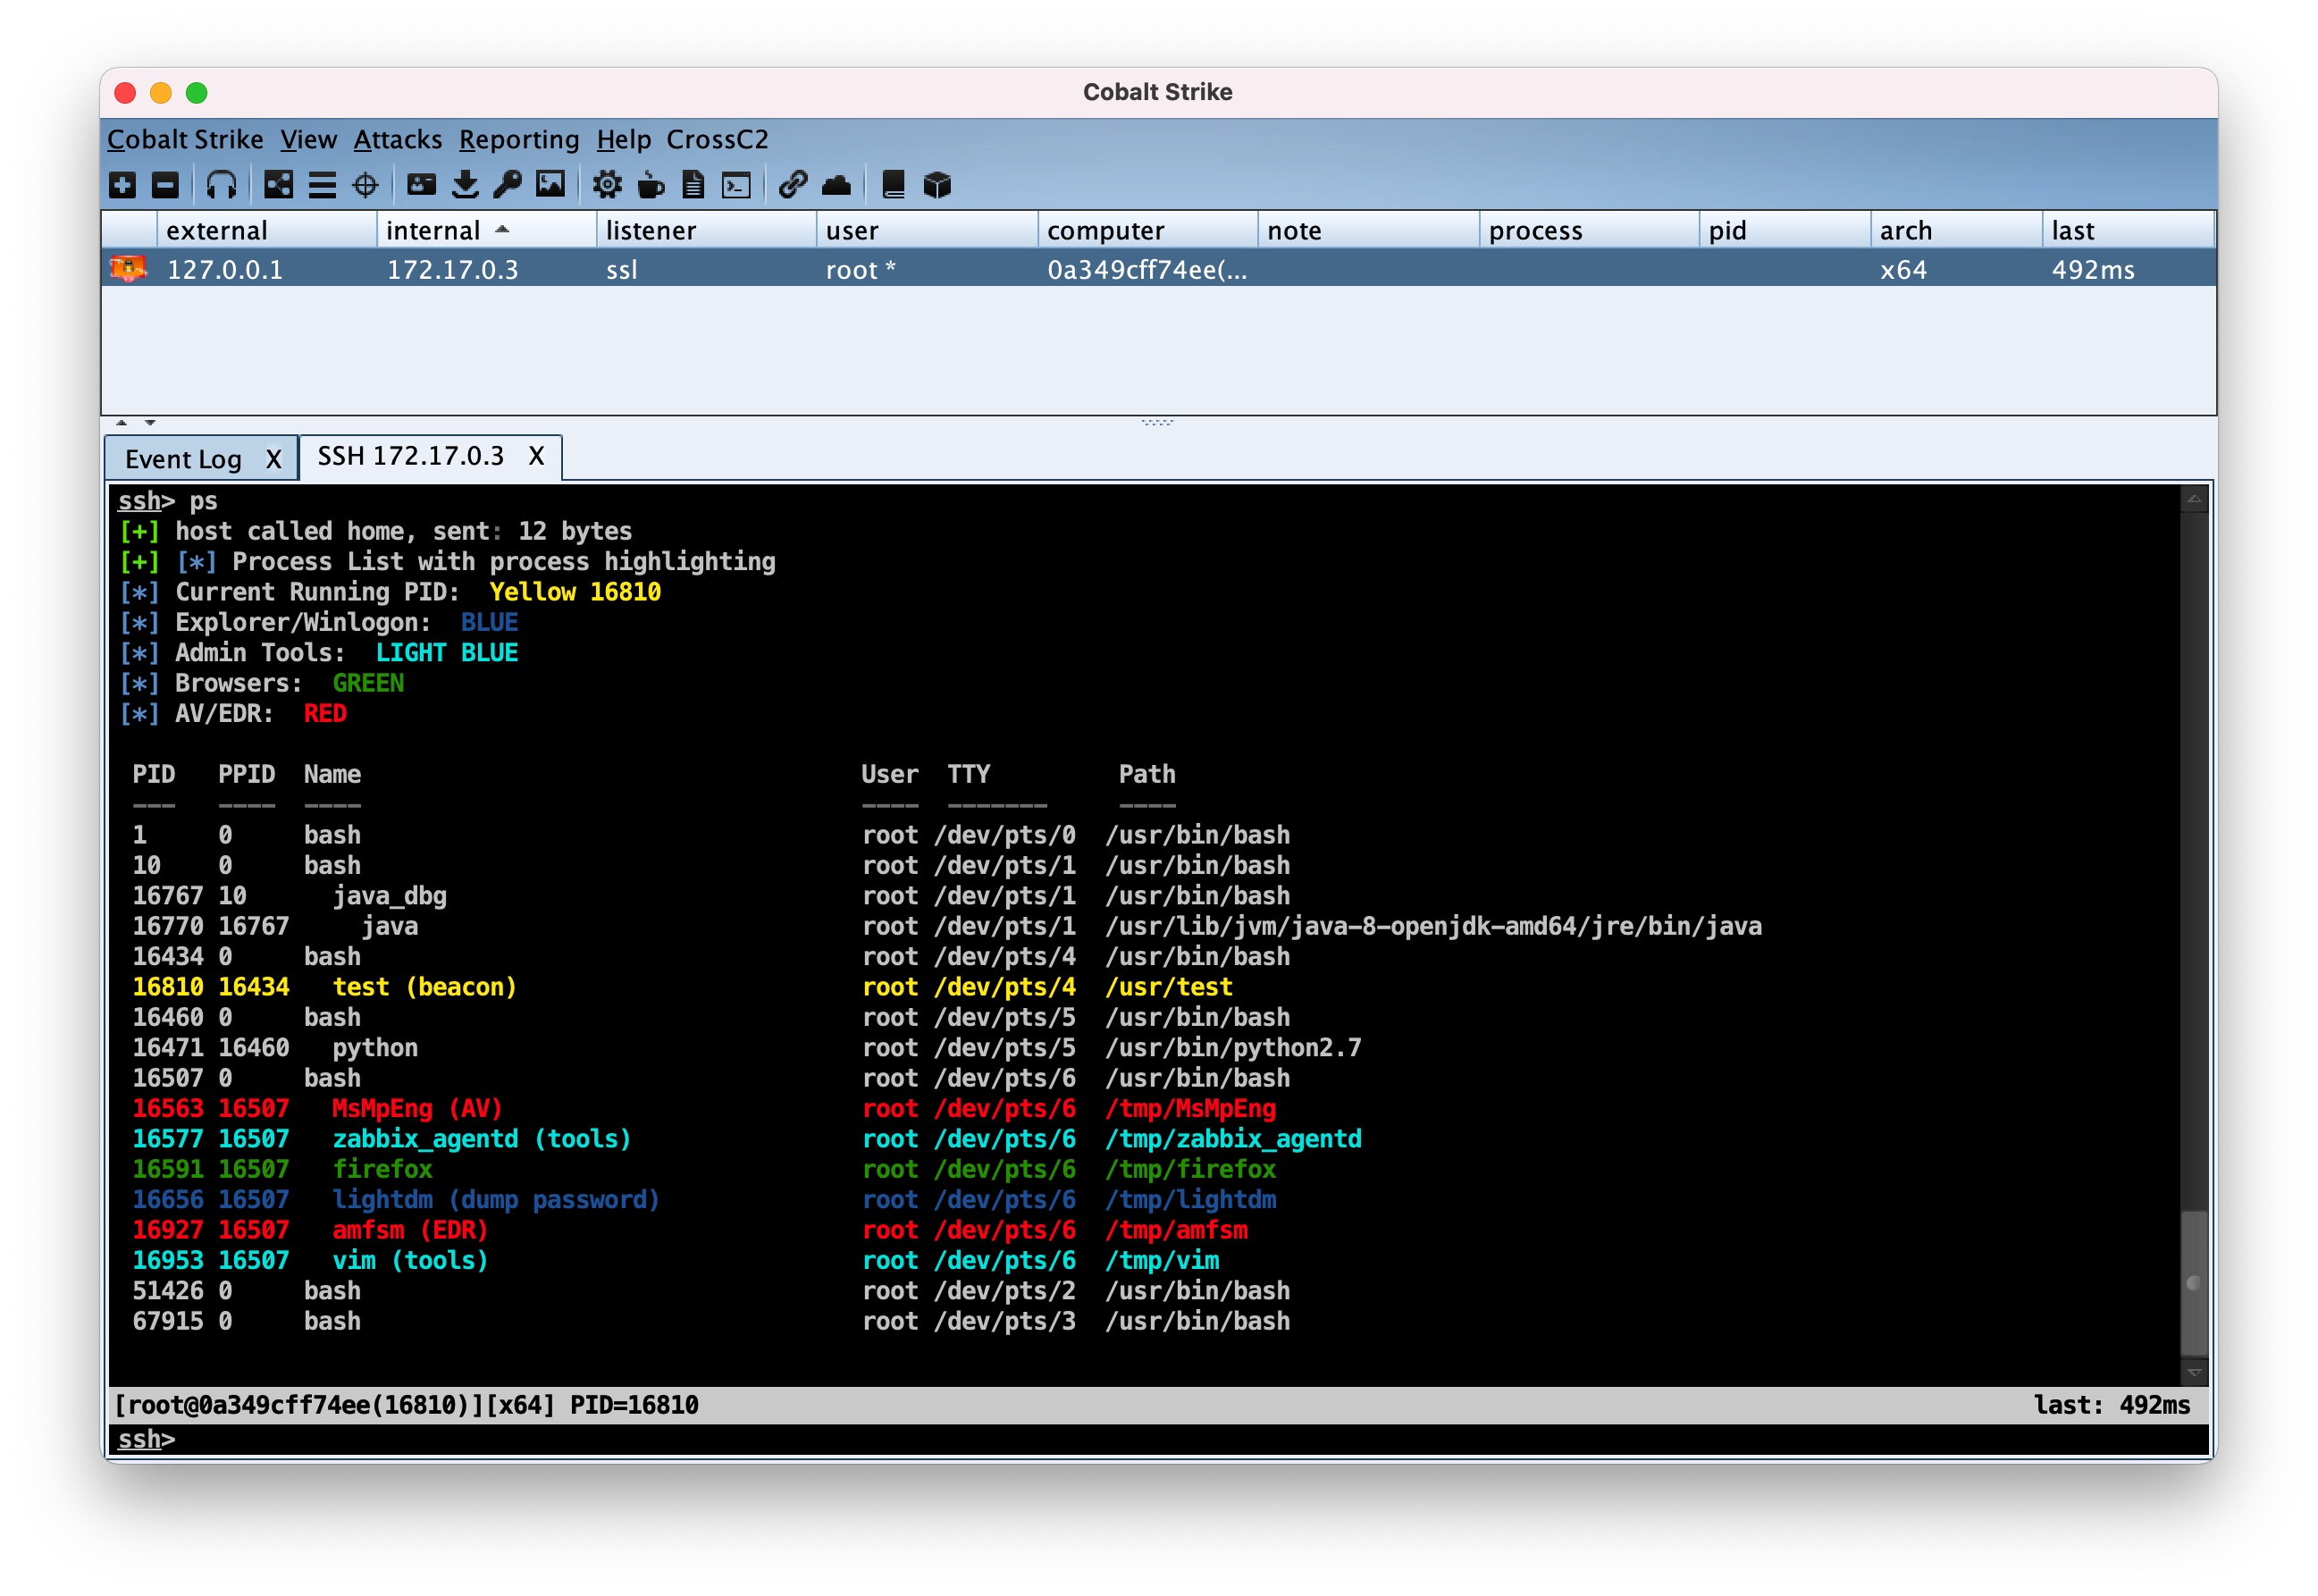 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…