

DeadMatter
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
qsecure-labs/deadmatterOffset Independent Credential Extraction Tool
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 blendin/3snake
Tool for extracting information from newly spawned processes
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 watchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451
Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
 egebalci/ticketbleed
This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
 bughuntar/cve-2025-5777
CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
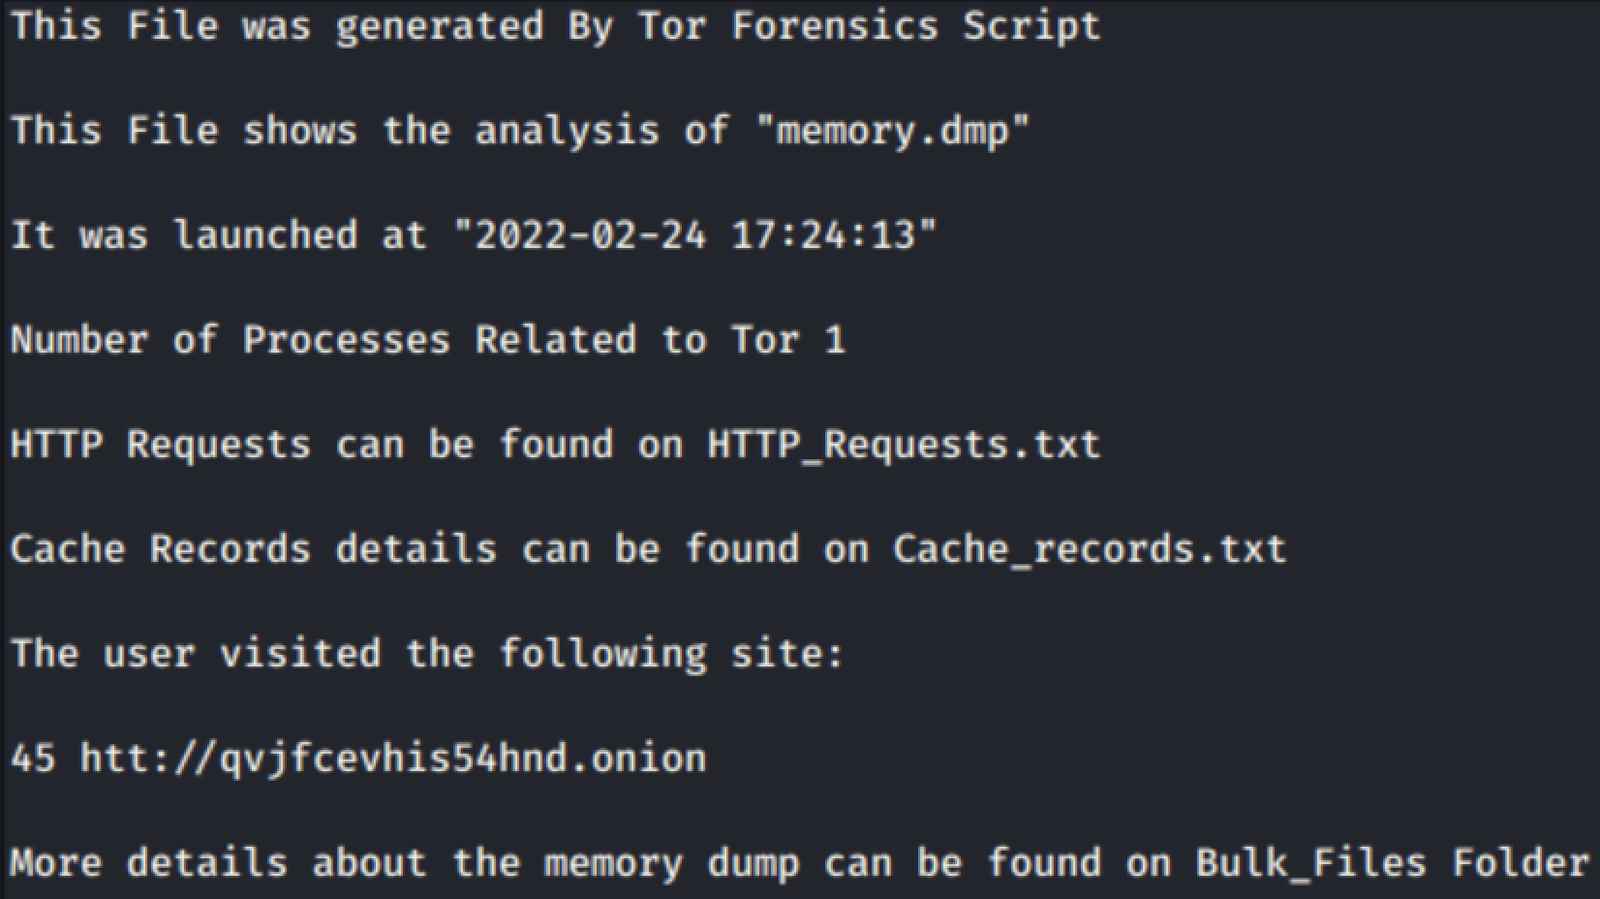 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
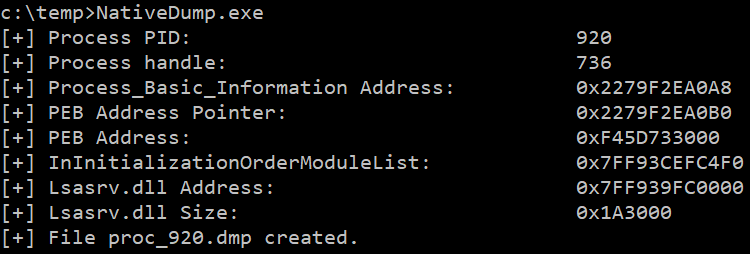 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 artemcyberlab/project-field-analysis-and-memory-leak-demonstration
The objective of this project was to assess a remote host for the Heartbleed vulnerability (CVE-2014-0160), verify its presence, and exploit it to…
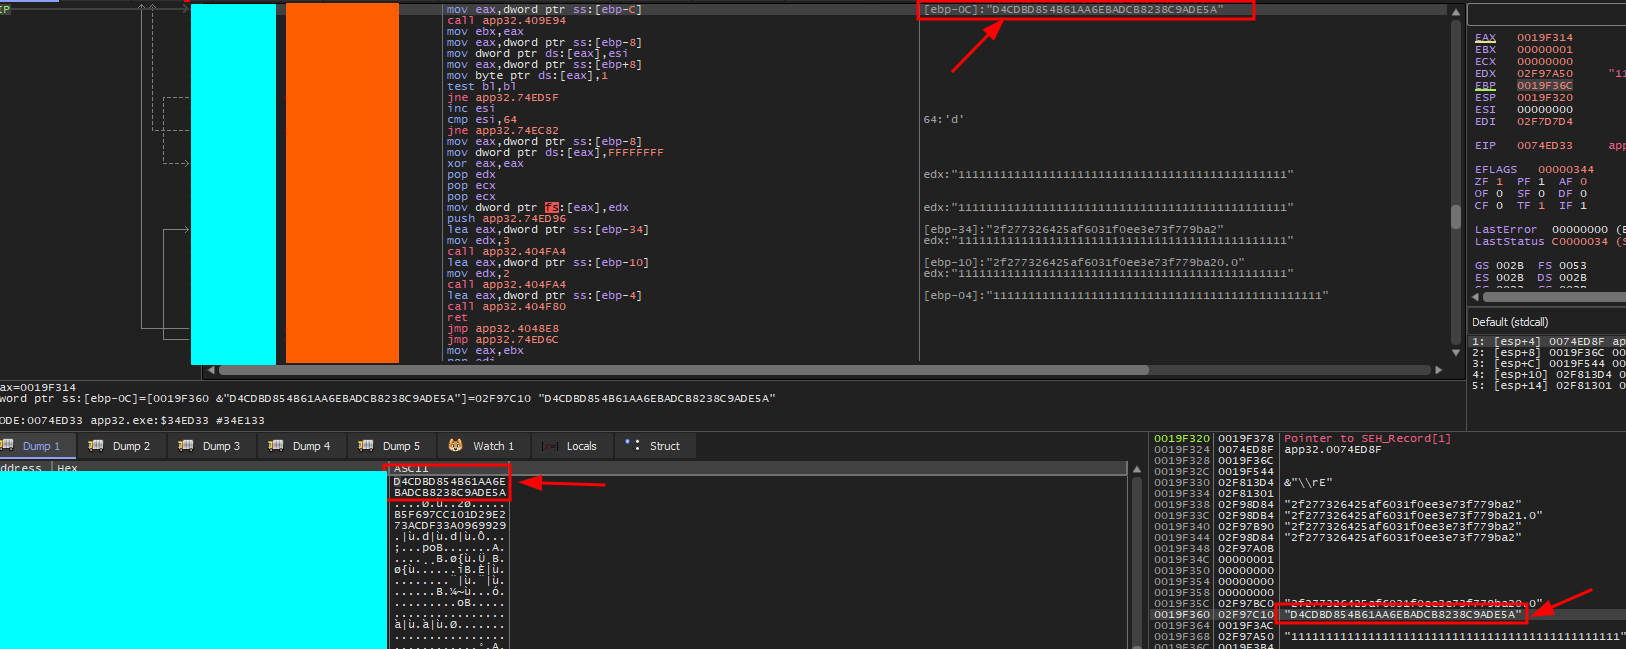 smarttfoxx/cve-2025-60791
Easywork Enterprise 2.1.3.354 is vulnerable to Cleartext Storage of Sensitive Information in Memory. The application leaves valid device-bound…