
DetectWindowsCopyOnWriteForAPI
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
anomaly-detectiondefensive-toolsforensics+3
198
nccgroup/detectwindowscopyonwriteforapiEnumerate various traits from Windows processes as an aid to threat hunting
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
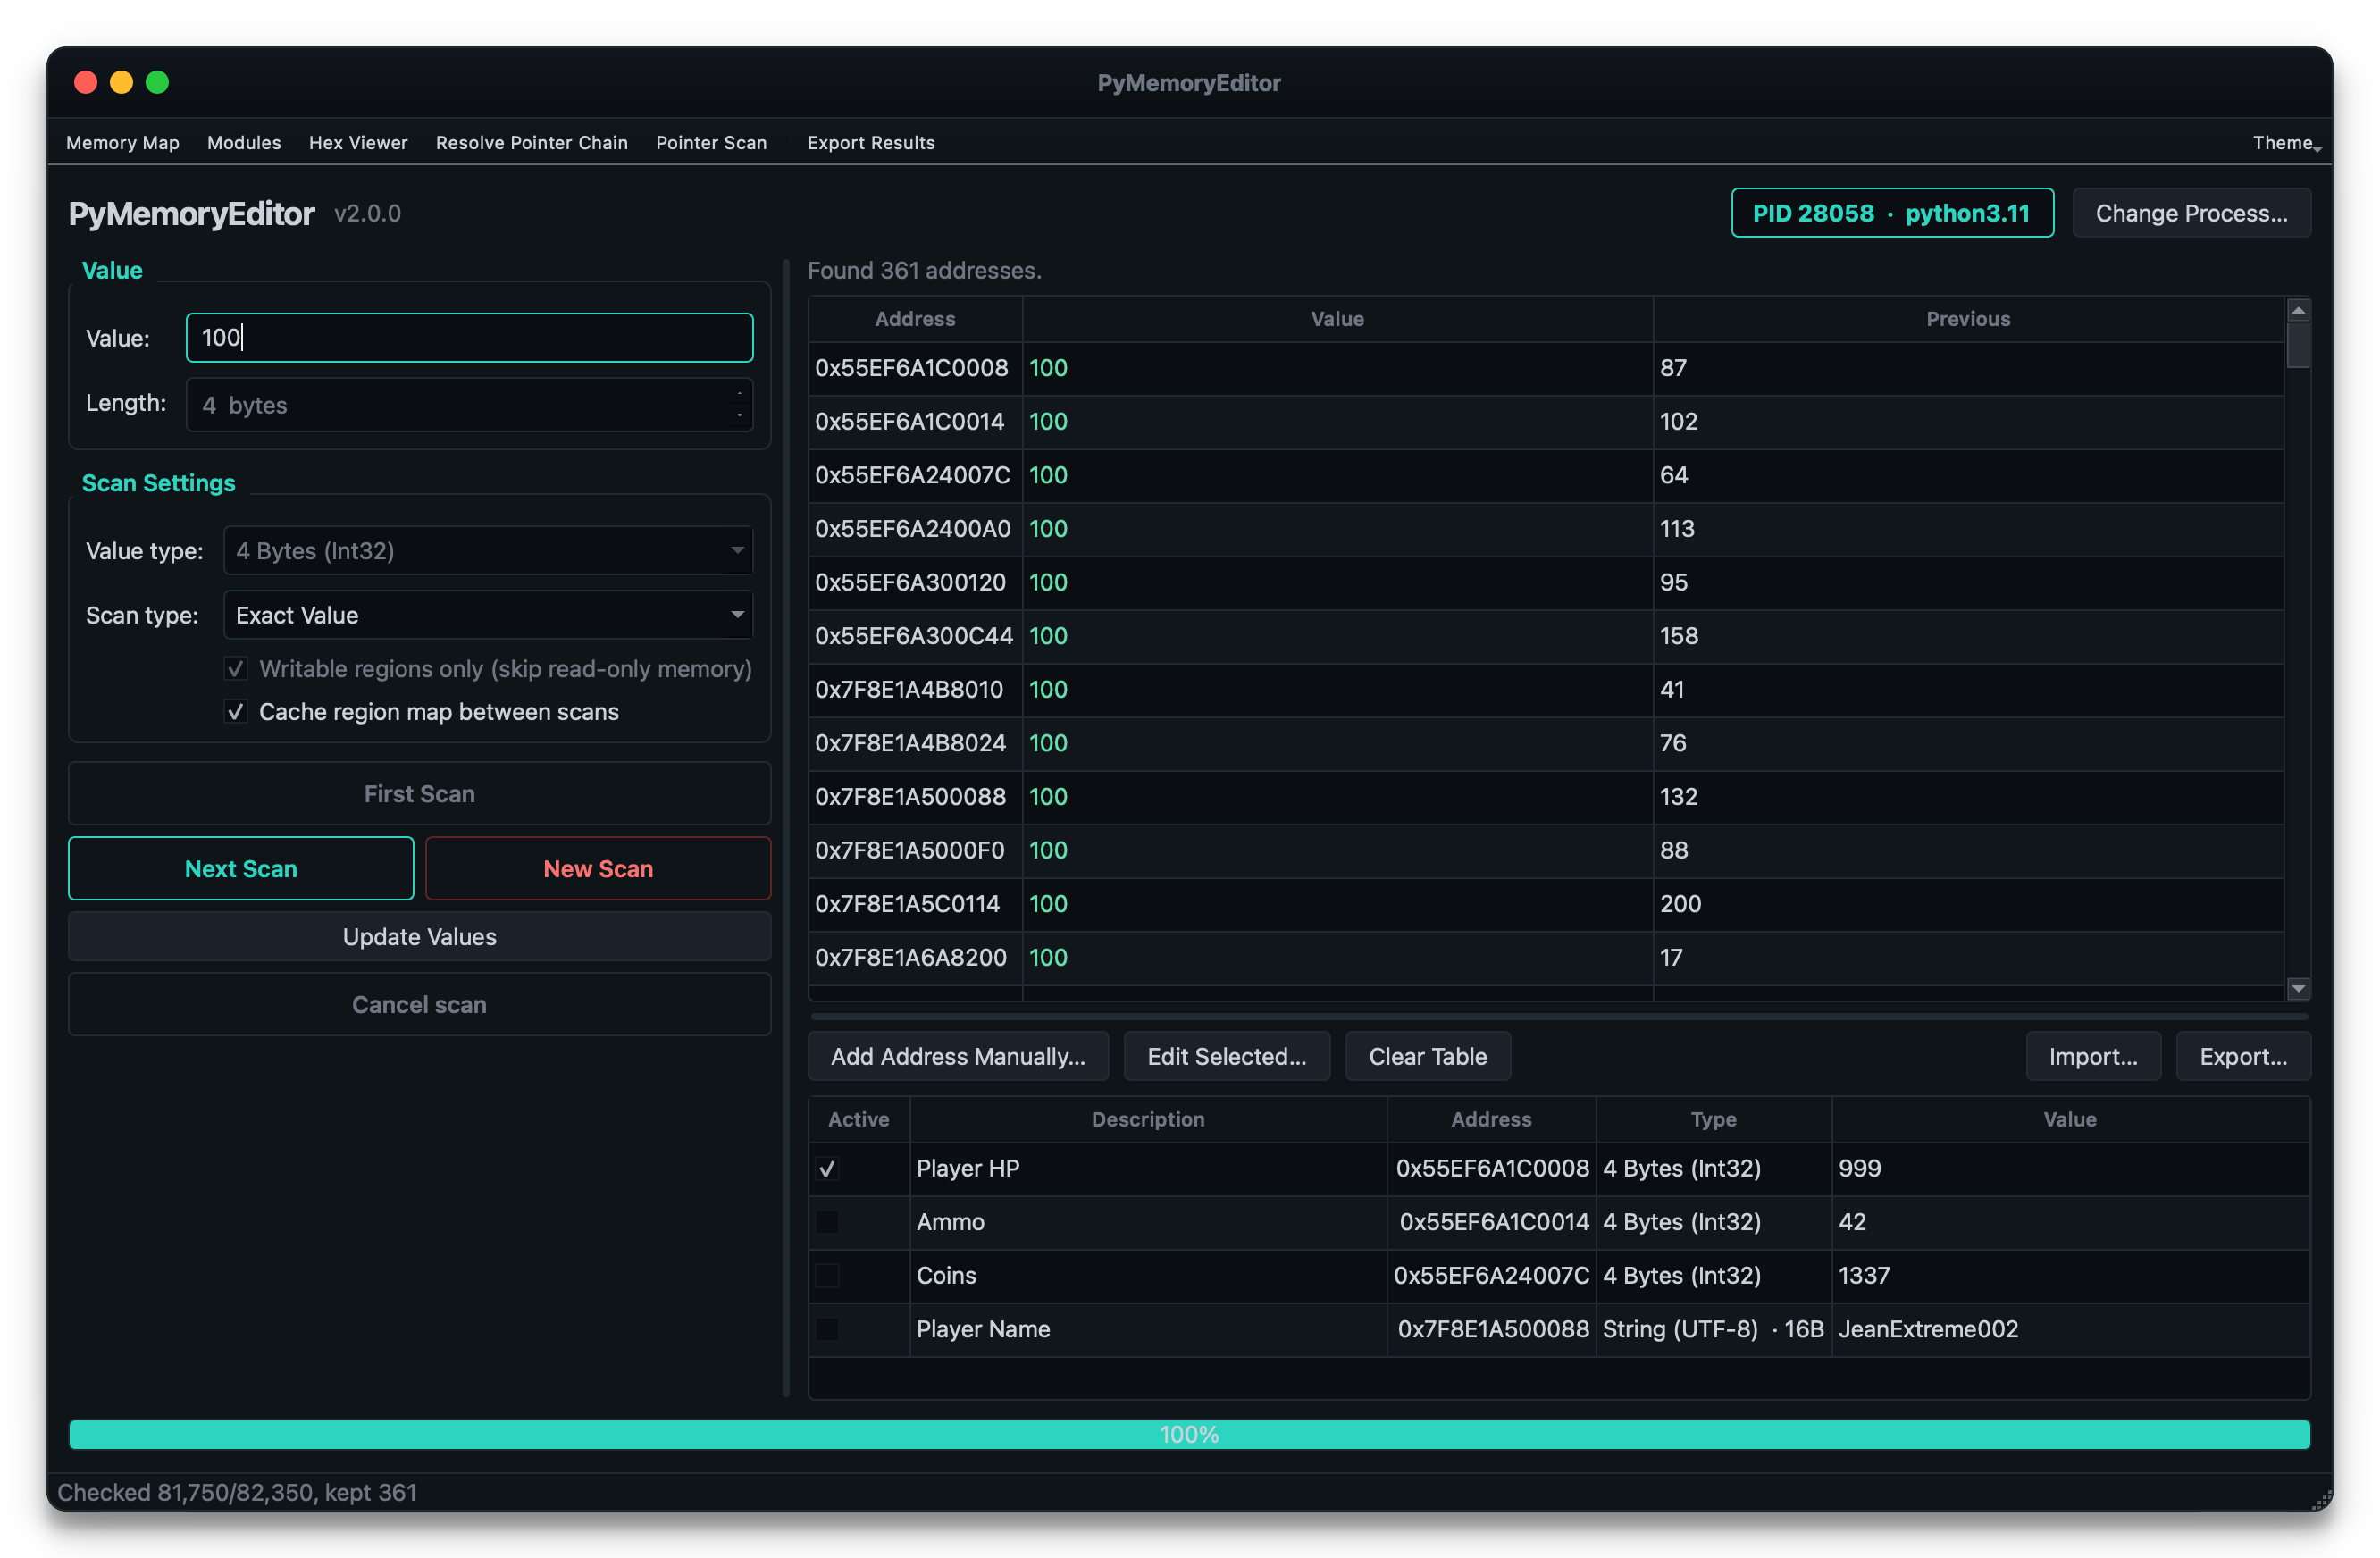 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
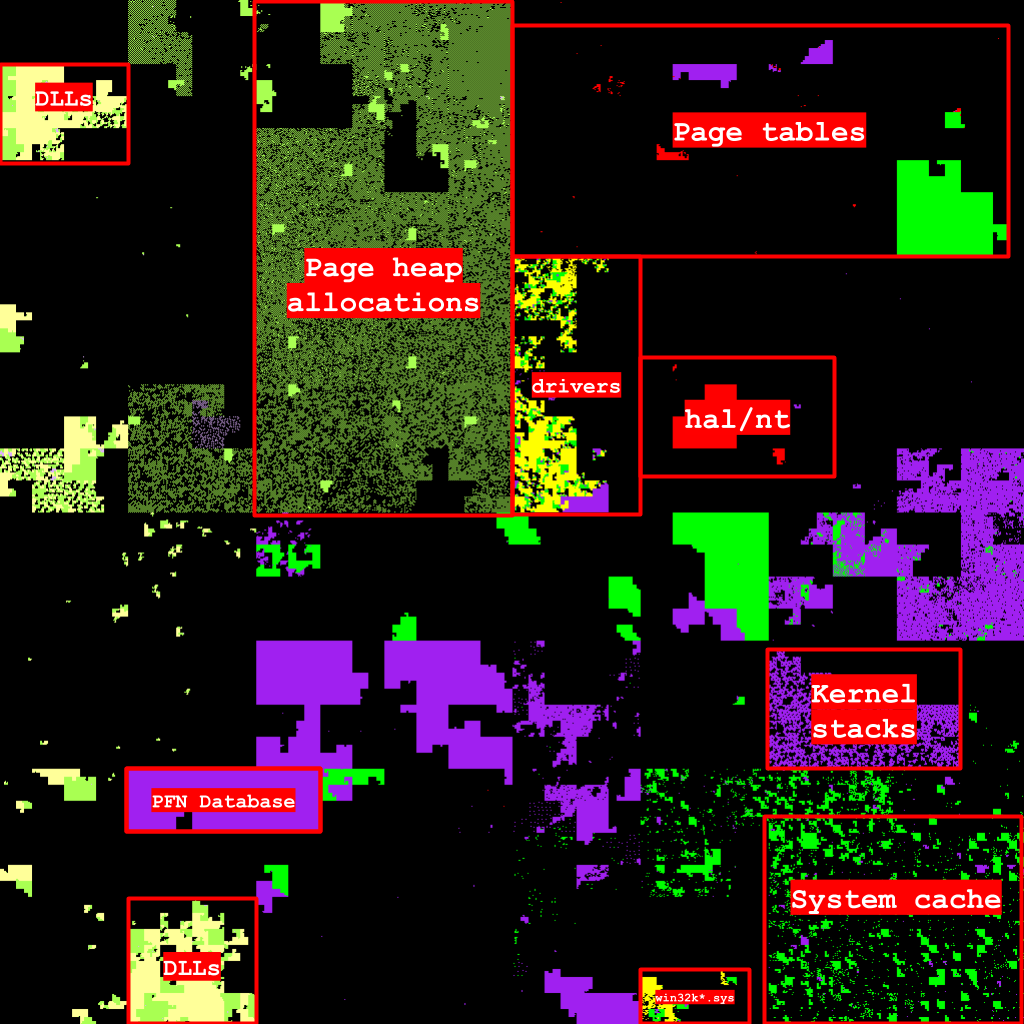 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
 fortra/nanodump
The swiss army knife of LSASS dumping
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
 v31l0x1/throttlestopppl
Poc for CVE-2025-7771 to modify PPL Protection
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 crackercat/cve-2021-44852
An issue was discovered in BS_RCIO64.sys in Biostar RACING GT Evo 2.1.1905.1700. A low-integrity process can open the driver's device object and…