
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
103 results
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k
3 years ago
inception preview

inception

GitHubcarmaa/inception

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
digital-forensicsexploitationhardware-security+6
1.6k1 year ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk
android-securitybinary-analysismemory-forensics+2
4343 days ago
SentinelNav preview

SentinelNav

GitHubsmolfiddle/sentinelnav

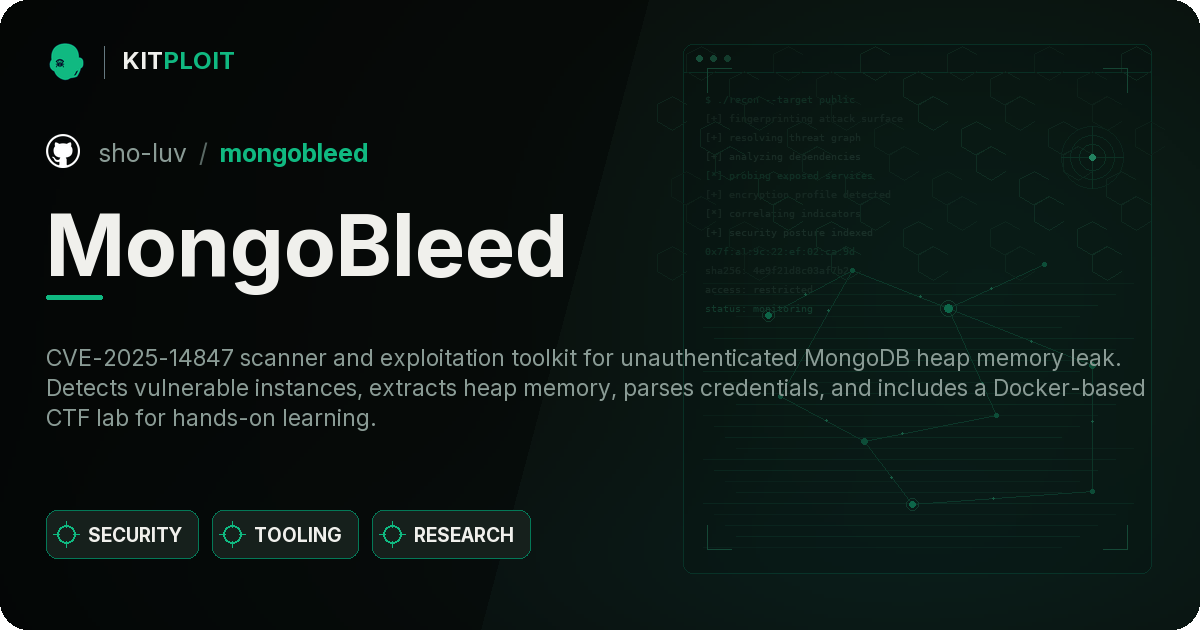
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
binary-analysisdata-recoverydigital-forensics+4
1489 months ago
MongoBleed preview

MongoBleed

GitHubsho-luv/mongobleed

CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
ctfdatabase-securityeducation+6
27 months ago
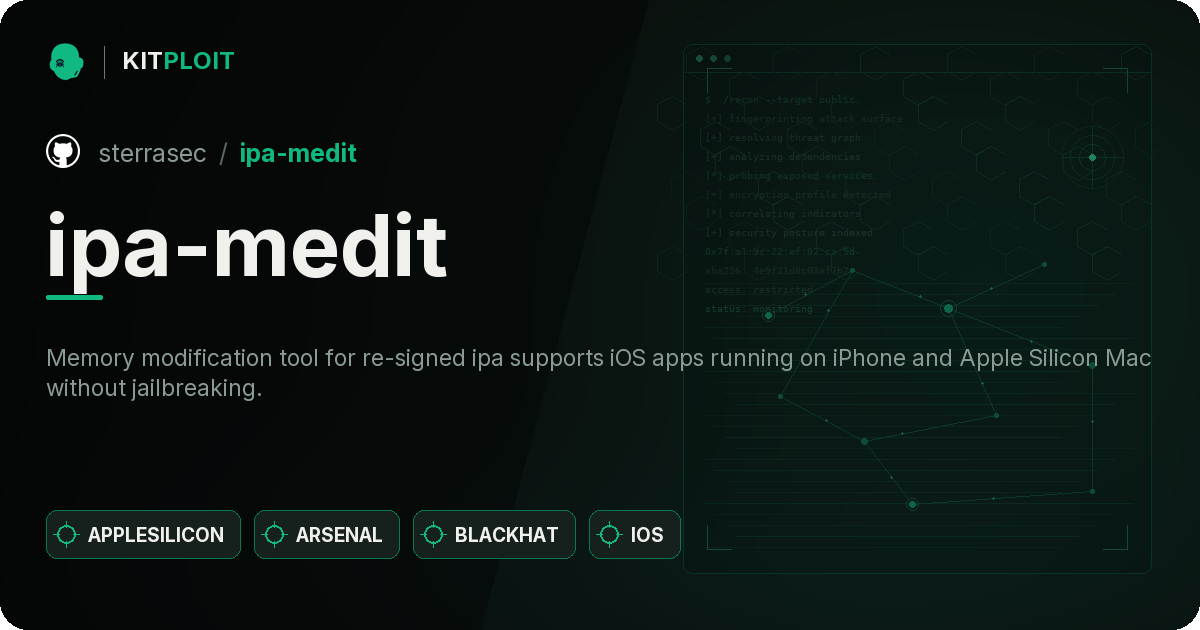
BLUESPAWN preview

BLUESPAWN

GitHubion28/bluespawn

An Active Defense and EDR software to empower Blue Teams
configuration-auditingdefensive-toolsincident-response+3
1.3k5 months ago
ipa-medit preview

ipa-medit

GitHubsterrasec/ipa-medit

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

binary-analysisios-securitymemory-forensics+3
2101 year ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k15 days ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
digital-forensicsforensicsincident-response+1
1.1k10h 23m ago
MultiDump preview

MultiDump

GitHubxre0us/multidump

MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
encryption-decryption-toolslateral-movementmemory-forensics+4
54110 months ago
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…

binary-analysisfirmware-analysisfuzzing+3
2221 year ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
672 months ago
invoker preview
Archived

invoker

GitHubivan-sincek/invoker

Penetration testing utility and antivirus assessment tool.
binary-analysiseducationexploitation+6
3123 years ago
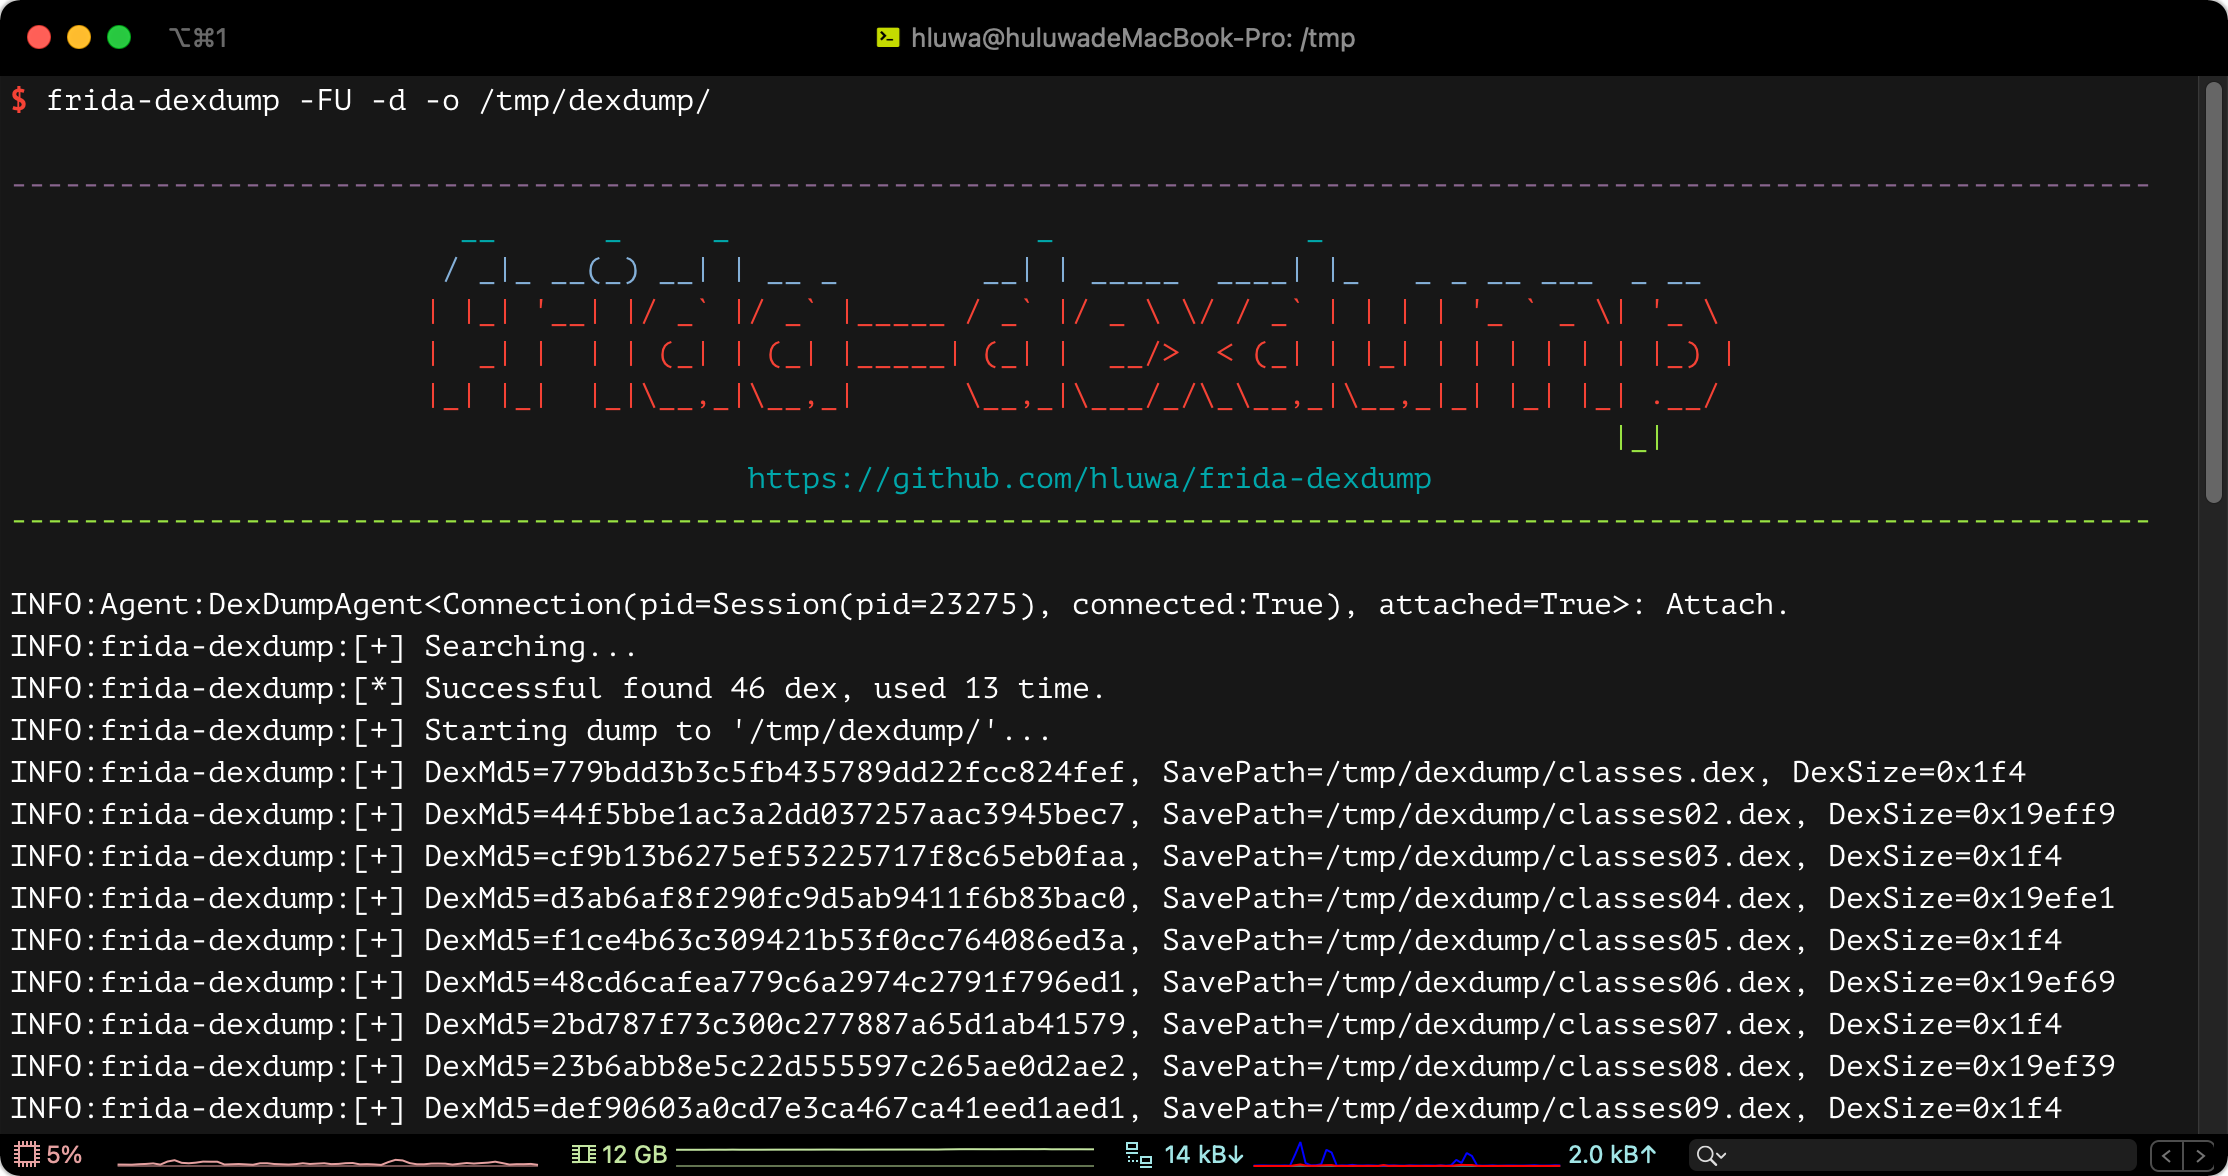
frida-dexdump preview
Archived

frida-dexdump

GitHubhluwa/frida-dexdump

A frida tool to dump dex in memory to support security engineers analyzing malware.
android-securitybinary-analysisdynamic-analysis-sandboxing+5
4.6k3 years ago
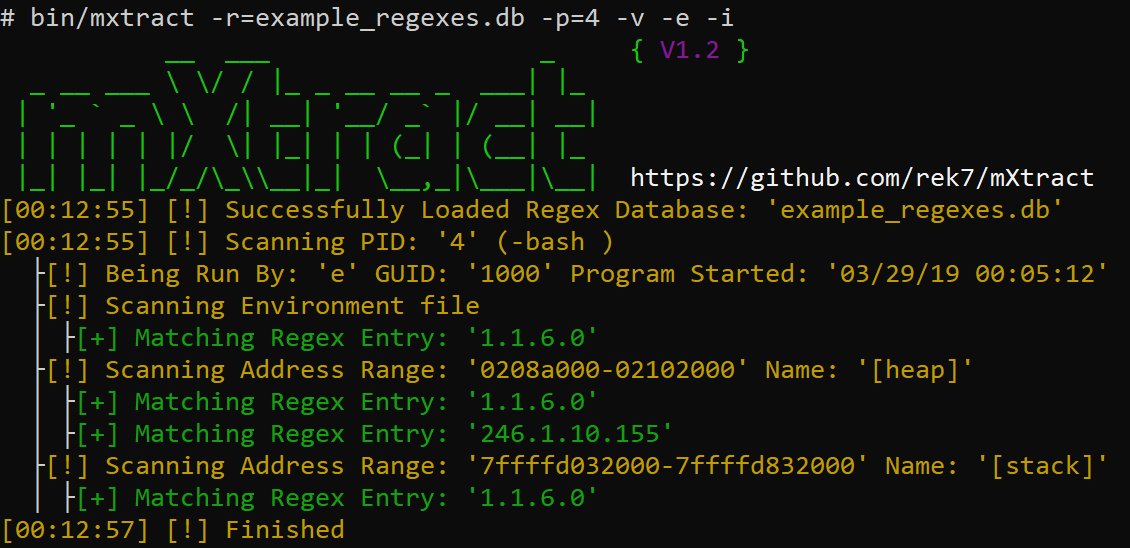
mXtract preview

mXtract

GitHubrek7/mxtract

mXtract - Memory Extractor & Analyzer
forensicsinformation-gatheringmemory-forensics+2
5874 years ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel

binary-analysisdebuggerseducation+2
1578 years ago
silph preview

silph

GitHubalmounah/silph

Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
authenticationmemory-forensicspassword-cracking+3
1669 months ago
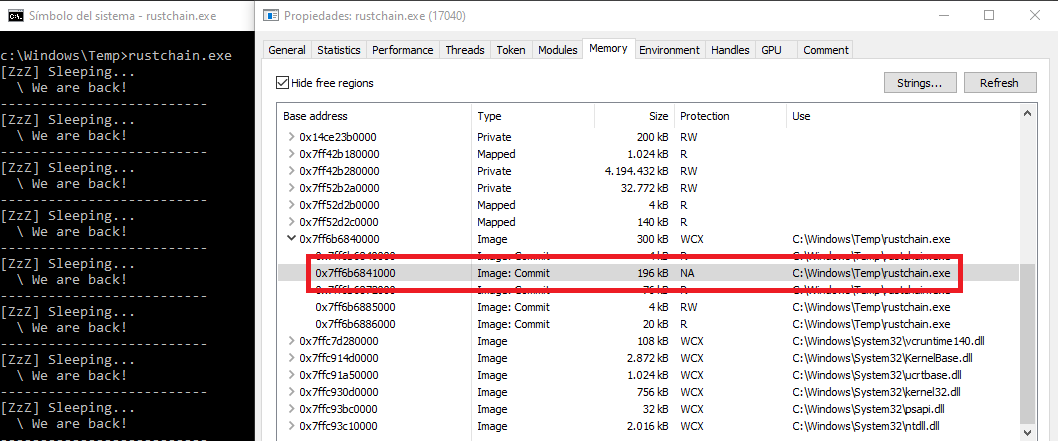
RustChain preview

RustChain

GitHubkudaes/rustchain

Hide memory artifacts using ROP and hardware breakpoints.

exploitationmemory-forensicspayload-development+1
1502 years ago
Previous123456Next