

YAMA-dev
 t-tani/yama-dev
Yet Another Memory Analyzer for malware detection
forensicsincident-responsemalware-analysis+1
243 years ago
t-tani/yama-devYet Another Memory Analyzer for malware detection
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
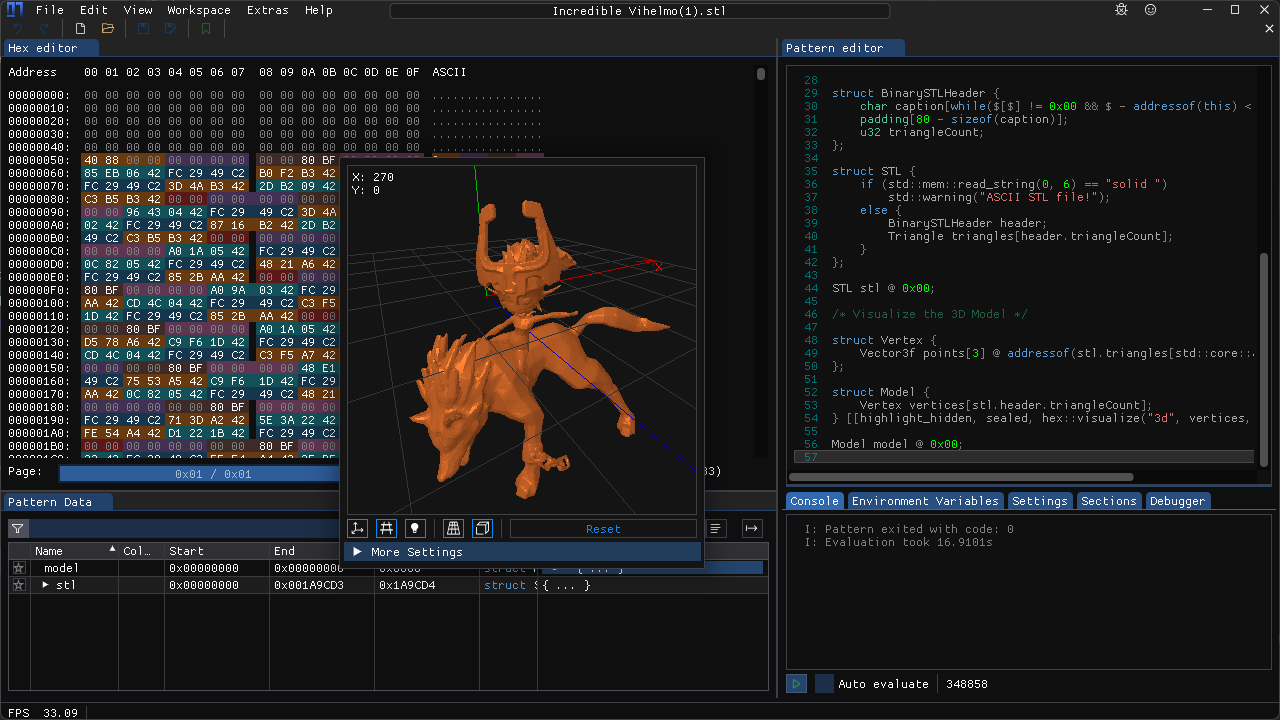 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
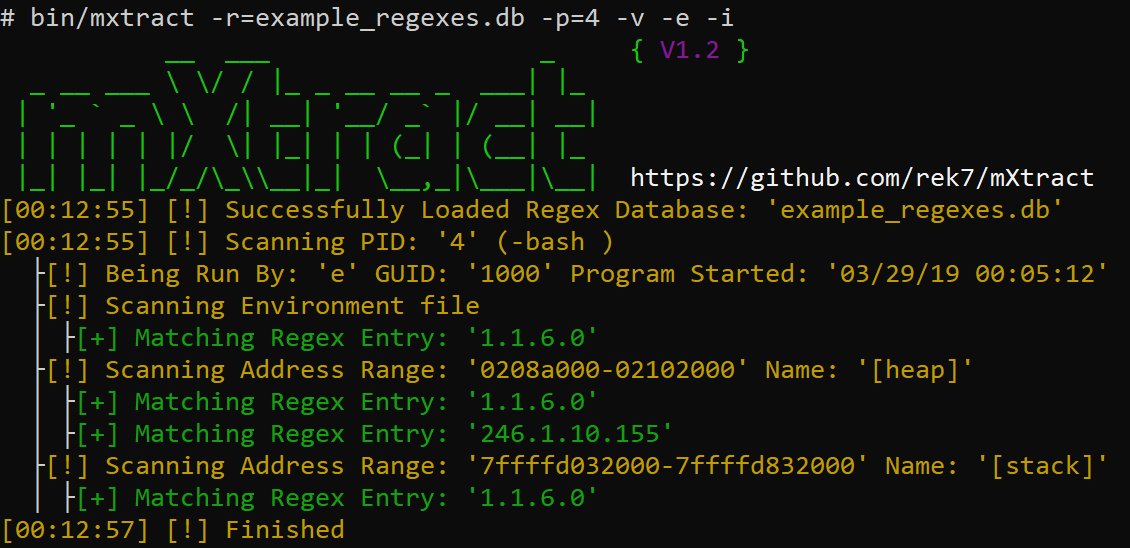 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
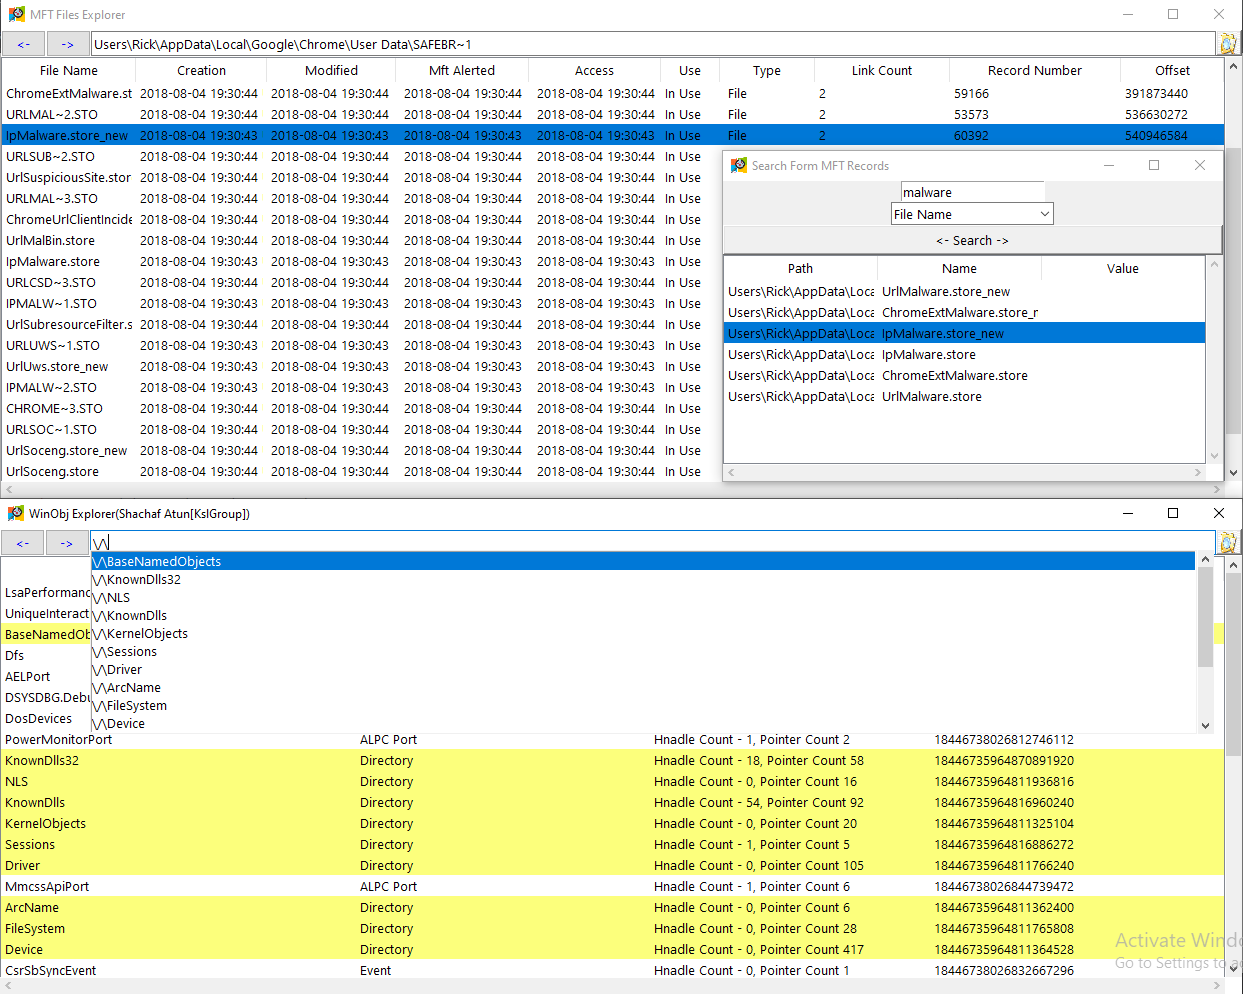 memoryforensics1/vol3xp
Volatility Explorer Suit (volatility 3)
 nccgroup/memaddressanalysis
Research project related to memory address analysis