
sshkey-grab
 netspi/sshkey-grab
Grab ssh keys from ssh-agent
exploitationmemory-forensicspost-exploitation
netspi/sshkey-grabGrab ssh keys from ssh-agent
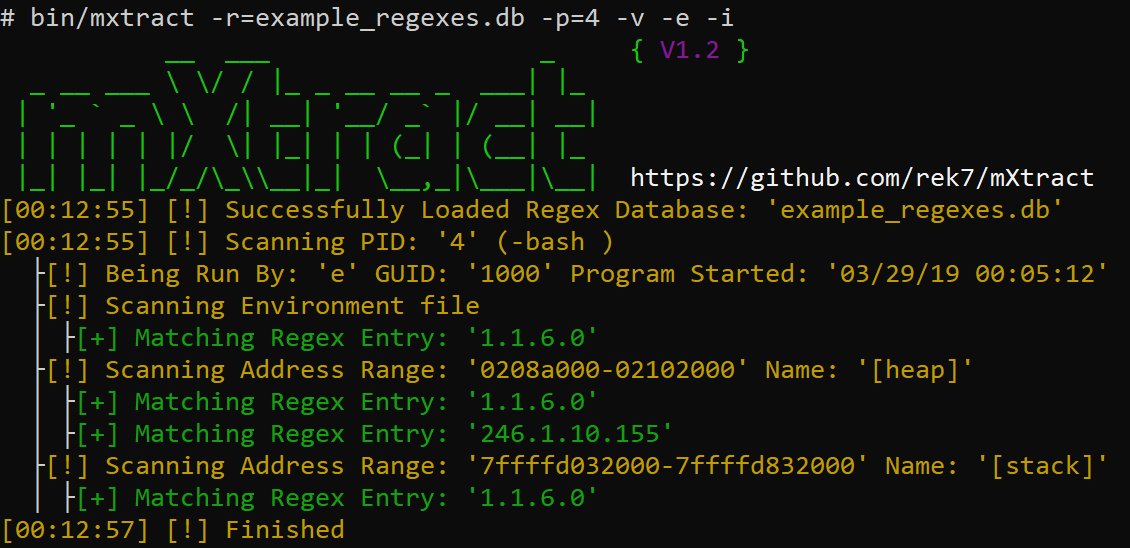 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 blendin/3snake
Tool for extracting information from newly spawned processes
 nccgroup/libmempool
Heap analysis tooling for mempool
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
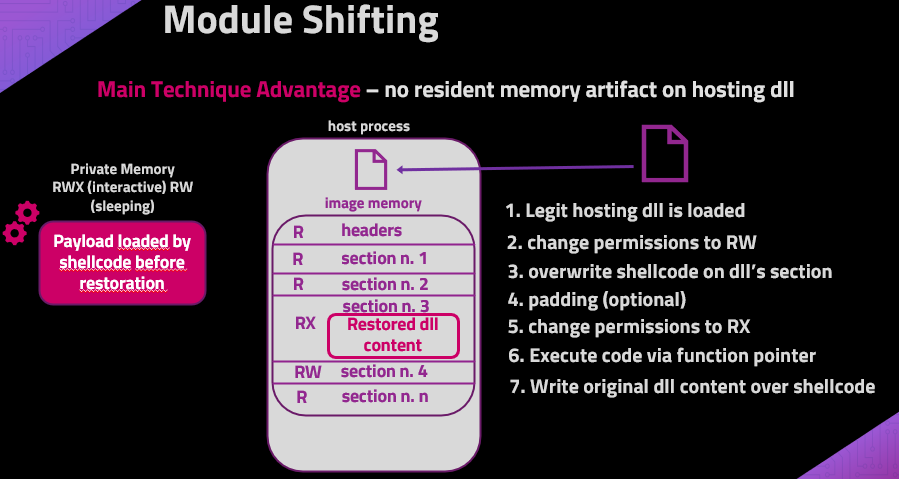 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
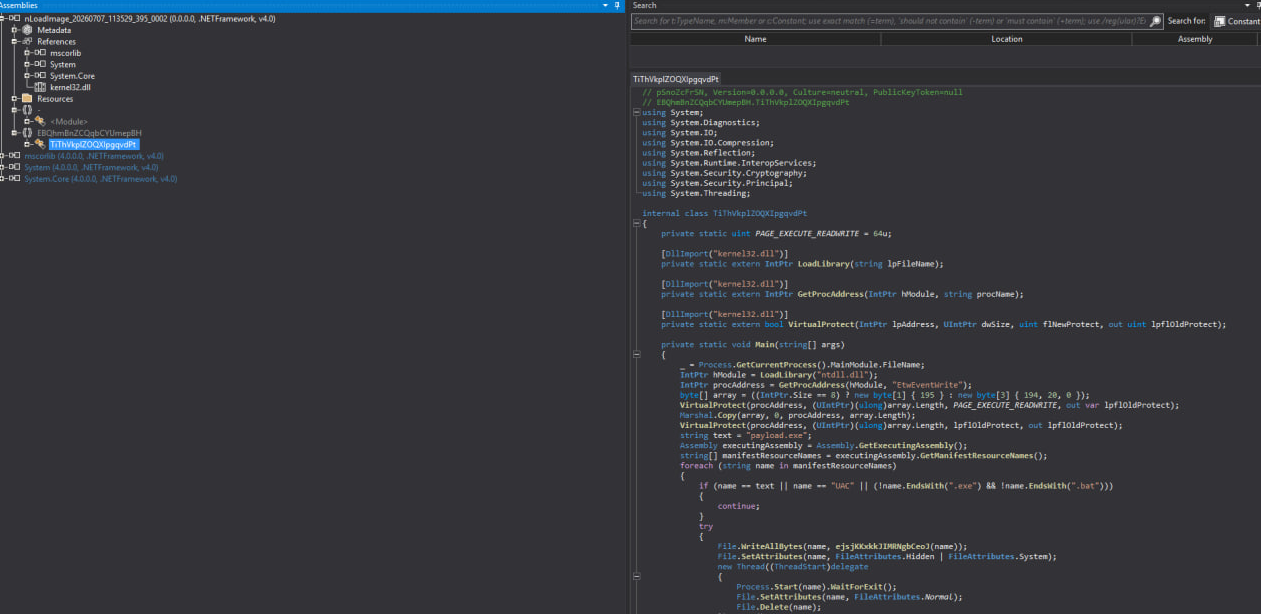 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…
 markuta/bw-dump
A proof-of-concept for (CVE-2023-38840) that extracts plaintext master passwords from a locked Bitwarden vault.
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
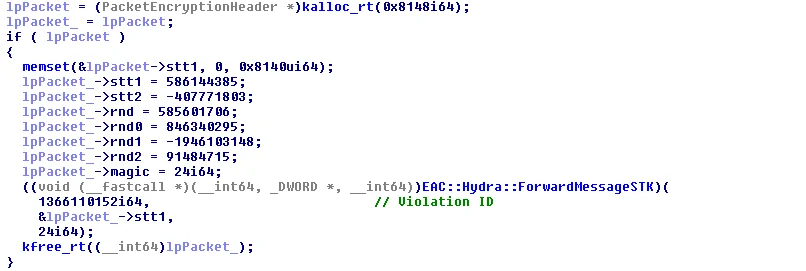 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.