

ModuleShifting
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
binary-exploitationmemory-forensicspayload-development+1
135
naksyn/moduleshiftingStealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
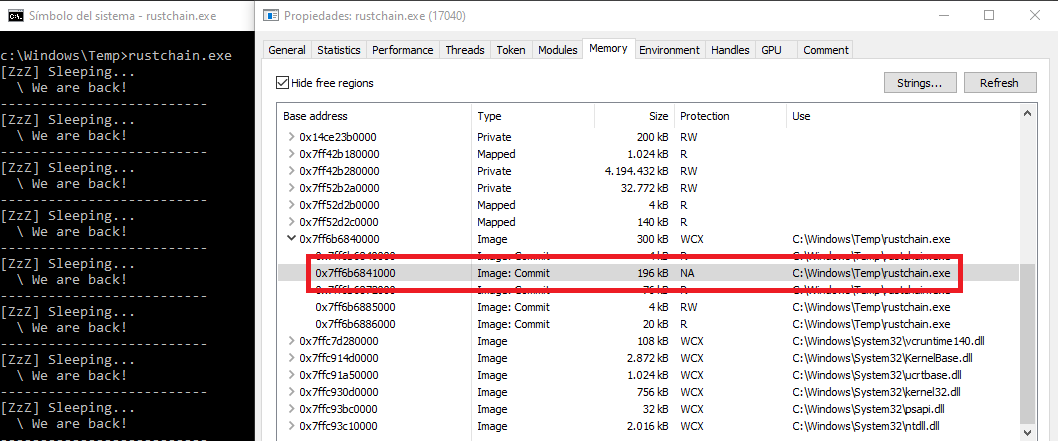 kudaes/rustchain
Hide memory artifacts using ROP and hardware breakpoints.
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 darthton/blackbone
Windows memory hacking library
 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 0neday/multi_path
CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer
 shirabo/cve-2025-2082-pov
Proof-of-Concept for CVE-2025-2082, demonstrating function pointer overwrite via signed-to-unsigned integer conversion bug in Tesla VCSEC, leading to…
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking