
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
39 results
mimikittenz preview

mimikittenz

GitHuborlyjamie/mimikittenz

A post-exploitation powershell tool for extracting juicy info from memory.
information-gatheringmemory-forensicspenetration-testing+1
1.9k
6 years ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.5k1 month ago
mongobleed preview

mongobleed

GitHubjoe-desimone/mongobleed

Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
database-securityexploitationinformation-gathering+3
94610 months ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
digital-forensicsforensicsinformation-gathering+3
8627 years ago
bmc-tools preview

bmc-tools

GitHubanssi-fr/bmc-tools

RDP Bitmap Cache parser

digital-forensicsforensicsinformation-gathering+1
6996 months ago
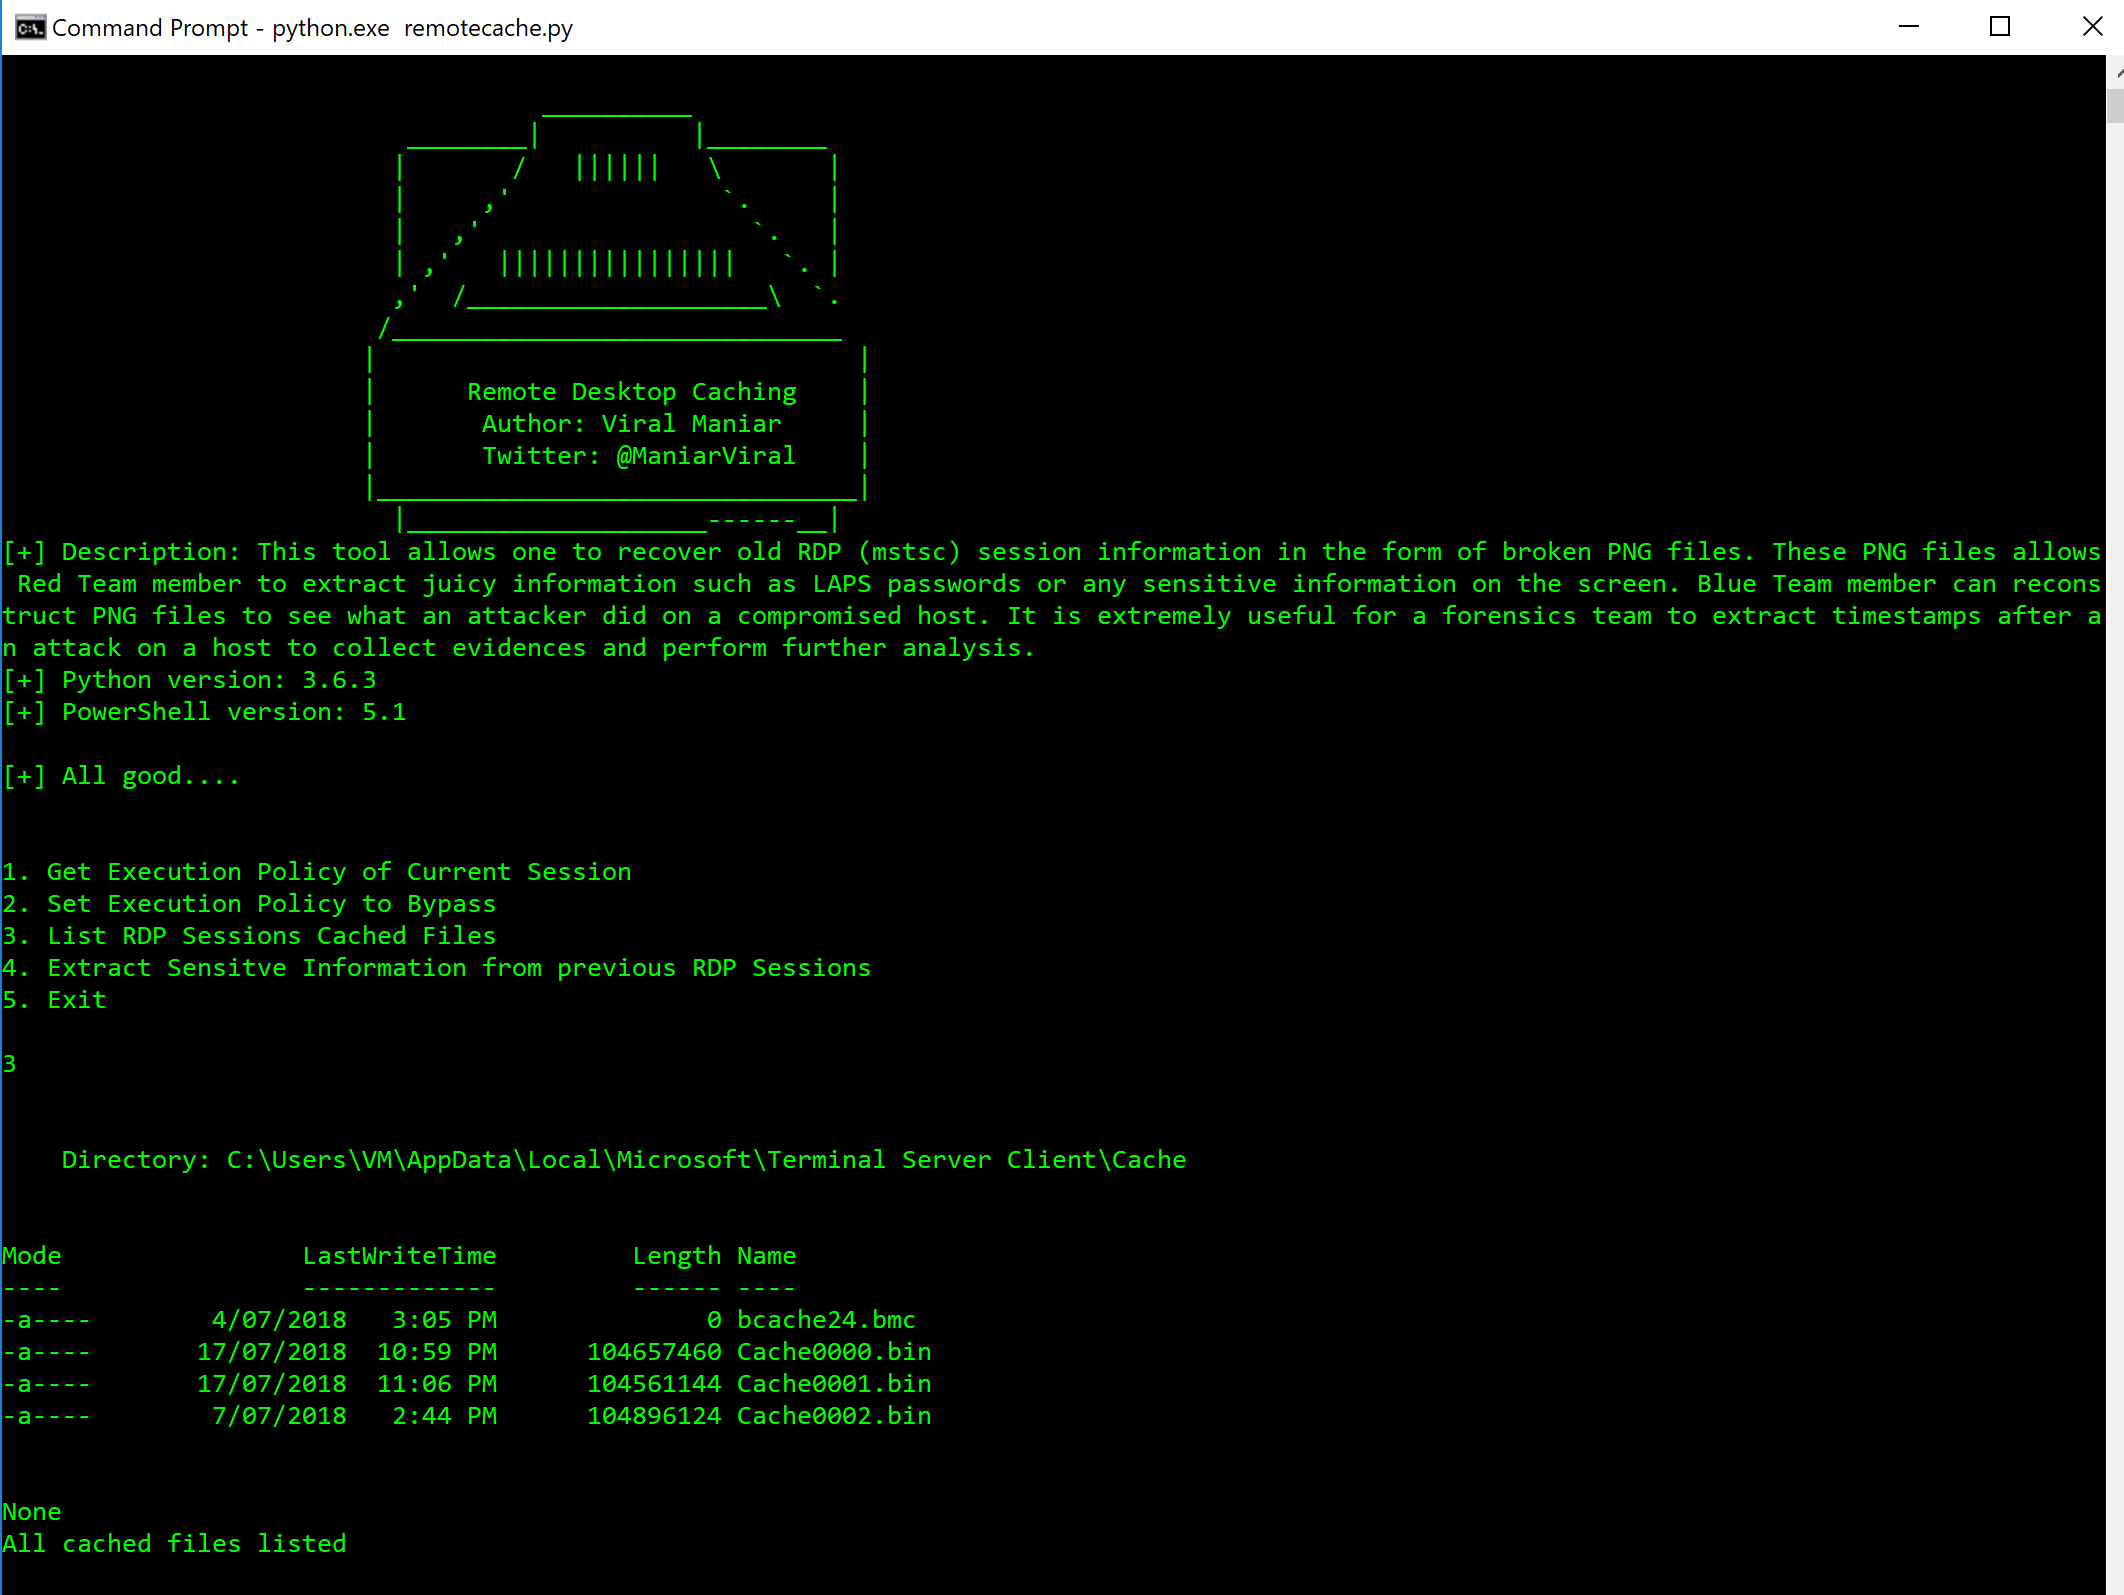
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
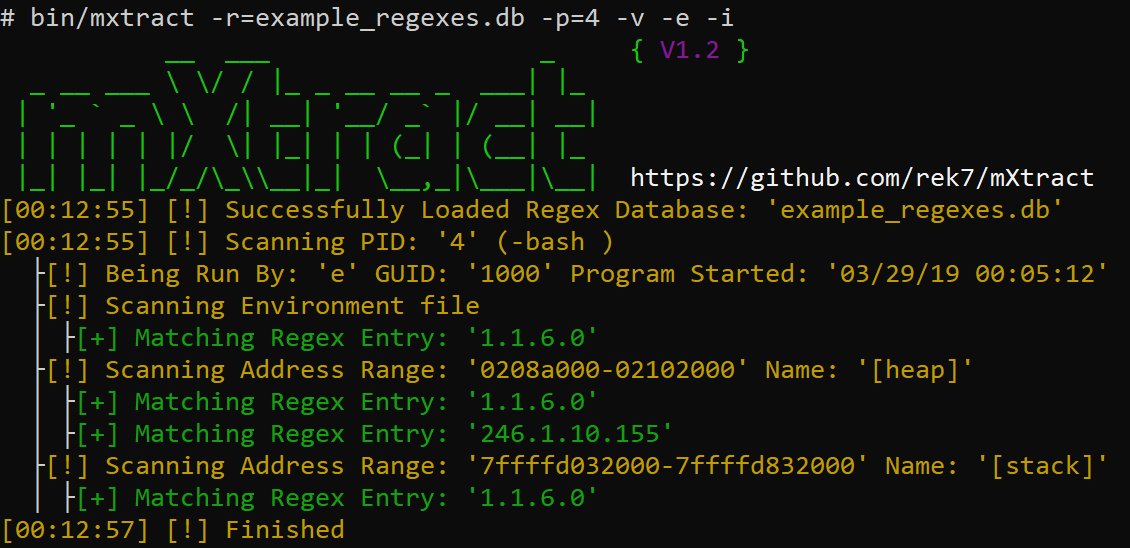
mXtract preview

mXtract

GitHubrek7/mxtract

mXtract - Memory Extractor & Analyzer
forensicsinformation-gatheringmemory-forensics+2
5874 years ago
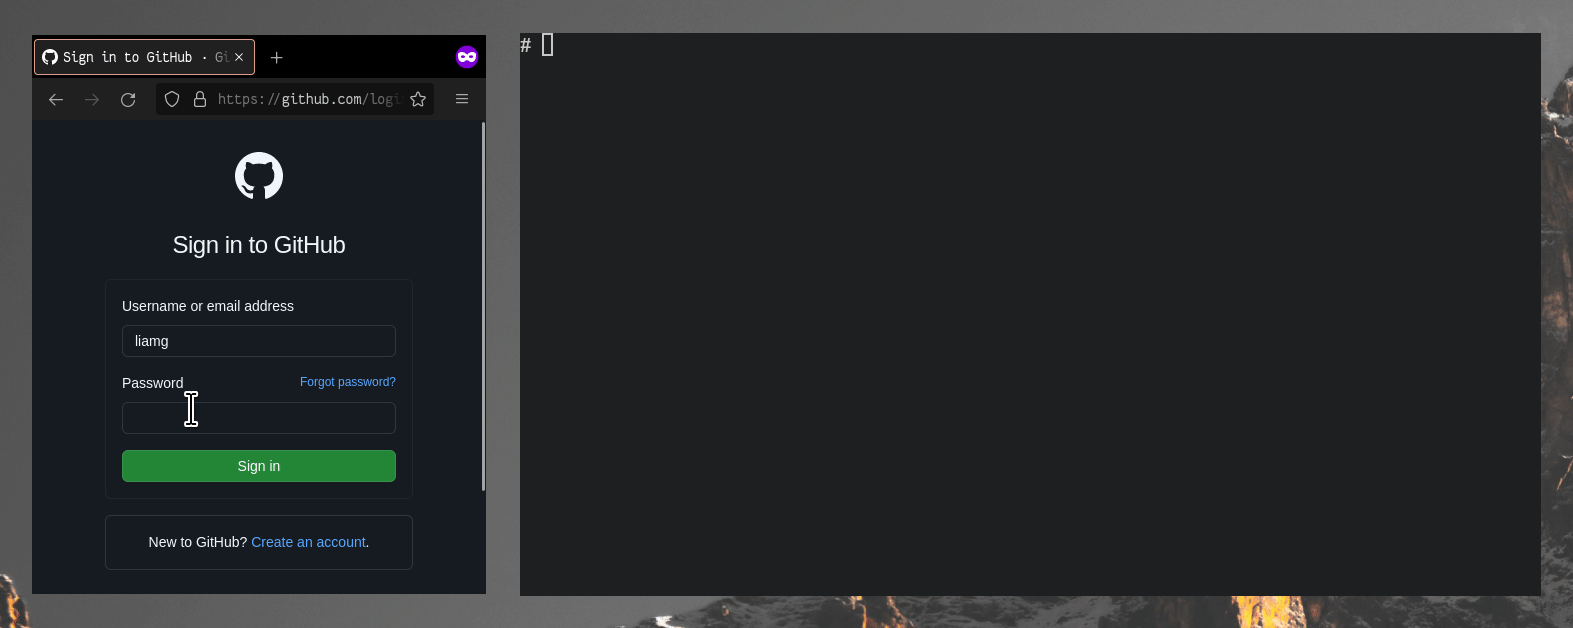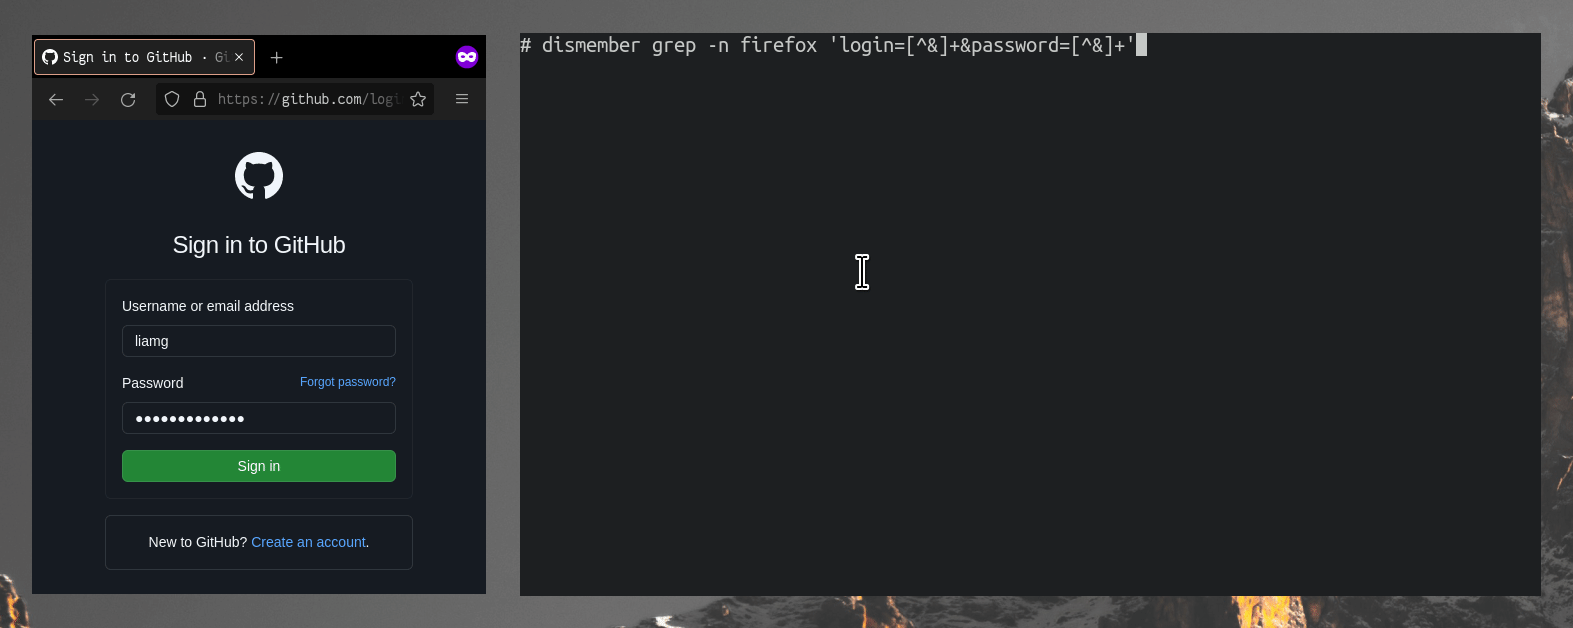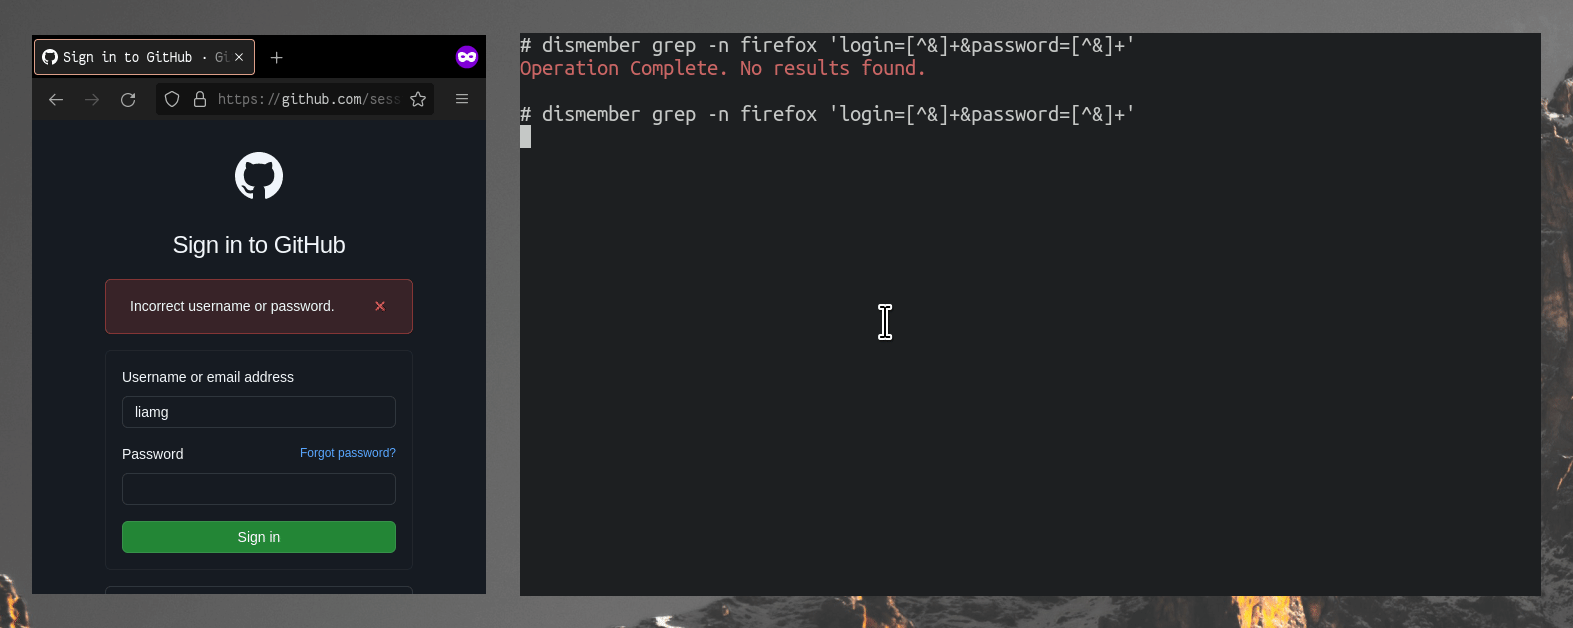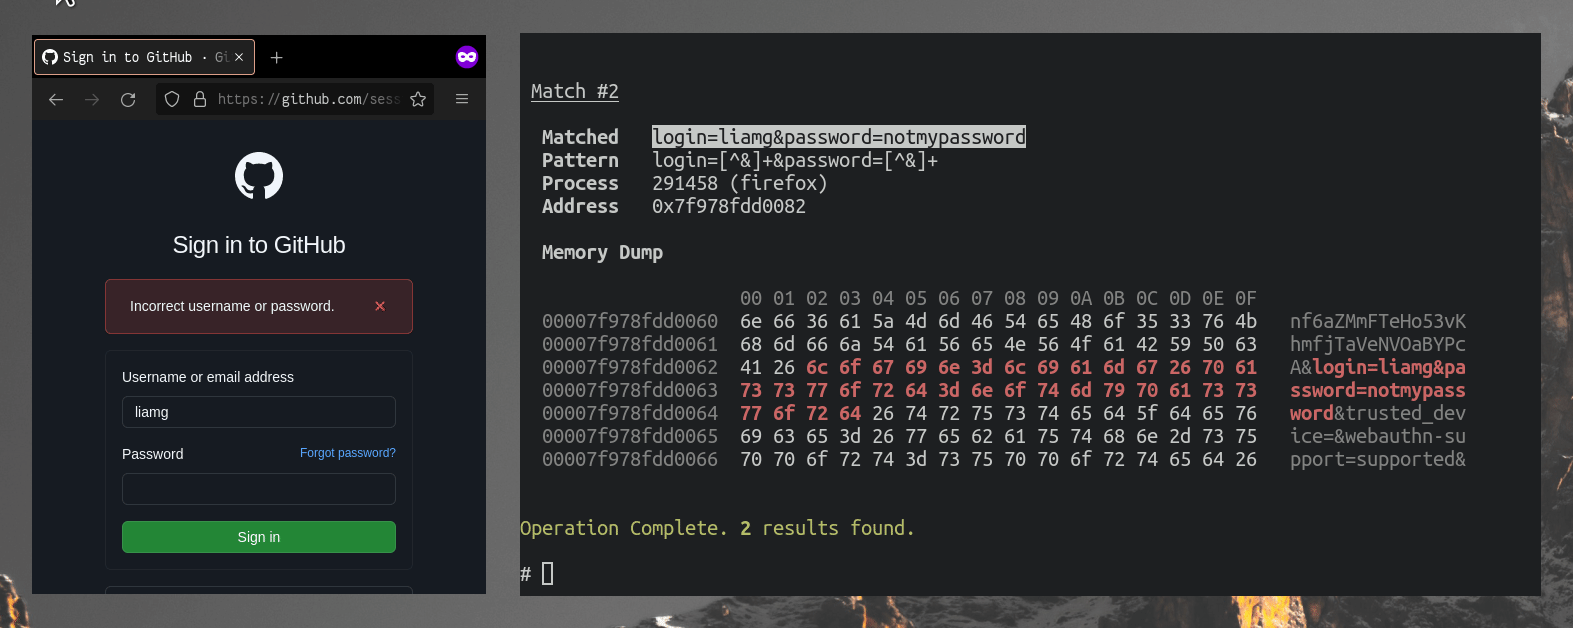
dismember preview

dismember

GitHubliamg/dismember

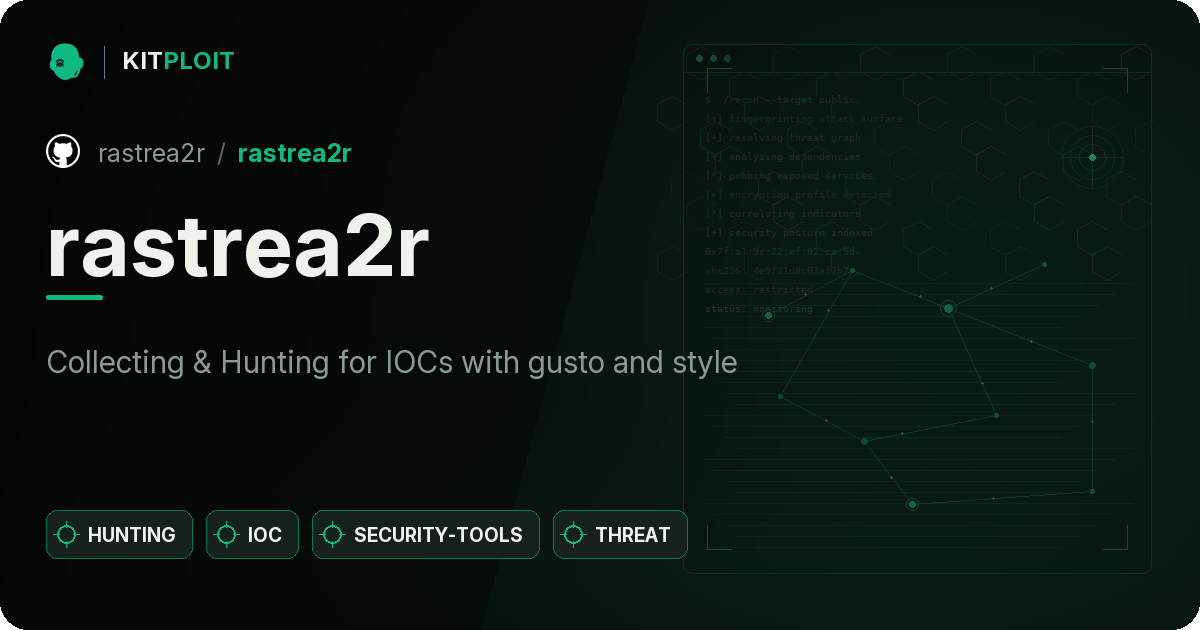
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
ctfforensicsinformation-gathering+2
6734 years ago
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecting & Hunting for IOCs with gusto and style
digital-forensicsforensicsincident-response+6
23815 days ago
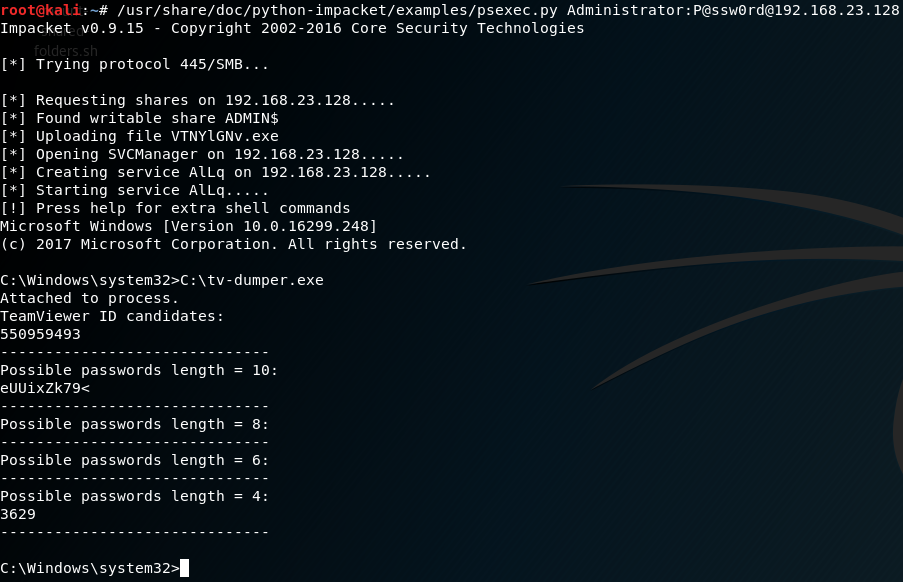
teamviewer-dumper preview

teamviewer-dumper

GitHubattackercan/teamviewer-dumper

Dump TeamViewer ID and password from memory. Works much better than other tools.
digital-forensicsforensicsinformation-gathering+3
988 years ago
memscan preview

memscan

GitHubnccgroup/memscan

Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
data-exfiltrationfuzzinginformation-gathering+5
12711 years ago
exploit-cve-2017-5715 preview

exploit-cve-2017-5715

GitHubopsxcq/exploit-cve-2017-5715

Spectre exploit
binary-exploitationexploitationhardware-security+3
548 years ago
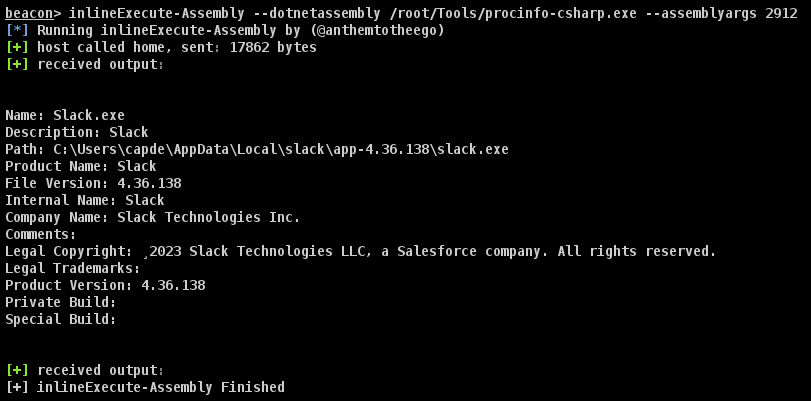
proctools preview

proctools

GitHubmlcsec/proctools

Small toolkit for extracting information and dumping sensitive strings from Windows processes
digital-forensicsforensicsinformation-gathering+2
1162 years ago
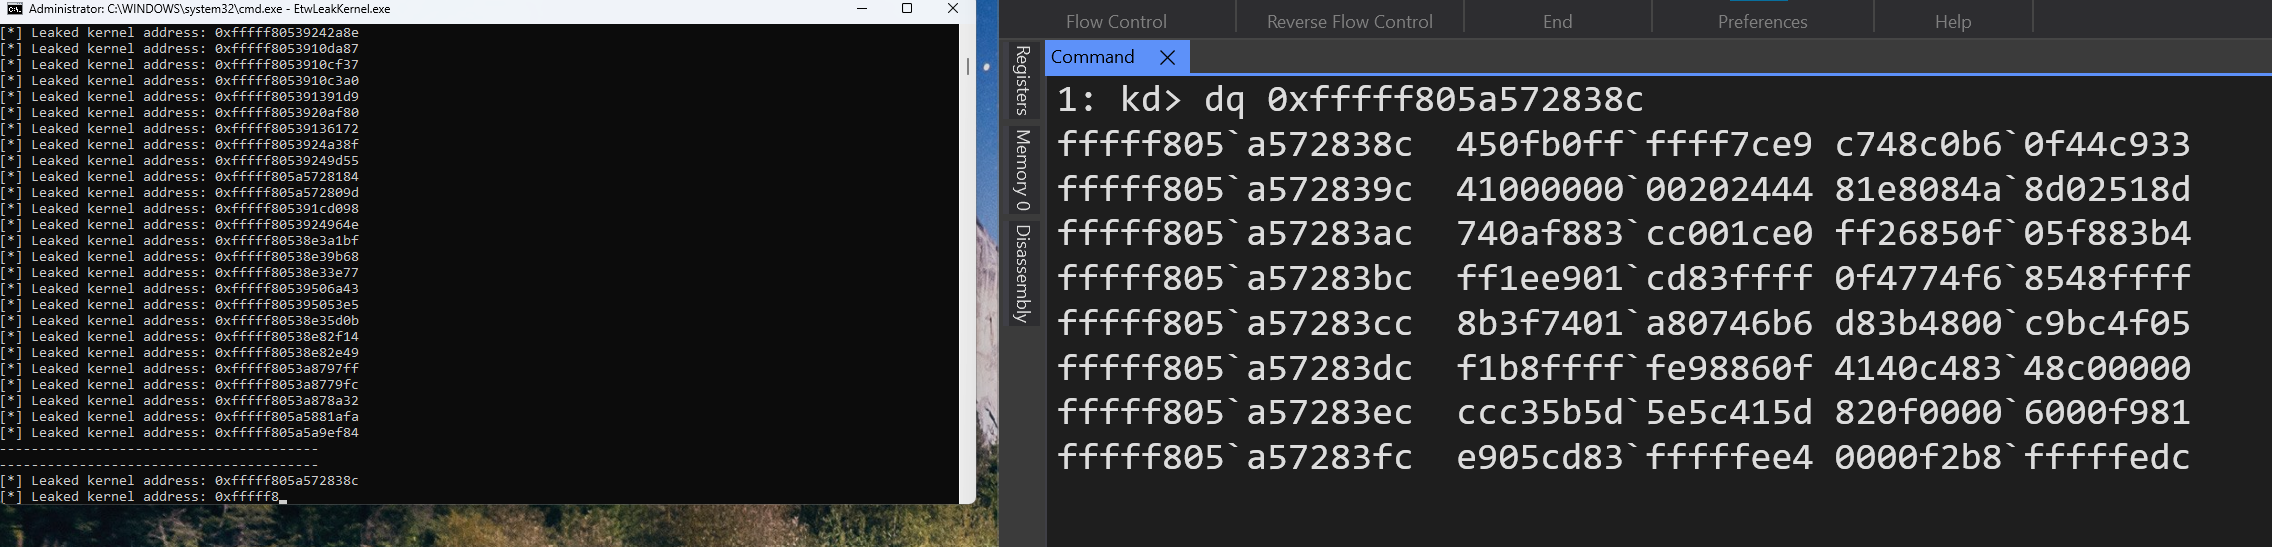
EtwLeakKernel preview

EtwLeakKernel

GitHubidov31/etwleakkernel

Leaking kernel addresses from ETW consumers. Requires Administrator privileges.
binary-exploitationexploitationinformation-gathering+2
9411 months ago
gargamel preview

gargamel

GitHublifars/gargamel

A forensic evidence acquirer

digital-forensicsforensicsincident-response+3
875 years ago
xpc-string-leak preview

xpc-string-leak

GitHubbazad/xpc-string-leak

CVE-2018-4248: Out-of-bounds read in libxpc during string serialization.
binary-exploitationexploitationinformation-gathering+3
548 years ago
syd preview

syd

GitHubsydsec/syd

Offline AI Security Assistant for Air-Gapped Pentesting
ai-securityexploitationforensics+8
876 months ago
linux_screenshot_xwindows preview

linux_screenshot_xwindows

GitHubeurecom-s3/linux_screenshot_xwindows

Volatility plugin to extract X screenshots from a memory dump

digital-forensicsforensicsinformation-gathering+1
378 years ago
Previous123Next