
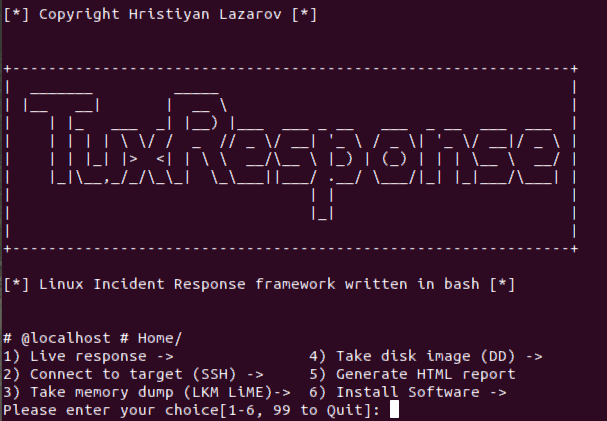
TuxResponse
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
la3ar0v/tuxresponseAutomated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 franksec42/mongobleed-exploit-cve-2025-14847
Explot, Lab, Scanner - external and docker container, for SMongobleed-CVE-2025-14847 plus phoenix security uploader
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 withsecurelabs/dotnet-gargoyle
A spiritual .NET equivalent to the Gargoyle memory scanning evasion technique
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 abdom.seada/security-checks
linux security checks
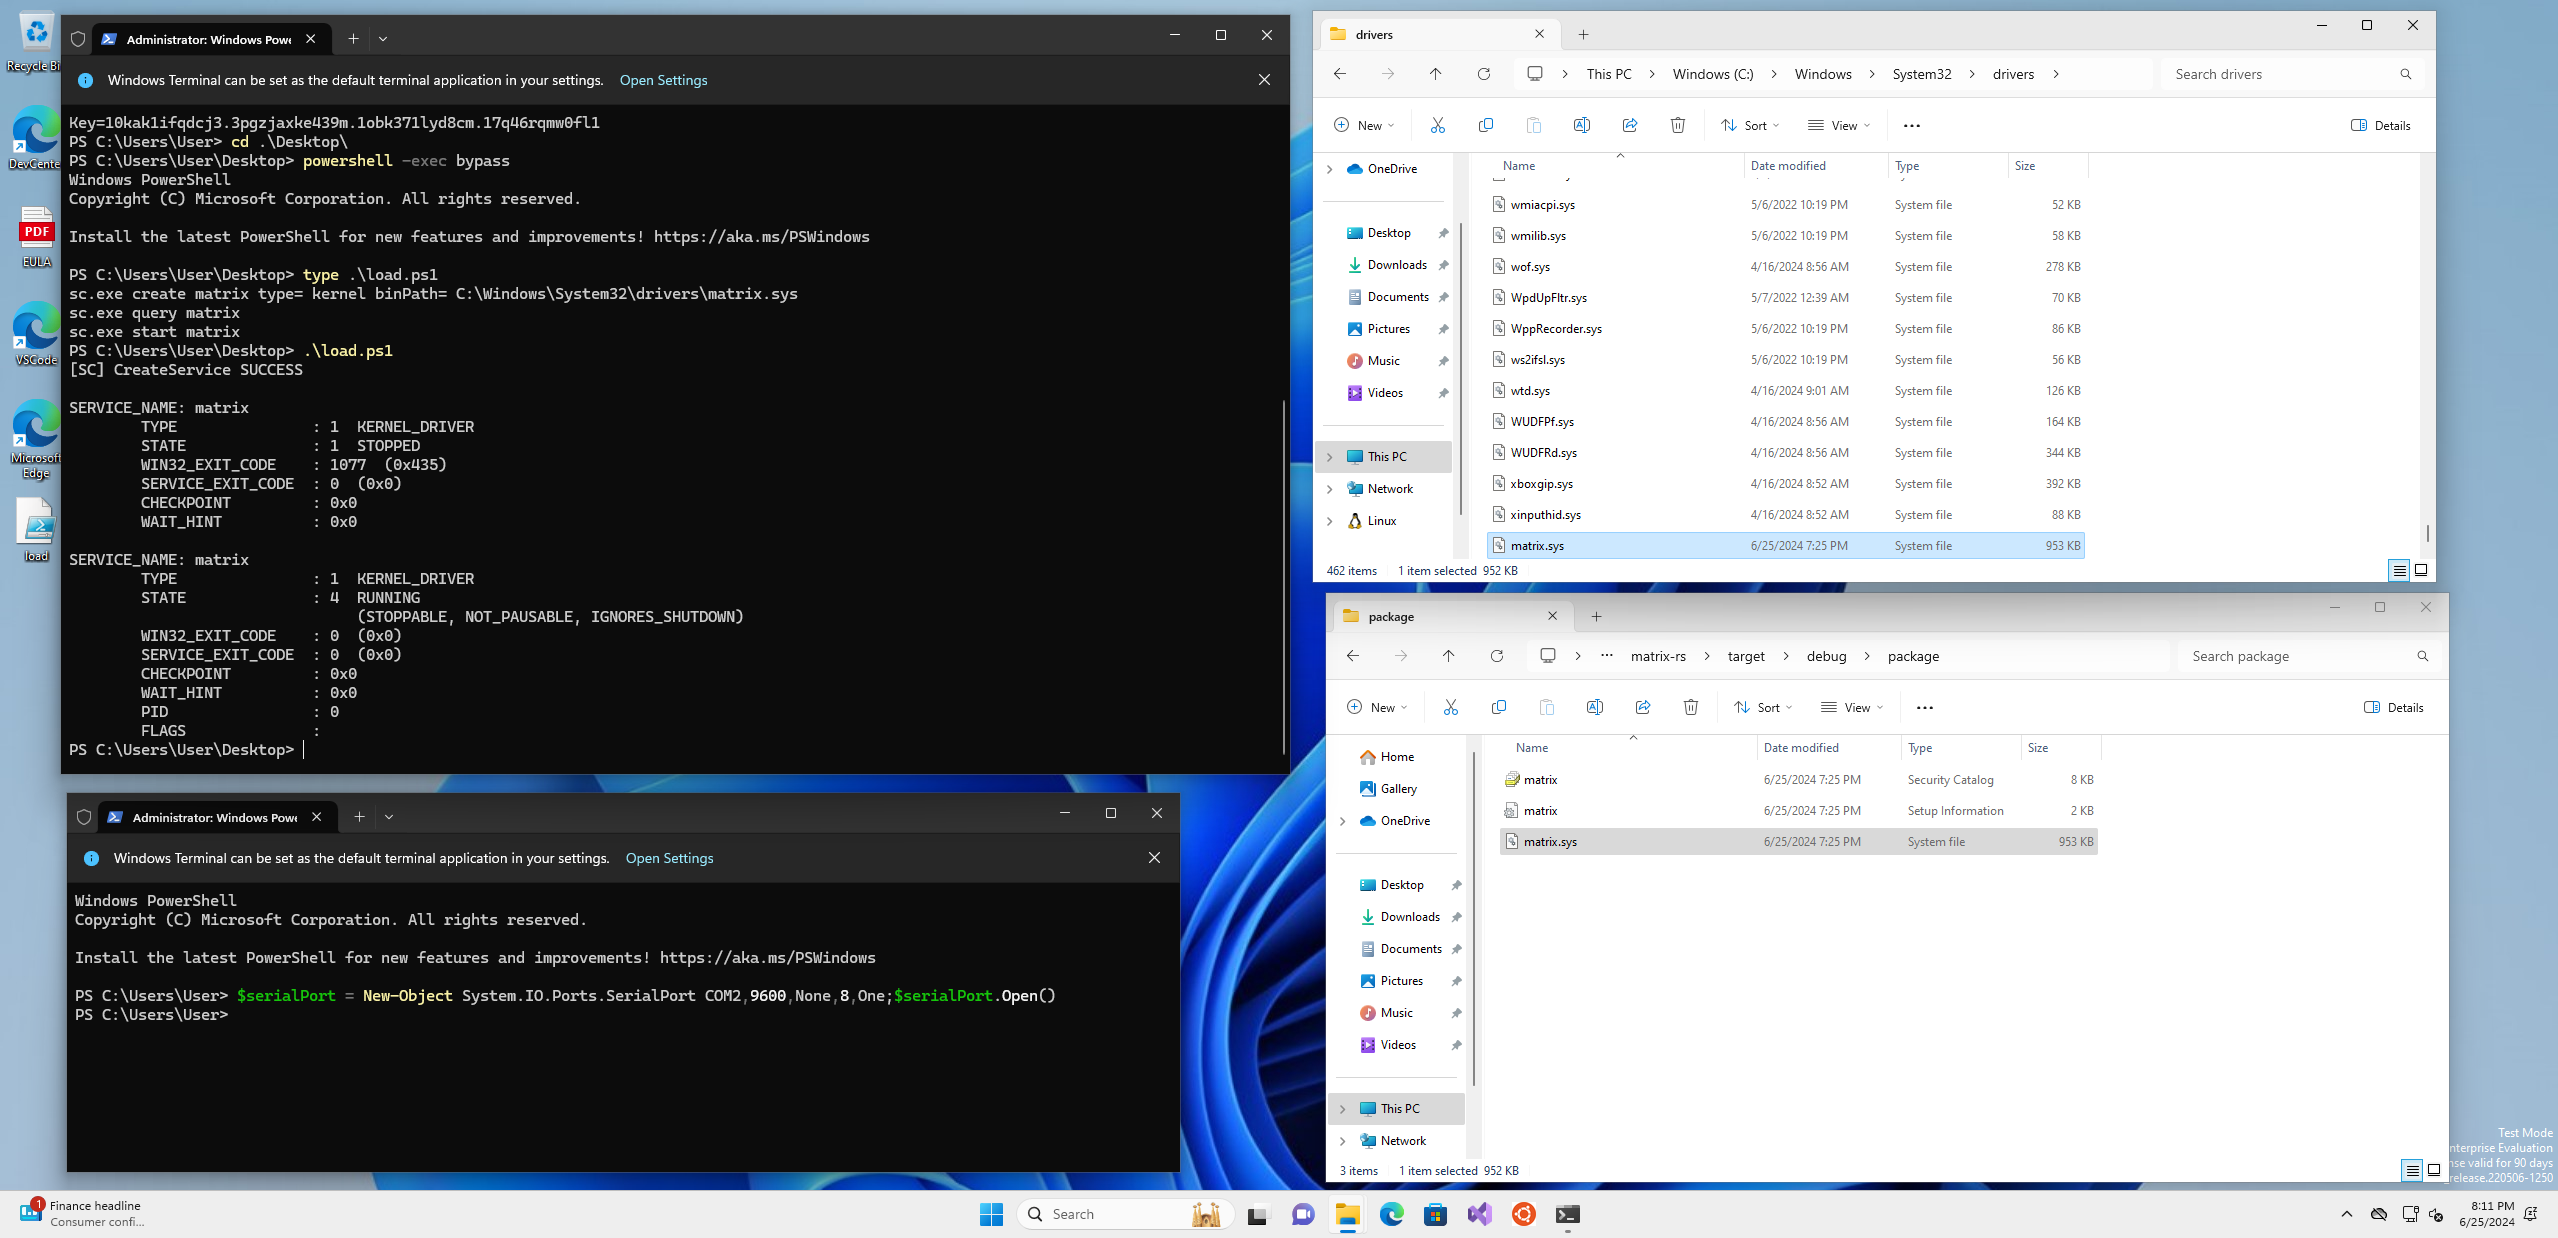 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 hasherezade/pesieve-go
Golang bindings for PE-sieve