cve-2023-4863-analysis

Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…

Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…

Cobalt Strike UDRL for memory scanner evasion.

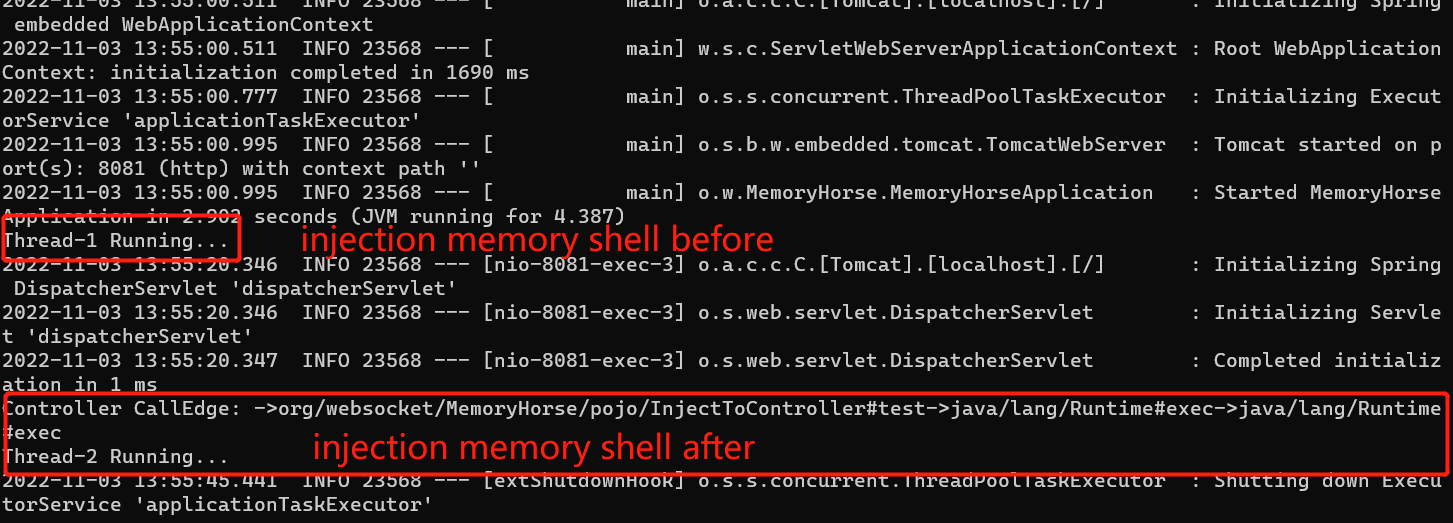
Java Agent memory horse scanner combined with Call Graph modus

Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

A centralized and enhanced memory analysis platform

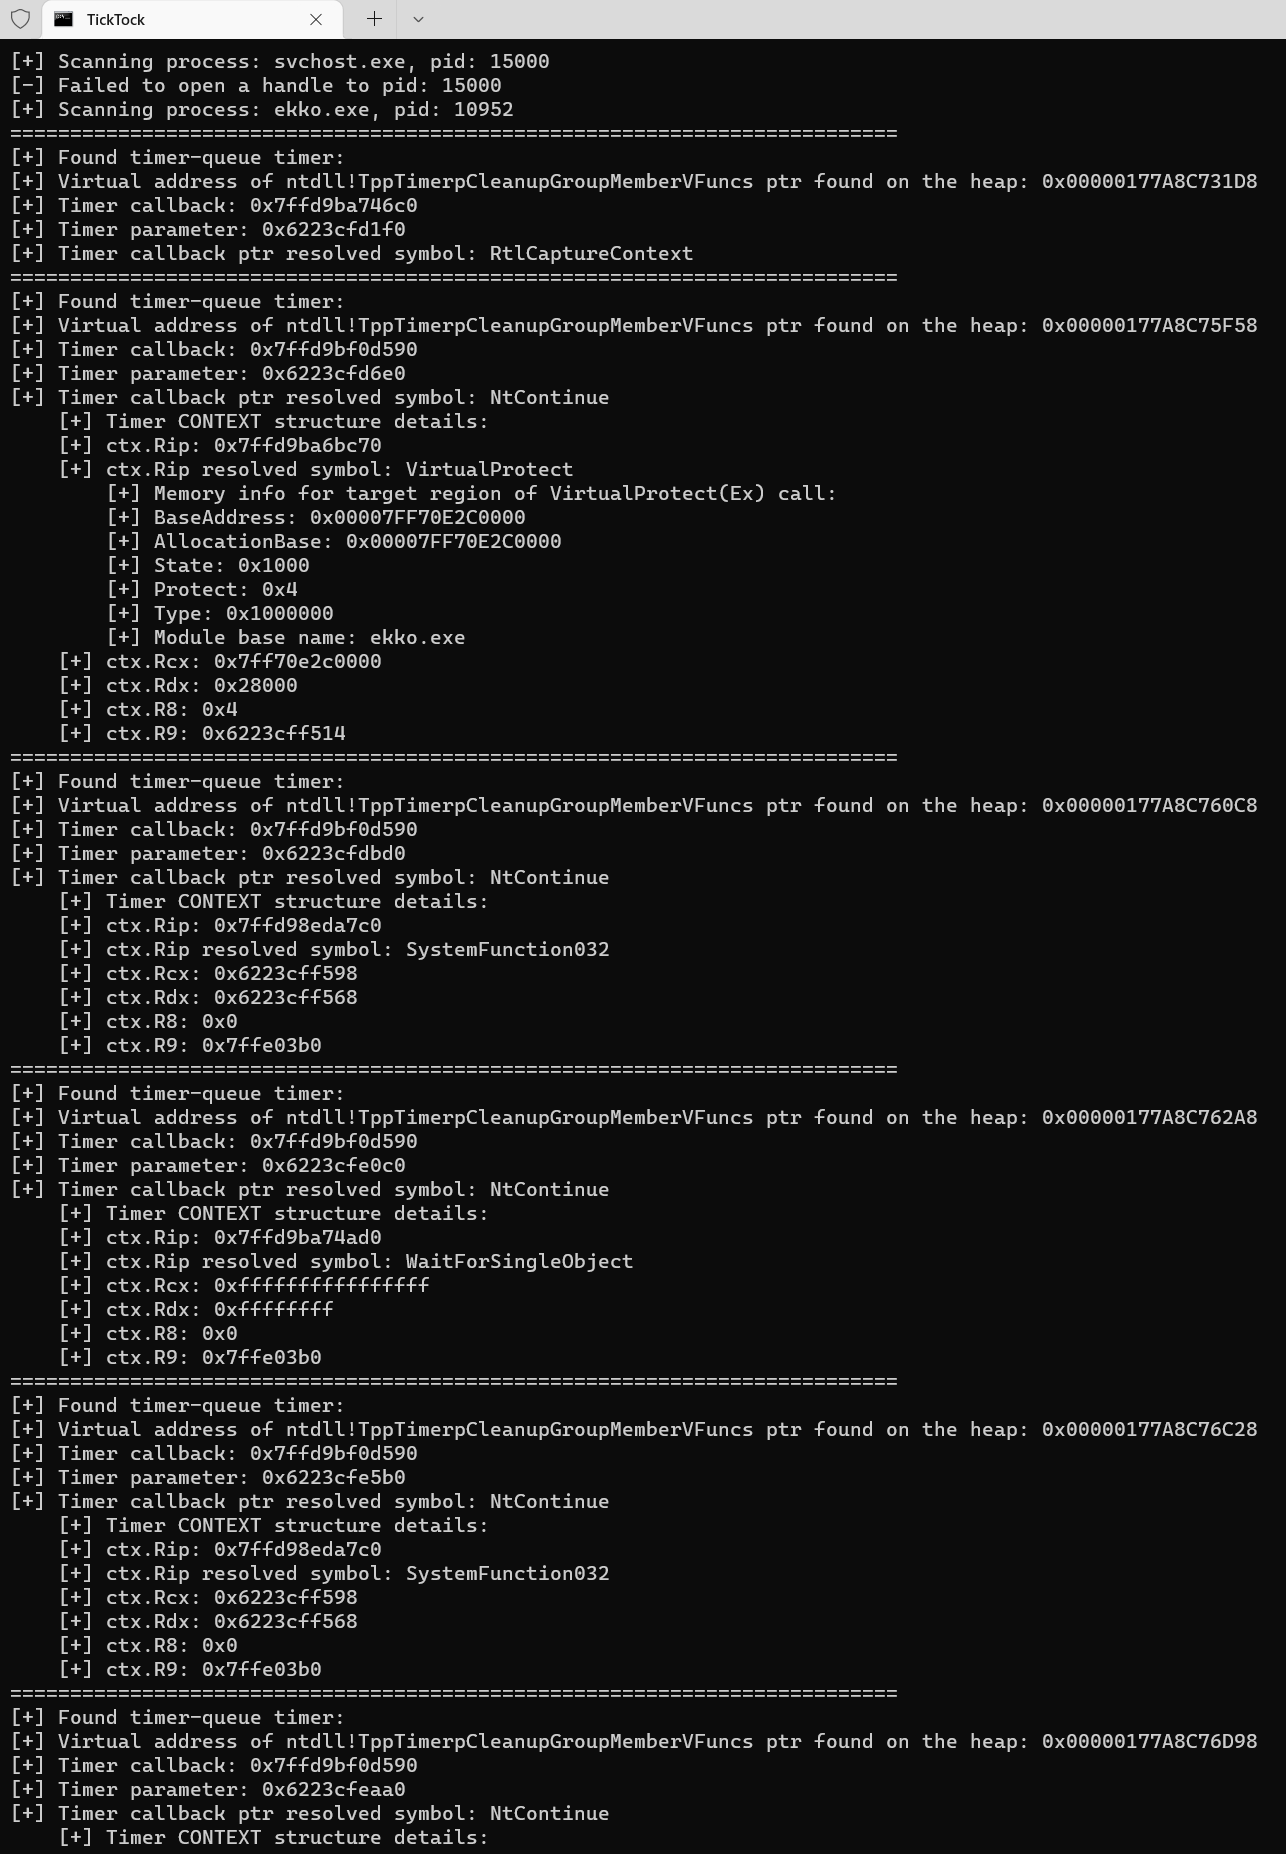
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…

Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space

ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.

This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

Defund the Police.

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux


List of Awesome CobaltStrike Resources


A post-exploitation powershell tool for extracting juicy info from memory.