

memory-forensic
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
13
securityronin/memory-forensicWalk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 3ndg4me/cve-2016-6415-benigncertain-monitor
Re-implementation of VirtueSecurity's benigncertain-monitor
 fuzzysecurity/cassowary-cve-2024-23222-x86_64
Adaptation of Cassowary CVE-2024-23222 for Linux x86_64
 rick2600/redis-stack-cve-2024-55656
Proof-of-concept exploit for CVE-2024-55656, an integer overflow in RedisBloom leading to heap-based OOB read/write and remote code execution in…
 ayushsinha322/heartbleed-lab
Self-contained Heartbleed (CVE-2014-0160) lab: builds vulnerable OpenSSL 1.0.1f in Docker and includes a Python memory-leak PoC for authorised…
 franksec42/mongobleed-exploit-cve-2025-14847
Explot, Lab, Scanner - external and docker container, for SMongobleed-CVE-2025-14847 plus phoenix security uploader
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
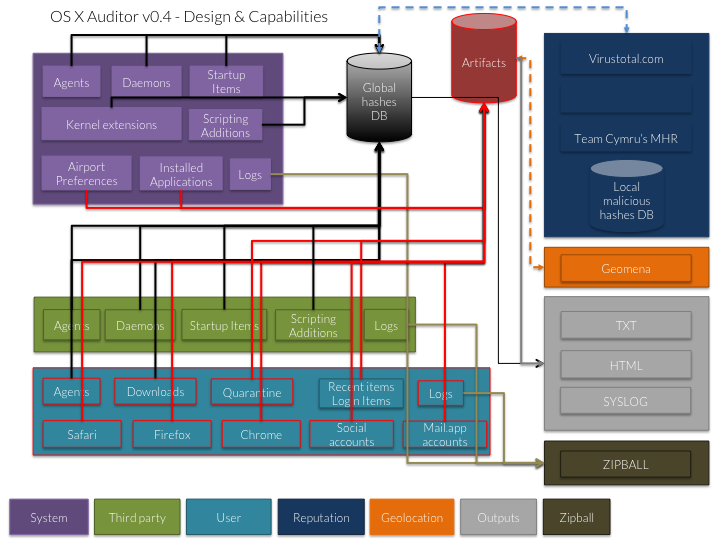 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
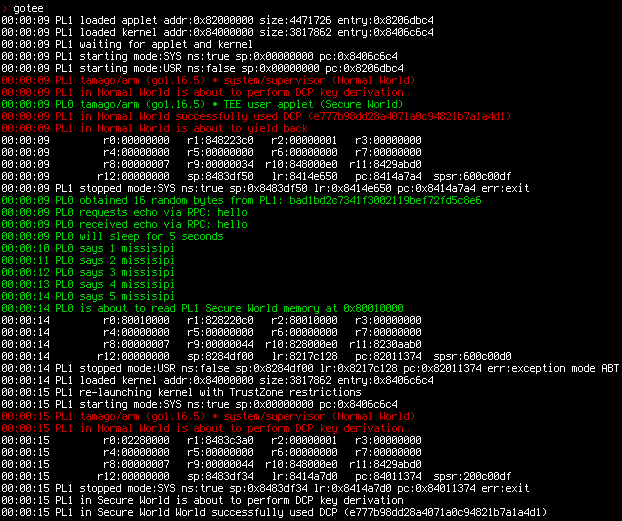 usbarmory/gotee-example
GoTEE - example application

 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…