

forensictools
 cristianzsh/forensictools
Collection of forensic tools
binary-analysisdata-recoverydigital-forensics+7
cristianzsh/forensictoolsCollection of forensic tools
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
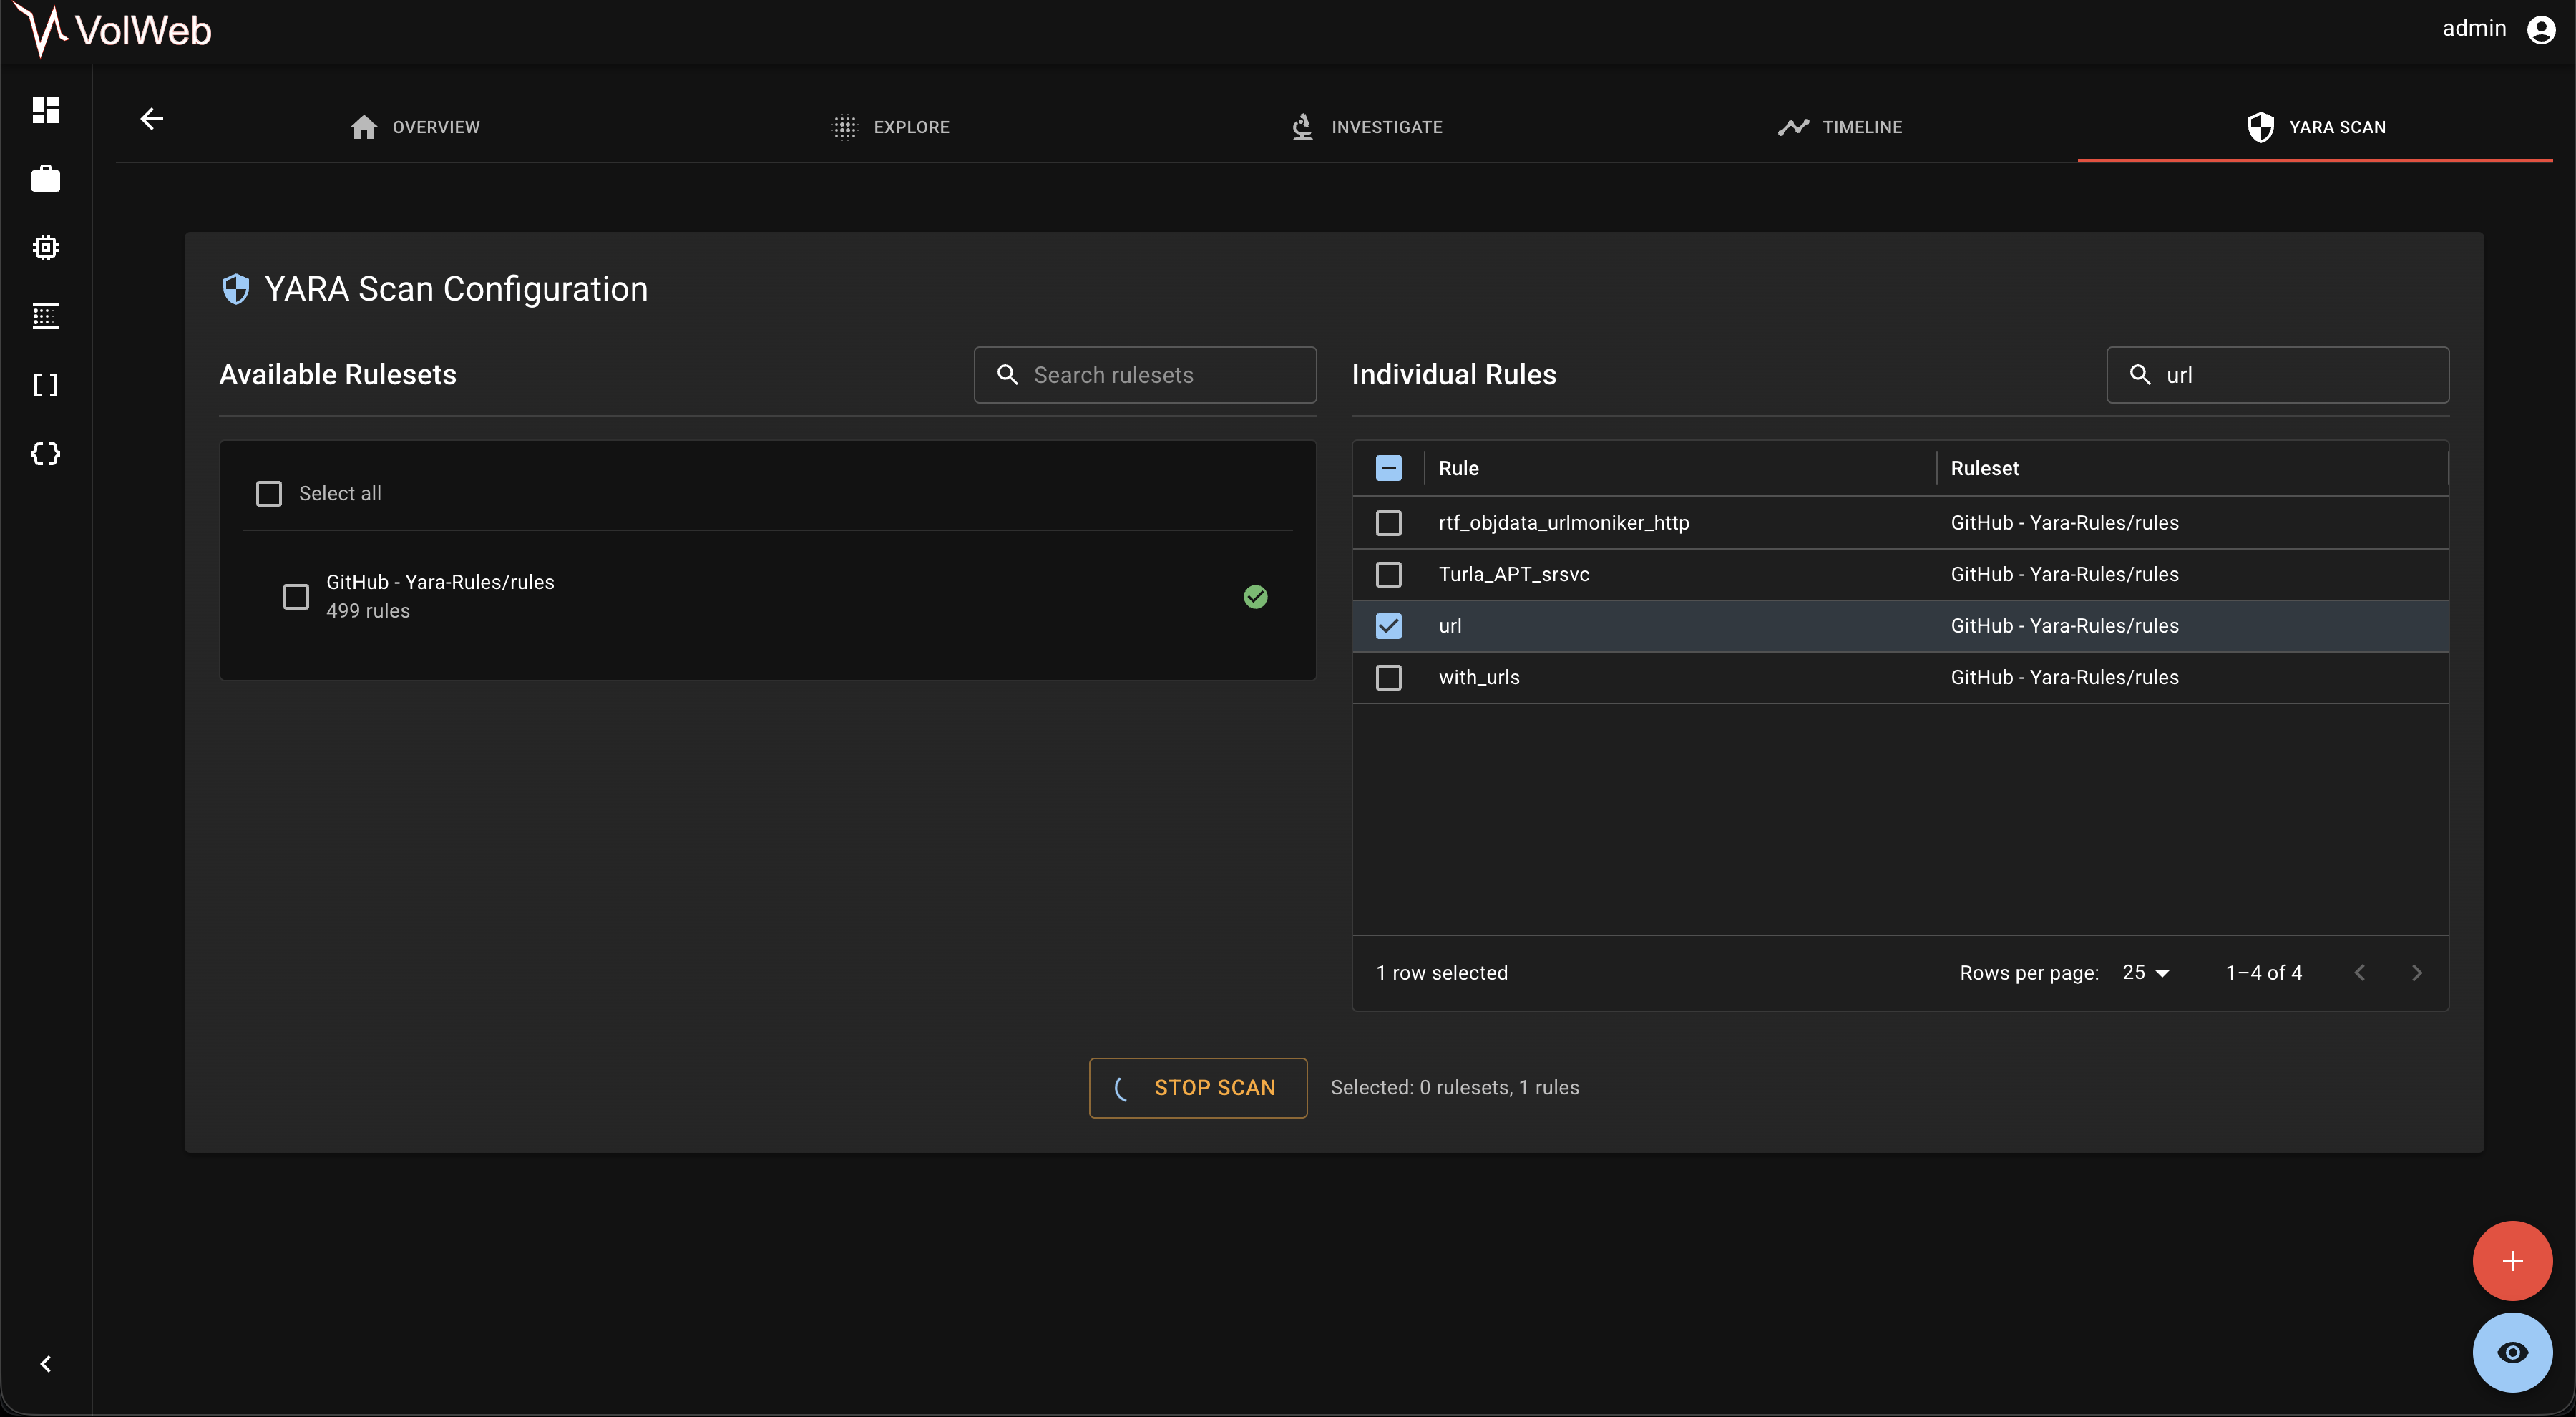 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
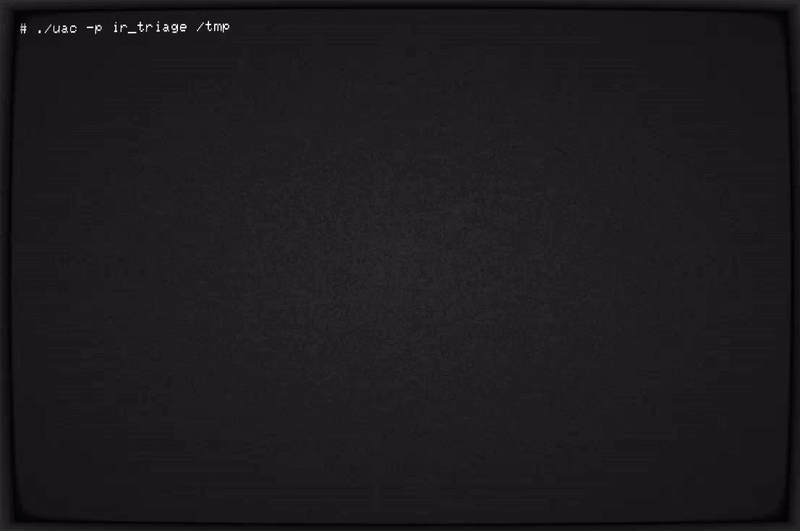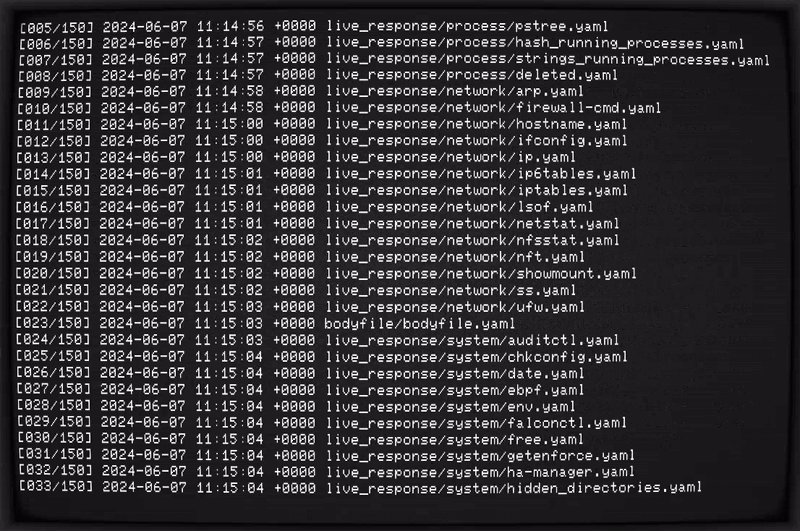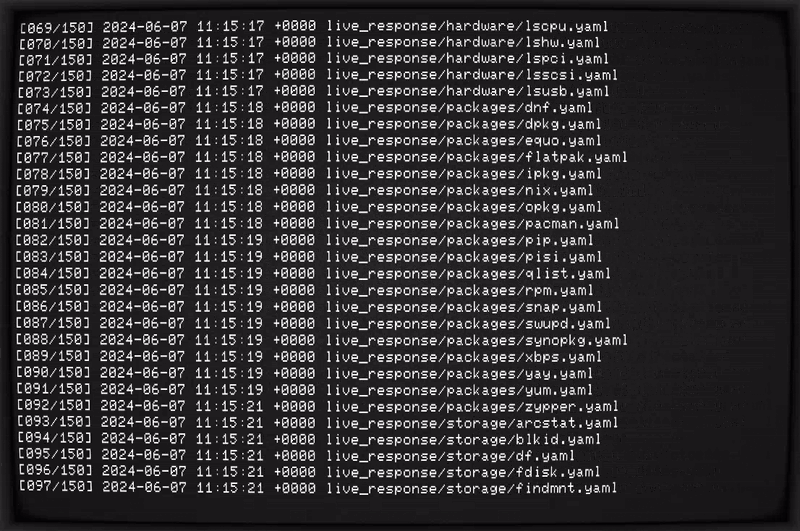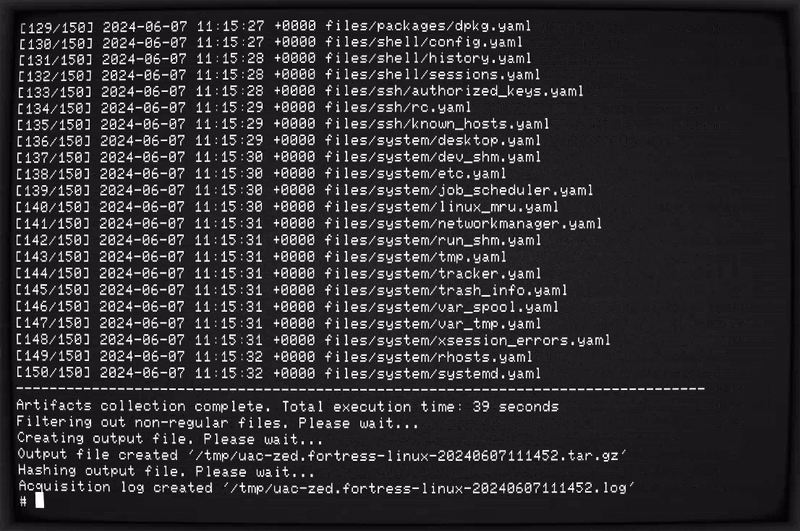 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
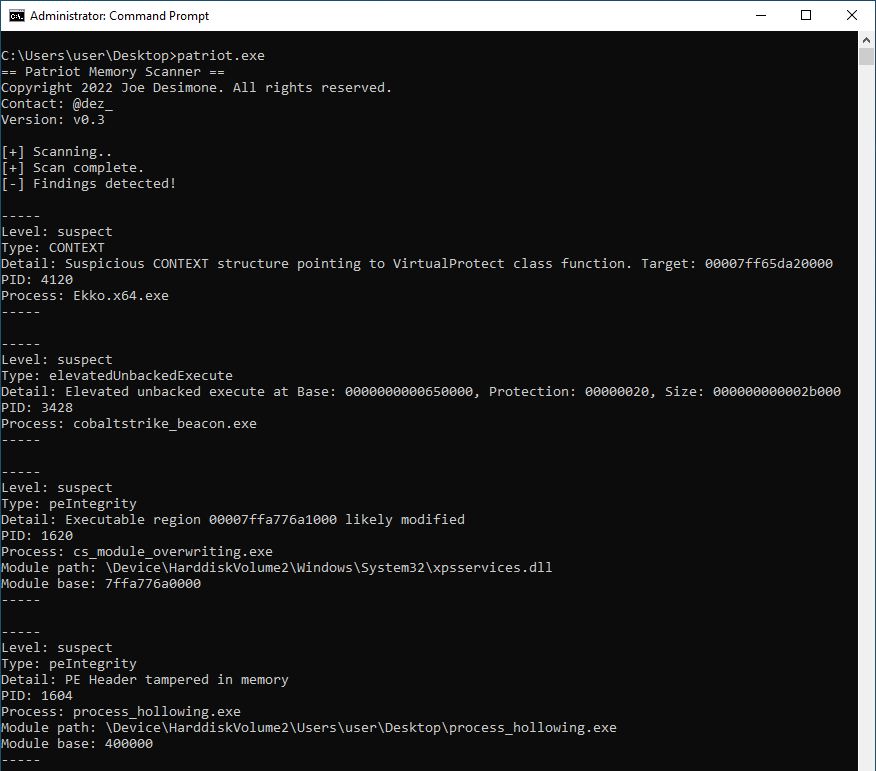 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
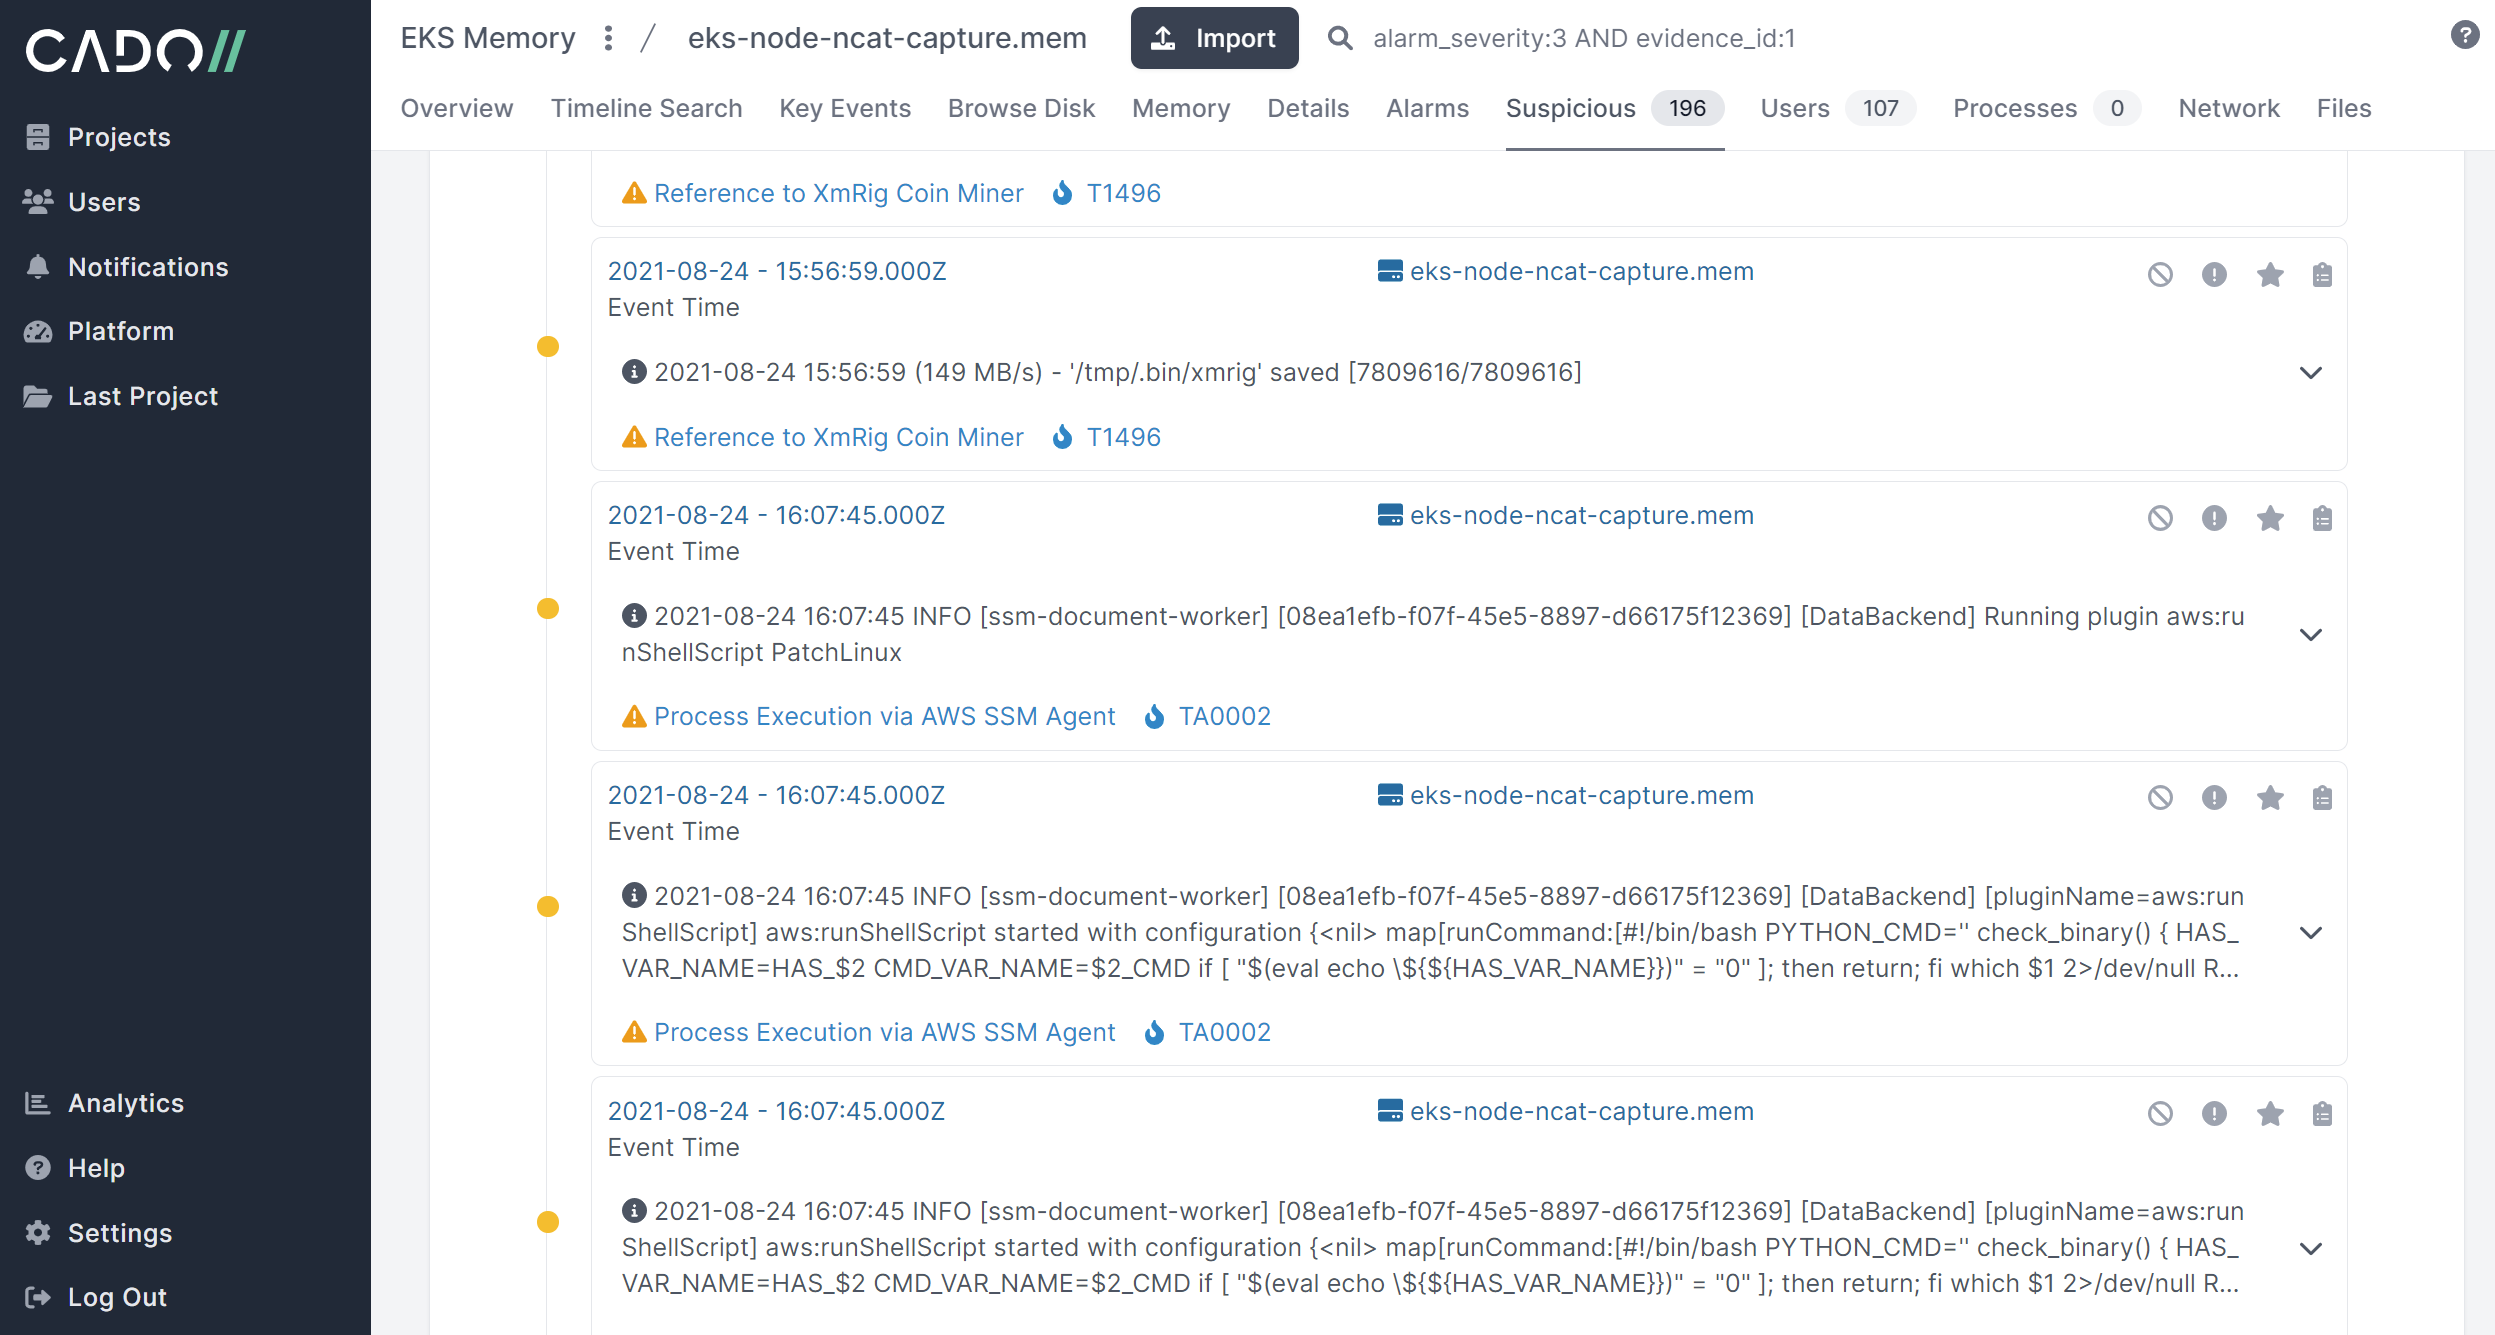 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 volatilityfoundation/volatility
An advanced memory forensics framework
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…