Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
107 results
VMInjector preview

VMInjector

GitHubhzphreak/vminjector

DLL Injection tool to unlock guest VMs

authentication-authorizationbinary-exploitationexploitation+4
23813 years ago
ATMMalScan preview

ATMMalScan

GitHubfboldewin/atmmalscan

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
digital-forensicsdisk-forensicsincident-response+2
565 years ago
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
anomaly-detectionbinary-analysisdefensive-tools+4
110 months ago
no-access-protection-x86 preview

no-access-protection-x86

GitHubgmh5225/no-access-protection-x86

It encrypts the text section and set the protection to NO_ACCESS.
anti-botbinary-analysisdefensive-tools+4
13 years ago
Soviet preview

Soviet

GitHubmephistolist/soviet

A Runtime Crypter in C for Linux ELF binaries.
anti-botbinary-analysisencryption-decryption-tools+6
358 months ago
EAC-Kernel-Packet-Fucker preview

EAC-Kernel-Packet-Fucker

GitHubgmh5225/eac-kernel-packet-fucker

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
anti-botbinary-analysisencryption-decryption-tools+6
174 years ago
RustChain preview

RustChain

GitHubkudaes/rustchain

Hide memory artifacts using ROP and hardware breakpoints.

exploitationmemory-forensicspayload-development+1
1513 years ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.0k1 year ago
MalSeclogon preview

MalSeclogon

GitHubantoniococo/malseclogon

A little tool to play with the Seclogon service

exploitationlateral-movementmemory-forensics+3
3274 years ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k12h 9m ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
2.7k11 days ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool
debuggersdynamic-analysis-sandboxingincident-response+2
3.1k6 days ago
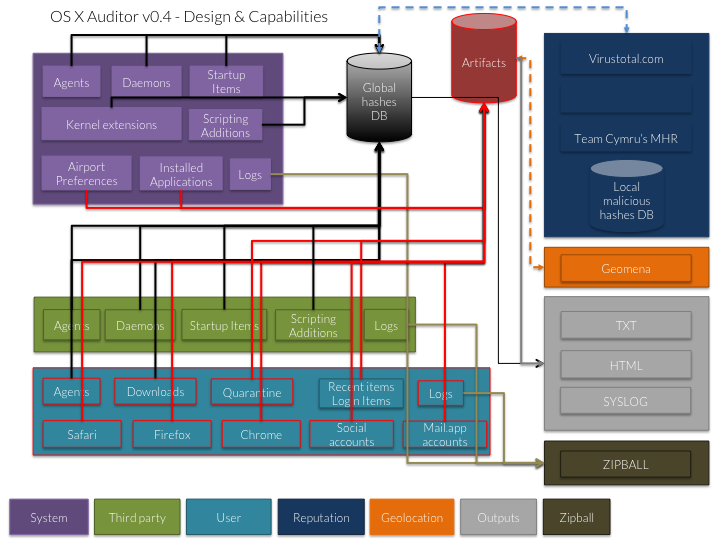
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

OS X Auditor is a free Mac OS X computer forensics tool

digital-forensicsdisk-forensicsforensics+4
3.1k6 years ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 month ago
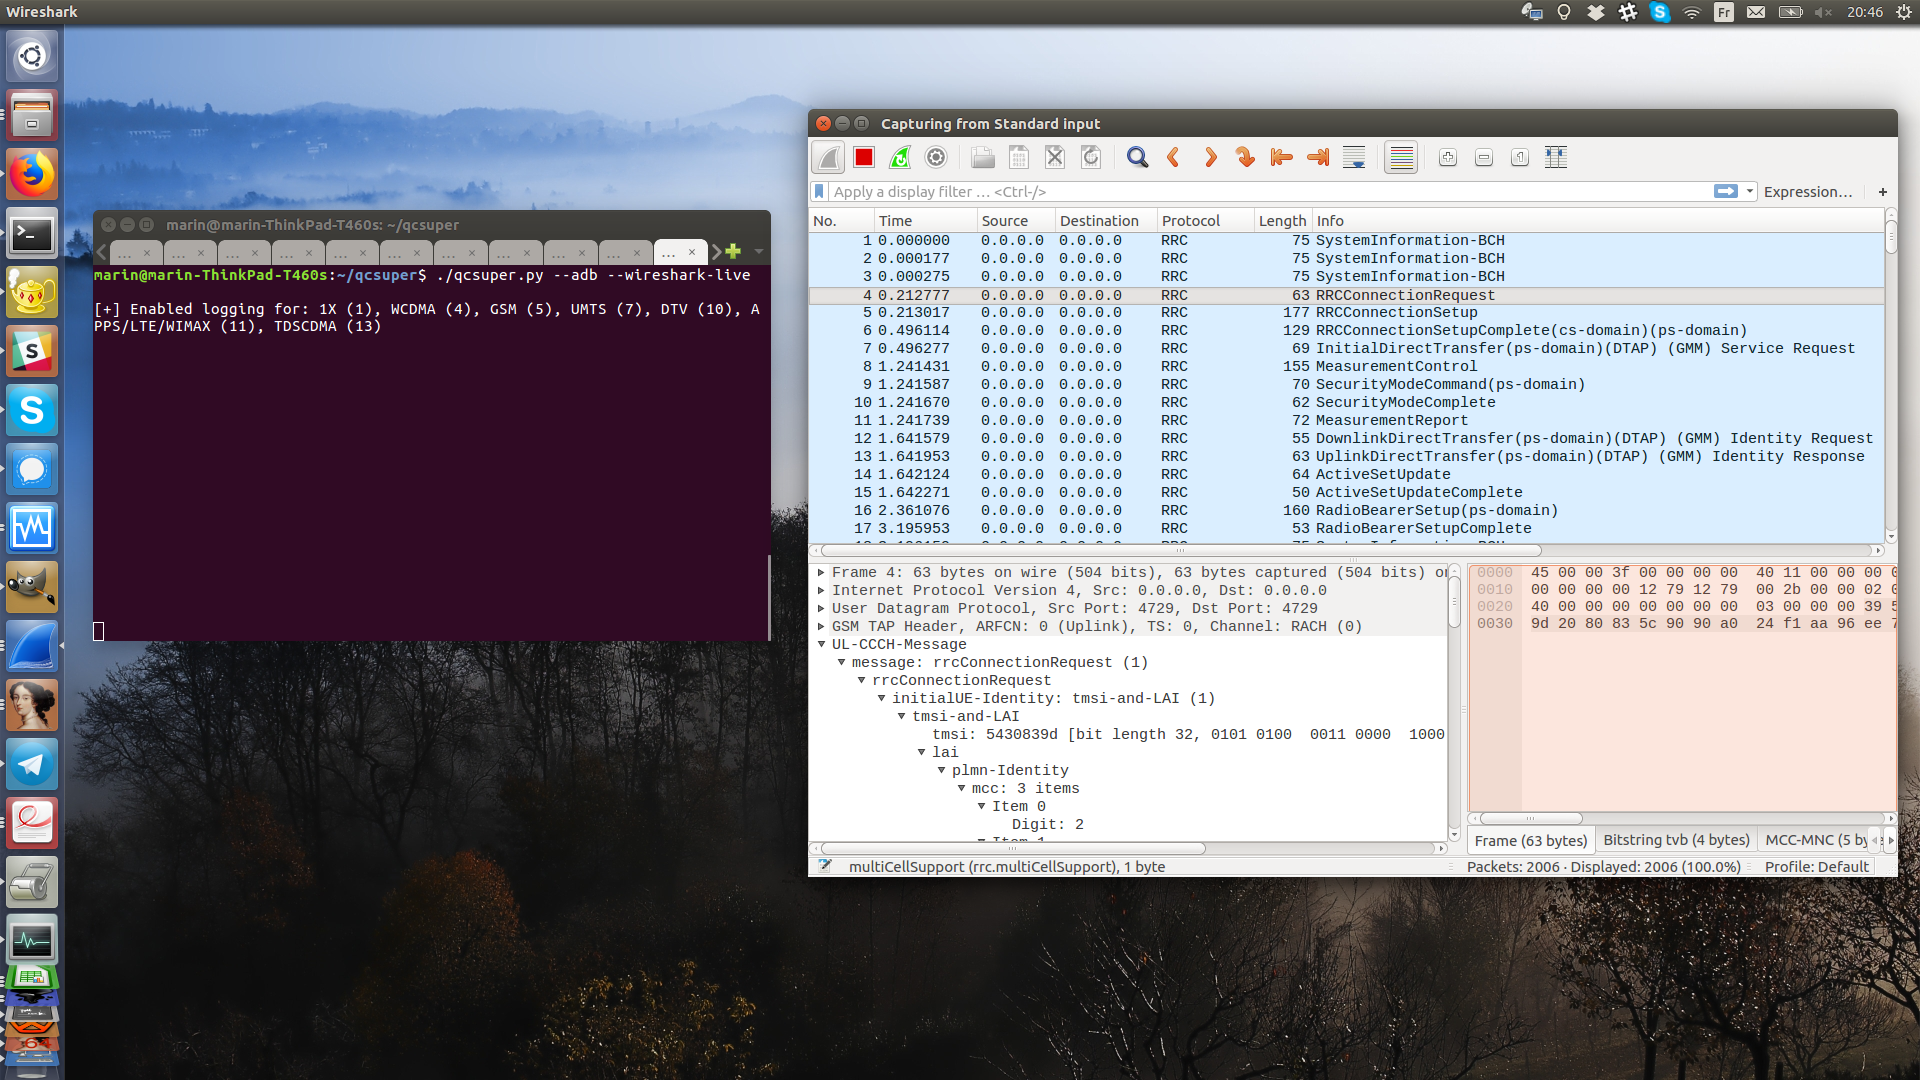
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.6k15 days ago
mimikittenz preview

mimikittenz

GitHuborlyjamie/mimikittenz

A post-exploitation powershell tool for extracting juicy info from memory.
information-gatheringmemory-forensicspenetration-testing+1
1.9k6 years ago
WinPmem preview

WinPmem

GitHubvelocidex/winpmem

The multi-platform memory acquisition tool.

digital-forensicsforensicsincident-response+1
1.0k13 days ago
mimikatz preview

mimikatz

GitHubparrotsec/mimikatz

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…

authenticationexploitationlateral-movement+5
2.6k6 years ago
Previous123456Next