
mimikittenz
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
information-gatheringmemory-forensicspenetration-testing+1
1.9k
orlyjamie/mimikittenzA post-exploitation powershell tool for extracting juicy info from memory.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 egebalci/ticketbleed
This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
 watchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451
Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
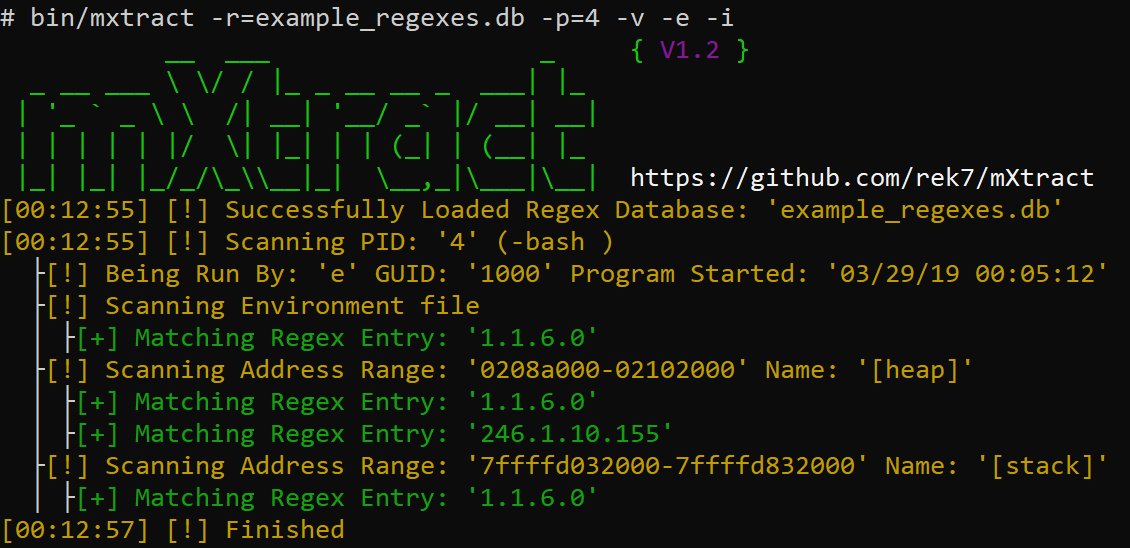 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 bughuntar/cve-2025-5777
CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)