

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
164 results
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.0k
1 year ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.7k8 days ago
hollows_hunter preview

hollows_hunter

GitHubhasherezade/hollows_hunter

Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…

defensive-toolsforensicsincident-response+2
2.4k4 months ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8174 months ago
DeepSleep preview

DeepSleep

GitHubtheflink/deepsleep

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
exploitationmemory-forensicspayload-development+1
3734 years ago
teamviewer-dumper preview

teamviewer-dumper

GitHubattackercan/teamviewer-dumper

Dump TeamViewer ID and password from memory. Works much better than other tools.

digital-forensicsforensicsinformation-gathering+3
988 years ago
CVE-2025-24204 preview

CVE-2025-24204

GitHubffri/cve-2025-24204

PoC and technical details of CVE-2025-24204

encryption-decryption-toolsexploitationmemory-forensics+2
1130 years ago
CVE-2023-36427 preview

CVE-2023-36427

GitHubtandasat/cve-2023-36427

Report and exploit of CVE-2023-36427
binary-exploitationexploitationhardware-security+3
902 years ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

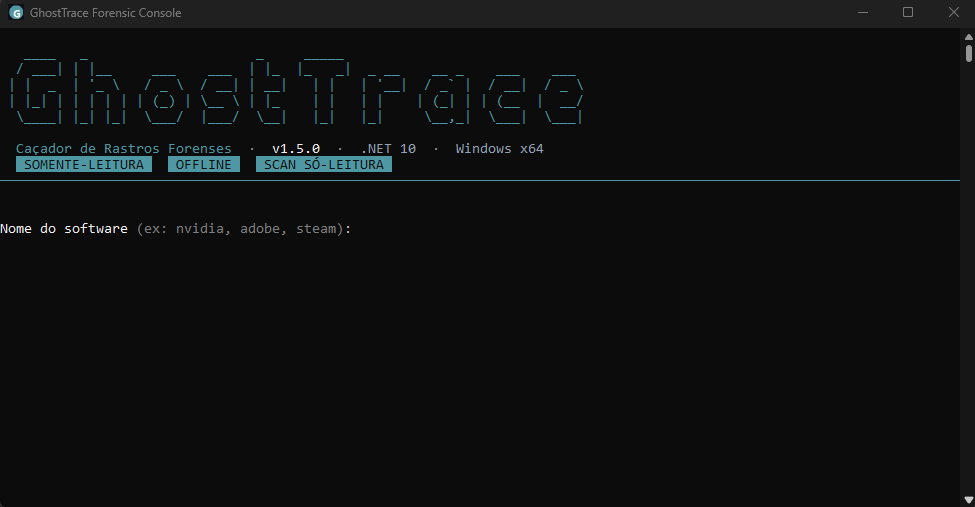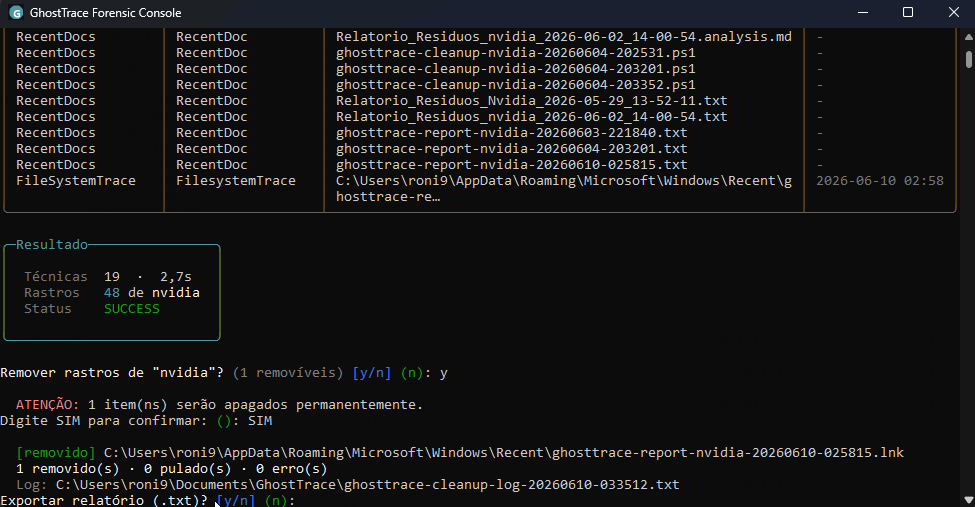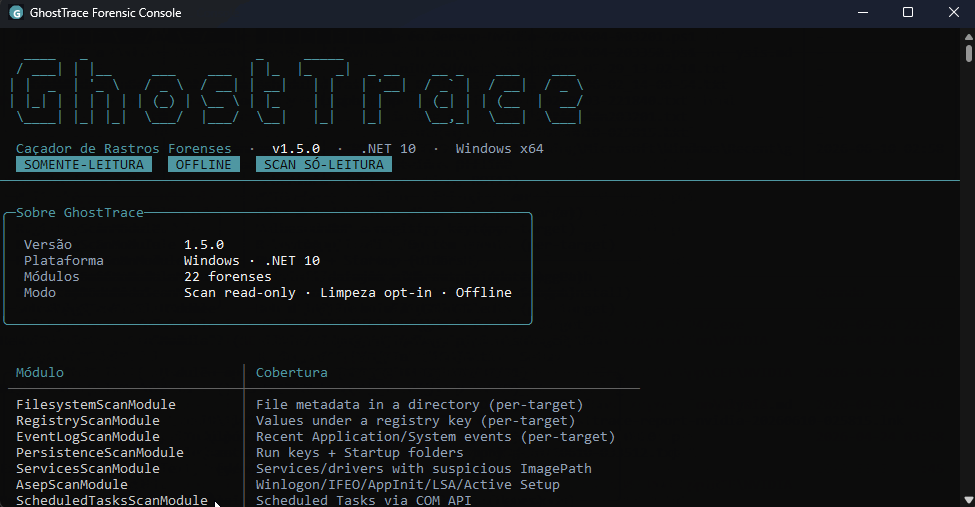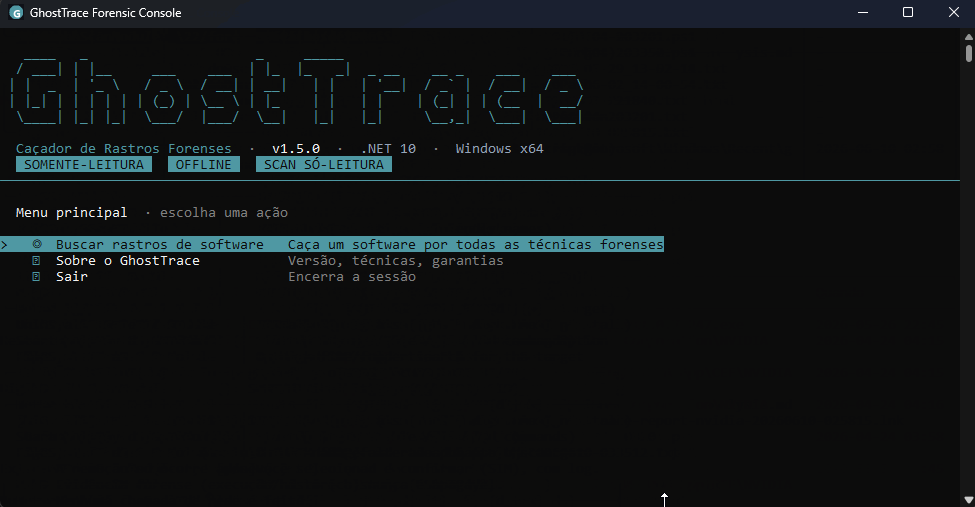
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
digital-forensicsforensicsincident-response+3
2 months ago
RAMnesia-Attack preview

RAMnesia-Attack

GitHubdemining/ramnesia-attack

Scientific investigation of hardware vulnerabilities (CVE-2025-6202, CVE-2023-39910) enabling ECDSA key recovery from Bitcoin infrastructure via…

binary-analysiscryptographyeducation+8
17 months ago
CVE-2025-54574-Squid-Heap-Buffer-Overflow preview

CVE-2025-54574-Squid-Heap-Buffer-Overflow

GitHubstarrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow

Vulnerability Found on Squid Proxy.
binary-analysisexploitationfuzzing+3
8 months ago
cve-2015-4843-type-confusion-phrack preview
Archived

cve-2015-4843-type-confusion-phrack

GitHubsoteria-research/cve-2015-4843-type-confusion-phrack

Demonstrates type confusion and heap overflow exploits for CVE-2015-4843 in Java, with demos for aarch64 and Morello, highlighting CHERI capability…
binary-exploitationeducationexploitation+3
2 years ago
CryKeX preview

CryKeX

GitHubcryptolok/crykex

Linux Memory Cryptographic Keys Extractor

cryptographydigital-forensicsencryption-decryption-tools+2
2423 years ago
CVE-2023-32784 preview

CVE-2023-32784

GitHubdawnl3ss/cve-2023-32784

Retrieve the master password of a keepass database <= 2.53.1

exploitationforensicsmemory-forensics+2
3 years ago
mal_unpack preview

mal_unpack

GitHubhasherezade/mal_unpack

Dynamic unpacker based on PE-sieve

binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
8425 months ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2682 years ago
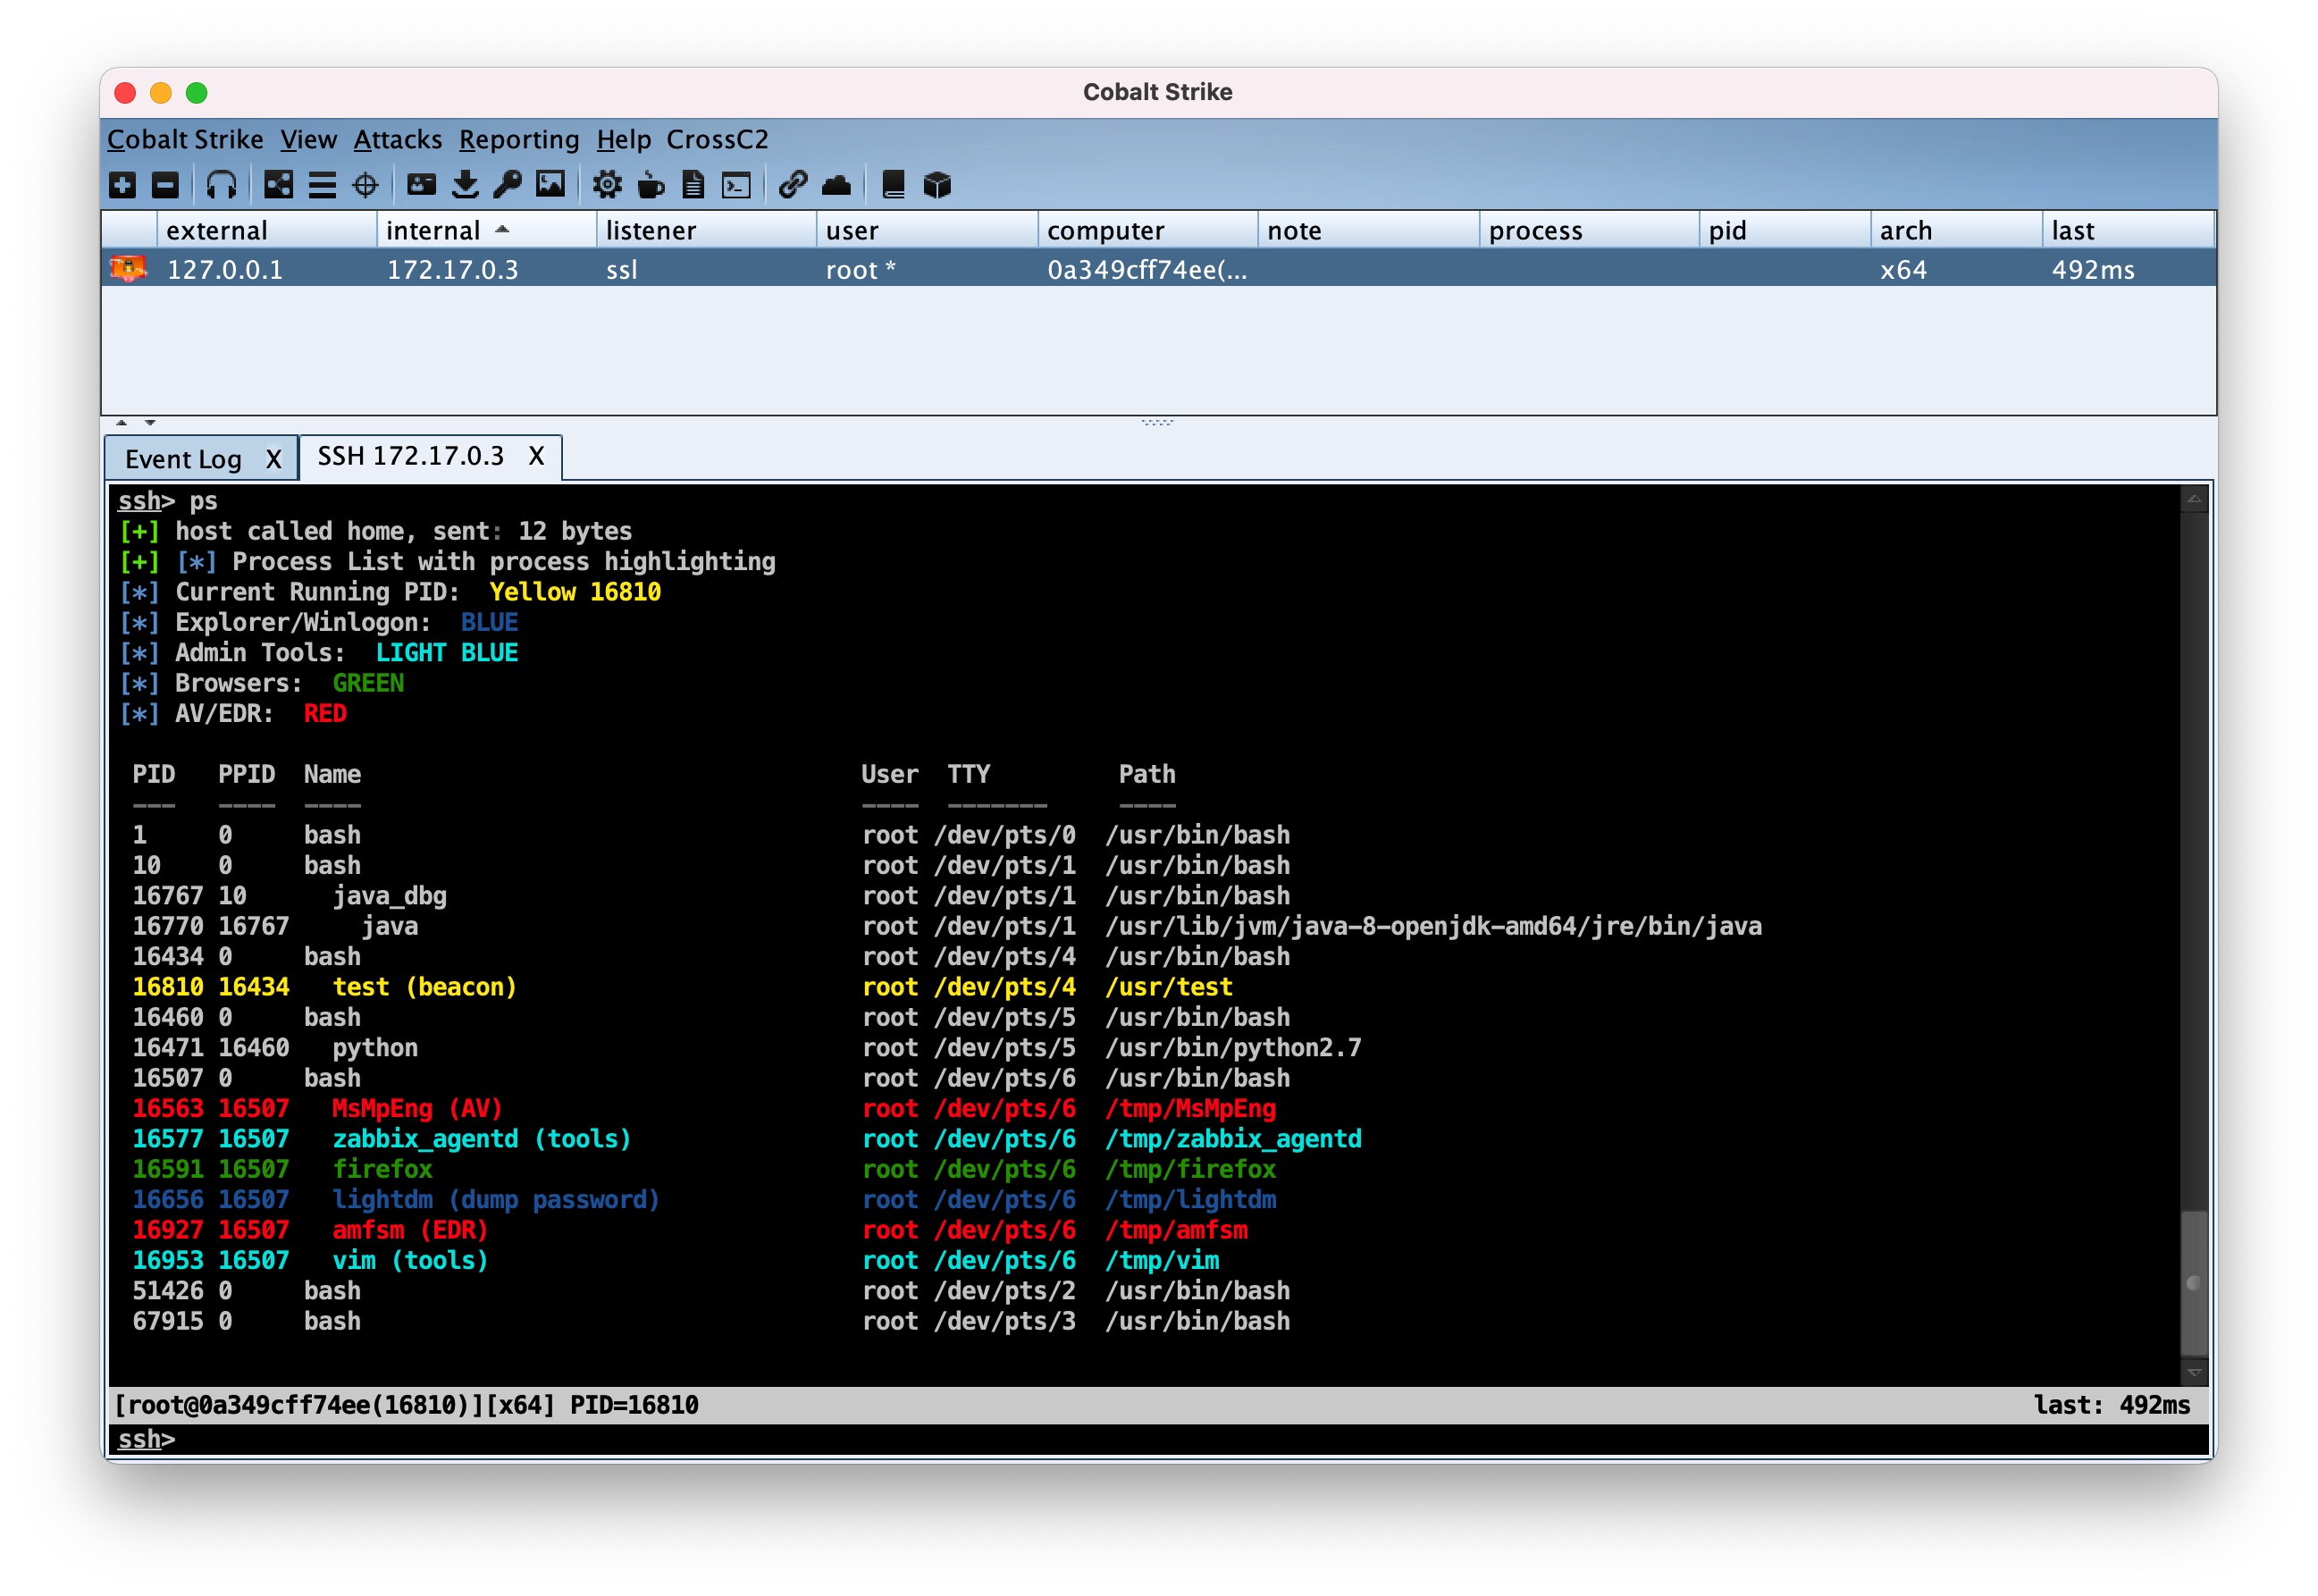
CrossC2Kit preview

CrossC2Kit

GitHubcrossc2/crossc2kit

CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…

command-and-controlexploit-frameworksinformation-gathering+7
2283 years ago
Previous1…678…10Next