
Centry
 0xpoly/centry
Panic button for protection against cold boot attacks
data-recoverydefensive-toolsencryption-decryption-tools+3
0xpoly/centryPanic button for protection against cold boot attacks
 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 fortra/nanodump
The swiss army knife of LSASS dumping

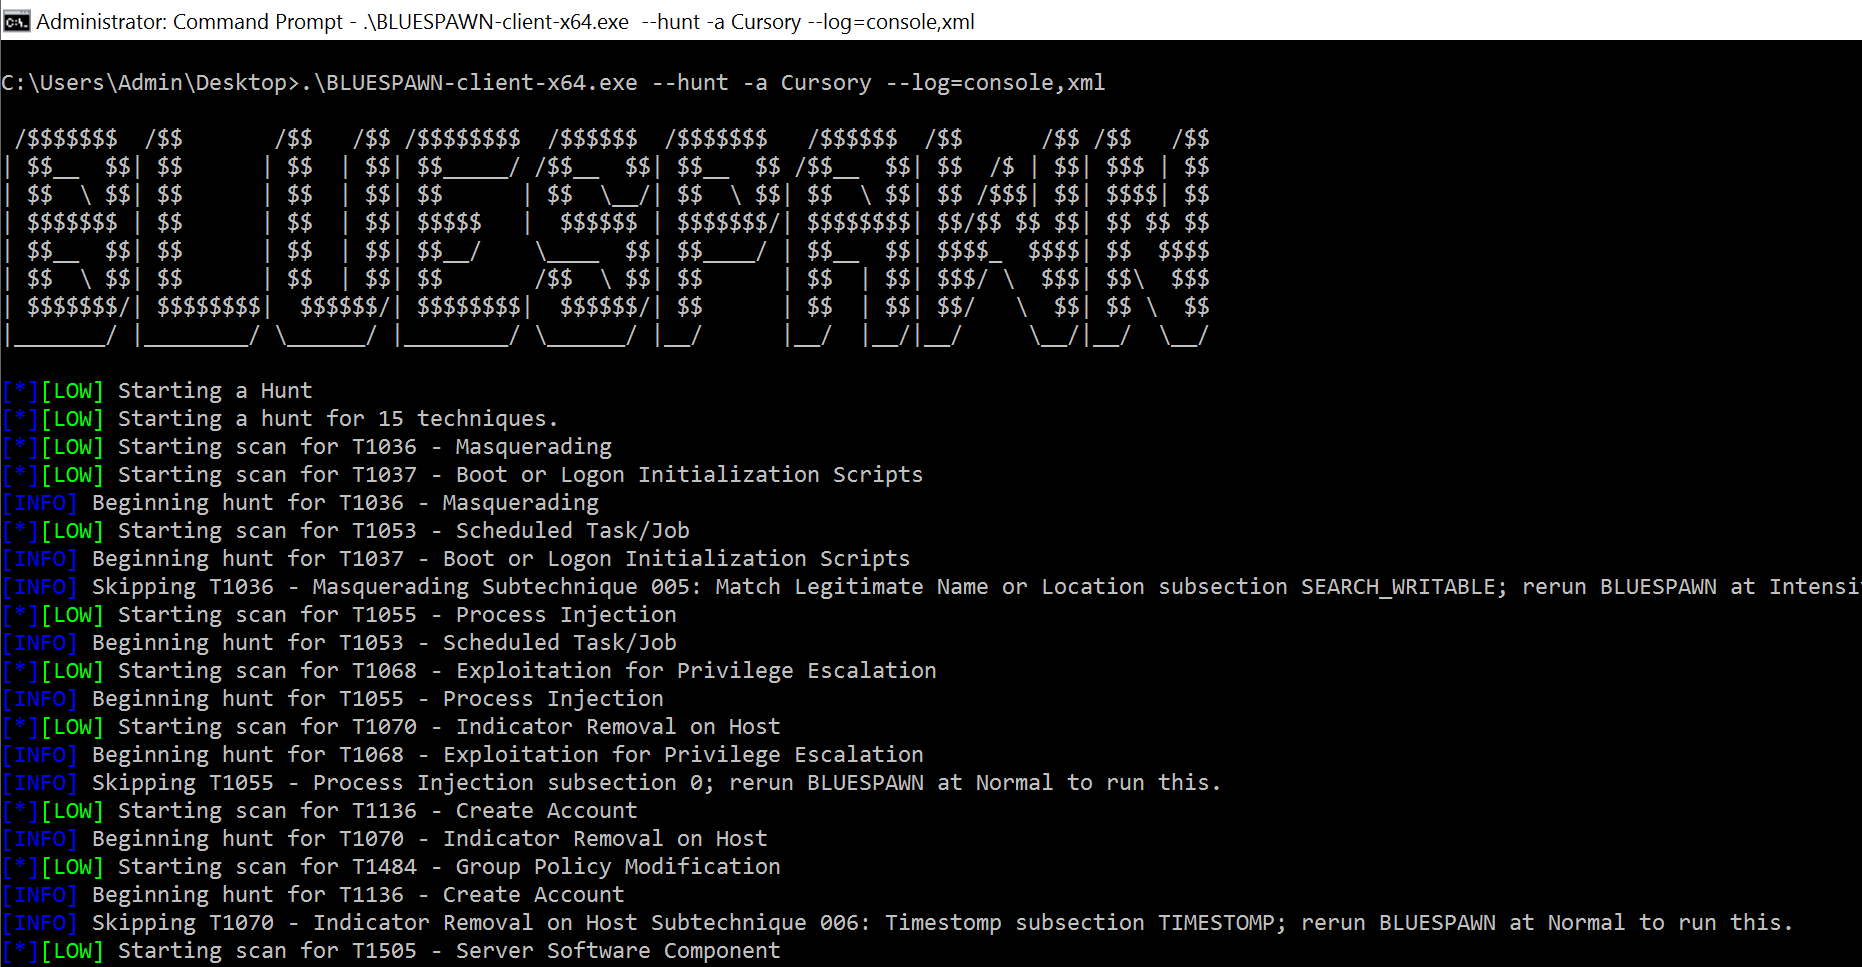 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams
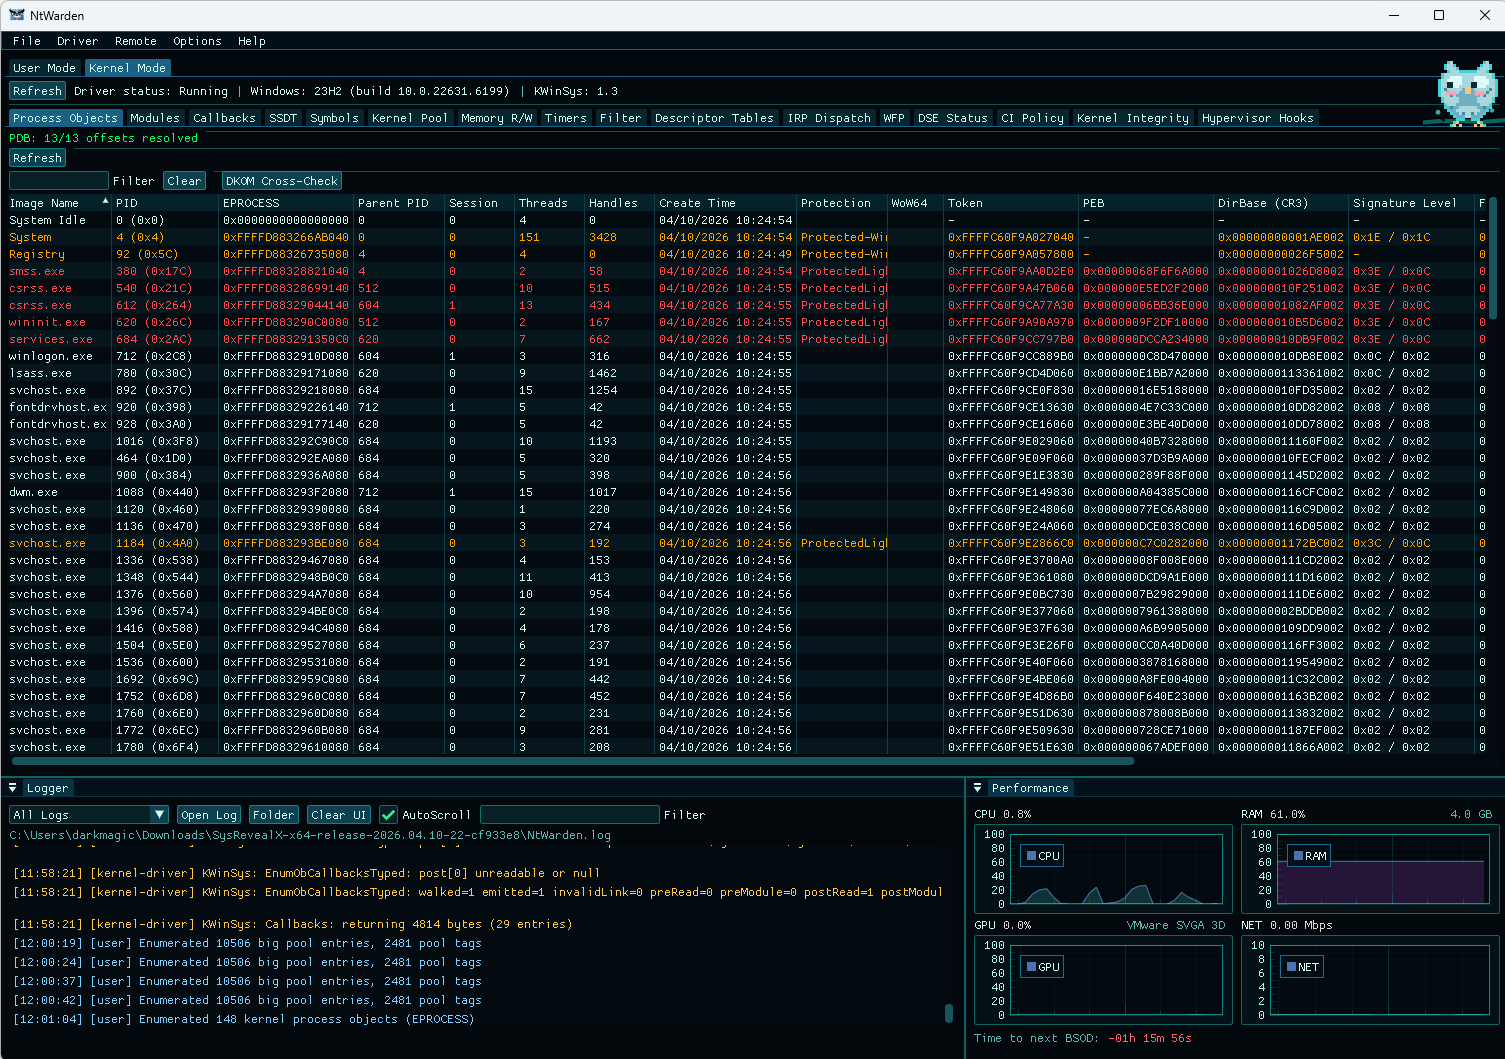 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
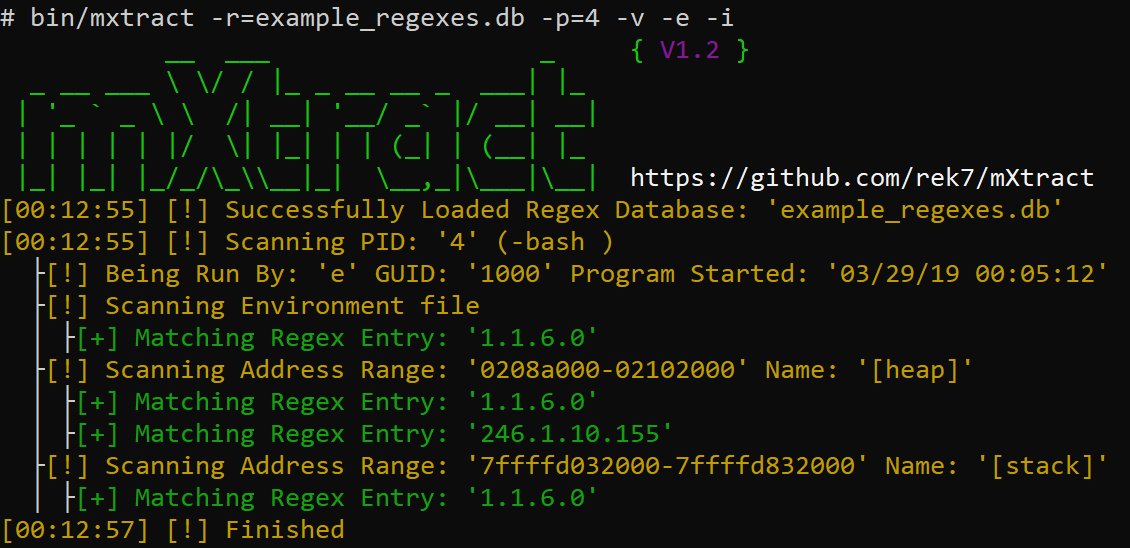 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
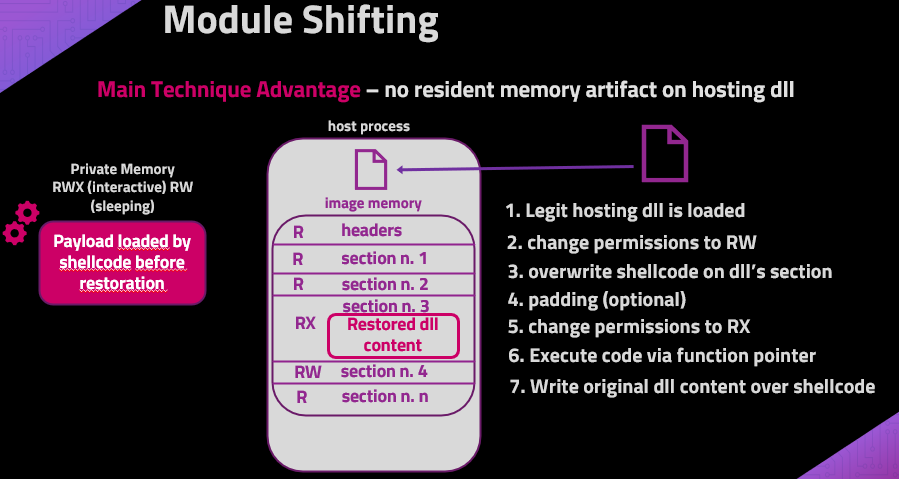 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes