

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
124 results
fsop-finder preview

fsop-finder

GitHubxf1les/fsop-finder

Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.

binary-analysisbinary-exploitationexploitation+5
12
4 years ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
binary-analysiscommand-and-controldata-exfiltration+6
62 months ago
copyfail-rs preview

copyfail-rs

GitHubliverwortenuresis371/copyfail-rs

Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
authenticationbinary-exploitationexploitation+7
8 days ago
cve-2023-31355-poc preview

cve-2023-31355-poc

GitHubfreax13/cve-2023-31355-poc

Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
binary-exploitationencryption-decryption-toolsexploitation+4
82 years ago
CVE-2026-29923 preview

CVE-2026-29923

GitHubsmarttfoxx/cve-2026-29923

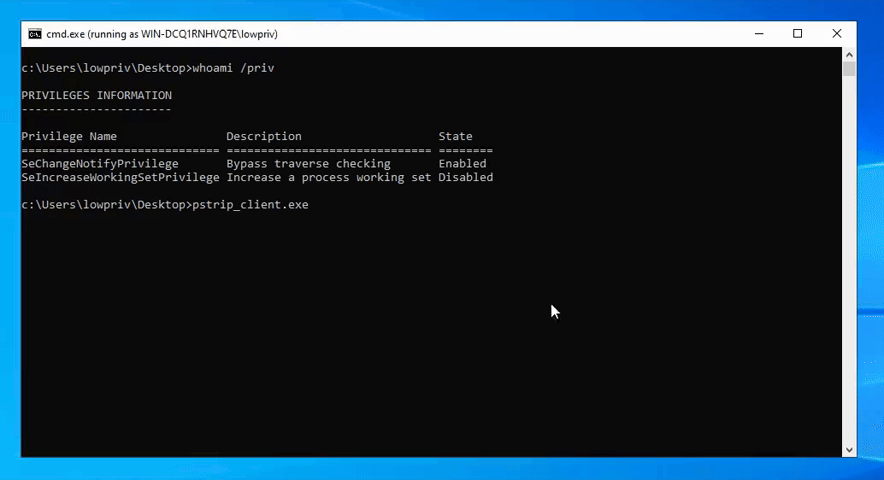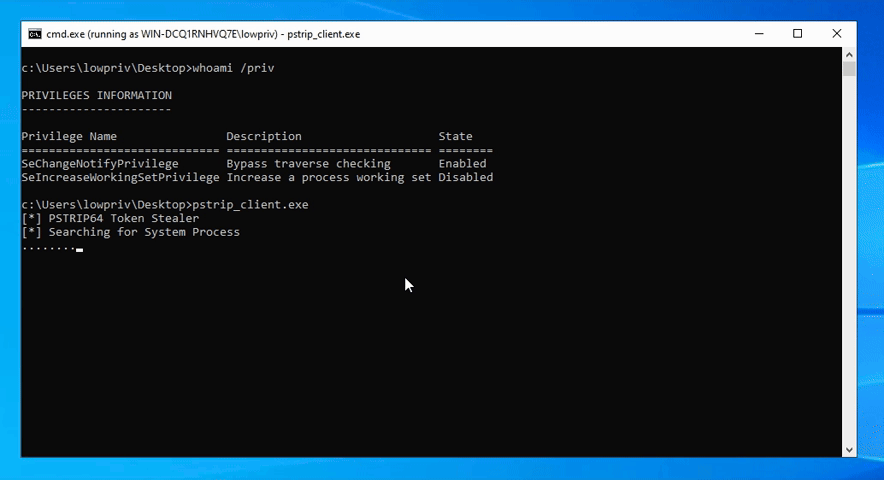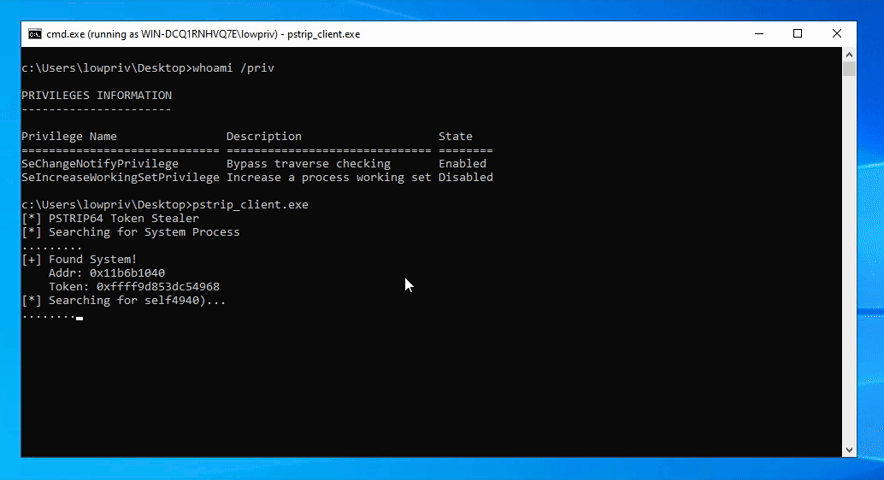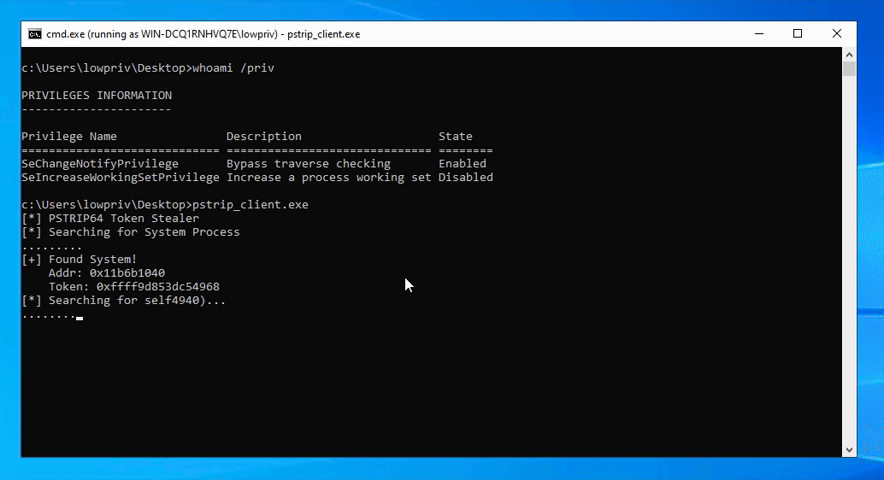
The pstrip64.sys kernel driver exposes an IOCTL that allows low-privileged users to map arbitrary ranges of physical memory into their own virtual…
binary-exploitationexploitationmemory-forensics+3
46 months ago
CVE-2021-46702 preview

CVE-2021-46702

GitHubexmak-s/cve-2021-46702

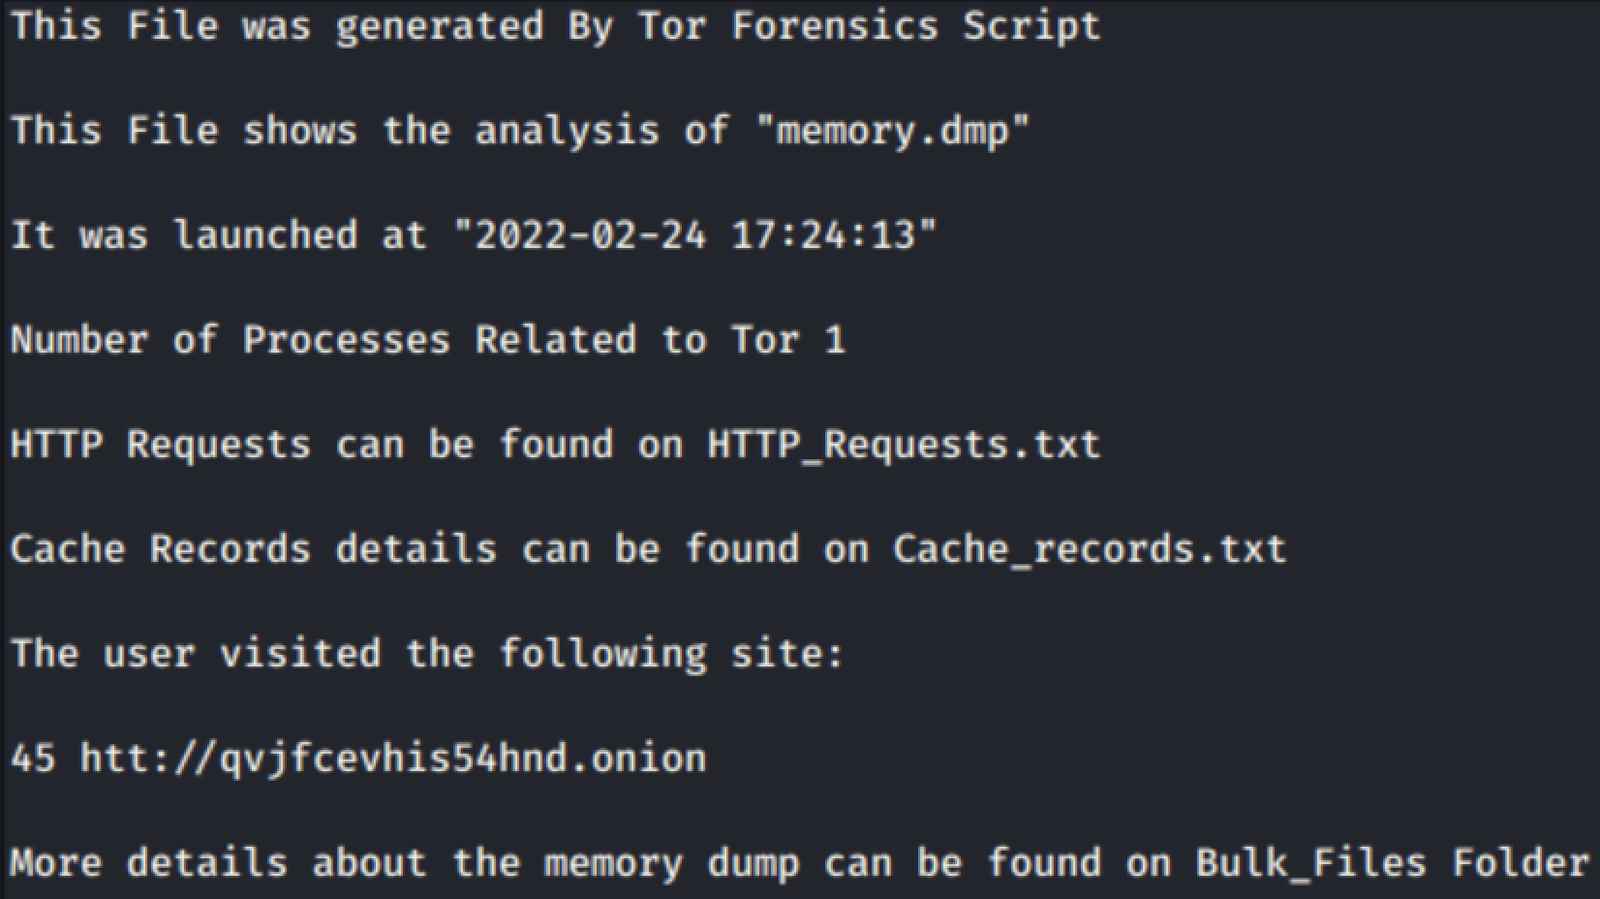
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…

digital-forensicsexploitationinformation-gathering+2
64 years ago
MSRMapper preview

MSRMapper

GitHubull0a/msrmapper

Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
binary-exploitationexploitationmemory-forensics+6
31 month ago
Embarcadero-Workaround preview

Embarcadero-Workaround

GitHubhelpsystems/embarcadero-workaround

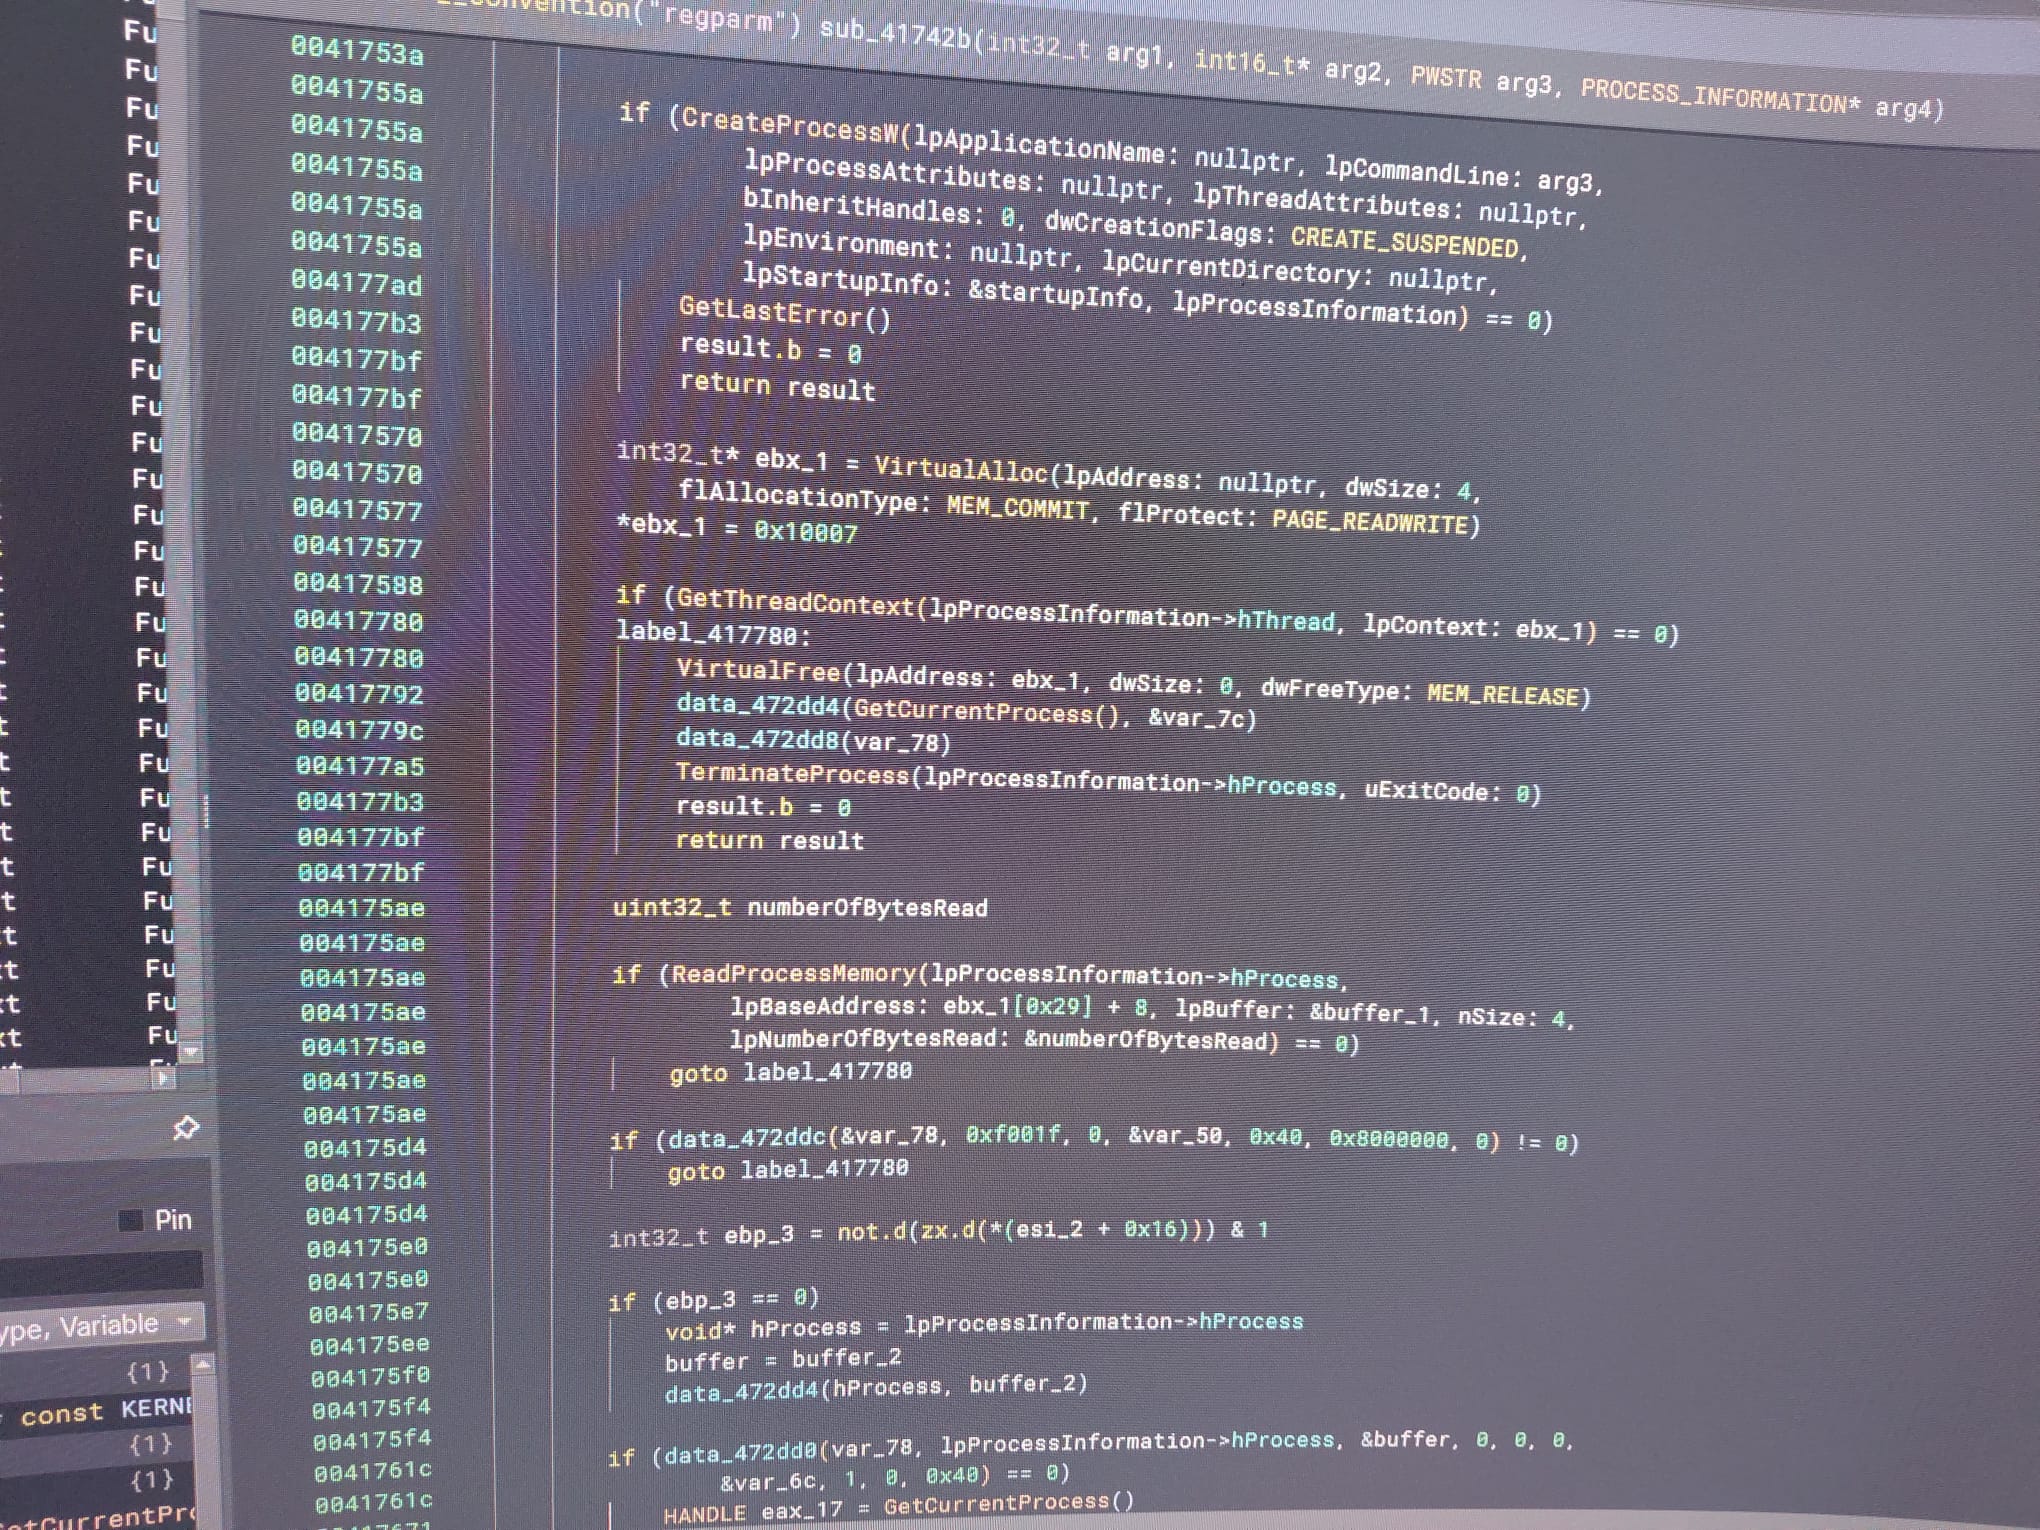
This is a workaround for CVE-2014-0993 and CVE-2014-0994 that patches on memory without the need to recompile your vulnerable software. This is not…
binary-analysisdefensive-toolsexploitation+3
111 years ago
-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis- preview

-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis-

GitHubkaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…

api-securitybinary-analysisdynamic-analysis-sandboxing+8
23 months ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
12 months ago
CVE-2024-33901-ProofOfConcept preview

CVE-2024-33901-ProofOfConcept

GitHubgmikisilva/cve-2024-33901-proofofconcept

Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
data-exfiltrationdigital-forensicsexploitation+3
21 year ago
cve-2018-12798 preview

cve-2018-12798

GitHubsandi-go/cve-2018-12798

Proof-of-concept exploit for CVE-2018-12798, a heap overflow in Adobe Acrobat Reader that enables remote code execution via malicious PDF files.

binary-exploitationexploitationmemory-forensics+2
7 years ago
linux-CVE-2006-4814 preview

linux-CVE-2006-4814

GitHubtagatac/linux-cve-2006-4814

A deadlock on the mmap semaphore ‘mmap sem’ in the CentOS 3.9 kernel, that is triggered by a specific interleaving of concurrent threads, one calling…
binary-exploitationexploitationmemory-forensics+1
12 years ago
CVE-2021-32537 preview
Archived

CVE-2021-32537

GitHub0vercl0k/cve-2021-32537

PoC for CVE-2021-32537: an out-of-bounds memory access that leads to pool corruption in the Windows kernel.

binary-exploitationexploitationmemory-forensics+1
555 years ago
SilkETW preview
Archived

SilkETW

GitHubmandiant/silketw

C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

anomaly-detectiondefensive-toolsdigital-forensics+8
8523 years ago
CVE-2026-110912 preview

CVE-2026-110912

GitHub0xblackash/cve-2026-110912

Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and…

defensive-toolseducationexploitation+5
16 days ago
memory-relocalloc preview

memory-relocalloc

GitHubgmh5225/memory-relocalloc

C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…

binary-exploitationexploitationmalware-analysis+6
24 years ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.3k14h 56m ago
Previous1234567Next