
Archived
DAMM
 504ensicslabs/damm
Differential Analysis of Malware in Memory
digital-forensicsforensicsincident-response+3
214

 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
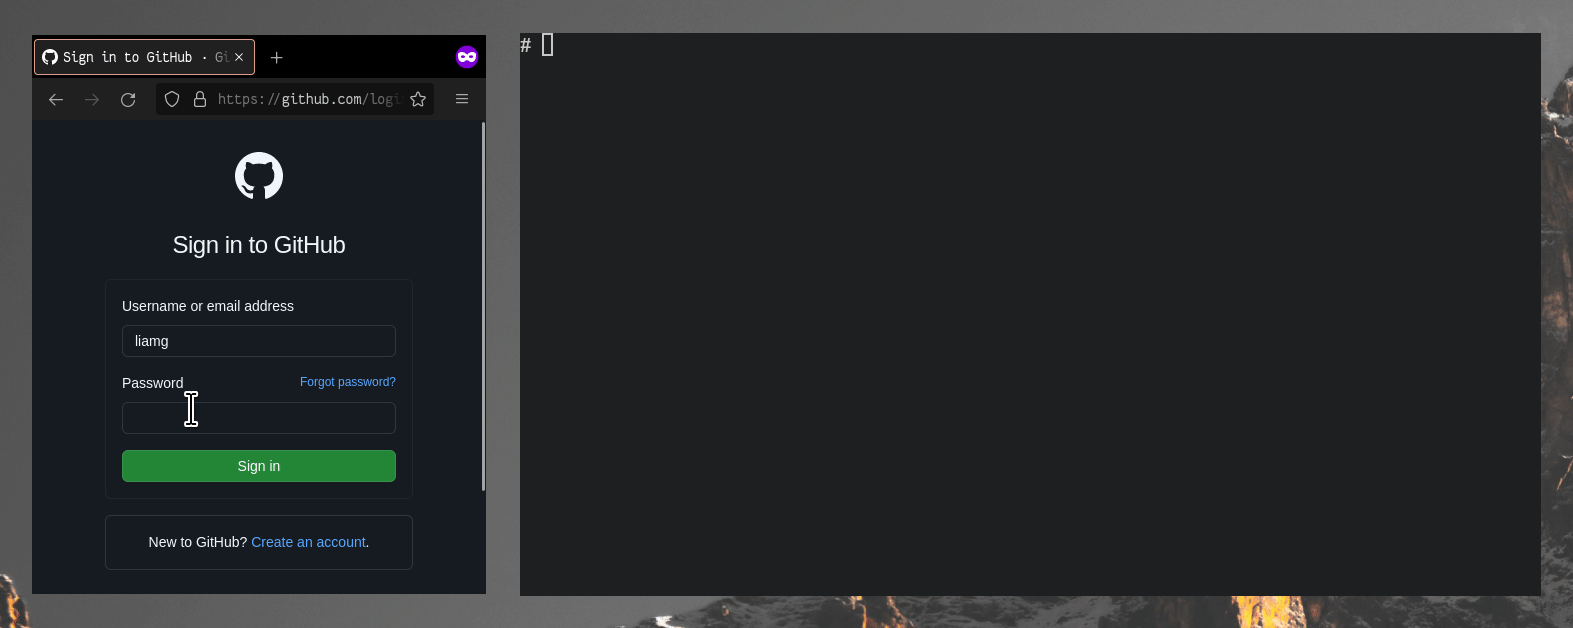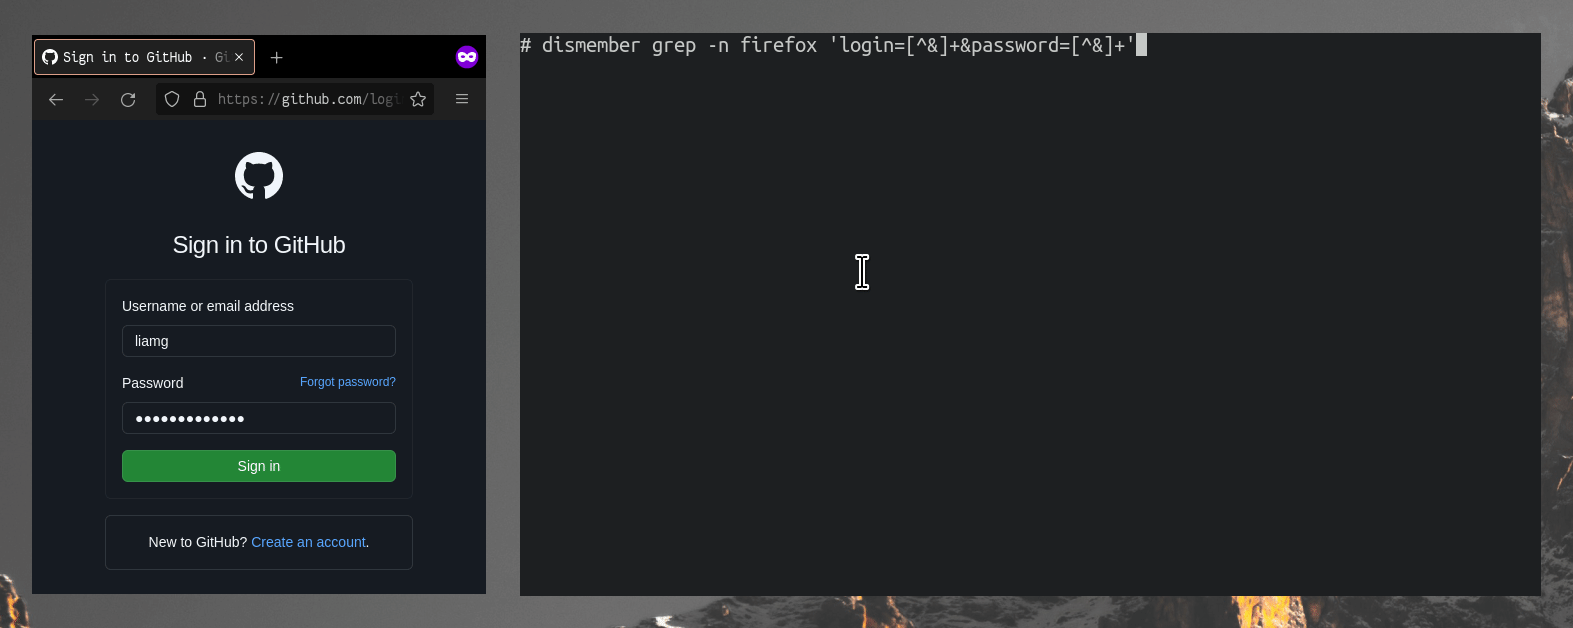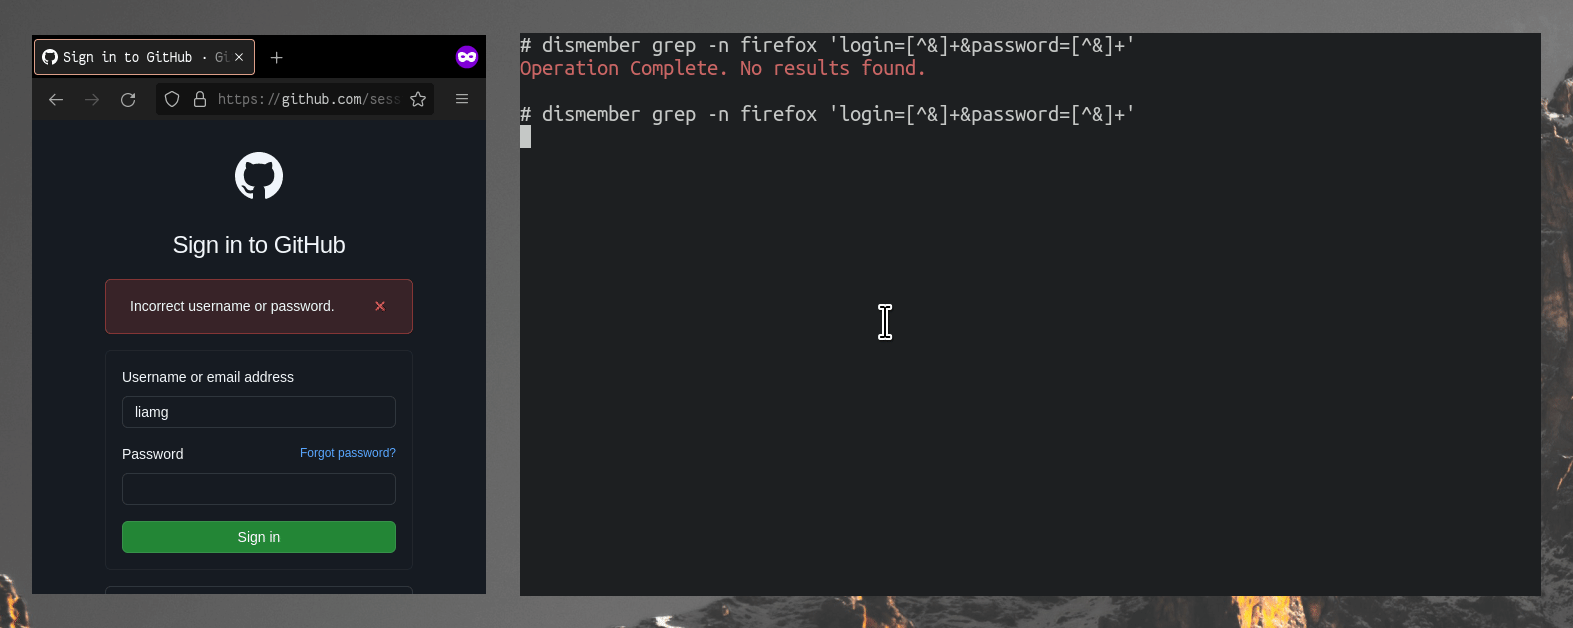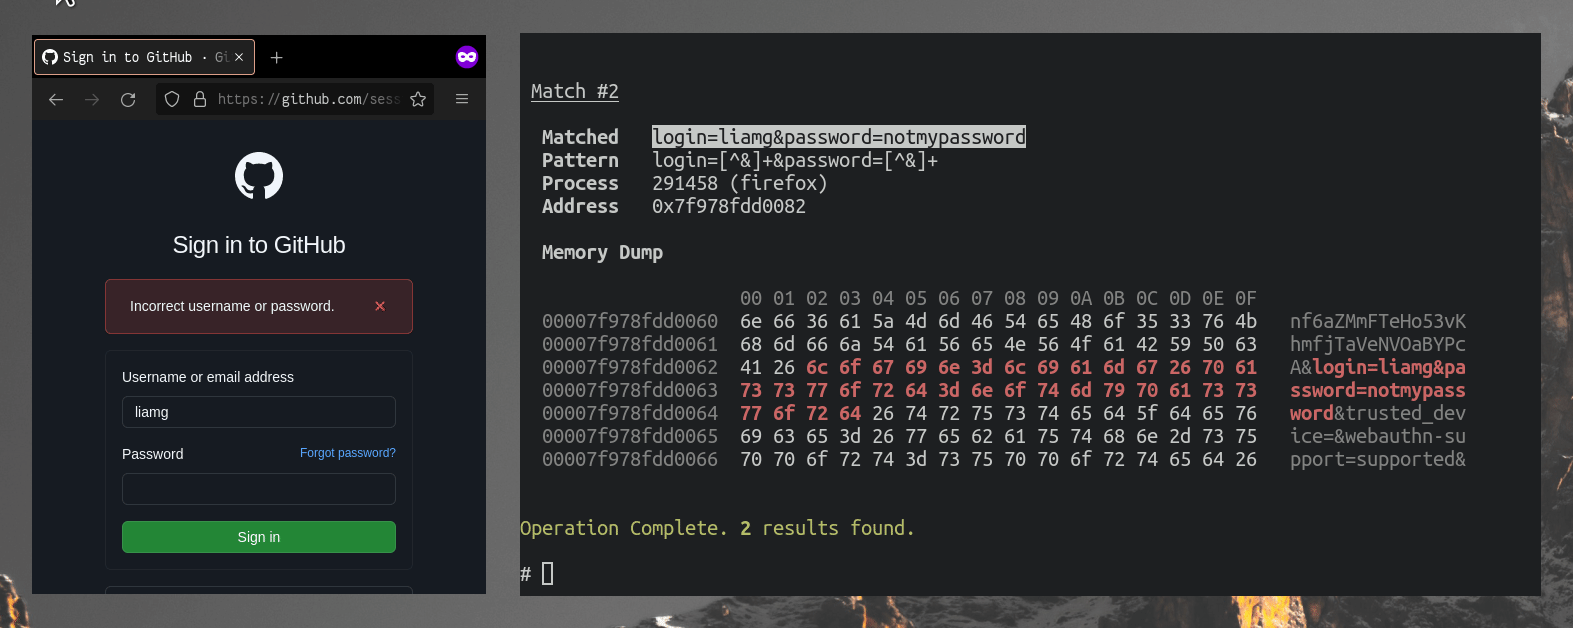 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 eurecom-s3/linux_screenshot_xwindows
Volatility plugin to extract X screenshots from a memory dump
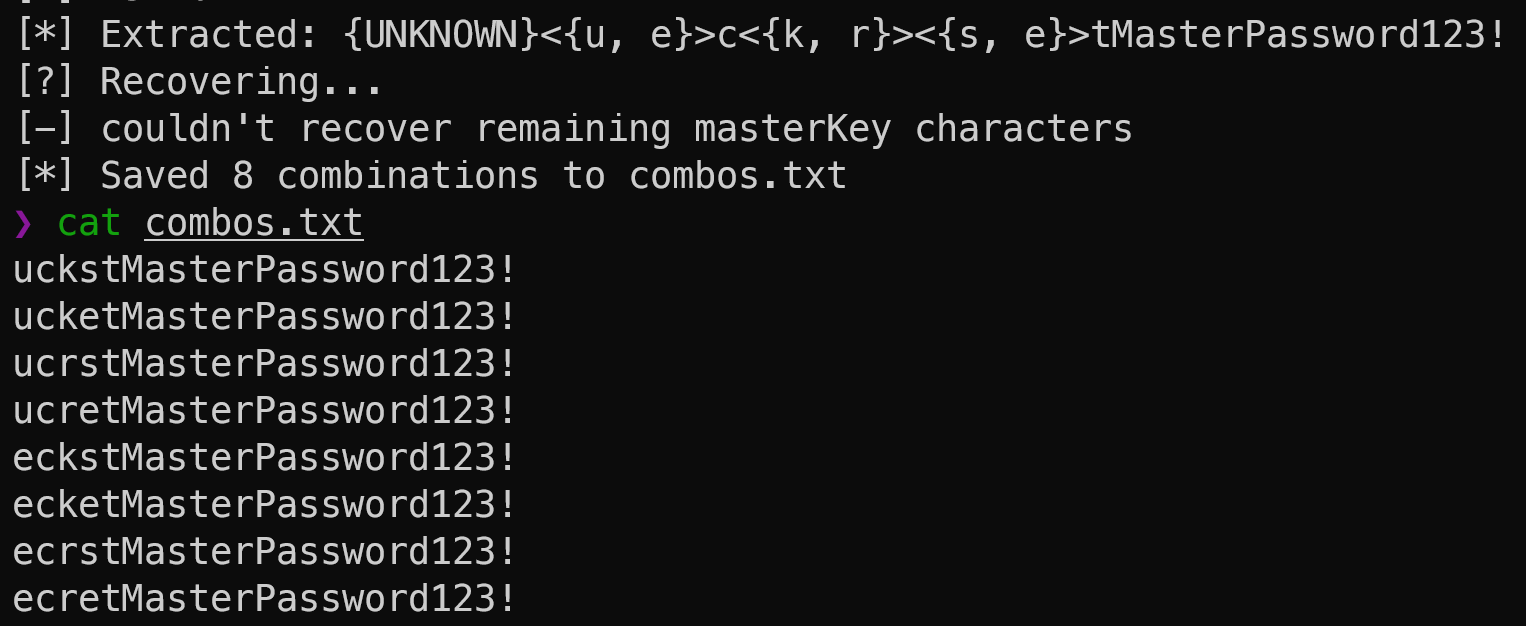 z-jxy/keepass_dump
KeePass 2.X dumper (CVE-2023-32784)
 ctm1/cve-2023-32784-keepass-linux
KeePass Master Password Extraction PoC for Linux
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
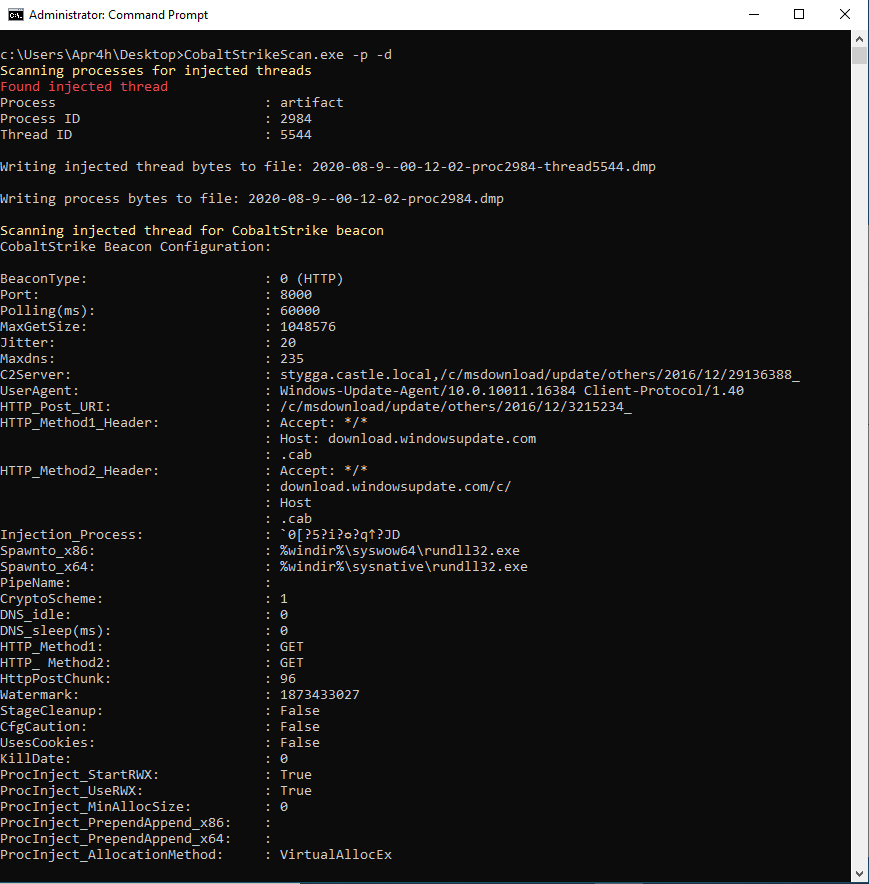 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
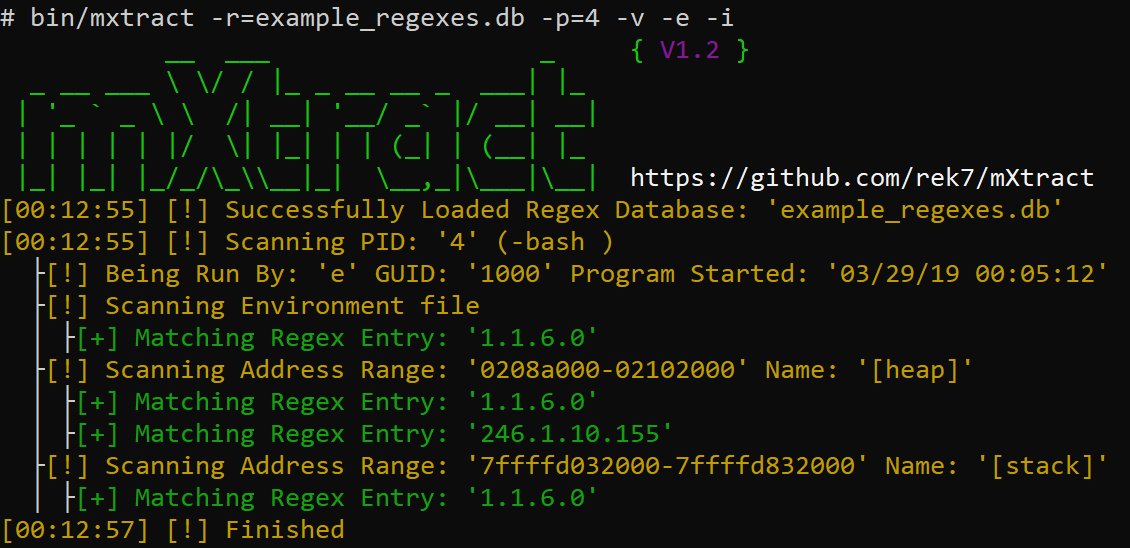 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
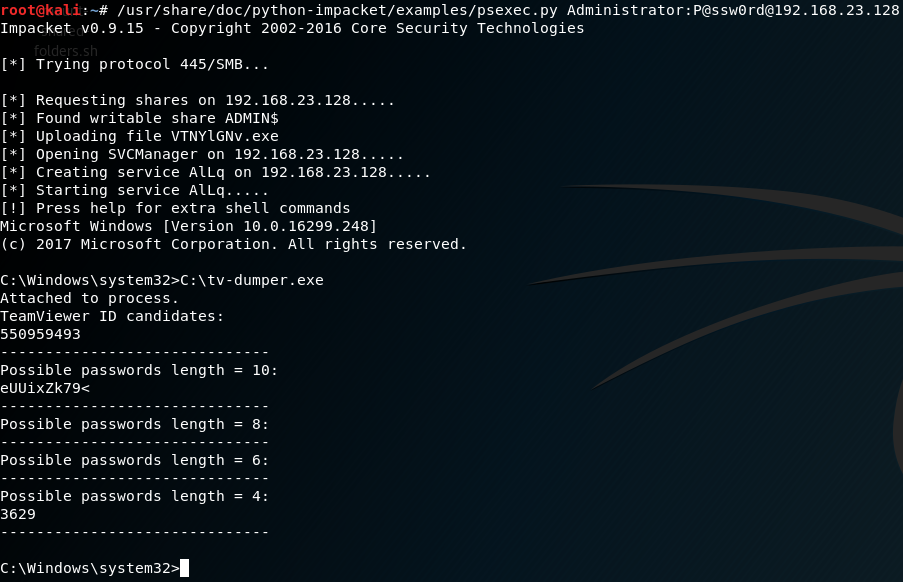 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
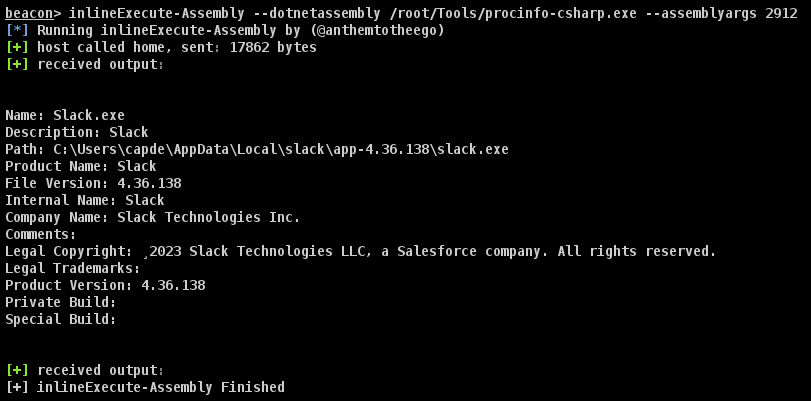 mlcsec/proctools
Small toolkit for extracting information and dumping sensitive strings from Windows processes
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting