
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
97 results
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
1578 years ago
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
1723 months ago
BSOD_bitlocker_recover preview

BSOD_bitlocker_recover

GitHubfishermavis/bsod_bitlocker_recover

Python script for carving Bitlocker VMK keys

data-recoverydigital-forensicsdisk-forensics+3
267 months ago
ForensicMiner preview

ForensicMiner

GitHubsecurityjoes/forensicminer

A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
digital-forensicsdisk-forensicsforensics+2
1651 year ago
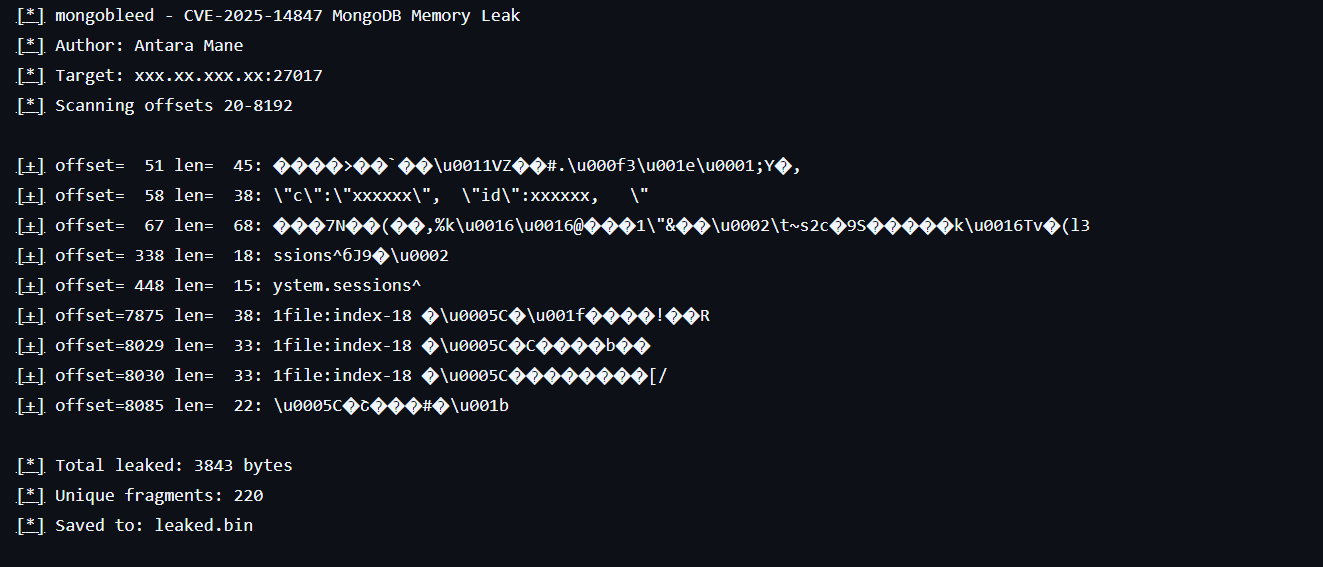
CVE-2025-14847-MongoDB preview

CVE-2025-14847-MongoDB

GitHubinfosecantara/cve-2025-14847-mongodb

Educational research tool demonstrating CVE-2025-14847 memory disclosure in MongoDB's BSON decompression. Simulates bounds-checking failures and…

database-securityeducationexploitation+3
17 months ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k7 days ago
LaZagne preview

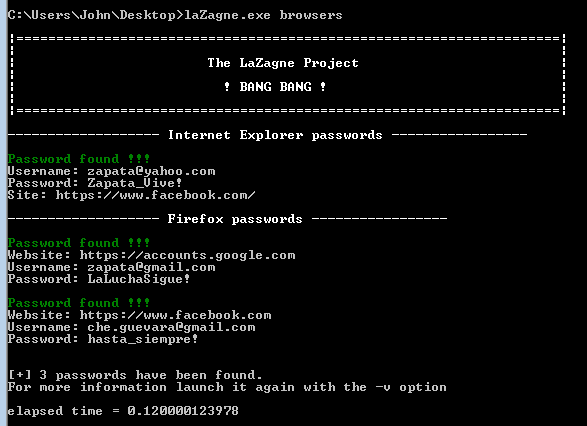
LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.0k0 years ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5215 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

digital-forensicsforensicsincident-response+4
2188 years ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
drmemory preview

drmemory

GitHubdynamorio/drmemory

Memory Debugger for Windows, Linux, Mac, and Android
debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.7k9 months ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
digital-forensicsforensicsinformation-gathering+3
8617 years ago
WinPmem preview

WinPmem

GitHubvelocidex/winpmem

The multi-platform memory acquisition tool.
digital-forensicsforensicsincident-response+1
1.0k11 months ago
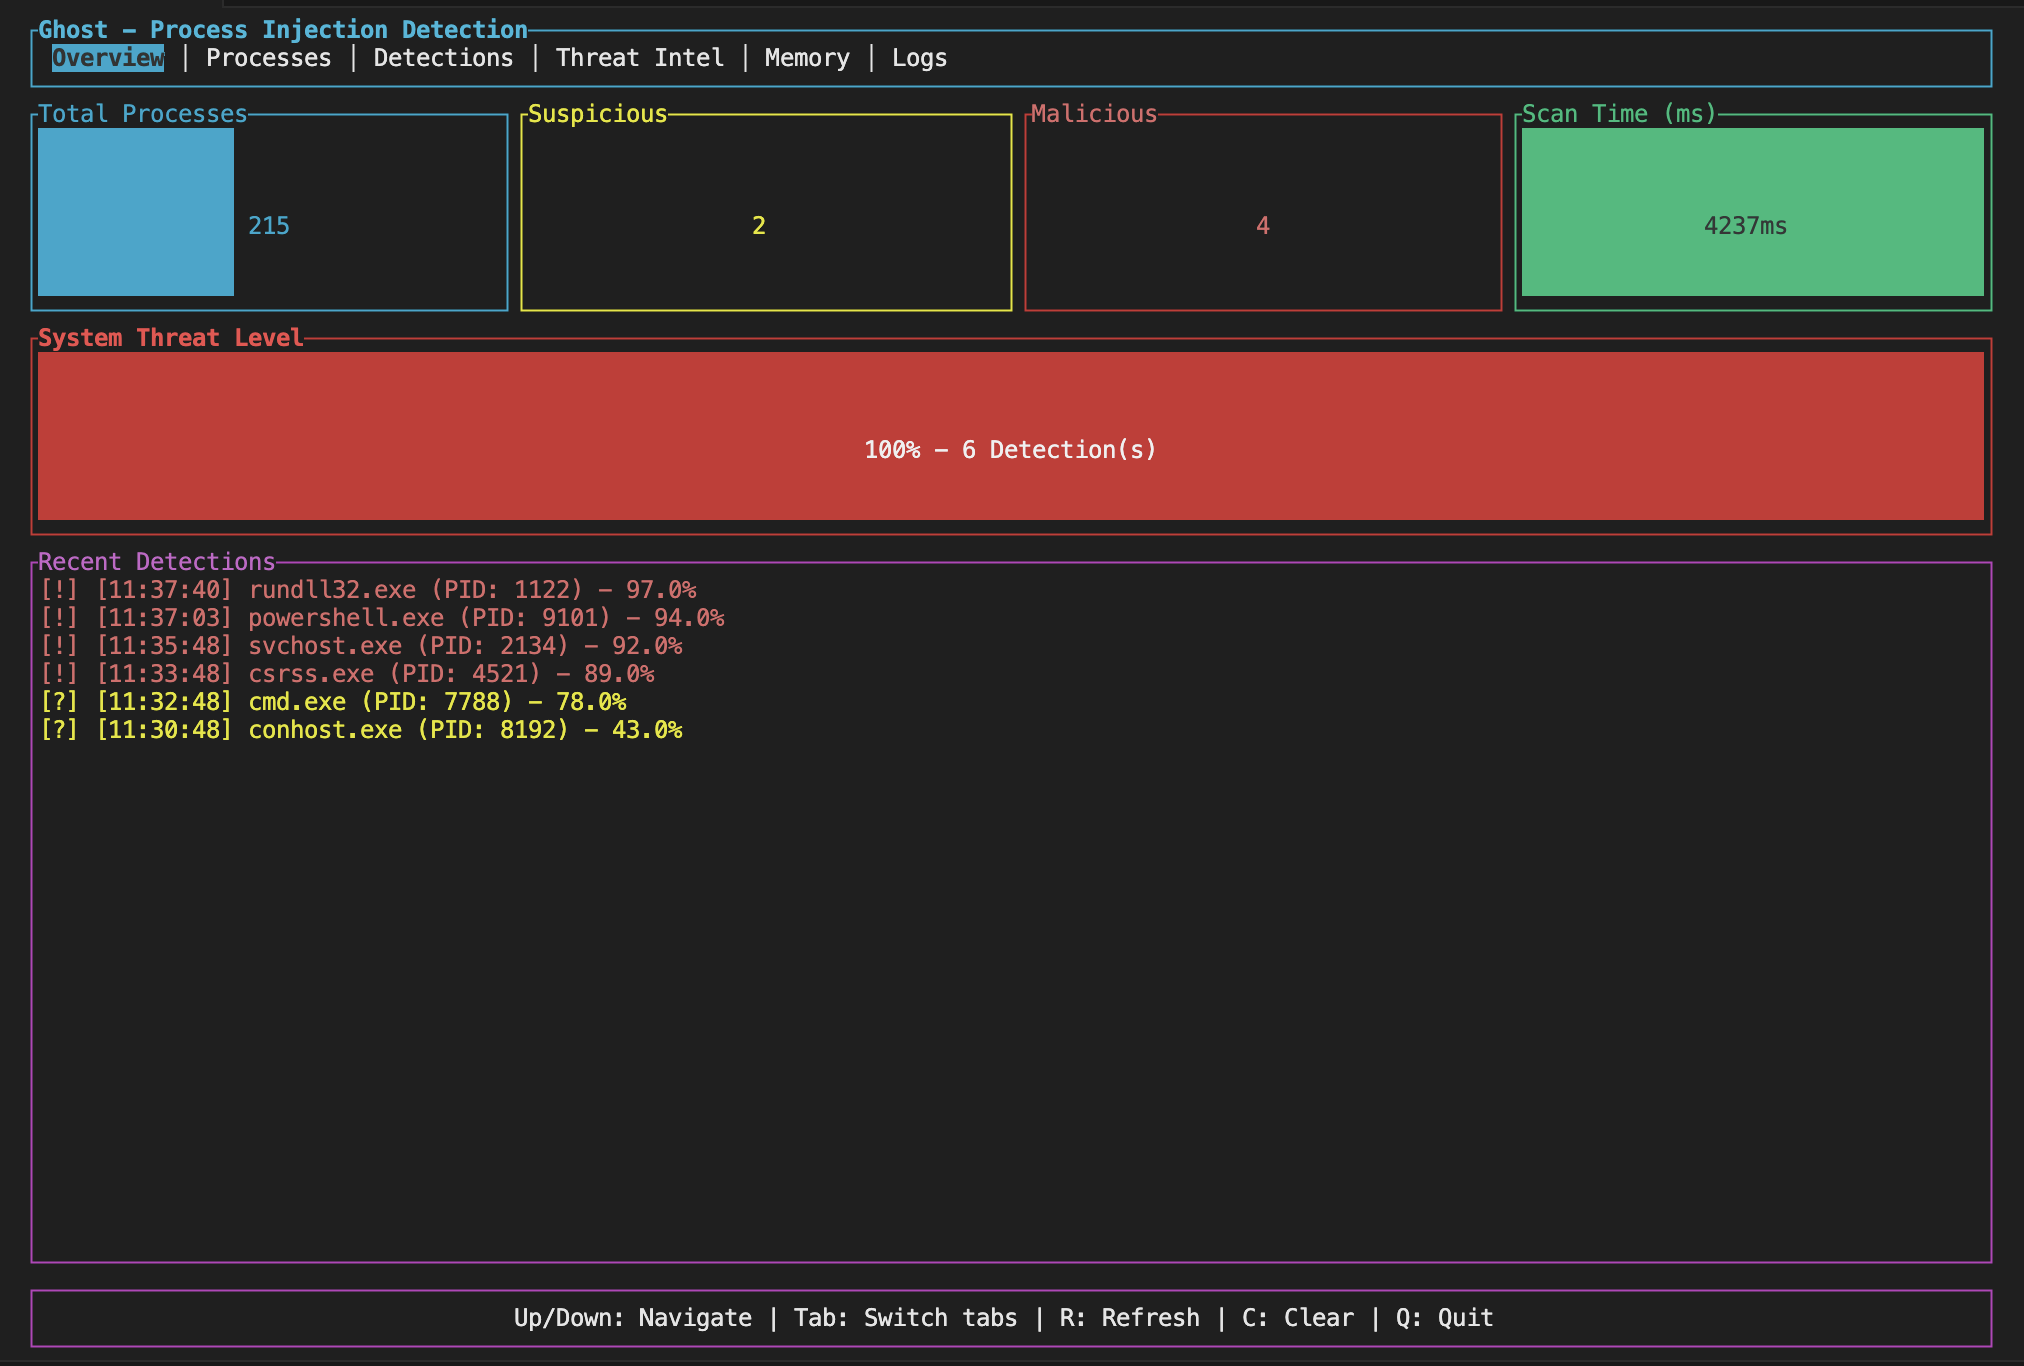
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3911 month ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
1267 years ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
data-recoverydigital-forensicsexploitation+3
1042 months ago
AzTokenFinder preview

AzTokenFinder

GitHubhackmichnet/aztokenfinder

Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
authenticationcloud-securitymemory-forensics+3
1093 years ago
EventHorizon preview

EventHorizon

GitHubhullabrian/eventhorizon

Tool that gathers a customizable set of ETW telemetry and generates user-defined detections

defensive-toolseducationforensics+5
567 months ago
Previous123456Next