

OnTheEdge
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
9
jssngc/ontheedgeWindows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
 cado-security/rip_raw
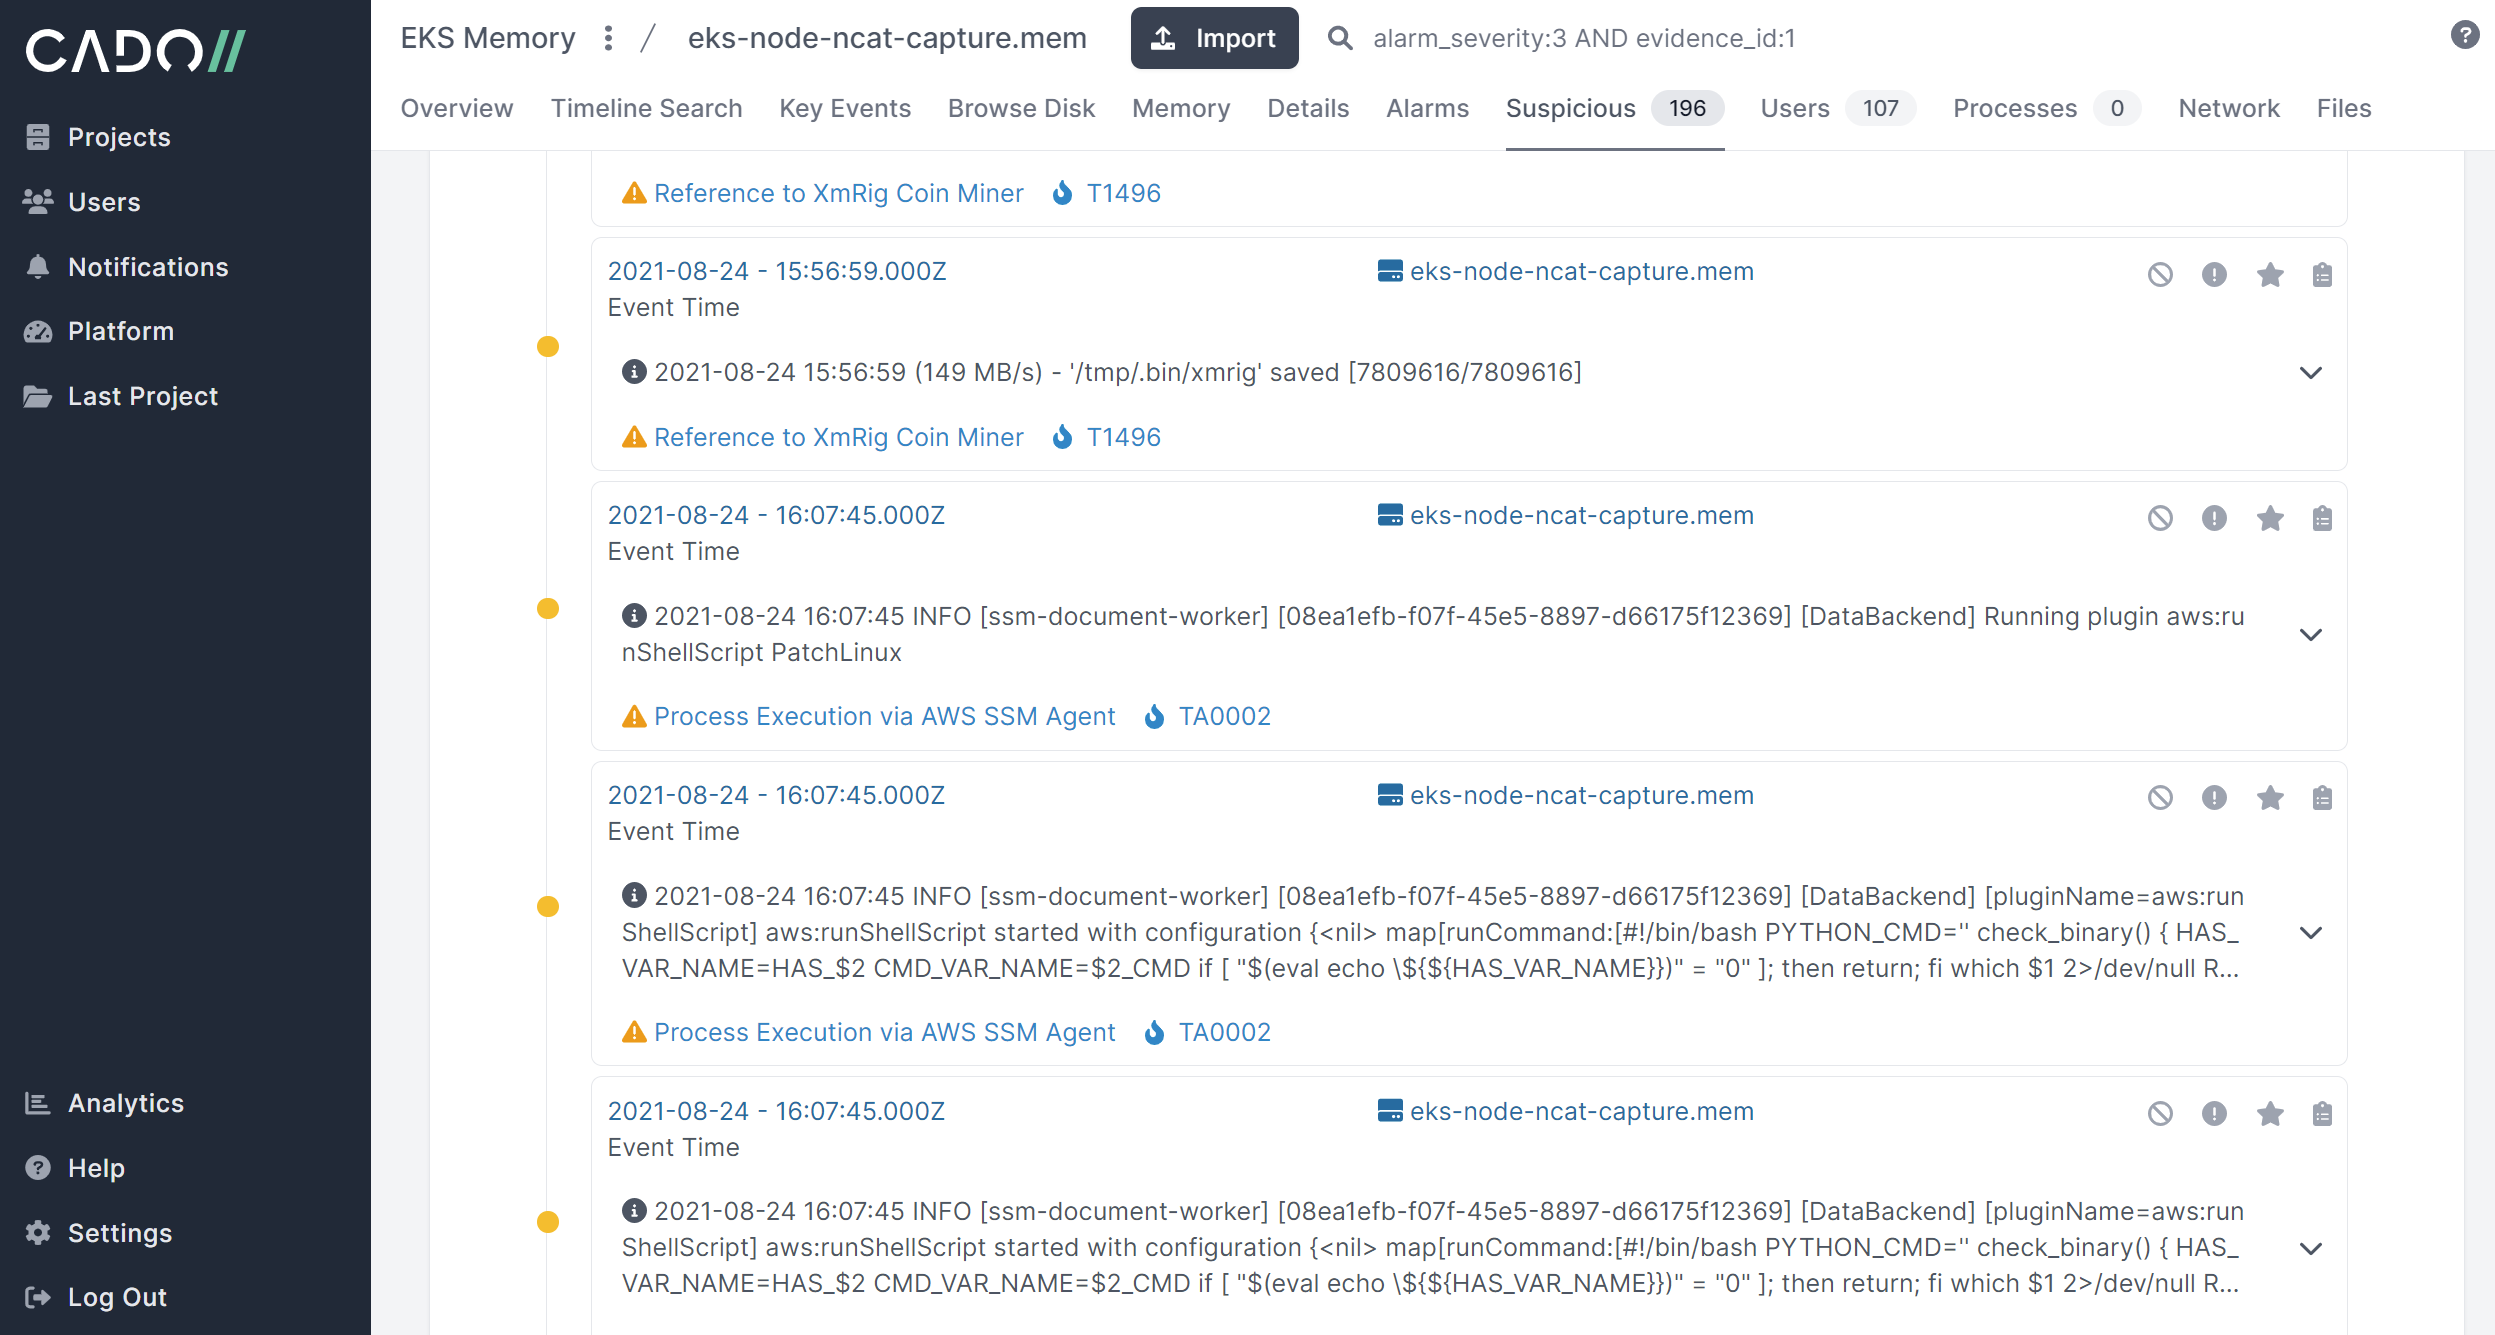
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 mmozeiko/aes-finder
Utility to find AES keys in running processes
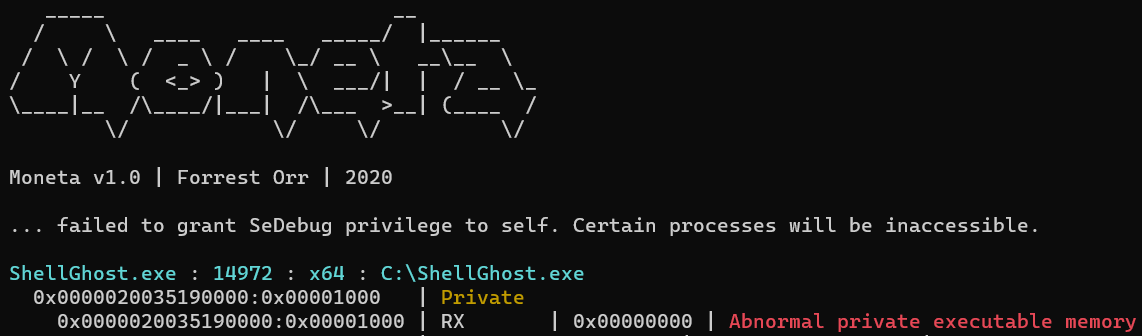 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
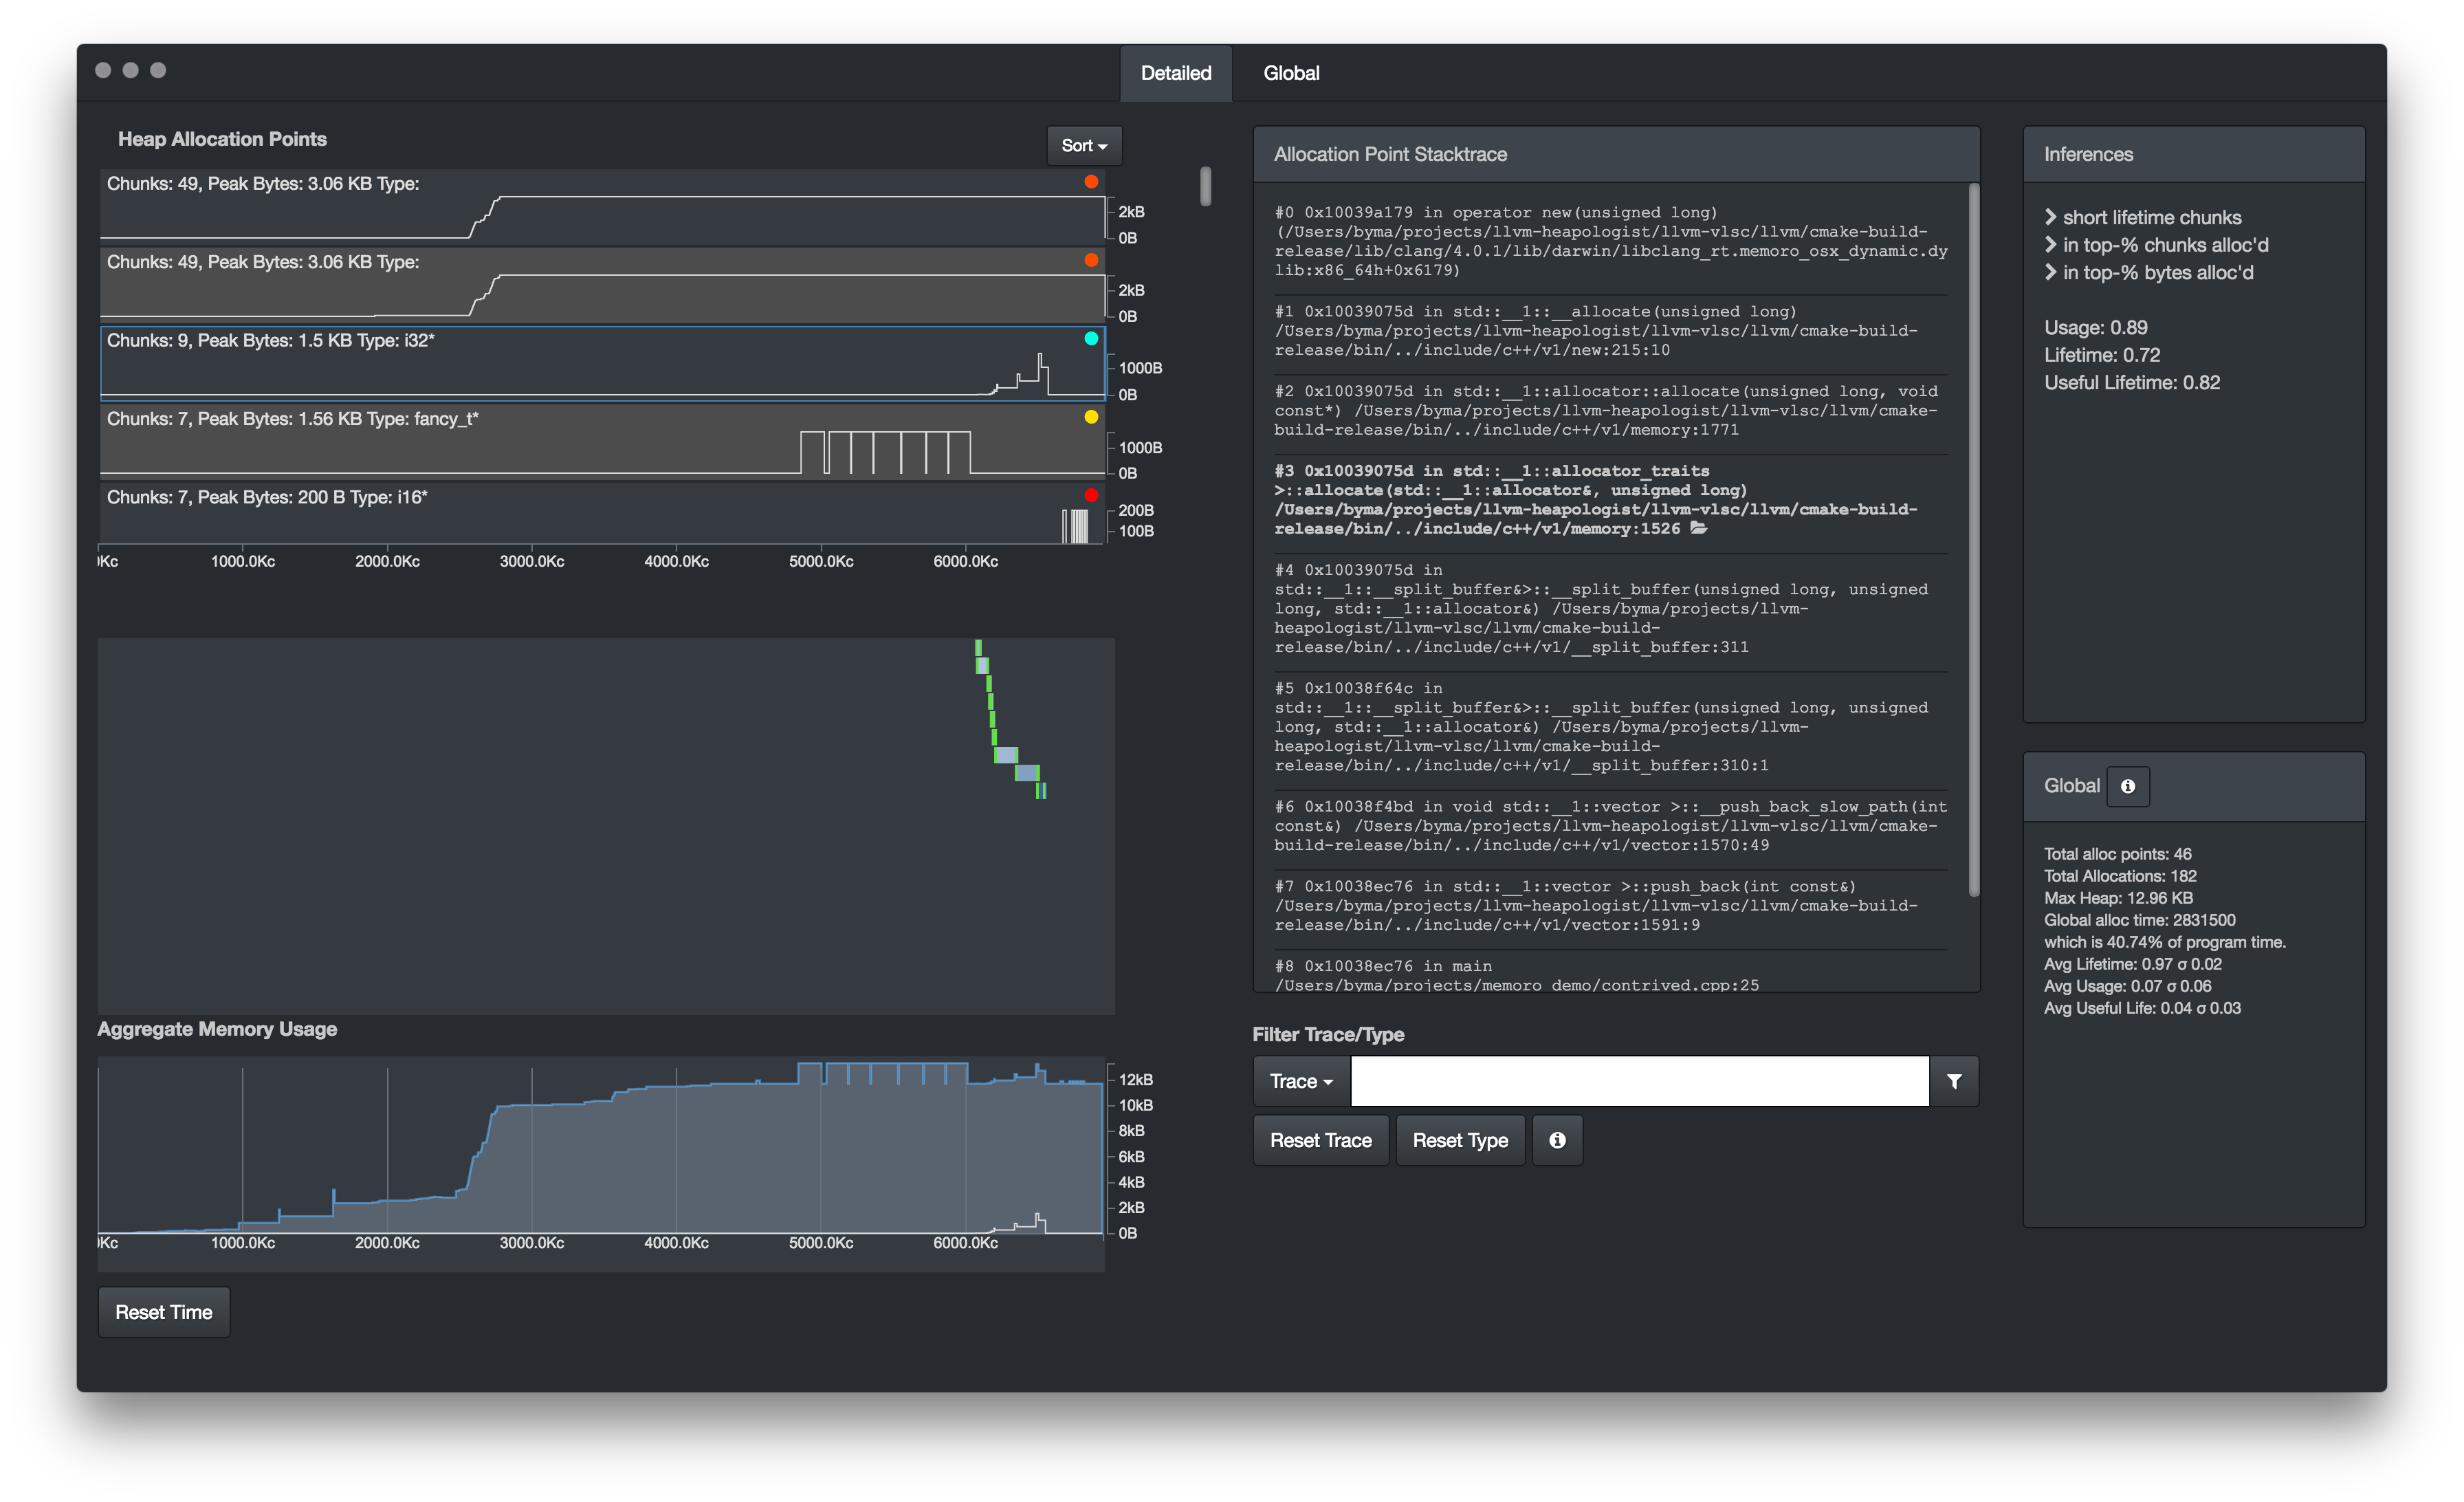 epfl-vlsc/memoro
Memoro: A Detailed Heap Profiler
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 nccgroup/windowspatchdetector
Experimental Windows .text section Patch Detector
 franksec42/mongobleed-exploit-cve-2025-14847
Explot, Lab, Scanner - external and docker container, for SMongobleed-CVE-2025-14847 plus phoenix security uploader
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)