

IRTriage
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
digital-forensicsforensicsincident-response+1
139
ajmartel/irtriageIncident Response Triage - Windows Evidence Collection for Forensic Analysis
 memoryforensics1/volexp
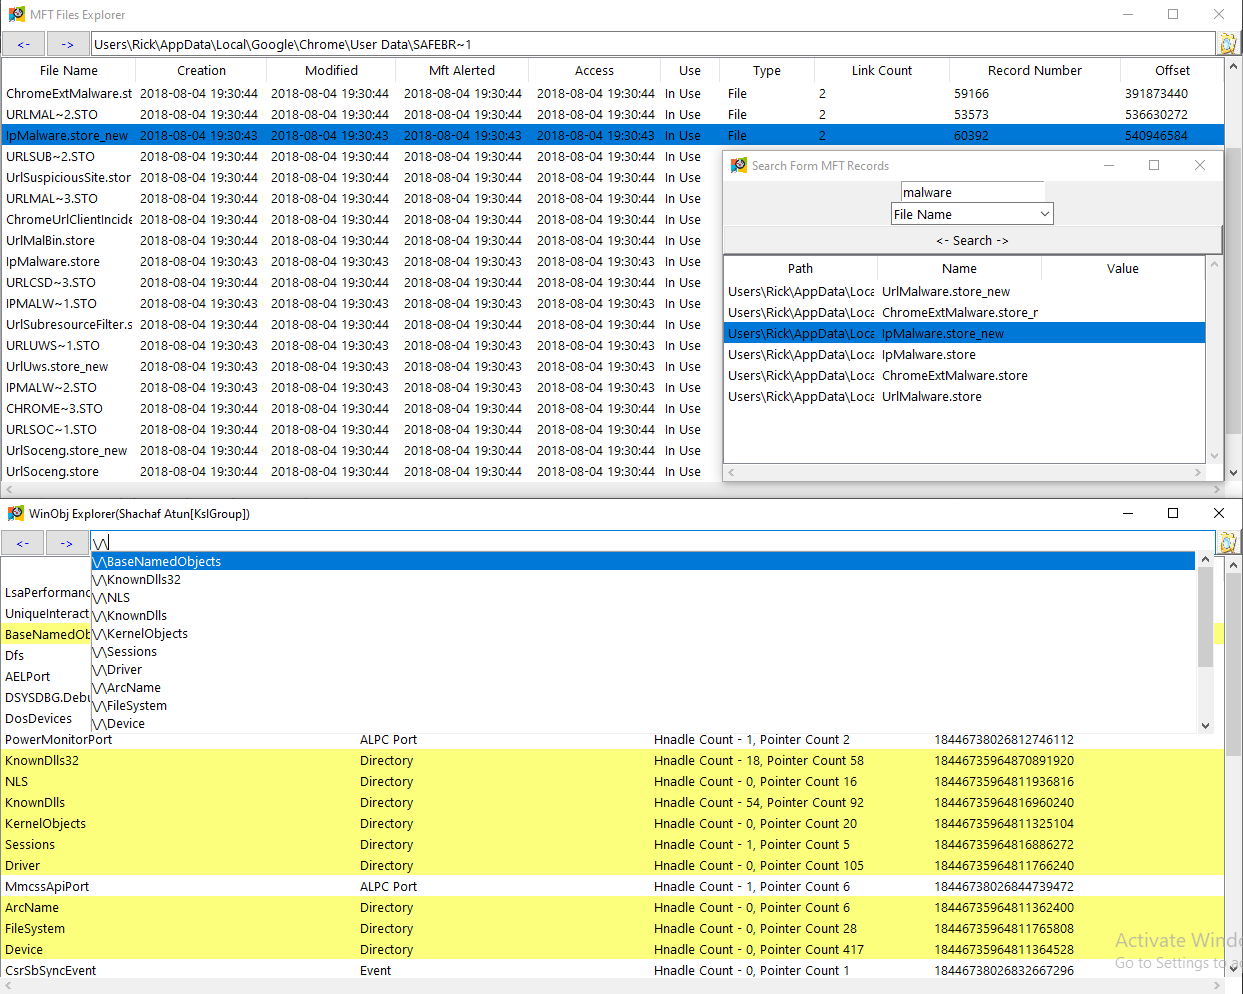
volatility explorer (volatility 2)
 kacperszurek/gpg_reaper
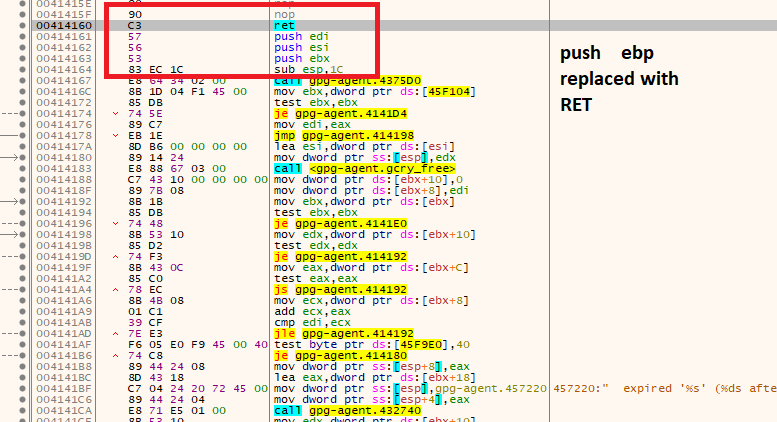
GPG Reaper - Obtain/Steal/Restore GPG Private Keys from gpg-agent cache/memory
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 zhuowei/apple-positional-audio-codec-invalid-header
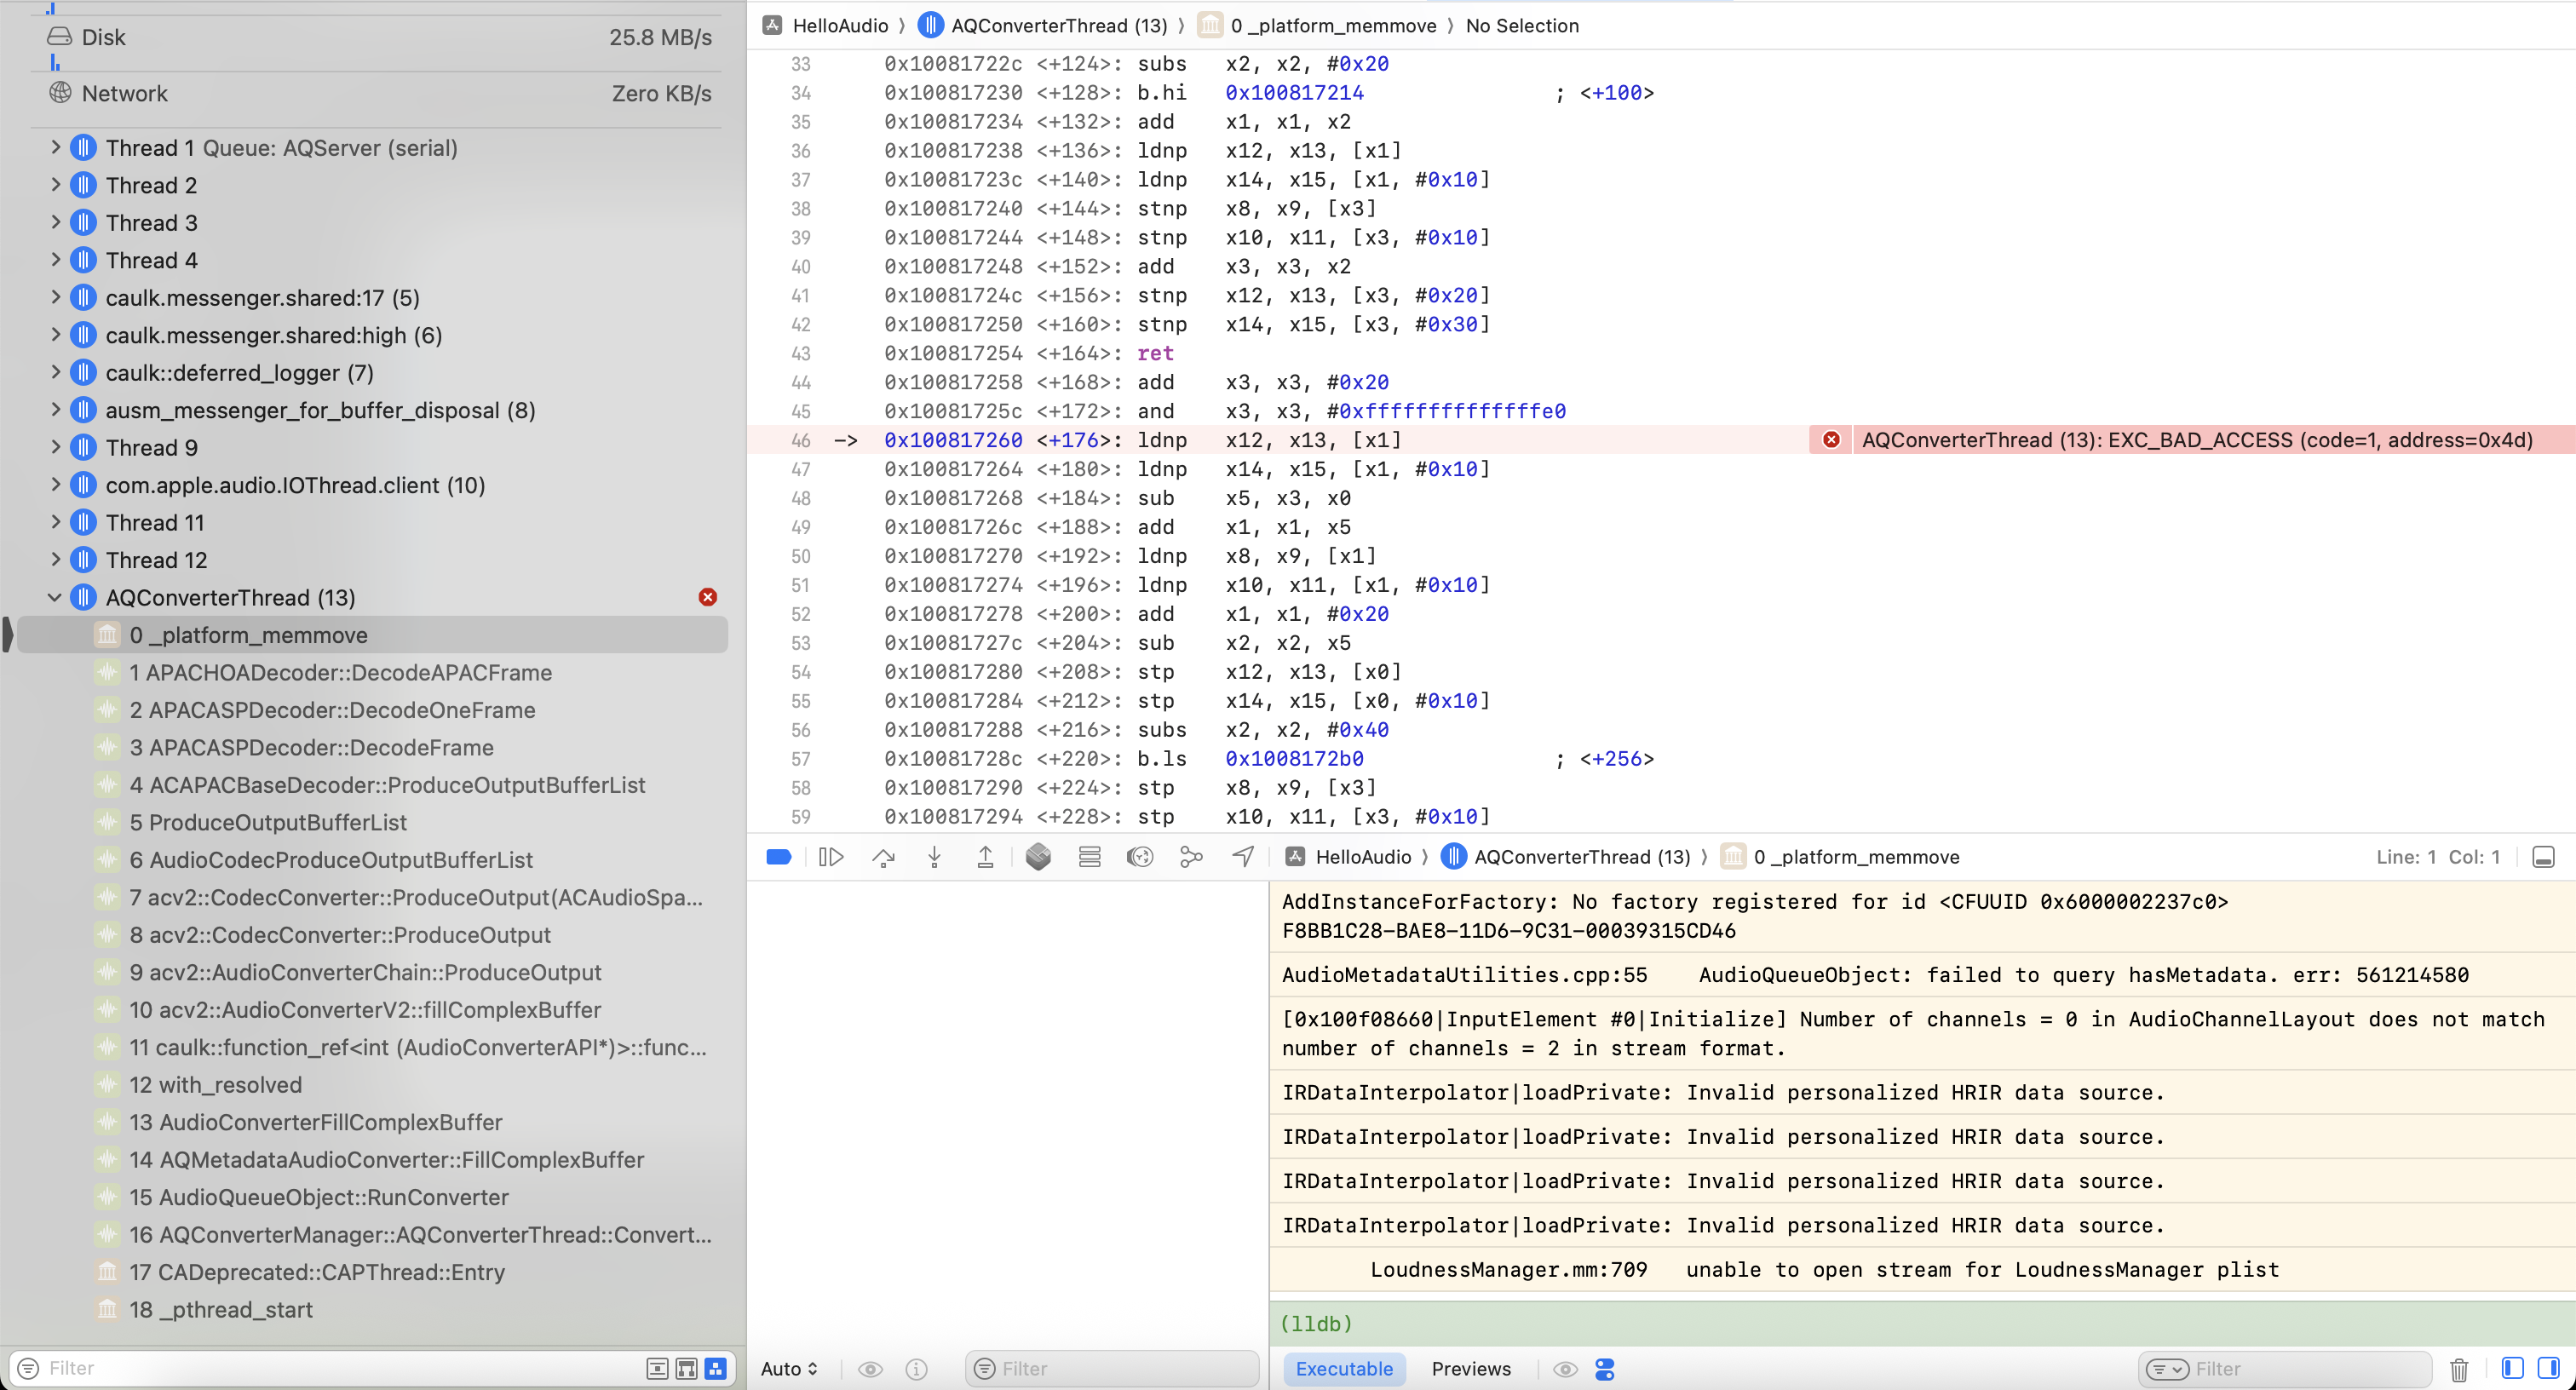
CVE-2025-31200 - @Noahhw46 figured it out
 controlplaneio/truffleproc
truffleproc — hunt secrets in process memory (TruffleHog & gdb mashup)
 codewhitesec/unmarshalpwn
POC for CVE-2018-0824
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
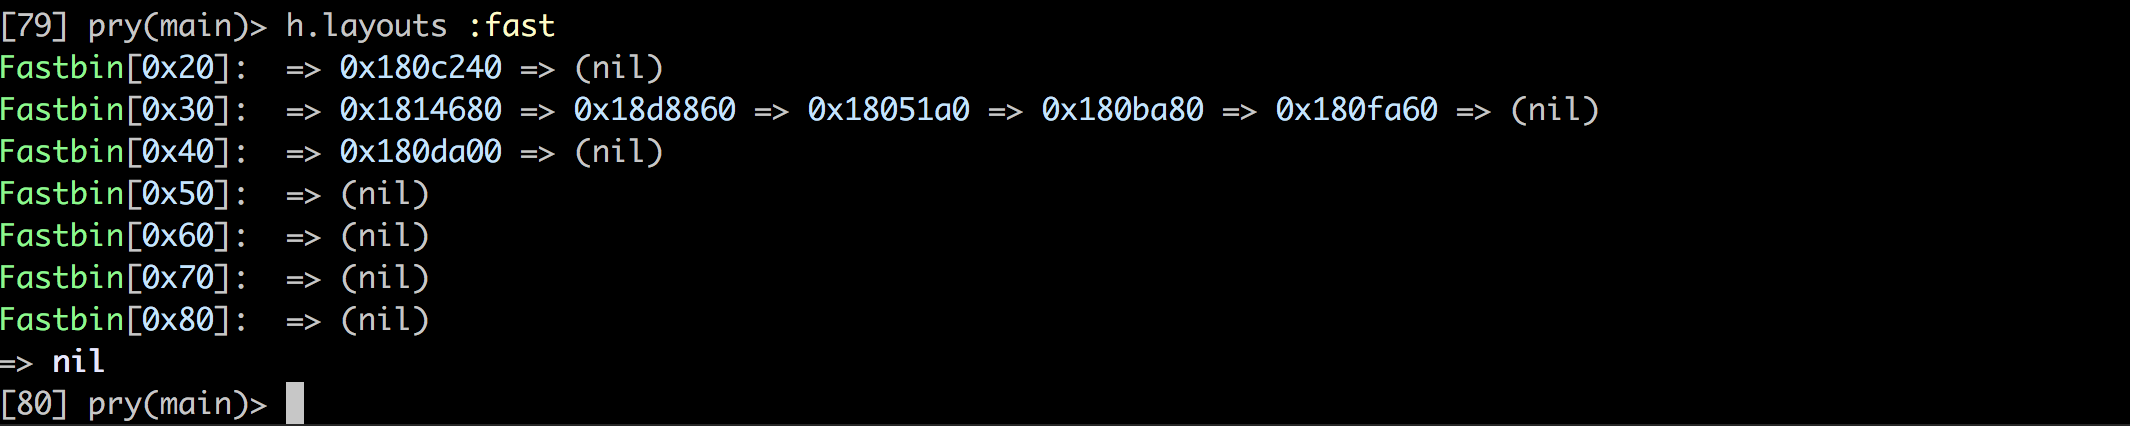 david942j/heapinfo
An interactive memory info for pwning / exploiting
 opsxcq/exploit-cve-2017-5715
Spectre exploit
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…
 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome
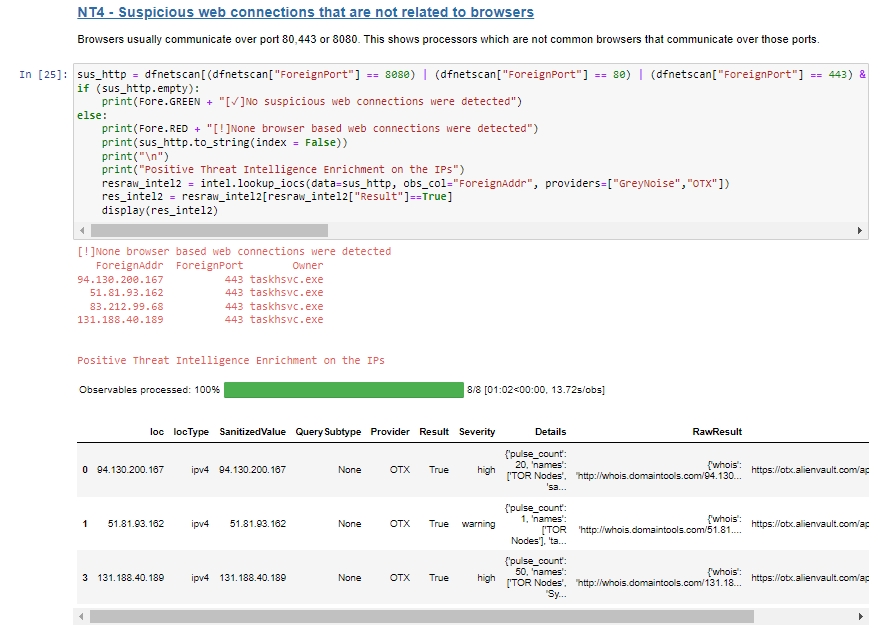 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.