

avml
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
digital-forensicsforensicsincident-response+1
1.1k
microsoft/avmlPortable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 velocidex/winpmem
The multi-platform memory acquisition tool.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
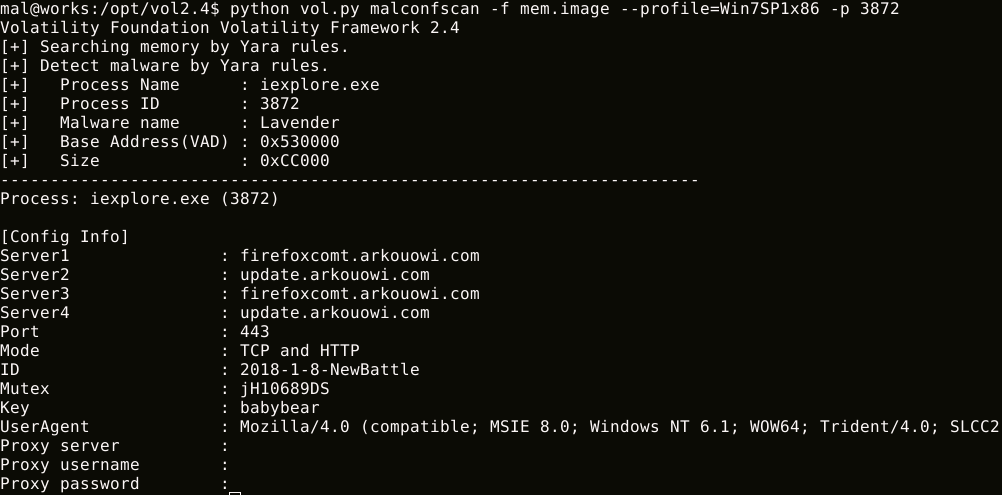 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
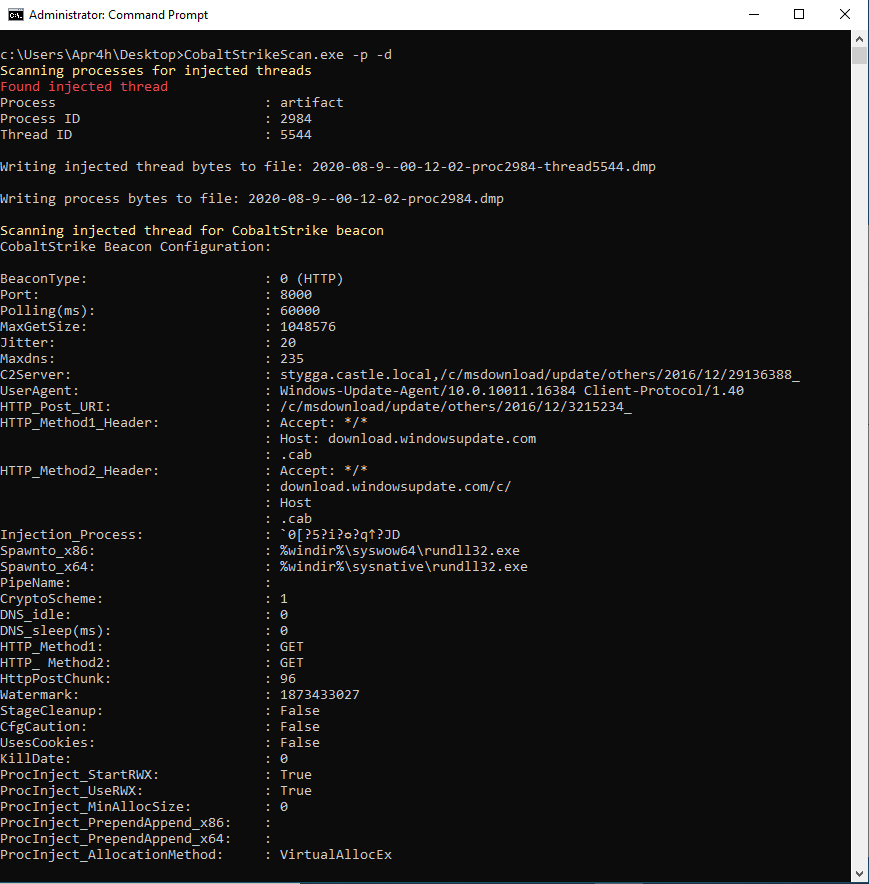 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
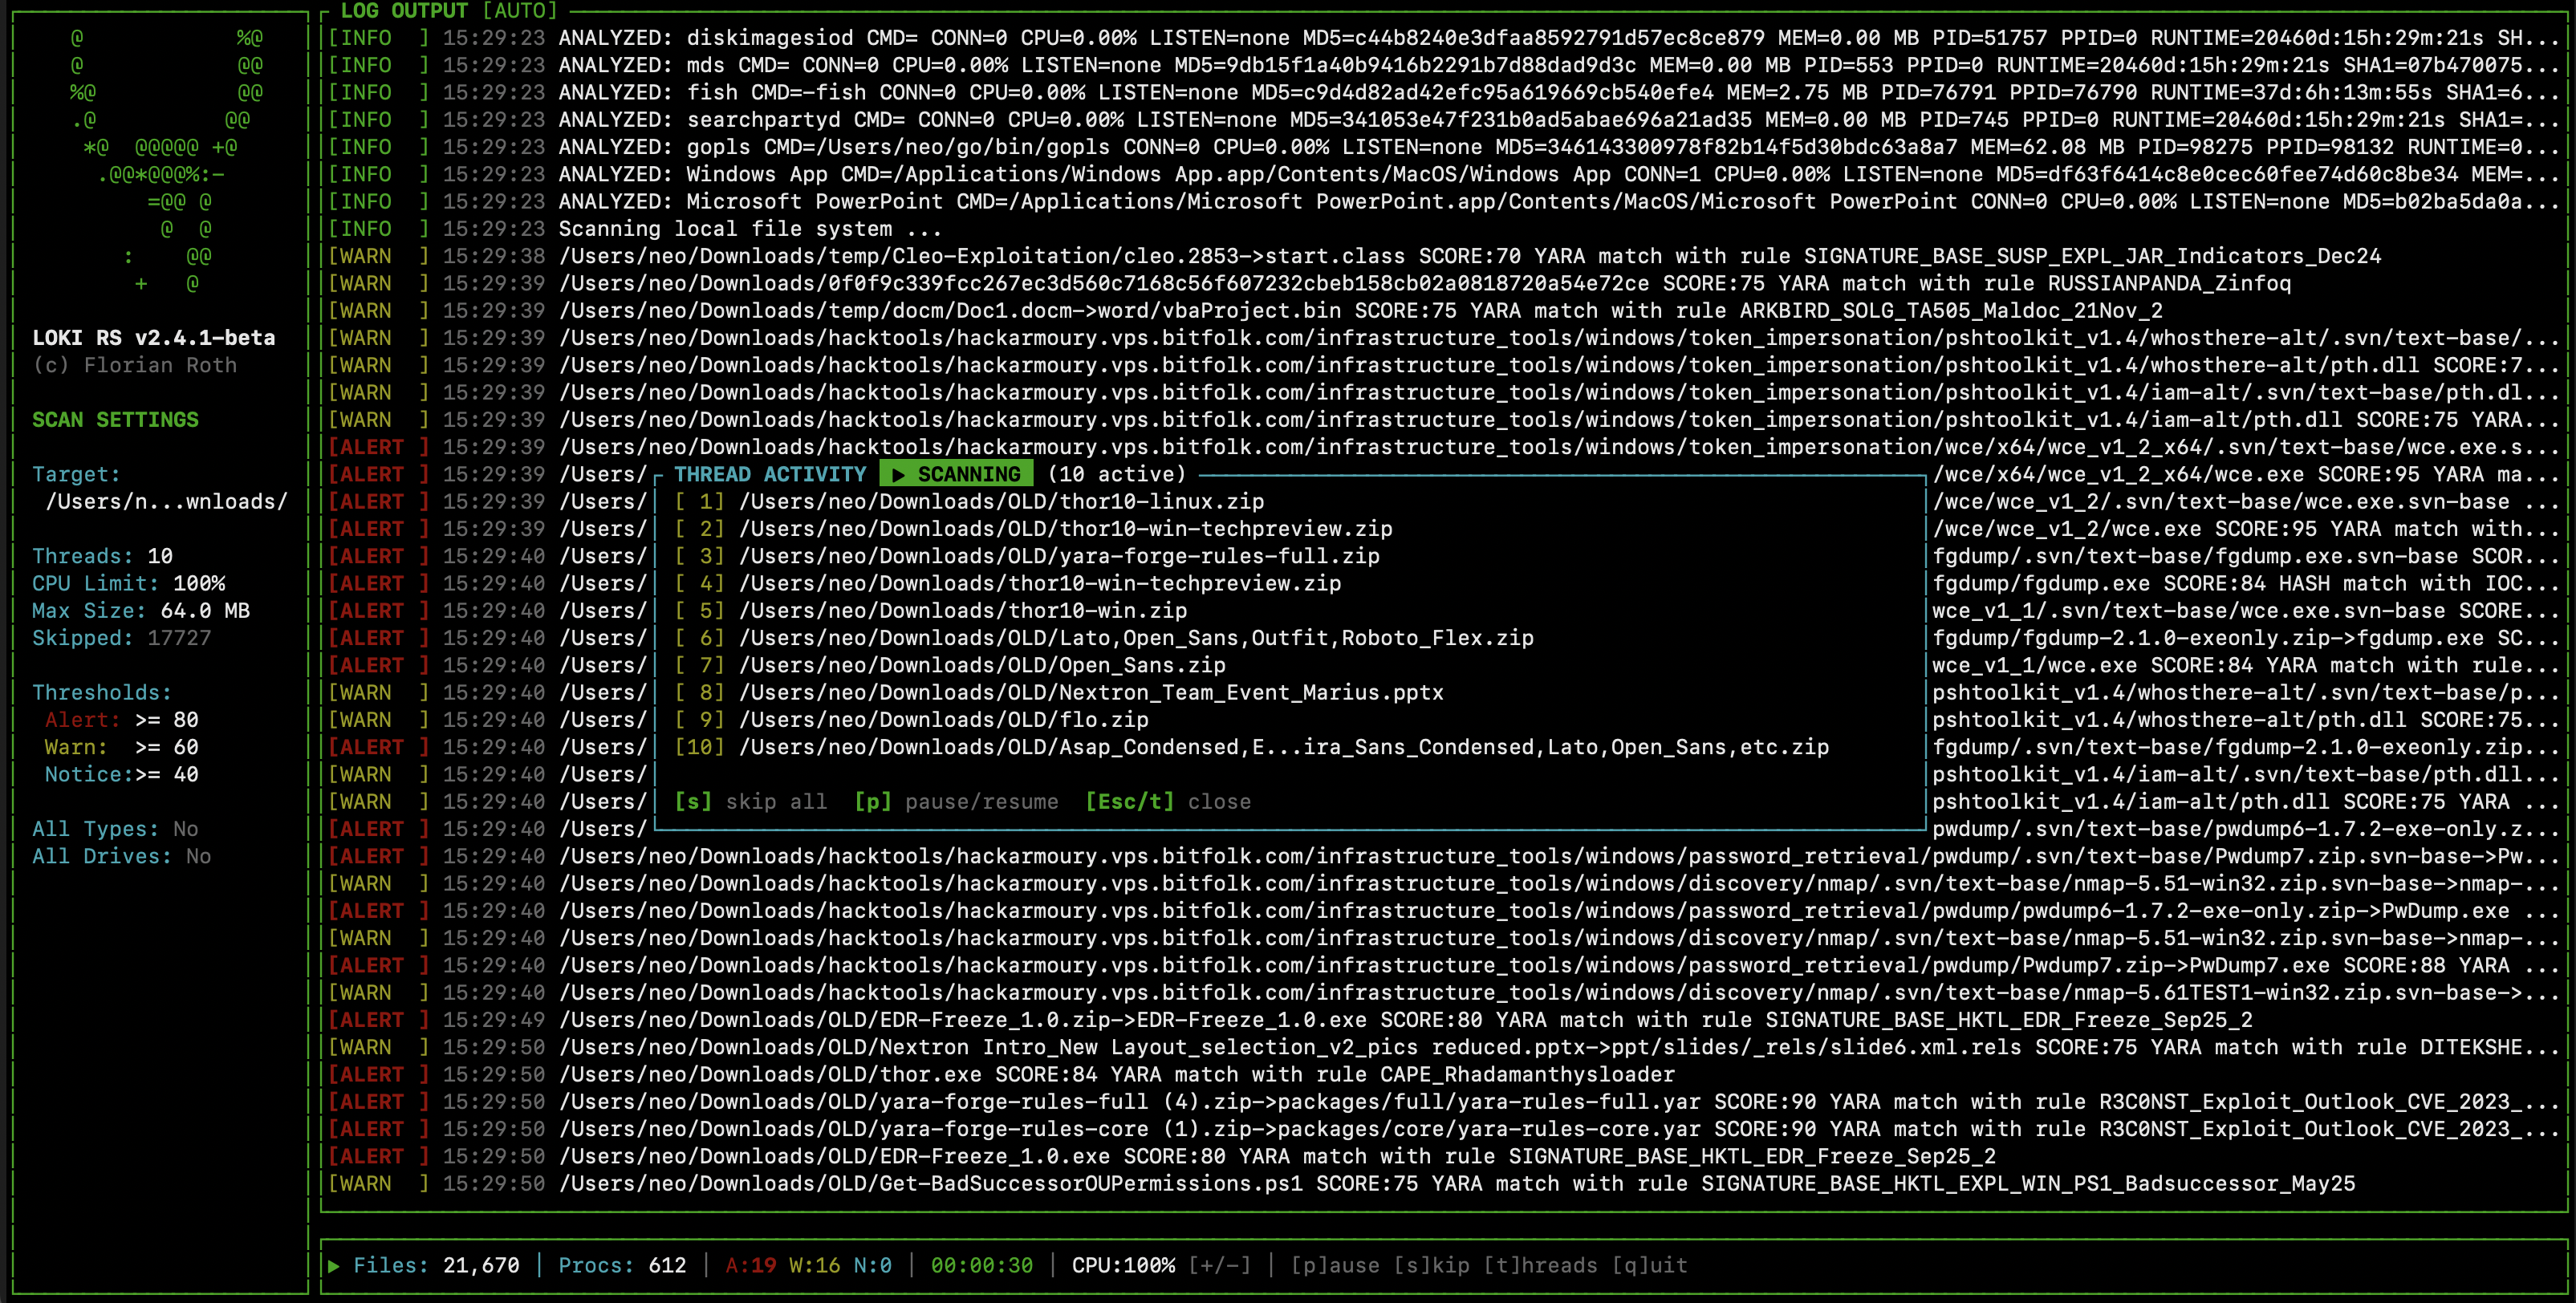 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 marcosd4h/memhunter
Live hunting of code injection techniques
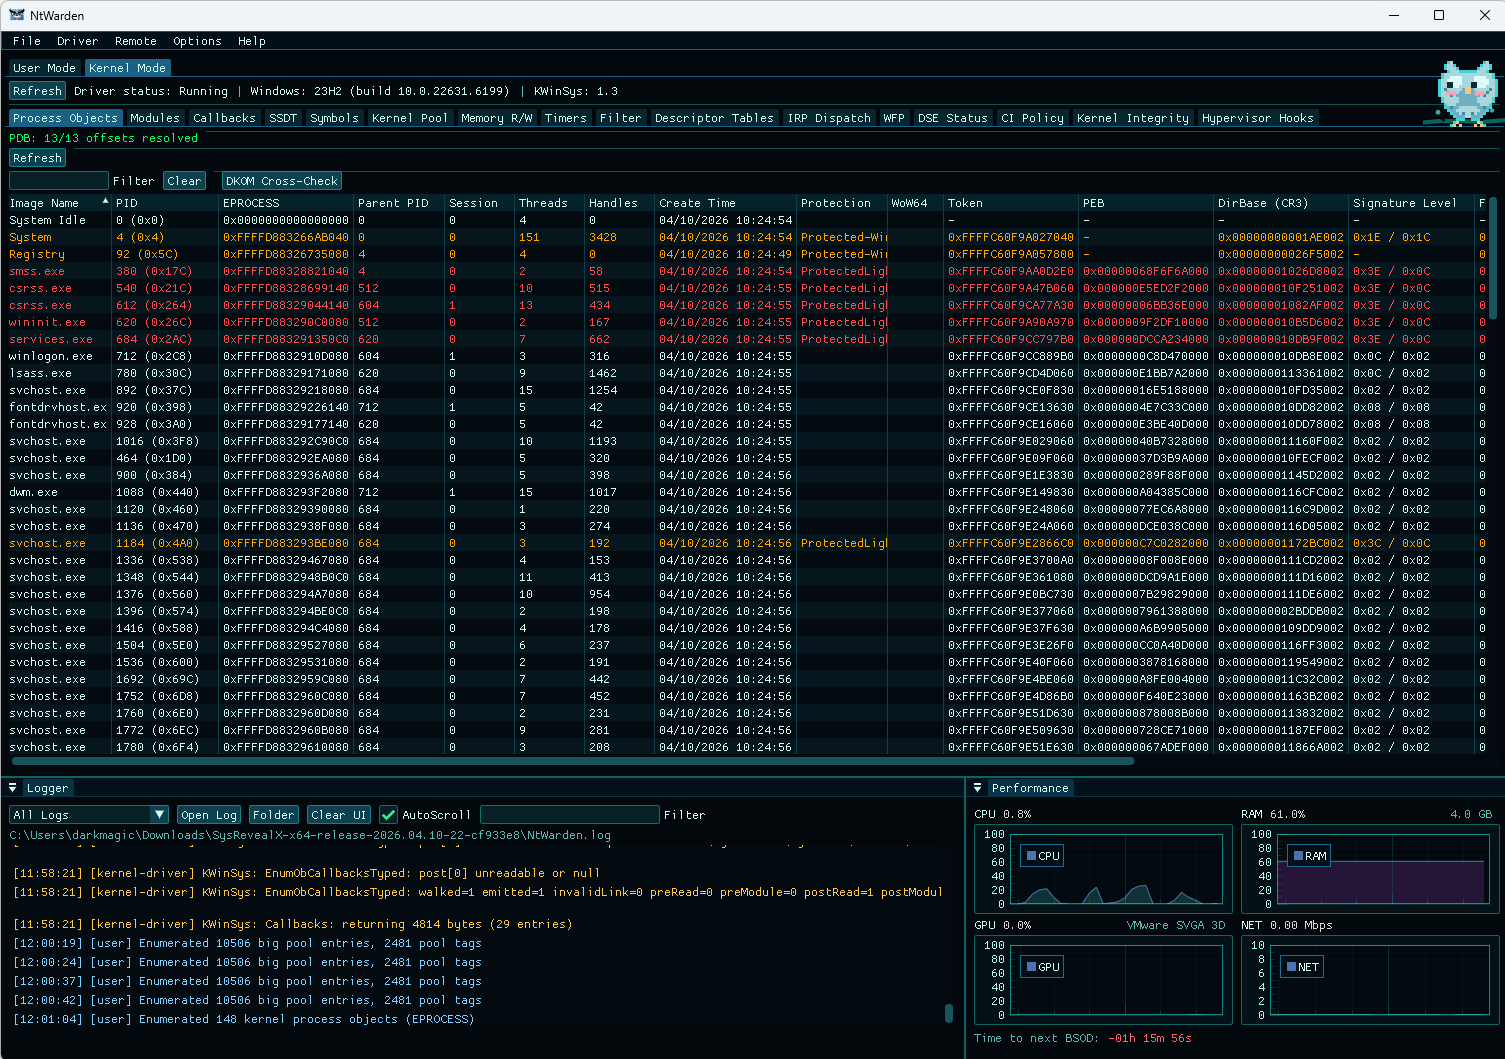 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
 halpomeranz/lmg
Script for automating Linux memory capture and analysis
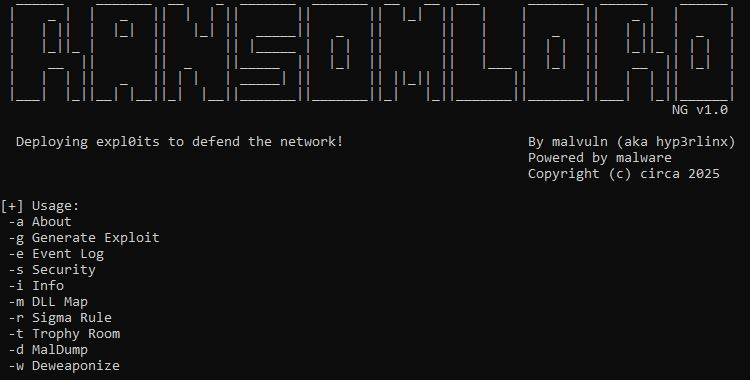 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.