
AllTools
 zodiacon/alltools
All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
zodiacon/alltoolsAll reasonably stable tools
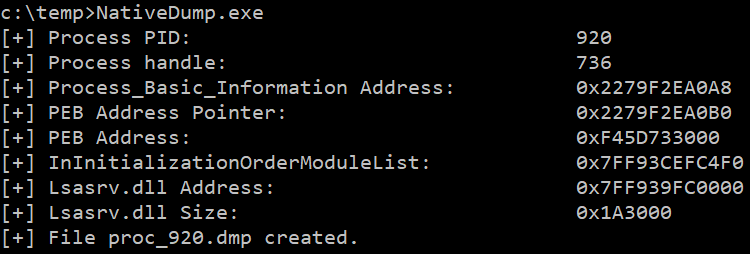 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 smarttfoxx/cve-2025-65320
Demonstrates cleartext storage of license keys in memory in Abacre Restaurant POS, enabling license activation bypass via debugger and memory dump…
 01luyicheng/cve-2026-99999
Simulation-only proof of concept for CVE-2026-99999, a Linux kernel virtio-net IPv4 csum_start validation bug enabling guest-to-host heap memory…
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

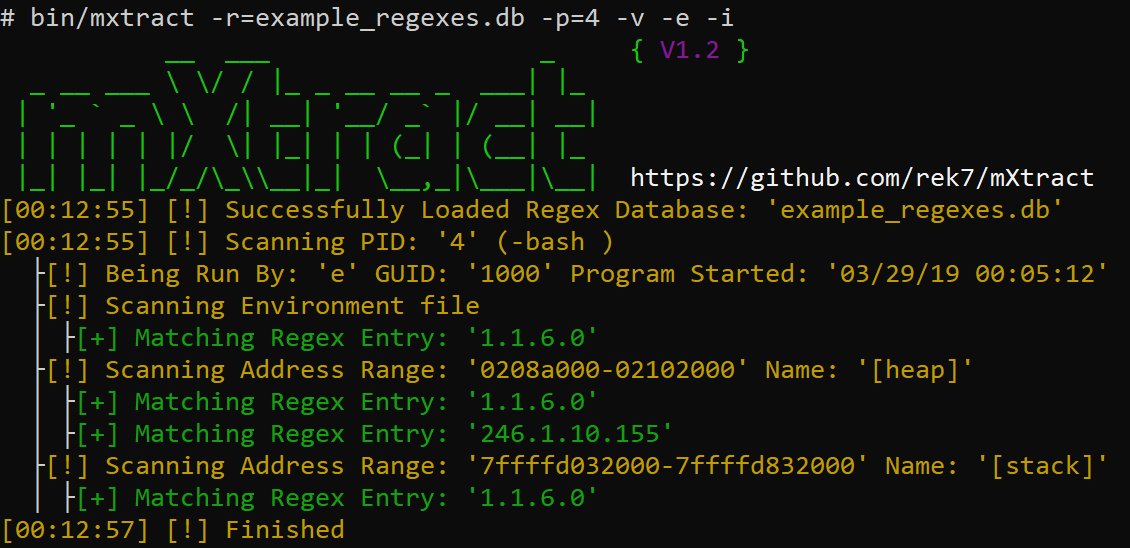 rek7/mxtract
mXtract - Memory Extractor & Analyzer