awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

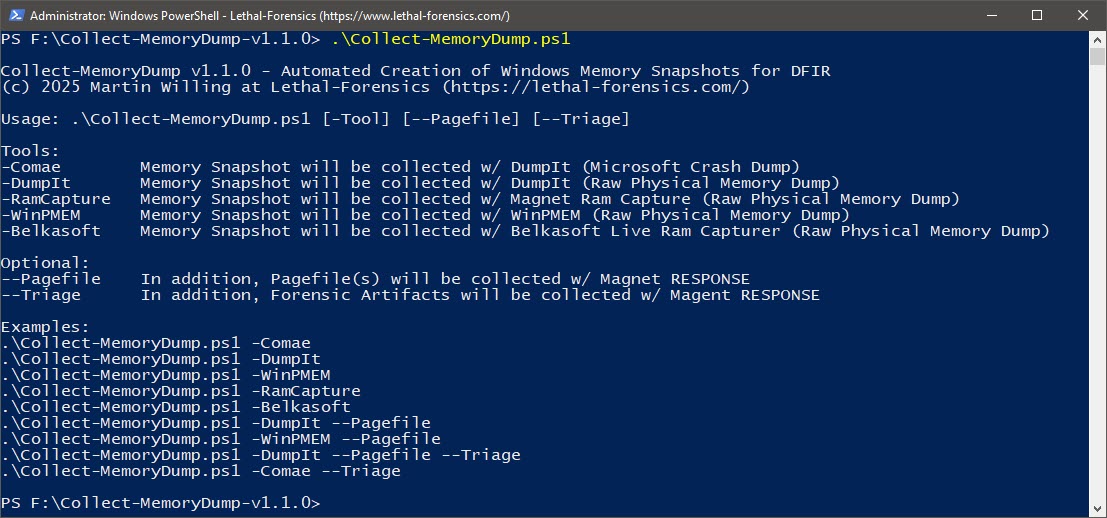
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

Live hunting of code injection techniques

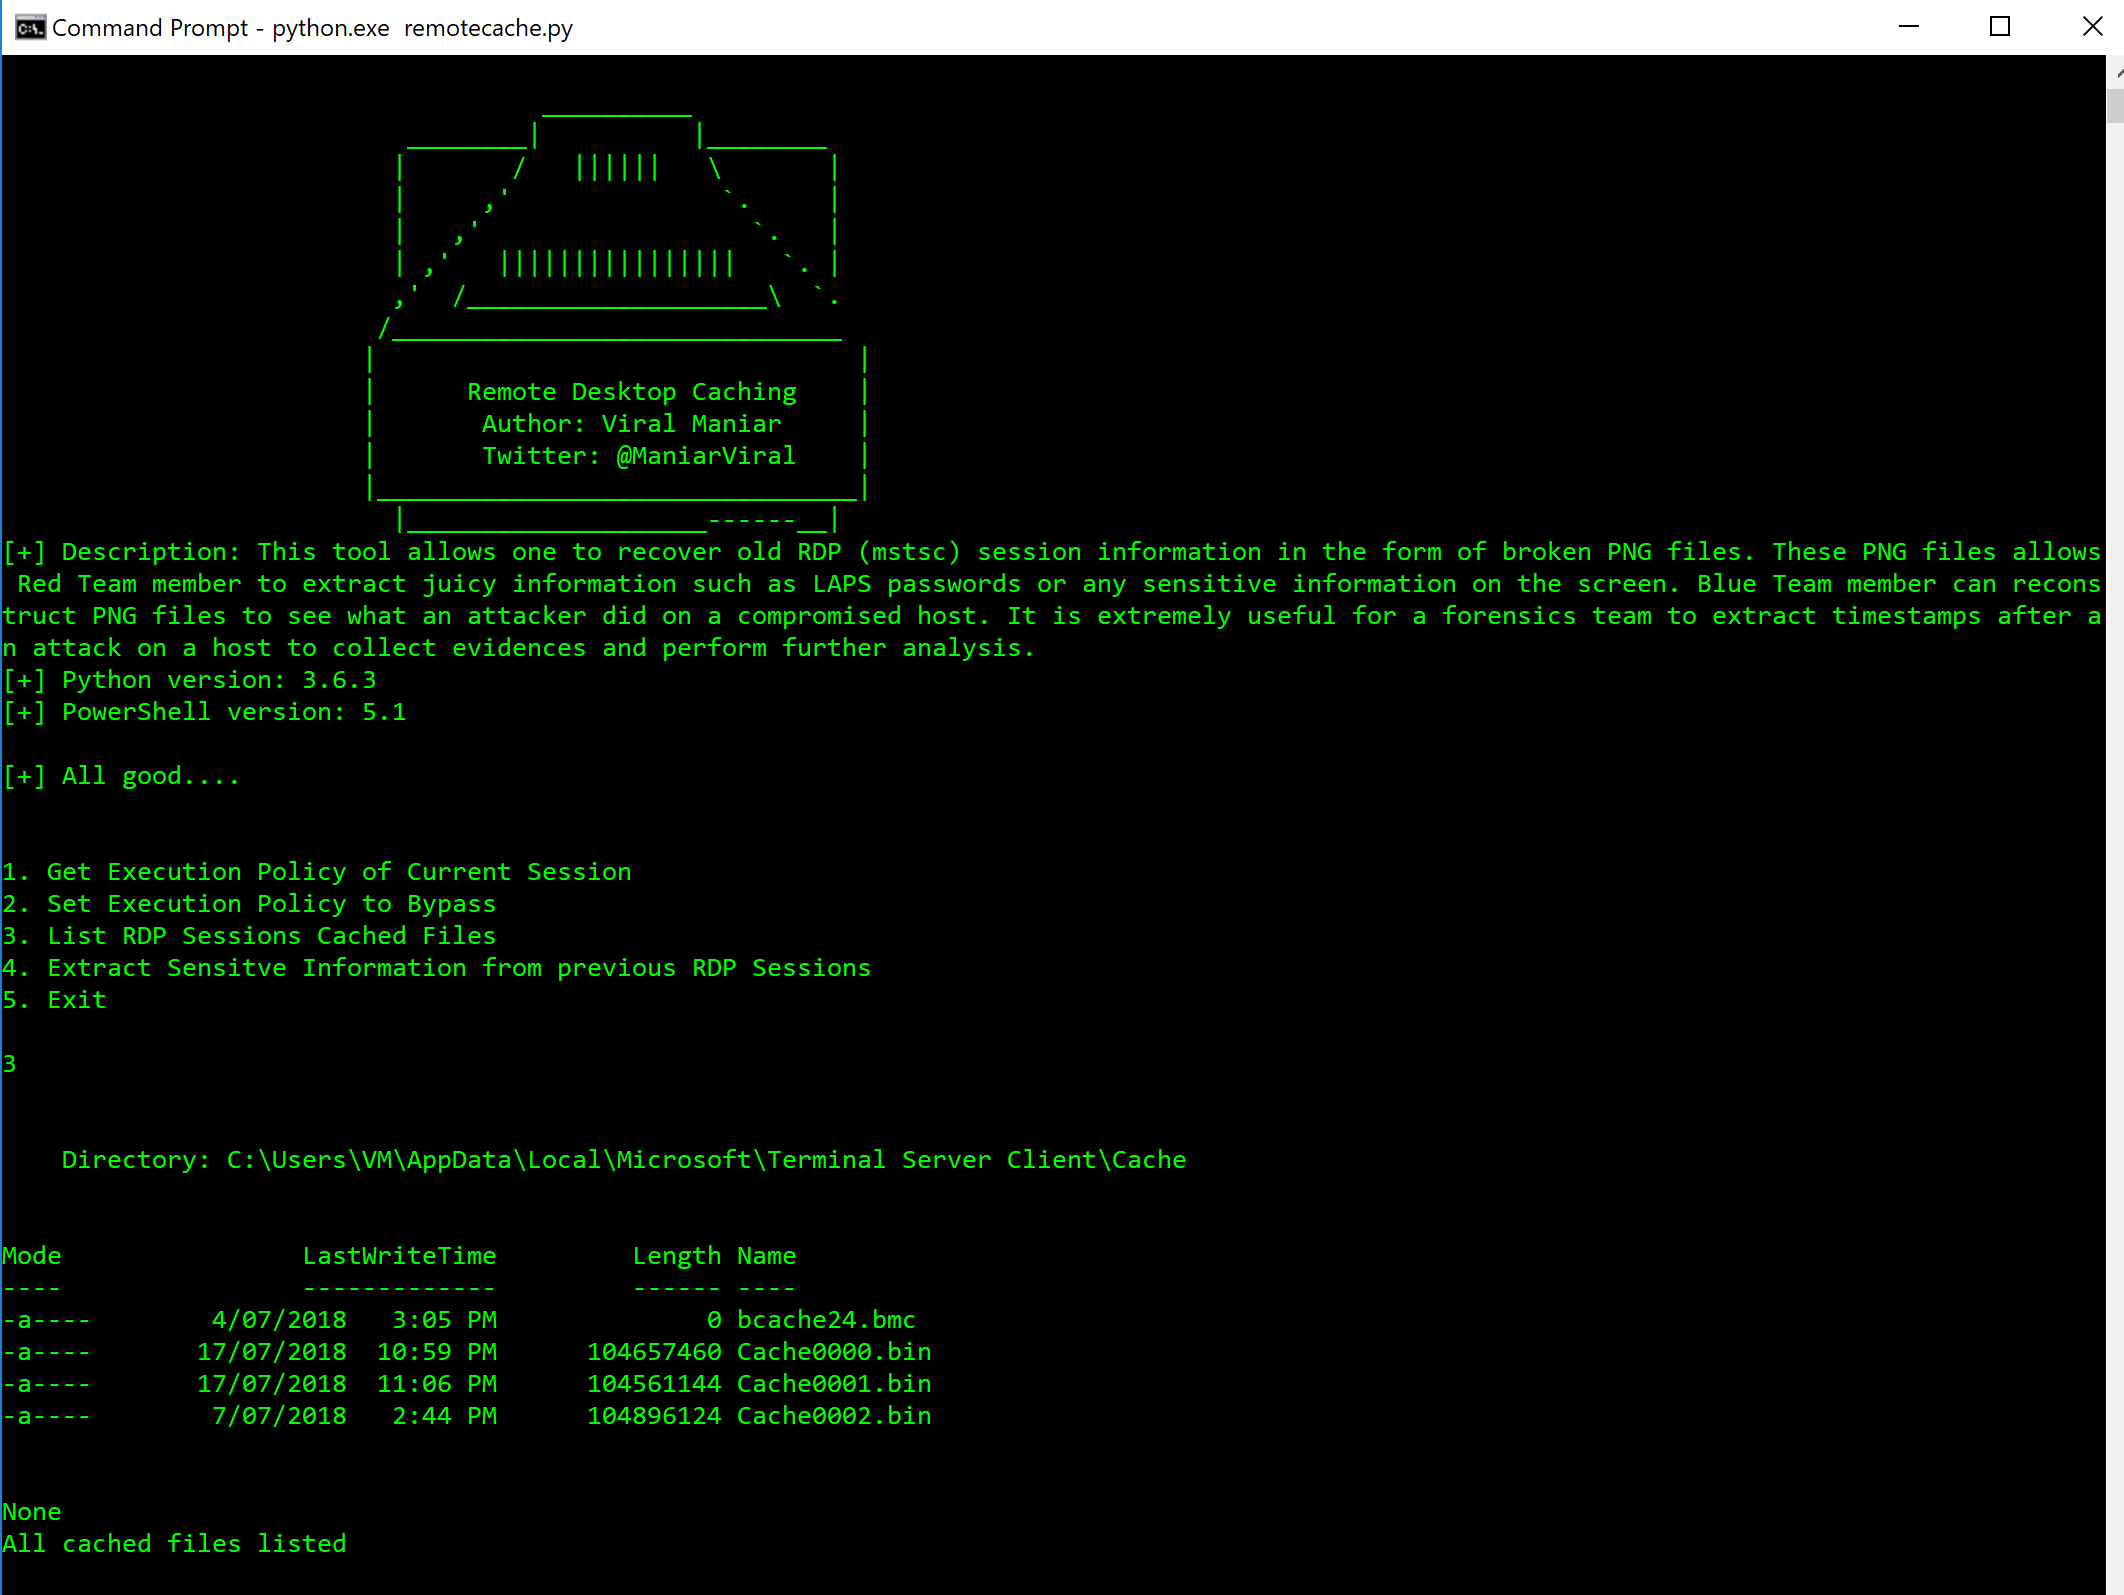
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

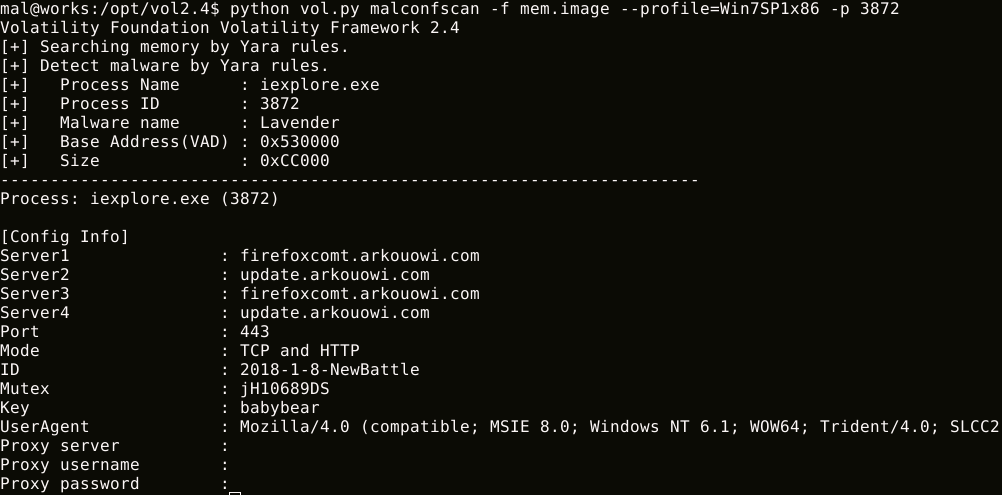
Volatility plugin for extracts configuration data of known malware

RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…

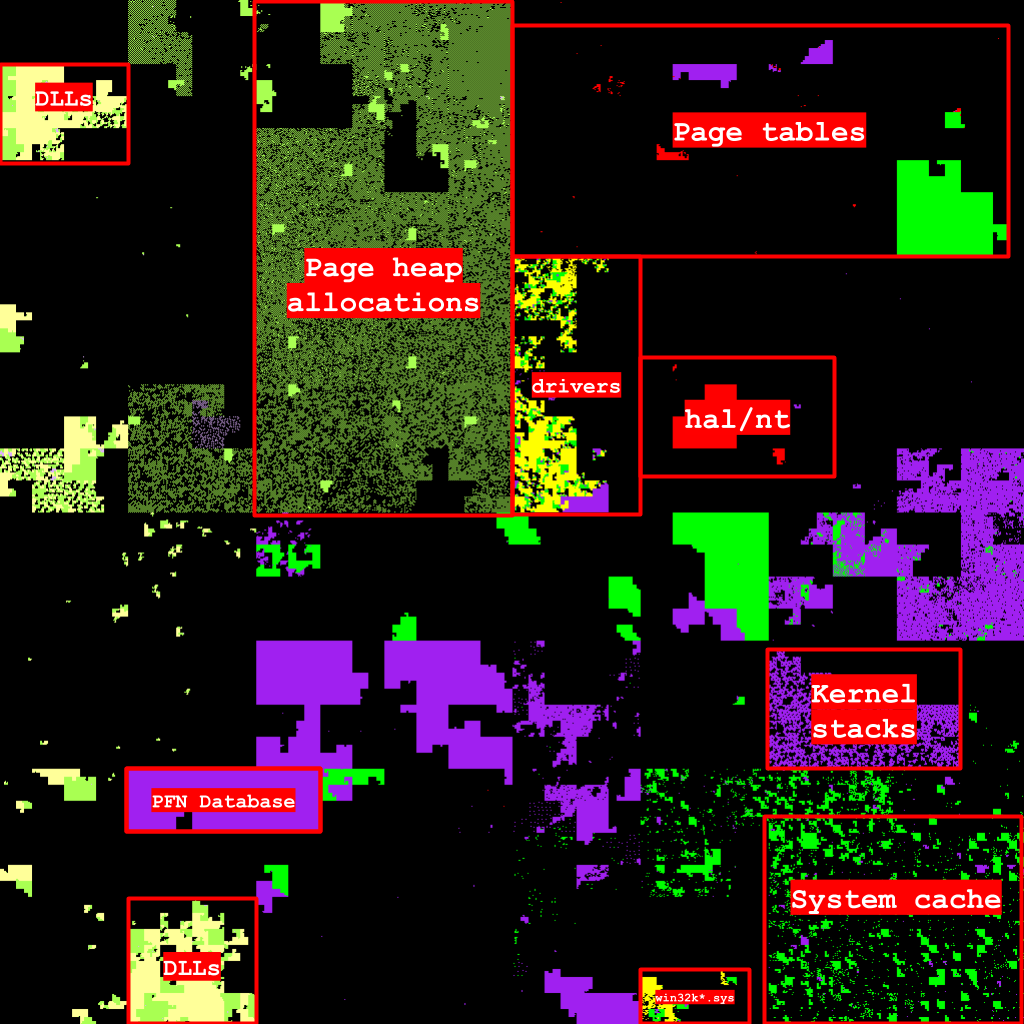
Visualize the virtual address space of a Windows process on a Hilbert curve.

A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.

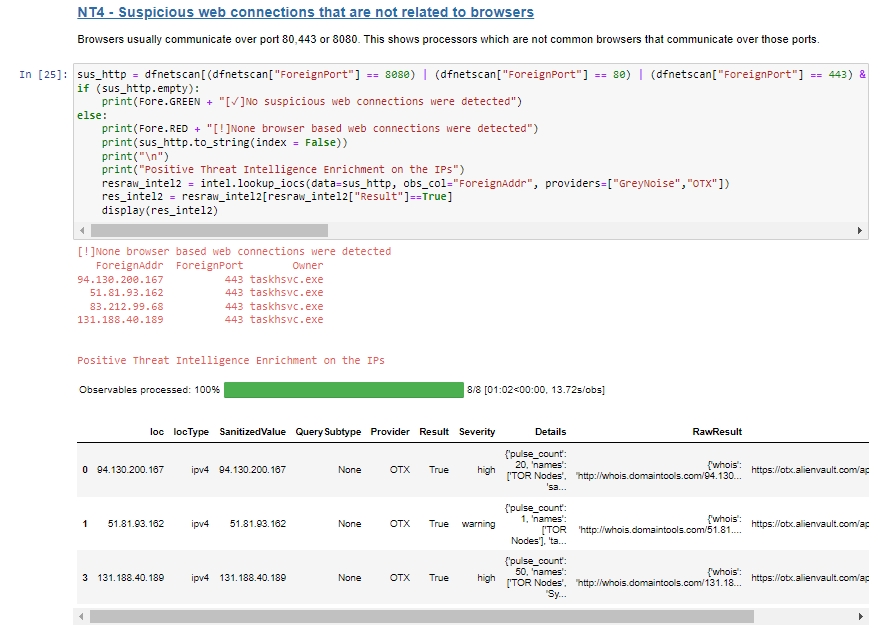
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.

Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

Retrieve the master password of a keepass database <= 2.53.1

Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.