
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
654 results
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

anomaly-detectionbinary-analysisdigital-forensics+3
61
4 years ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…

binary-analysisdebuggersdigital-forensics+9
452 years ago
PrologWinDbg preview

PrologWinDbg

GitHubdumpanalysis/prologwindbg

Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
binary-analysisdebuggersdigital-forensics+4
1514 days ago
StealMyBitcoin-PoC preview

StealMyBitcoin-PoC

GitHubkillaboi/stealmybitcoin-poc

A public release of the Steal My Bitcoin challenge
binary-exploitationctfexploitation+5
1.0k8 days ago
NtWarden preview

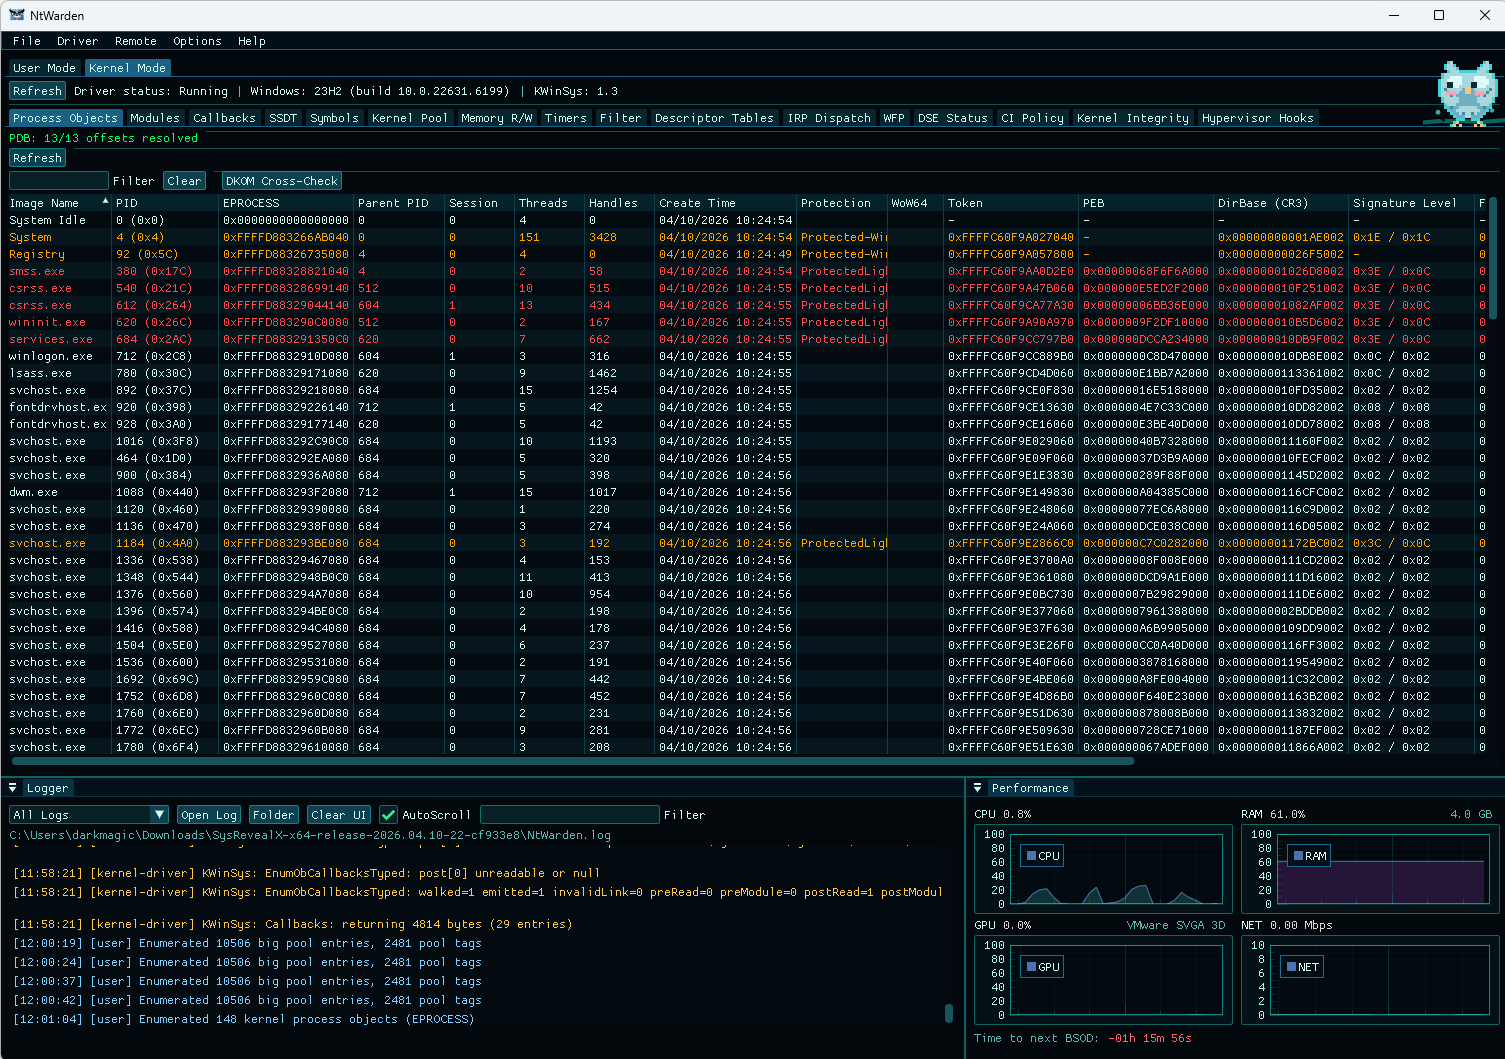
NtWarden

GitHubmrt4ntr4/ntwarden

Windows Analysis and Research Toolkit
binary-analysisdefensive-toolsdigital-forensics+4
6766 months ago
RansomLord preview

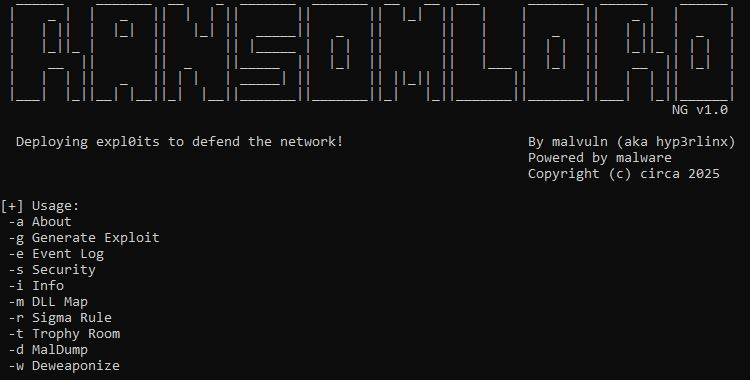
RansomLord

GitHubmalvuln/ransomlord

RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…

binary-exploitationdefensive-toolsexploitation+4
5161 year ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…

binary-analysisdebuggersdigital-forensics+10
8.9k27 days ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k1h 43m ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

encryption-decryption-toolsforensicshash-analysis+8
11.0k1 year ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.3k22 days ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

data-recoverydigital-forensicsdisk-forensics+7
3.4k8 days ago
fibratus preview

fibratus

GitHubrabbitstack/fibratus

Security sensor for realtime threat detection and protection

defensive-toolsforensicsincident-response+3
2.5k15 days ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k9 months ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.

binary-analysisforensicsmalware-analysis+2
1.9k1 month ago
jshookmcp preview

jshookmcp

GitHubvmoranv/jshookmcp

A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
ai-securitybinary-analysisdebuggers+9
2.1k14h 11m ago
mimikittenz preview

mimikittenz

GitHuborlyjamie/mimikittenz

A post-exploitation powershell tool for extracting juicy info from memory.
information-gatheringmemory-forensicspenetration-testing+1
1.9k6 years ago
drmemory preview

drmemory

GitHubdynamorio/drmemory

Memory Debugger for Windows, Linux, Mac, and Android
debuggersdynamic-analysis-sandboxingmemory-forensics+2
2.7k10 months ago
xnu preview

xnu

GitHubapple-oss-distributions/xnu

Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…

debuggersembedded-systems-securityfirmware-analysis+2
3.5k1 year ago
Previous123…37Next