

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
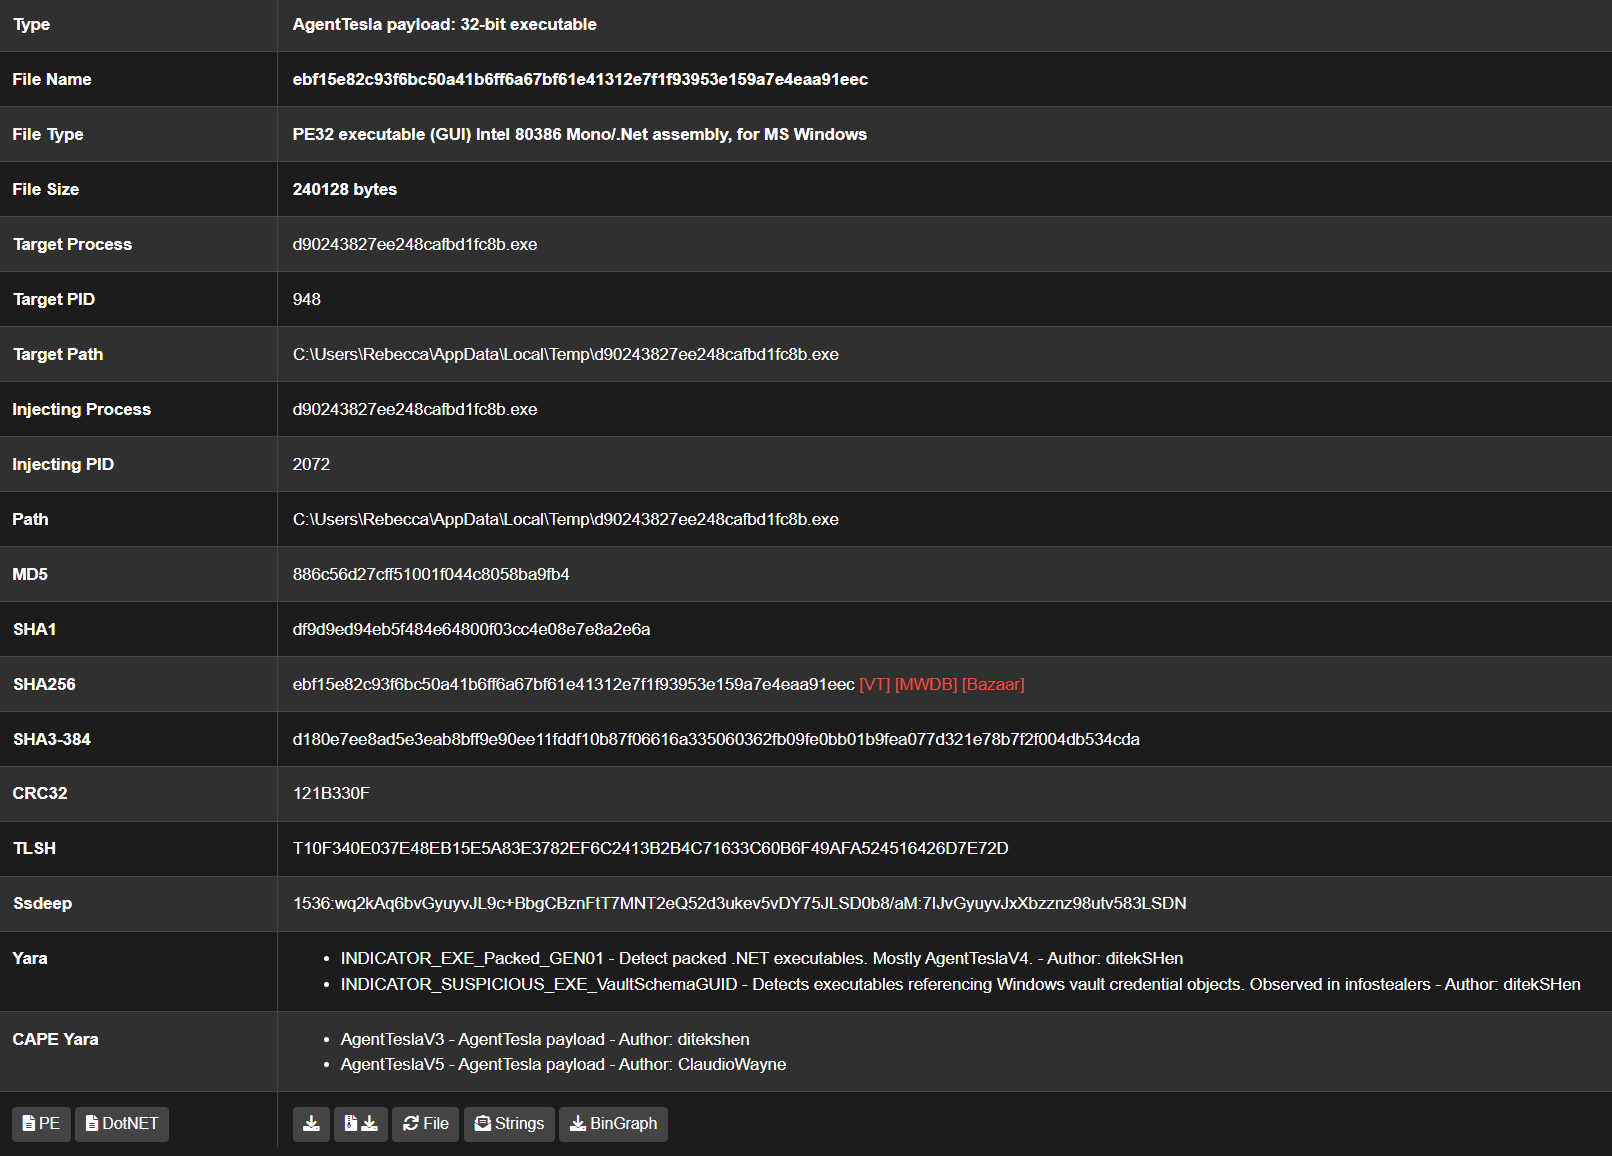 kevoreilly/capev2
Malware Configuration And Payload Extraction
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.

 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass

 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…