
MemProcFS-Analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

SLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

A PoC Java Stager which can download, compile, and execute a Java file in memory.

Security sensor for realtime threat detection and protection

Windows tool for dumping malware PE files from memory back to disk for analysis.

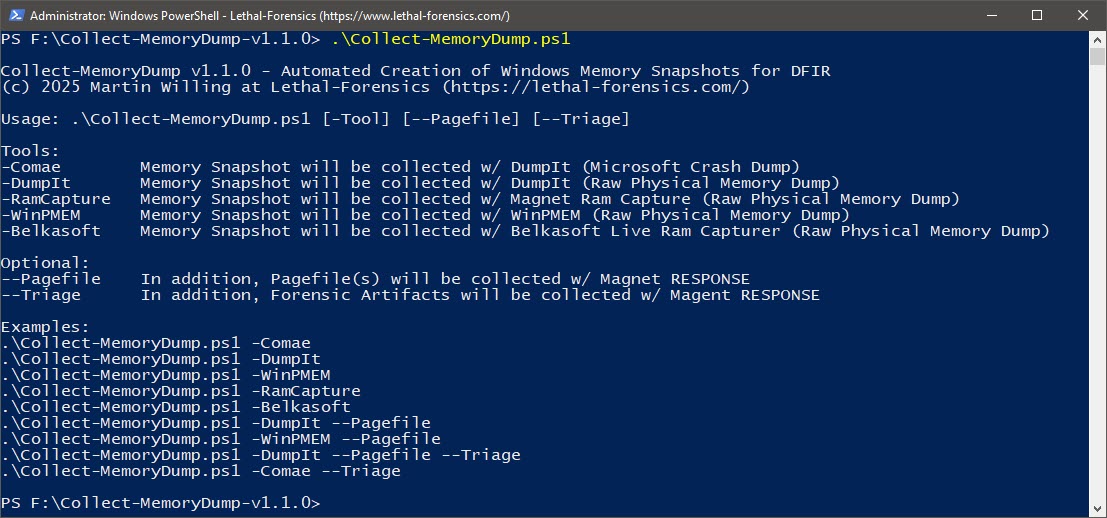
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…