

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
72 results
memory-relocalloc preview

memory-relocalloc

GitHubgmh5225/memory-relocalloc

C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…

binary-exploitationexploitationmalware-analysis+6
2
4 years ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

ai-assisted-reversingbinary-analysisbinary-exploitation+7
28 days ago
NativePe preview

NativePe

GitHubhabanada/nativepe

Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
binary-analysisbinary-exploitationdynamic-analysis-sandboxing+5
1821 days ago
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

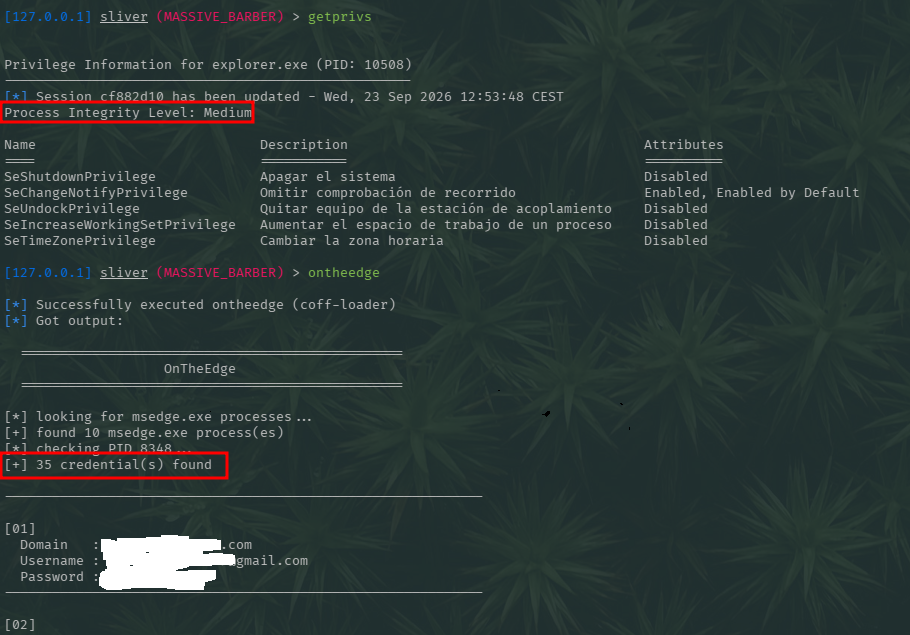
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

command-and-controldata-exfiltrationmalware-analysis+4
1129 days ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
3 years ago
CVE-2026-85048-the-gpu-died preview

CVE-2026-85048-the-gpu-died

GitHubsneakynachos/cve-2026-85048-the-gpu-died

Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…

binary-exploitationdebuggersexploitation+4
11 month ago
DMA-ProcessDumper preview

DMA-ProcessDumper

GitHubgmh5225/dma-processdumper

Simple Process Dumper using DMA over a PCIe FPGA device

data-exfiltrationforensicshardware-hacking+3
4 years ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
exploitationmemory-forensicspayload-development+2
3.4k13 years ago
KsDumper-11 preview

KsDumper-11

GitHubmastercodeon314/ksdumper-11

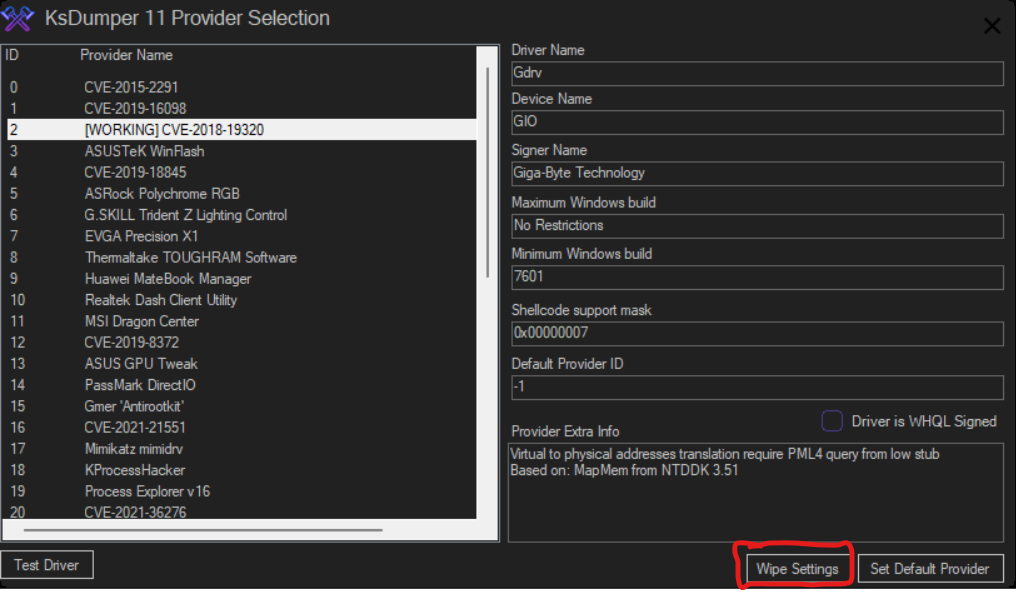
A revival of the classic and legendary KsDumper

binary-analysisexploitationmemory-forensics+1
5941 year ago
community preview

community

GitHubvolatilityfoundation/community

Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…
digital-forensicsmalware-analysismemory-forensics
3786 years ago
memdumper preview

memdumper

GitHubcenobyte-vincit/memdumper

Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…

digital-forensicsids-ips-evasioninformation-gathering+4
12 months ago
keepass-exfil-forensics preview

keepass-exfil-forensics

GitHubpugazhendii22/keepass-exfil-forensics

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…

ctfdata-exfiltrationdigital-forensics+6
2 months ago
physmem2profit preview

physmem2profit

GitHubreverseclabs/physmem2profit

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
data-exfiltrationdigital-forensicsmemory-forensics+4
4234 years ago
AzTokenFinder preview

AzTokenFinder

GitHubhackmichnet/aztokenfinder

Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
authenticationcloud-securitymemory-forensics+3
1093 years ago
truffleproc preview

truffleproc

GitHubcontrolplaneio/truffleproc

truffleproc — hunt secrets in process memory (TruffleHog & gdb mashup)

debuggersdigital-forensicsmemory-forensics+1
1303 years ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2684 years ago
clairvoyance preview

clairvoyance

GitHub0vercl0k/clairvoyance

Visualize the virtual address space of a Windows process on a Hilbert curve.

digital-forensicsforensicsmemory-forensics
3125 years ago
ChromeKatz preview

ChromeKatz

GitHubmeckazin/chromekatz

Dump cookies and credentials directly from Chrome/Edge process memory

data-exfiltrationdebuggersmemory-forensics+3
1.5k6 months ago
Previous1234Next