MemProcFS-Analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
anomaly-detectiondigital-forensicsincident-response+5

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Research project related to memory address analysis

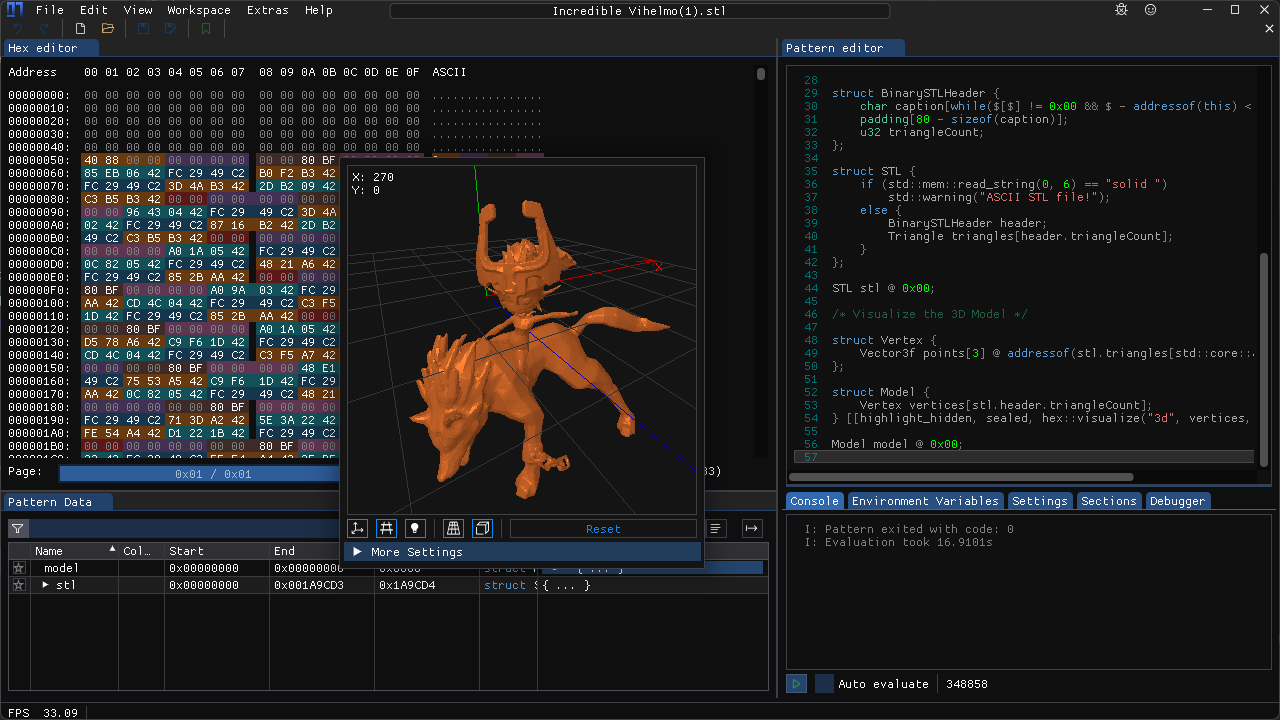
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

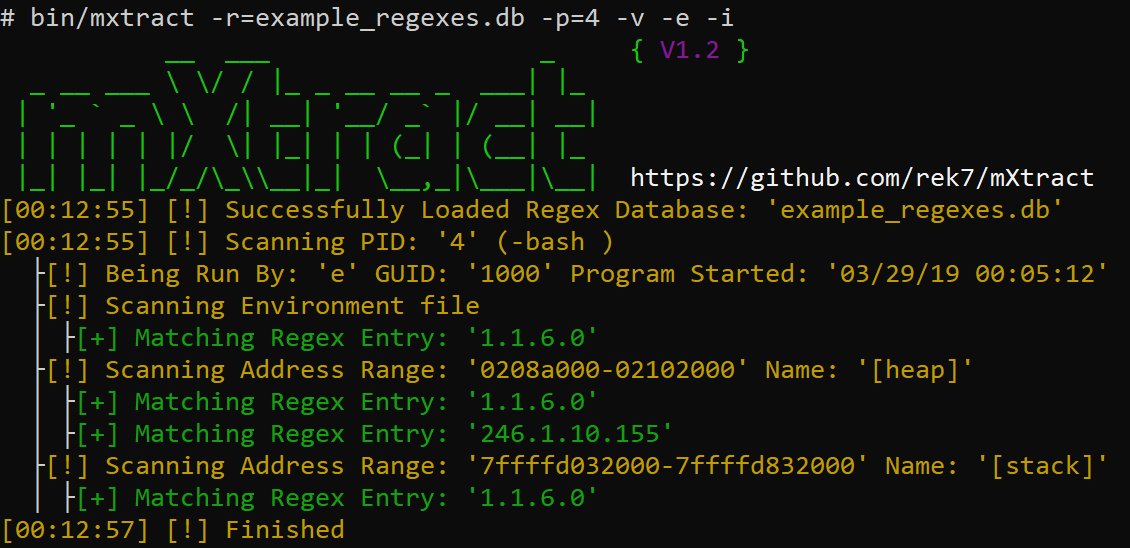
mXtract - Memory Extractor & Analyzer

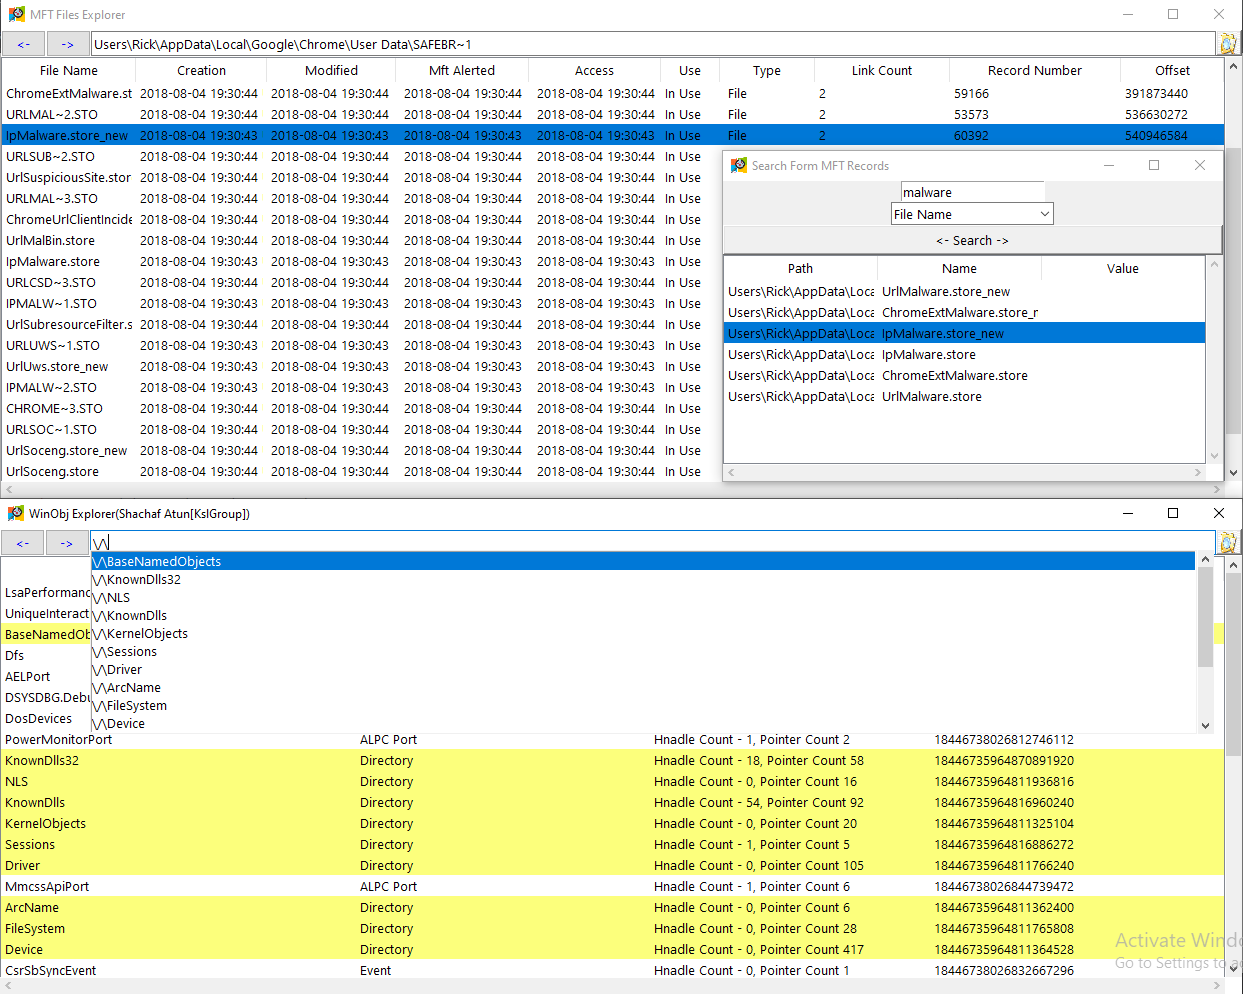
Volatility Explorer Suit (volatility 3)

Yet Another Memory Analyzer for malware detection

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…